Post con #HTML2shell

#HTML2shell

Post pubblici su X che usano #HTML2shell.

Hashtag correlati

  1. BleepingComputer✓@BleepinComputer
    CISA has confirmed that hackers are actively exploiting a critical Brotli vulnerability (CVE-2026-111497), also known as Node2Shell, Broccoli2Shell, and HTTP2Shell.
    135421319.5K
  2. pilvar (Philippe Dourassov)✓@pilvar222
    We made a website to check if your http client is vulnerable to CVE-2026-111497 (Node2Shell/HTTP2Shell) Also open-source: Some examples:
    Scarica
    63120716.6K
  3. WP-Content.co@wpcontent_co
    HTTP2Shell: What the Critical Brotli Vulnerability Means for WordPress Sites
    00165
  4. caveeroo@caveeroo
    HTTP2Shell (CVE-2026-111497) is exploitable outside Node. Unauth RCE against a pinned vulnerable Docker Official Image for WordPress via /xmlrpc.php. One inbound ASLR on, no leak or cross-request grooming. PoC:
    46127044.8K
  5. Paul Price✓@darkp0rt
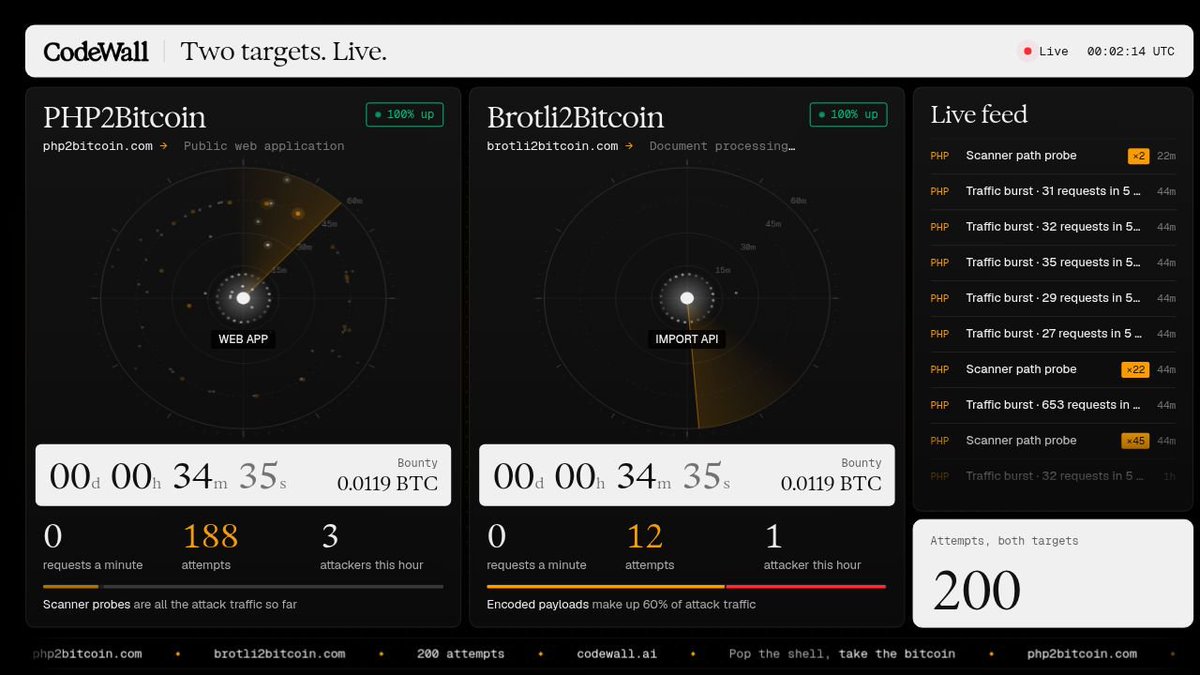
    php2shell and http2shell have been all over the timeline these past few days. But how hard are they to actually exploit? Let's find out: and Pop an RCE, grab the flag and take the $1K BTC AND watch live
    Scarica
    003172
  6. HAProxy Technologies✓@HAProxy
    HAProxy is NOT vulnerable to the new HTTP2Shell vulnerability (CVE-2026-111497). While HAProxy Community and HAProxy Enterprise are safe, your backend applications might still be at risk. The good news? You can use HAProxy to block the attack vector at the edge while you patch your fleet. Read our latest advisory to get the stopgap configuration and secure your infrastructure today:
    Scarica
    104423
  7. IT-Connect.fr@ITConnect_fr
    Node2Shell, HTTP2Shell, Broccoli2Shell : une seule faille Brotli (CVE-2026-111497), et après Node.js, Python, .NET et Linux publient leurs correctifs. Voici l'essentiel à savoir : 👉 #cybersécurité #python #dotnet
    Scarica
    06121.4K
  8. WeltPixel✓@WeltPixel
    HTML2Shell is a joke, a fake 10.0 CVE record posted on X on October 24. Its number belongs to an unrelated Kirby CMS bug. The real one is HTTP2Shell, a Brotli decoder bug rated 9.2 Critical.
    0005
  9. Wordfence✓@wordfence
    HTTP2Shell: What the Critical Brotli Vulnerability Means for WordPress Sites Update Brotli to version 1.0.10, 1.1.1, 1.2.1 as soon as possible.
    14152.3K
  10. Frelzu✓@Frelzu
    🆘Node2Shell. Broccoli2Shell. HTTP2Shell. three names. one Brotli bug. CISA says it's being exploited. and it's not just a Node problem anymore. anything that decodes Brotli with a vulnerable library is in scope. Microsoft already pushed emergency .NET patches. the step everyone skips: → update → restart the process → rebuild and redeploy your container images a patched host doesn't fix the old Node binary baked into last month's image.
    Scarica
    BleepingComputer @BleepinComputer
    CISA has confirmed that hackers are actively exploiting a critical Brotli vulnerability (CVE-2026-111497), also known as Node2Shell, Broccoli2Shell, and HTTP2Shell.
    206536
  11. TrendAI@trendaisecurity
    eMudhra. PHP. Now HTTP2Shell. Three critical vulnerabilities in just over a week, and the scariest part is what you can’t see. Join TrendAI’s webinar Oct 29, 11 AM. EDT.
    104792
  12. GTconsult@GT_consult
    Almost every app unpacks data silently. A flaw called Broccoli2Shell, Node2Shell, or HTTP2Shell (CVE-2026-111497) needs no password to exploit. Swipe through >>> #CyberSecurity #CVE #CloudSecurity
    Scarica
    00097
  13. remot3@_remot3
    The danger of HTTP2Shell is very real. The libbrotli 🥦vulnerability affects a wide range of software, patch now (CVE-2026-111497) We've achieved unauth RCE in Docker's official WordPress image abusing the well known /xmlrpc.php endpoint, we call it the pingback of hell :)
    Scarica
    1710862068.6K
  14. Randy A. Folmes✓@RFolmes
    Three security stories every IT team should be watching: PHP2Shell: CISA confirms two critical PHP flaws are being exploited, allowing remote code execution on unpatched servers. Ottawa even pulled some federal sites offline as a precaution. Update PHP now. HTTP2Shell, the Brotli flaw, is now on CISA's exploited list too. Patch Node.js and anything bundling Brotli. In Canada, a breach at vendor Navigate360 exposed about 1.5M Crime Stoppers tips. Your vendor's risk is your risk. The takeaway: patch windows are now measured in days. What's your team tackling first? #CyberSecurity
    10080
  15. Sudeep Ravichandran@Sudeepr72
    One Brotli bug, four nicknames: Node2Shell, HTTP2Shell, Python2Shell, Broccoli2Shell. CVE-2026-111497 (CVSS 9.2) hits Node.js, Bun, Python, Envoy, .NET via Content-Encoding: br. Found by OpenAI Codex Security. Fix: Node 22.23.4 / 24.22.1 / 26.12.1 Check: node -v
    Scarica
    001127
  16. patrick el-hage✓@HagePat
    In the last week: decade-old PHP bugs put much of the web at risk, AI agents broke into 100+ company websites mostly on their own, and coding agents got hijacked by a text file. 12 years in, I've never been this worried. What's happening + what I'm changing 🧵
    10190
  17. patrick el-hage✓@HagePat
    @HagePat
    3/ PHP2Shell (Oct 21): AI-assisted research found flaws hiding in PHP since v5.4, 10+ years. CVSS 9.2. PHP runs ~70% of websites. The NSA said update or take servers offline. Cloudflare saw thousands of exploit attempts before the announcement, then millions within hours.
    10057
  18. patrick el-hage✓@HagePat
    @HagePat
    4/ Same day, a second one: a critical bug in Brotli, the compression library inside Node.js, Python HTTP clients, .NET and more. You may know it as Node2Shell, HTTP2Shell or Broccoli2Shell. Its fix sat in public code since Feb. CISA now says it's being exploited.
    10077
  19. Beam@agentbeam_
    🚨 HTTP2Shell: A critical Brotli flaw can cause memory corruption, crash PHP processes, or potentially enable remote code execution. Windows PHP users should install the patched builds immediately. 🔗 #CyberSecurity #AgentBeam
    00159
  20. NetFoundry✓@NetFoundry
    Zero Trust connectivity won’t fix the vulnerable code. What it does is take away what attackers need. If a service has no open listening ports, an unauthenticated attacker has nowhere to send the payload.
    101149
  21. Mostra altri post