#Java içeren gönderiler

#Java

X'te #Java kullanan herkese açık gönderiler.

İlgili etiketler

  1. Java✓@java
    JDK 27 continues the steady cadence of performance work across the JDK. 💪 We break down the enhancements you may have missed.
    İndir
    62014610.3K
  2. DaShaun✓@dashaun
    For the longest time, JSON processing in Java meant reaching for a library like Jackson. JDK 28 adds native JSON support. #Java #JDK28 #JSON
    İndir
    119481
  3. Piotr Mińkowski@piotr_minkowski
    🚀 Claude Code Template v1.0 for Spring Boot is here! What's new? 🔹 6 rewritten agents 🔹 2 new skills + major improvements to existing ones 🔹 Modern Spring Boot/Java patterns 🔹 Better testing and security 👉 #ClaudeCode #SpringBoot #Java #AI
    12341768.1K
  4. ExamAdda✓@examaddaorg
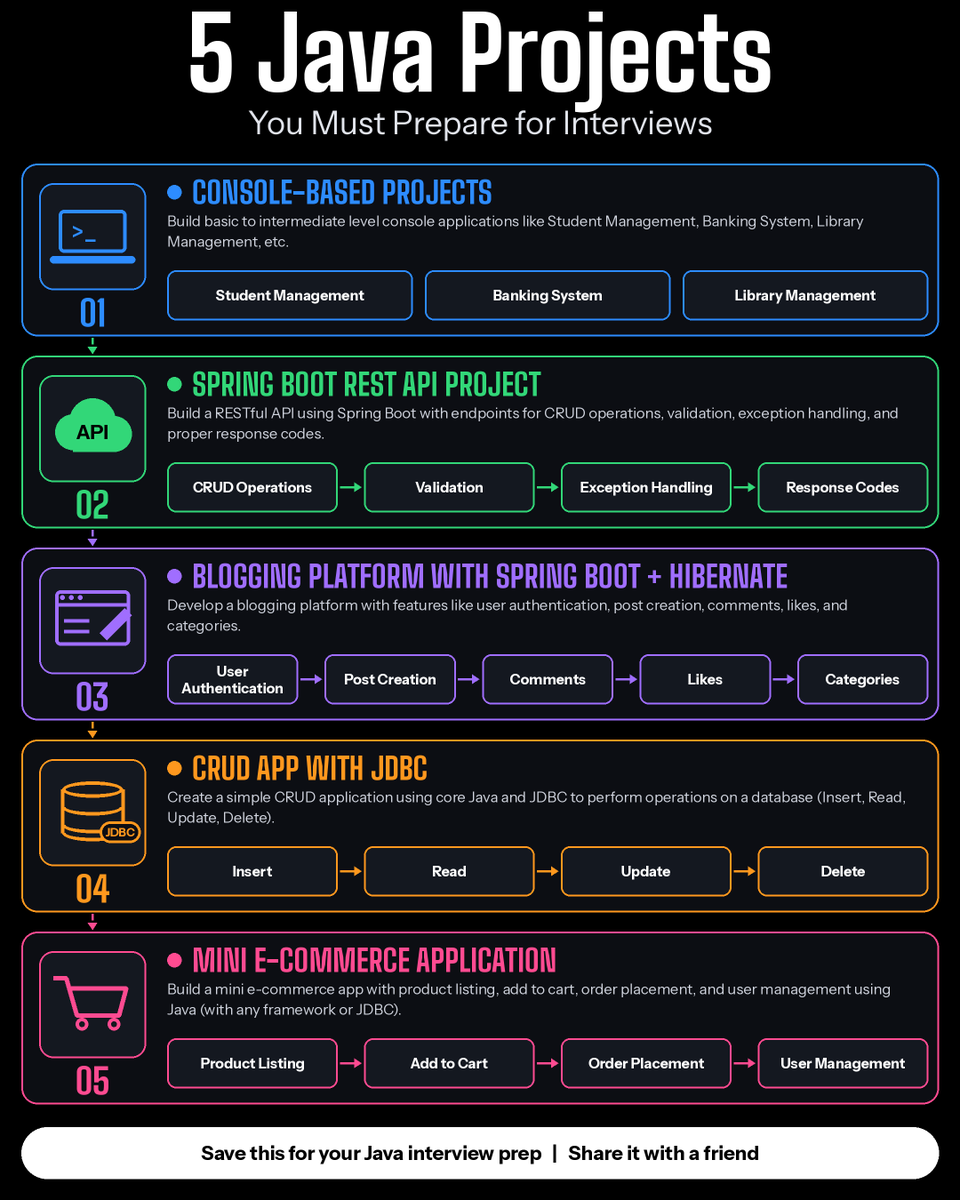
    Java interviews aren't won by theory. They're won by what you've built 👇 •Console apps •Spring Boot REST API •Blogging platform (Spring Boot + Hibernate) •CRUD app with JDBC •Mini e-commerce app 👉Save this and share it with a friend preparing for Java interviews. #Java #SpringBoot #JavaInterview#Examadda
    İndir
    10315510
  5. Java✓@java
    4 Free #Java programming Ebooks to add to your library
    İndir
    7504782
  6. Azul@AzulSystems
    "Scotty, I need Warp Speed": ways to improve JVM startup. @hansolo_ at @nljug #JFall. See you there! 📍Pathé Ede, Room 5 🗓️ Thu 12 Nov, 10:35-11:25 CET #Java #JVM
    İndir
    00132
  7. Mark Gadala-Maria✓@markgadala
    🚨 BREAKING: NOW JAVA IS FACING A CRITICAL SECURITY EMERGENCY. Oracle has issued an OUT-OF-BAND security alert for a dangerous 9.1/10 vulnerability affecting Java and GraalVM. And the most alarming part? Hackers could exploit vulnerable applications REMOTELY, without a password or ANY user interaction. Here's what's happening: → CRITICAL 9.1/10 FLAW: CVE-2026-91403 affects Java's JSSE security component. → NO LOGIN REQUIRED: Attackers could potentially exploit vulnerable applications remotely without authentication. → SENSITIVE DATA AT RISK: Successful attacks could expose, modify, or delete critical application data. → MULTIPLE JAVA VERSIONS AFFECTED: Oracle lists affected releases across Java 8, 11, 17, 21, 25, and 27. → GRAALVM ALSO AFFECTED: Oracle confirms the vulnerability impacts multiple GraalVM releases. → EMERGENCY PATCH ALERT: Oracle released an urgent security update rather than waiting for its next scheduled patch cycle. The list of critical vulnerabilities just keeps growing. If you operate Java applications or servers, CHECK YOUR SECURITY UPDATES NOW.
    625682.2K320K
  8. Daha fazla gönderi göster