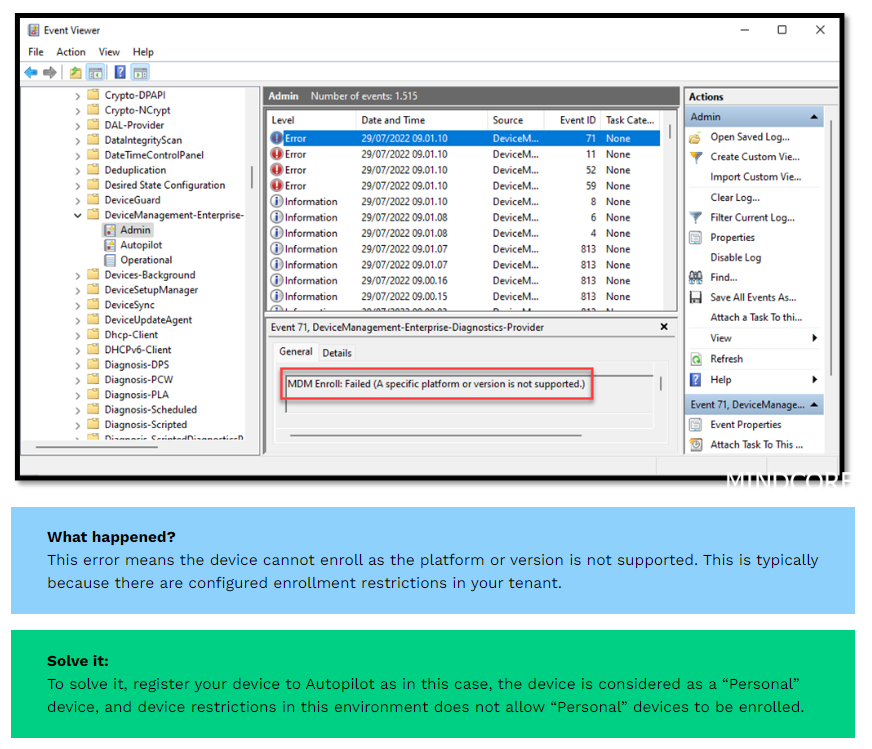
Just updated my site with Intune errors and solutions. You might find some of it useful (66.000 views) 😀 If you have any good errors, send it to me and I'll reference you and add it here.
#MSIntune#Errors#Solutions#Community
The key to #Excel errors is to know what they stand for and how they can be solved quickly.
We have done our homework and compiled the 10 most common #errors in this #CheatSheet! 🤓
👉 If you want to know more solutions to each of these:
running a company nowadays feels kinda dystopian
my team is 50+ people in 12 countries, but i talk to my agents more than my human teammates
- voice note to grokbot
- mattpocock/skills /grill-me so the agent interrogates the idea before anything gets built
- spec drops into linear through the linear mcp
- exa + firecrawl agent reads every competitor site, pricing page and changelog
- to find ideas and trends
- apify pulls g2, reddit and app store reviews
- prompt: "find the 10 complaints that show up most and quote the users"
- context7 so the agent reads the latest docs before it touches any api
the design
- claude code + paper mcp
- 4 versions of every screen before a single line of code
- pick pieces from 2, it merges them. diverge then converge
- frontend-design skill from anthropic/skills + our own design system skill
- cleanshot screenshots of any ui i like go straight in with "make it feel like this"
the build
- pingdotgg/t3code as the control surface for every agent, from my phone too
- stablyai/orca runs a fleet of agents in parallel, each in its own git worktree
- graphify maps the whole codebase into a knowledge graph so agents navigate instead of guess
- headroom compresses tool outputs before they hit the model, so tokens go 20-95% further
- lsp plugins so the agent sees types and errors like an ide does
- security guidance hook flags risky edits before they land
- supabase mcp for the database, stripe for billing
- github mcp opens the pr, vercel spins up a preview
- loops run overnight, i check what shipped over coffee
the user testing
- lightpanda as the headless browser, way lighter than chromium so you can run hundreds at once
- agents click every flow on the preview like a first-time user
- one persona is impatient, one is confused, one is on a phone
- playwright + chrome devtools mcp for regression tests
the bugs
- sentry mcp catches the error
- agent reads the stack trace and opens a fix pr in under 10 minutes
- human just approves
the data
- posthog mcp cron at 7am on yesterday's funnel
- any step that drops more than 10%, the agent watches 20 session replays and tells me why
- stripe mcp pulls every cancellation reason into one doc every monday
the agents' tools
- orgo so every agent gets its own computer
- agentmail so every agent gets its own inbox
- agentphone so i can call them from the car
- composio connect-apps for every other connector
- akitaonrails/ai-memory, a git-backed markdown wiki so they remember what we decided last week
the skills
- wshobson/agents so skills work across claude code, codex and opencode
- my writing voice
- our design system
- how we write specs
- skill creator so the agents write new skills themselves
some helpful tricks
- one agent per platform. the x agent never touches email
- cheap model for triage, opus for anything that ships
- every output gets scored 1-10 by an llm judge. under 8 goes back
- every agent writes a 5-line log at night so i can read the whole company in 2 minutes
- every agent mistake becomes a new skill, so it only happens once
the team
- humans get version 5, not my voice note which they are happy about lol
- their job is creative feedback, relationships and telling the agents what they got wrong
a human pm reviews the funnel once a week. this reviews it every morning
running a company is now voice notes and inference
🔥Do you know the difference between #exceptions & #errors in Dart? In this new video of the #Dart#Crash#Course, we will have a look at the difference between the two and how to handle them WATCH 🚀 =>
I served as a poll watcher today and noticed something that struck me as rather odd.
Throughout the evening, I carefully kept a handwritten tally of every voter who cast a ballot. Each time I compared my count with the total displayed on the voting machine, the machine consistently showed one or two more votes than I had recorded.
To eliminate the possibility of an error in my counting, I repeatedly reset my handwritten tally to match the machine's displayed total and began counting again from that point forward. Yet, at the next comparison, the machine was once again ahead by one or two votes.
This happened repeatedly throughout the evening.
I'm not suggesting I know the reason for the discrepancies, but the consistency certainly caught my attention. I would be interested in understanding why the machine totals repeatedly differed from my firsthand count of voters.
🚨 VERY IMPORTANT: DISTURBING REPORT FROM SAN DIEGO BALLOT DROP-OFF LOCATION
An eyewitness reports that the ballot drop box at the library on Voltaire Street was so full that voters were being turned away.
According to the witness, ballots were on the ground as election workers slowly emptied the overflowing box, filling TWO bags.
The witness says one worker then loaded the bags into an unmarked minivan.
When she began recording, an election worker allegedly told her to DELETE THE VIDEO.
She refused.
🚨 VERY IMPORTANT: DISTURBING REPORT FROM SAN DIEGO BALLOT DROP-OFF LOCATION
An eyewitness reports that the ballot drop box at the library on Voltaire Street was so full that voters were being turned away.
According to the witness, ballots were on the ground as election workers slowly emptied the overflowing box, filling TWO bags.
The witness says one worker then loaded the bags into an unmarked minivan.
When she began recording, an election worker allegedly told her to DELETE THE VIDEO.
She refused.
🚨 SOMEONE LEAKED THE PROMPT THAT MAKES CLAUDE CODE CREATE ITS OWN SKILLS AND WORK BETTER EVERY DAY WITHOUT YOU TOUCHING ANYTHING
No programming. Just paste. A single prompt does it all:
Time needed: 2 minutes
Actions: copy and paste into Claude Code
The mistake 90% of people make with Claude: explaining the same thing to it every day. The same tone, the same steps, the same corrections. And the next day it starts from scratch again.
→ Detects what you repeat: reviews your project and asks you what tasks you do every week
→ Creates a skill for each one: instructions, templates, and examples that Claude loads only when it needs them
→ Tests them before giving them to you: runs each skill with a real case and fixes it if it fails
→ Learns from your corrections: every time you correct something, it updates the skill so it doesn't repeat the error
→ Zero code: you tell it what you do and Claude builds its own library of skills
Before, this meant writing manuals, templates, and processes for weeks.
Now it's just Ctrl+V.
Save it before they delete it 🔖
Follow @tomcruise824458 for more...
Attacks will accelerate from here on - We are there: Six months ago I said Mythos like capability will be widely available. It's happening. A critical vulnerability, a social engineering attack that looks innocuous, or daisy chaining publicly available vulnerabilities and conducting a sniper strike is all being witnessed in the wild. Incident responders have never been busier.
Some key points:
- attacks are not becoming more sophisticated, it's the same attacks, faster and by a lot more people.
- attack path discovery which took trial and error and multiple attempts is now trivial, open source LLMs are here to help
- you are as secure as your supply chain, insecure down or upstream players who have access to your infrastructure could be the next attack path, marketplaces and supply chain is an easier vector
The increase in activity is a result of more people becoming better at hacking due to the ease of being able to attack. Had not contemplated that in my calculus.
Please:
1. Test your infrastructure for accessible vulnerabilities and misconfigurations
2. Fix your code and demand your vendors do.
3. Old infra, or insecure infra at the perimeter needs to be updated first
4. New AI tools, especially coding need a security framework. Your developers will do more with code, new skills, and more automation. Don't forget the coding models have trained on human code.
Stay safe this Halloween :)