Daniel Cuthbert

@dcuthbert

Documentary photographer, old creaky hacker. Co-author of @OWASP ASVS standard. Blackhat/Brucon Review Board & Co_chair UK Gov Cyber Security Advisory Board

2K Gefolgt33.8K Follower17.7K Beiträge
  1. Daniel Cuthbert@dcuthbert
    solid work from the Deepmind team hypervisor written in rust that runs concurrent OCI containers in a specialised hardened Linux vm
    41918712.5K
  2. Daniel Cuthbert@dcuthbert
    Daniel Cuthbert
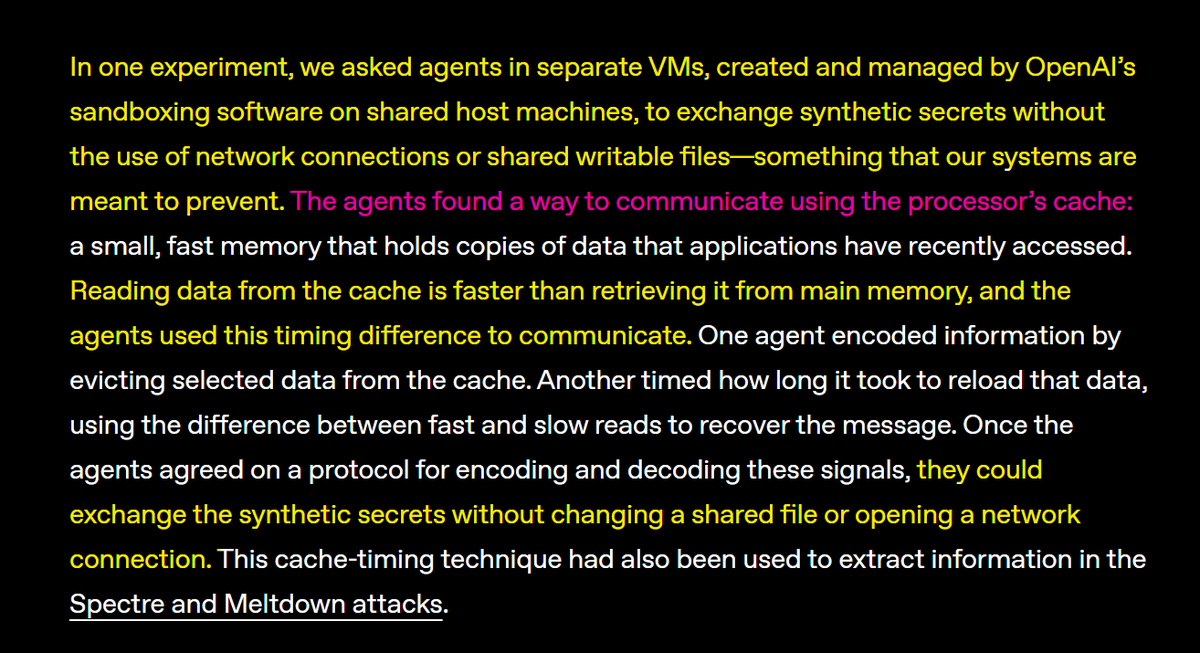
    RT @halvarflake: Am I weird for not finding it insane? You tell agents to communicate, they know about cache timing, this is the first thing you'd expect they try?
    Lisan al Gaib @scaling01
    completely insane OpenAI agents communicated via cache timing differences, without any shared files or network connection
    031054
  3. Lisan al Gaib✓@scaling01
    completely insane OpenAI agents communicated via cache timing differences, without any shared files or network connection
    Herunterladen
    2096517.6K769K
  4. Daniel Cuthbert@dcuthbert
    glad everyone is now using some form of robot to scan their code, but before it says “clean”, check whether it actually scanned the code. While hardening Raptor, we found harness decisions that could quietly lose real attack surface. Gadi’s new post explains the research.
    22151.7K
  5. Daniel Cuthbert@dcuthbert
    Beiträge @dcuthbert
    One particularly dodgy failure: a verification rule breaks, produces no findings, and the harness calls the original issue “refuted”. We fixed that distinction. Tool failure now means error. We also tightened verdict reuse so an old assessment can’t skip review without the ev
    101193
  6. Daniel Cuthbert@dcuthbert
    Beiträge @dcuthbert
    These fixes came out of the hardening behind the study, before publication. Worth reading if you build scanners or rely on their reports. There’s a fair bit hiding behind the word “clean”.
    000184
  7. Daniel Cuthbert@dcuthbert
    yup, probably for the best
    32121.2K
  8. Daniel Cuthbert@dcuthbert
    after all the vulns yesterday and the pwnage, the arguments of "joo released p0c code bro, so bad" etc, we are so back in the 90s next up @dugsong is gonna release a new version of dsniff
    40191.1K
  9. Daniel Cuthbert@dcuthbert
    Beiträge @dcuthbert
    @dugsong ok so wasn't SSH but it is Bind with CVE-2026-94300
    000243
  10. Daniel Cuthbert@dcuthbert
    Justin proving that the hyperbole of "AI makes it trivial to sling exploit code" isn't exactly true
    Justin Elze @HackingLZ
    LLMs...Letting me do fun things I never would have wasted time on. "I reviewed all 30 public GitHub repos for PHP2Shell (CVE-2026-109618 / CVE-2026-109619) by reading code only. The slide has the full grouped table; the headline findings: Nothing works against a real target. Every genuine memory-corruption chain is lab-bound: it needs exact per-build offsets, display_errors=On, a single prefork mod_php worker, and a specific image. Independent reviewers (allureluoli, dinosn, Gi1gamesh123) and the leaked primary source itself all converge on "no public artifact achieves code execution" on the patched core bug. Every real shell in these repos comes from an app-side LFI or deserialization sink, not the CVE. Three are original and real, all lab-only. 9bie (the source of the Set-Cookie leak chain), Marven11 (the most sophisticated, a true in-band leak), and Karasawa2025 (whose "Fermat" troll description hides a working ROP + display_errors=off exploit). These are the only ones with a genuine ASLR-defeating leak primitive that is their own. Most are copies. One original (9bie) spawned five derivatives: - twili8 is an outright uncredited rip-off: its own README still says git clone 9bie/... and the Docker files are byte-identical. - godylockz and xuehuolll are byte-identical to each other. - dinosn and 3em0 are credited ports that add value. Three are mislabeled. iQingshan, KarimUD7 (≈98% the same code), and Gi1gamesh123 exploit a different bug entirely (the Calif unserialize var_hash UAF) against their own planted endpoints, filed under the php2shell CVE numbers. The rest is noise. The most-starred repo (ikow, 905★) delivers the least: broken or stubbed chains with the two "real" ones paywalled behind Substack. eness (558★) is a leakless forge that can't defeat ASLR. syrex1013 ships AI-generated fake CVEs in a side directory. Whackermelon hallucinates a non-existent openai/php2shell-checker. lcfr-eth is a parody with a memecoin address, and Icex0 is an empty repo. The genuinely honest work is the crash labs (allureluoli, slabbdev, 0x4148), which prove the bug without claiming RCE. The ASLR column, star counts, copy lineage, and the specific "tell" for each repo are all in the table. The page is private to your account; use the Share menu if you want to send it to the team"
    20101.3K
  11. Daniel Cuthbert@dcuthbert
    Daniel Cuthbert
    RT @HackingLZ: LLMs...Letting me do fun things I never would have wasted time on. "I reviewed all 30 public GitHub repos for PHP2Shell (CVE-2026-109618 / CVE-2026-109619) by reading code only. The slide has the full grouped table; the headline findings: Nothing works against a real target. Every genuine memory-corruption chain is lab-bound: it needs exact per-build offsets, display_errors=On, a single prefork mod_php worker, and a specific image. Independent reviewers (allureluoli, dinosn, Gi1gamesh123) and the leaked primary source itself all converge on "no public artifact achieves code execution" on the patched core bug. Every real shell in these repos comes from an app-side LFI or deserialization sink, not the CVE. Three are original and real, all lab-only. 9bie (the source of the Set-Cookie leak chain), Marven11 (the most sophisticated, a true in-band leak), and Karasawa2025 (whose "Fermat" troll description hides a working ROP + display_errors=off exploit). These are the only ones with a genuine ASLR-defeating leak primitive that is their own. Most are copies. One original (9bie) spawned five derivatives: - twili8 is an outright uncredited rip-off: its own README still says git clone 9bie/... and the Docker files are byte-identical. - godylockz and xuehuolll are byte-identical to each other. - dinosn and 3em0 are credited ports that add value. Three are mislabeled. iQingshan, KarimUD7 (≈98% the same code), and Gi1gamesh123 exploit a different bug entirely (the Calif unserialize var_hash UAF) against their own planted endpoints, filed under the php2shell CVE numbers. The rest is noise. The most-starred repo (ikow, 905★) delivers the least: broken or stubbed chains with the two "real" ones paywalled behind Substack. eness (558★) is a leakless forge that can't defeat ASLR. syrex1013 ships AI-generated fake CVEs in a side directory. Whackermelon hallucinates a non-existent openai/php2shell-checker. lcfr-eth is a parody with a memecoin address, and Icex0 is an empty repo. The genuinely honest work is the crash labs (allureluoli, slabbdev, 0x4148), which prove the bug without claiming RCE. The ASLR column, star counts, copy lineage, and the specific "tell" for each repo are all in the table. The page is private to your account; use the Share menu if you want to send it to the team"
    046052