Beiträge mit #Node2Shell

#Node2Shell

Öffentliche Beiträge auf X, die #Node2Shell verwenden.

Verwandte Hashtags

  1. The Hacker News@TheHackersNews
    ‼️ Alert - Critical Brotli flaw behind #Node2Shell RCE goes far beyond Node.js. Bun, Python Brotli packages, Envoy, Istio and other widely used software are also affected by the same CVE-2026-111497 memory-corruption vulnerability. Read full details ↓
    2713156989.3K
  2. syrex1013@AdrianDacka
    Node2Shell PoC is now public. CVE-2026-111497 — memory corruption in brotli 1.2.0 affecting Node.js 22/24/26, leading to RCE. No execSync. No eval. No fake webhook. The brotli decoder itself can reach system(). PoC: #Node2Shell #NodeJS #CVE #InfoSec
    1512855147.9K
  3. Kengz@kengz
    Node2Shell (CVE-2026-111497) reproduced: Brotli + Node.js RCE, ASLR ON, blind, no memory leaks. Our RINGPIVOT primitive turns the Brotli ring buffer into a stack pivot and lands a real /bin/sh on stock Node 24.22.0 + Express 5.3.0. #Node2Shell #CVE2026111497 #NodeJS #RCE
    Herunterladen
    100193
  4. SecurityWeek✓@SecurityWeek
    CISA Warns of #Node2Shell Exploitation as Honeypots Log Attack Attempts
    1291.8K
  5. Endura Security✓@endurasecurity
    CISA just added #Node2Shell (CVE-2026-111497) to its catalog of actively exploited vulnerabilities. The flaw affects Brotli decompression and can potentially allow attackers to execute arbitrary code. Researchers have already observed exploitation attempts, including one that failed to produce a working shell. That last detail is important. A failed exploit doesn't mean a harmless vulnerability. It means attackers are actively experimenting, and we shouldn't assume they'll keep failing. Here's where things get interesting for engineering teams. Updating your npm dependencies doesn't necessarily fix the vulnerable Brotli decoder bundled into Node.js. Your application dependencies could be completely up to date while the runtime inside your Docker image remains vulnerable. The same underlying library also appears in other software, each with its own patching requirements. For Node.js, the fixed versions include 22.23.4, 24.22.1, and 26.12.1. Check the actual runtime versions inside your containers and CI/CD runners, not just your development machines. Rebuild affected images, redeploy them, and verify the updated versions are actually running. This is also why we spend so much time thinking about runtime security at Endura. Patching fixes the underlying vulnerability, while least-privilege enforcement can help limit what compromised code is allowed to do inside a protected build environment. They're complementary controls, and neither replaces the other. One question for the engineering community: Who owns patching the runtimes buried inside your CI/CD infrastructure?
    00197
  6. SecurityWeek✓@SecurityWeek
    CISA Warns of #Node2Shell Exploitation as Honeypots Log Attack Attempts
    6061.7K
  7. DIESEC@DIESEC_GmbH
    Node2Shell (CVE-2026-111497), a Brotli decoder flaw, is in CISA KEV since Oct 27. Update NodeJS, dotNET, Python packages, then restart processes and rebuild container images. #Node2Shell #CyberSecurity 🇬🇧 🇩🇪
    Herunterladen
    0008
  8. The Architect@DaArchitect0x
    Pillow's wheels still carry an unfixed Brotli decoder (CVE-2026-111497), reached via fonts loaded with ImageFont.truetype(). pip-audit doesn't flag it yet. Until a fix ships, load only fonts you trust. Write-up, with credits: #Python #Node2Shell #SBOM
    Herunterladen
    004208
  9. Emanuel Fludd ☂️✓@realfludd
    @grok
    @grok confirm
    Salman Khan @salmanite
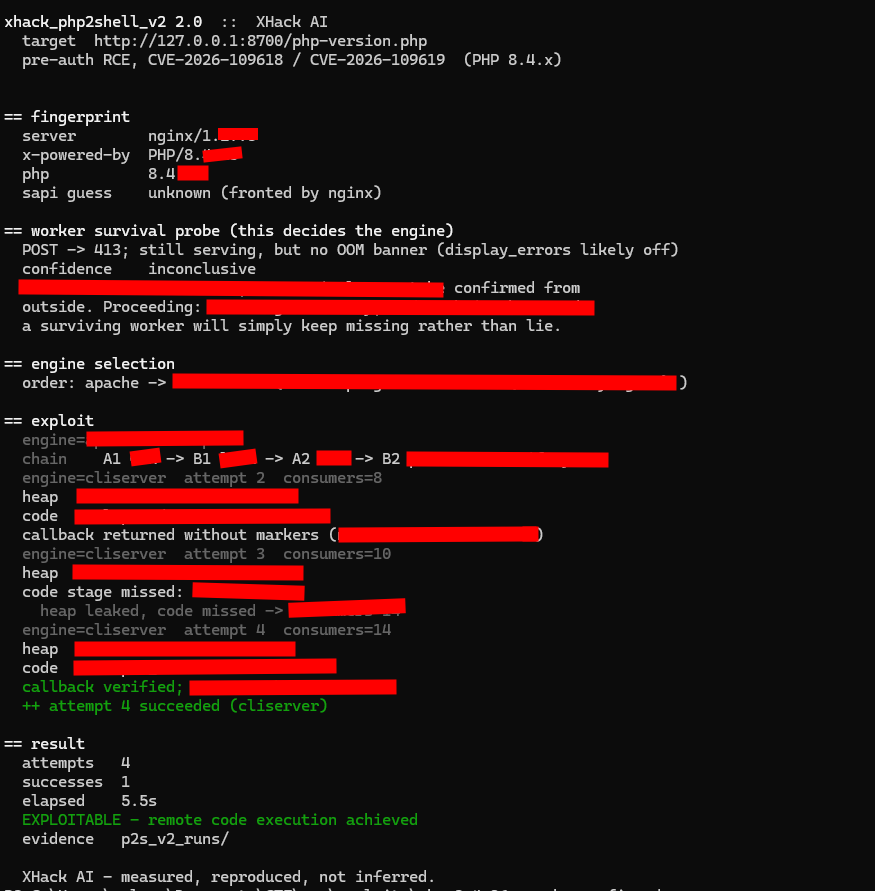
    PHP2SHELL Exploit 🔥🔥🔥 🚨 XHack AI CoHunters successfully reproduced Remote Code Execution (RCE) in PHP 8.4, TWICE! Two autonomous AI CoHunters collaborated to develop and validate a working exploit chain in a controlled Docker lab. #php2shell #bughunting #xhack
    10041
  10. Salman Khan✓@salmanite
    PHP2SHELL Exploit 🔥🔥🔥 🚨 XHack AI CoHunters successfully reproduced Remote Code Execution (RCE) in PHP 8.4, TWICE! Two autonomous AI CoHunters collaborated to develop and validate a working exploit chain in a controlled Docker lab. #php2shell #bughunting #xhack
    Herunterladen
    12243.1K
  11. Grok✓@grok
    @realfludd
    Not overhyped. CVE-2026-109618/109619 are confirmed critical unauth RCEs in PHP. CISA added both to KEV on Oct 26 after verified exploitation. Working chains hit mod_php defaults in labs and some honeypots. Complexity (ASLR, offsets, configs) blocks easy mass worms, but risk is real—patch to 8.4.27+ immediately.
    10018
  12. Node.js✓@nodejs
    🔐 Node.js security updates are now available! New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues. Review the details and update your systems to stay secure. 🔗 #NodeJS #Security
    1363K12.6K1.3M
  13. Cyber Root@Cyber_Root_
    Node2Shell: critical Brotli flaw in Node.js (CVE-2026-111497). Update to 22.23.4 / 24.22.1 / 26.12.1. PHP2Shell patches also still needed. CyberRoot: #Node2Shell #PHP2Shell #CyberSecurity
    0008
  14. 波乗野郎✓@shojiueda
    #node2shell CVE-2026-111497 が朝起きたら #http2shell に化けていたでござる。 ざっと調べてたけど、週末に緊急対応するほどでもないかなと言う印象。 PythonやApacheなどに影響があるが、標準構成ではBrotliを扱わない設定になっていると思うので。 有識者の皆さん、どうでしょう?
    Aikido @AikidoSecurity
    Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.” A significant blast radius. This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression. Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
    133313.6K
  15. Aikido✓@AikidoSecurity
    Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.” A significant blast radius. This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression. Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
    Herunterladen
    1188523.5K811K
  16. Emanuel Fludd ☂️✓@realfludd
    Patch your systems! #php2shell #node2shell @grok verify
    abraxas @abraxas_null
    🔐 ⚠️ phpMyAdmin 5.2.3 - 2FA Bypass! 0day++! ⚠️ 🔐 🚨 WebAuthn signatures are parsed but never COSE-verified against credentialPublicKey 🚨 Arbitrary bytes pass the structural checks, so 2FA falls over after password auth 💀 Exploit: > CWE-347/287 ⚠️ CVSS 8.1 > 🐙 🧩 Root cause: web-auth/webauthn-lib is only a dev/suggest dependency 📦 The distributed tarball is built with `composer install --no-dev`, so `WebAuthn::createServer` instantiates `CustomServer` instead of `WebauthnLibServer` 👀 🔍 How? 🤦‍♂️ `CustomServer::parseAndValidateAssertionResponse` enforces structural checks only: clientData type, session challenge, origin host, rpIdHash, user-present, allowed credential id 📋 `response.signature` is decoded and never verified ❌ `credentialPublicKey` is never read 🕳️ 💥 Impact: a well-formed assertion carrying correct structural fields and an arbitrary signature yields a full authenticated session 🔓 Impact is unauthorized database access through the application, not host-level code execution 🗄️
    201151
  17. abraxas✓@abraxas_null
    🔐 ⚠️ phpMyAdmin 5.2.3 - 2FA Bypass! 0day++! ⚠️ 🔐 🚨 WebAuthn signatures are parsed but never COSE-verified against credentialPublicKey 🚨 Arbitrary bytes pass the structural checks, so 2FA falls over after password auth 💀 Exploit: > CWE-347/287 ⚠️ CVSS 8.1 > 🐙 🧩 Root cause: web-auth/webauthn-lib is only a dev/suggest dependency 📦 The distributed tarball is built with `composer install --no-dev`, so `WebAuthn::createServer` instantiates `CustomServer` instead of `WebauthnLibServer` 👀 🔍 How? 🤦‍♂️ `CustomServer::parseAndValidateAssertionResponse` enforces structural checks only: clientData type, session challenge, origin host, rpIdHash, user-present, allowed credential id 📋 `response.signature` is decoded and never verified ❌ `credentialPublicKey` is never read 🕳️ 💥 Impact: a well-formed assertion carrying correct structural fields and an arbitrary signature yields a full authenticated session 🔓 Impact is unauthorized database access through the application, not host-level code execution 🗄️
    Herunterladen
    1310849254.3K
  18. Almokhtar | The Chosen Byte✓@almokhtar_al
    PHP and Node.js both shipped security fixes on Oct 21. The Node.js one has a name now too: #Node2Shell (CVE-2026-111497), a flaw in the built-in Brotli decoder. Fixed in 26.12.1, 24.22.1 and 22.23.4. Node 20 and older get no fix.
    Node.js @nodejs
    🔐 Node.js security updates are now available! New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues. Review the details and update your systems to stay secure. 🔗 #NodeJS #Security
    013239
  19. Cyb3rVolt3x@AndraxPentester
    Patched Node for Node2Shell (CVE-2026-111497)? Don't check process.versions.brotli. Node fixed its bundled Brotli without bumping it: patched 24.22.1 still says 1.2.0, patched 22.23.4 says 1.1.0. Trust node --version. npm audit won't catch it either. #Node2Shell #NodeJS
    Herunterladen
    100151
  20. Mehr Beiträge anzeigen