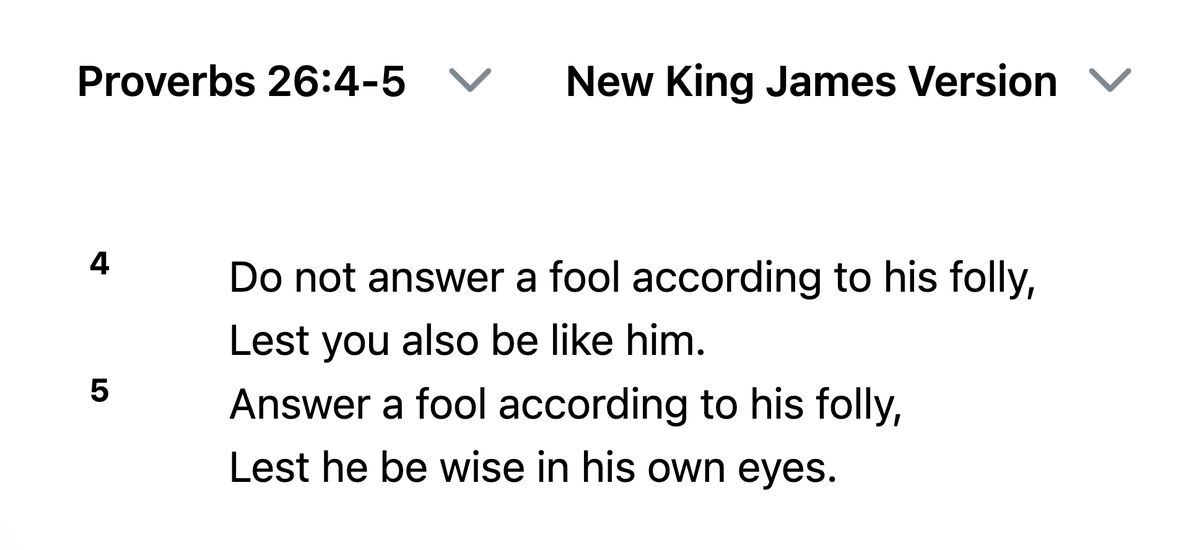
NEW VIDEO ----> Decision models are now a thing....but what exactly are they? Who is Jev? Clef? Bob?
(link in the reply)
111822138.7K
@NetworkChuck
Believer. Beard. Coffee. Tech. Youtube. Check the link in my bio to see my latest video!
zack0x01 @zack0x01_Bug bounty has definitely changed. I used to spend hours analyzing HTTP requests, switching back and forth between Firefox and Burp Suite. Now, I open my terminal, point my AI skills at a target, intercept and analyze HTTP traffic using Burp Suite MCP, and offload heavy tasks to my HackBot running on a VPS. But here’s the thing: AI doesn’t replace your hacking skills. It scales them. The goal is to get really good at manual hacking first, then use AI to automate and scale what you already know. Not the other way around. You don’t start by building a HackBot and expecting it to hack for you when you don’t even understand what it’s doing. Learn to hack first. Automate second. Scale third. Keep hacking! ✌️

NetworkChuck @NetworkChuckNEW VIDEO ----> Decision models are now a thing....but what exactly are they? Who is Jev? Clef? Bob? (link in the reply)
NetworkChuck @NetworkChuckNEW VIDEO ----> Decision models are now a thing....but what exactly are they? Who is Jev? Clef? Bob? (link in the reply)
International Cyber Digest @IntCyberDigest‼️ Researcher Erica Windisch skipped coordinated vulnerability disclosure and published 11 unpatched Tailscale flaws. In her lab, Tailscale SSH race conditions let one hacked device get root on other servers and add a rogue node.


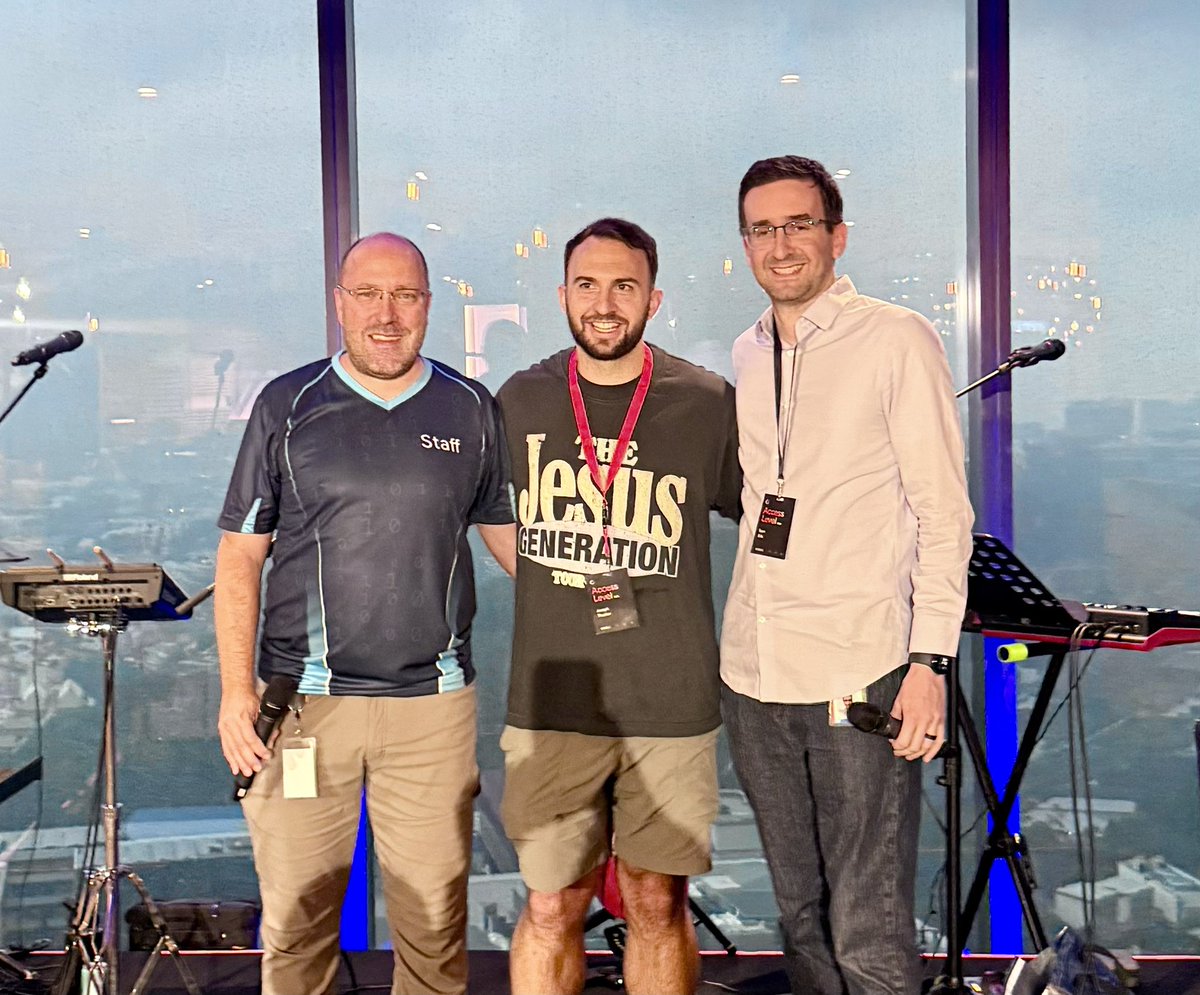
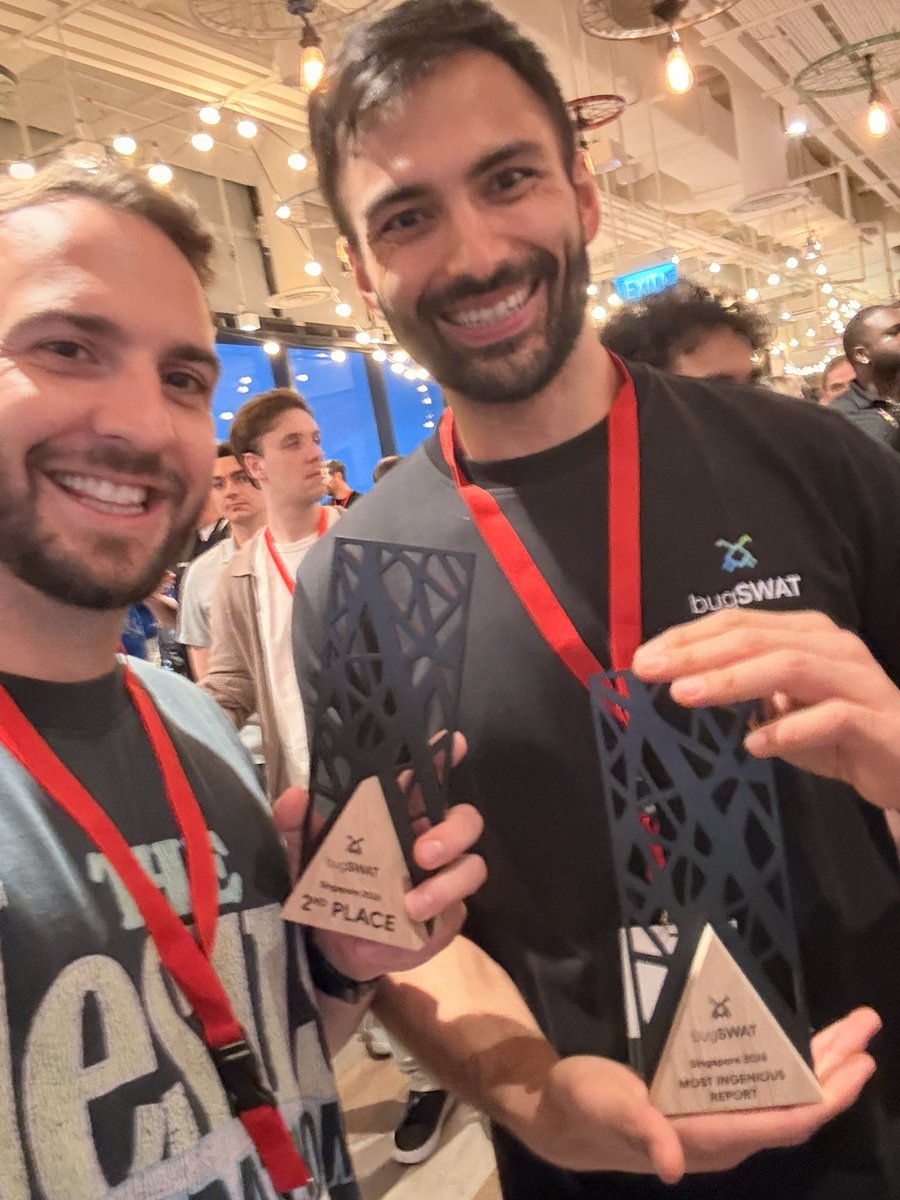
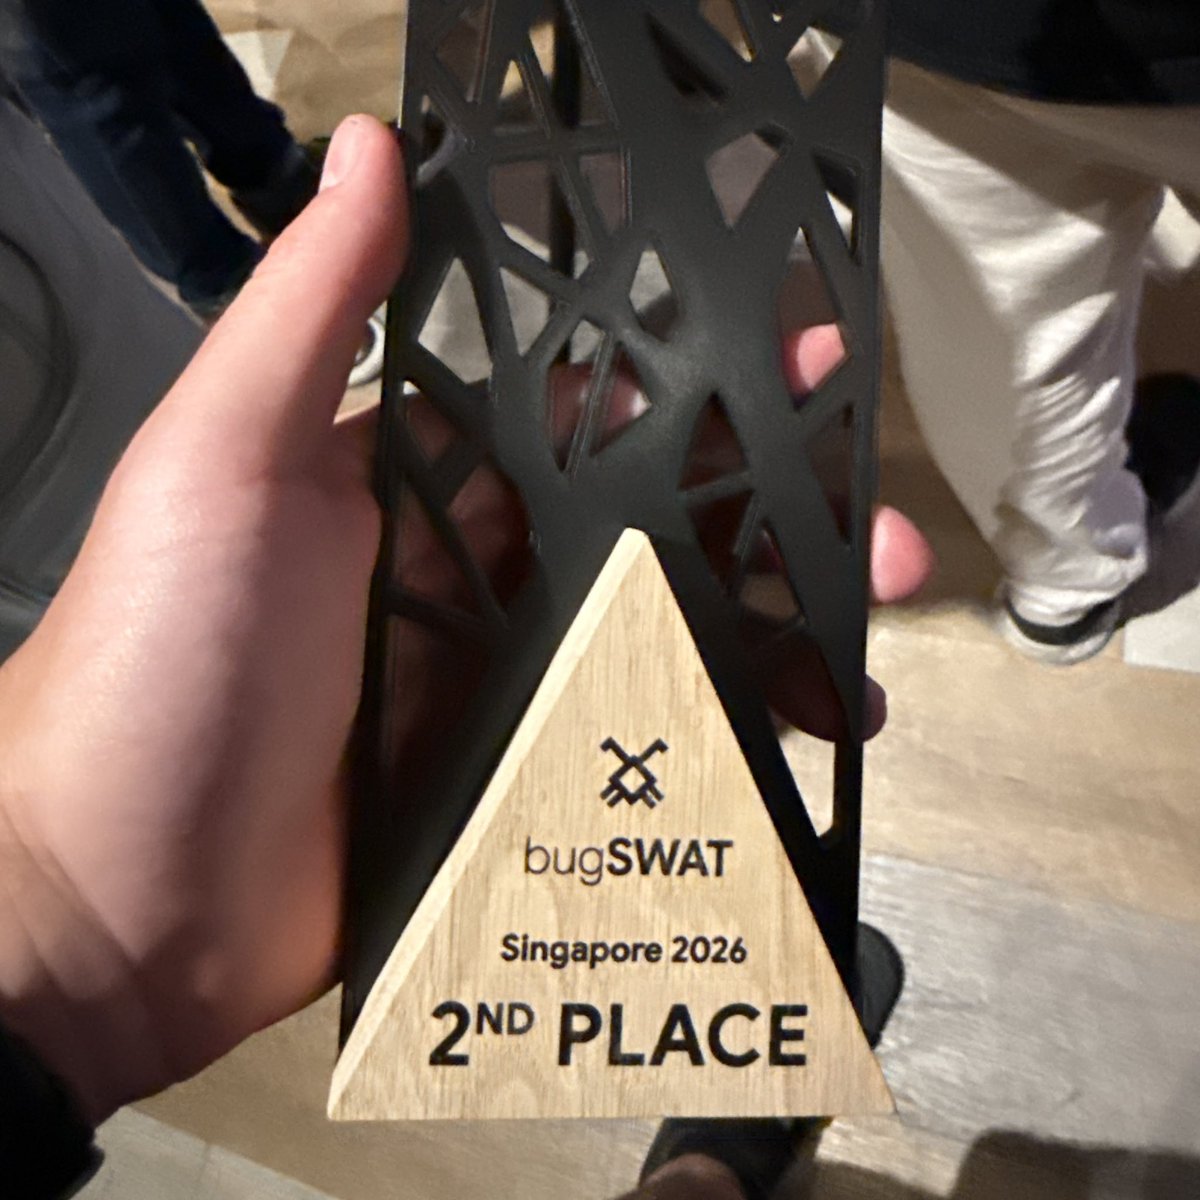
Joseph Thacker @rez0__I got second overall at the Google Bugswat in Singapore!! 🎉☺️ It was a talented group of almost 50 hackers so I am really proud of the findings and thankful to have been invited!


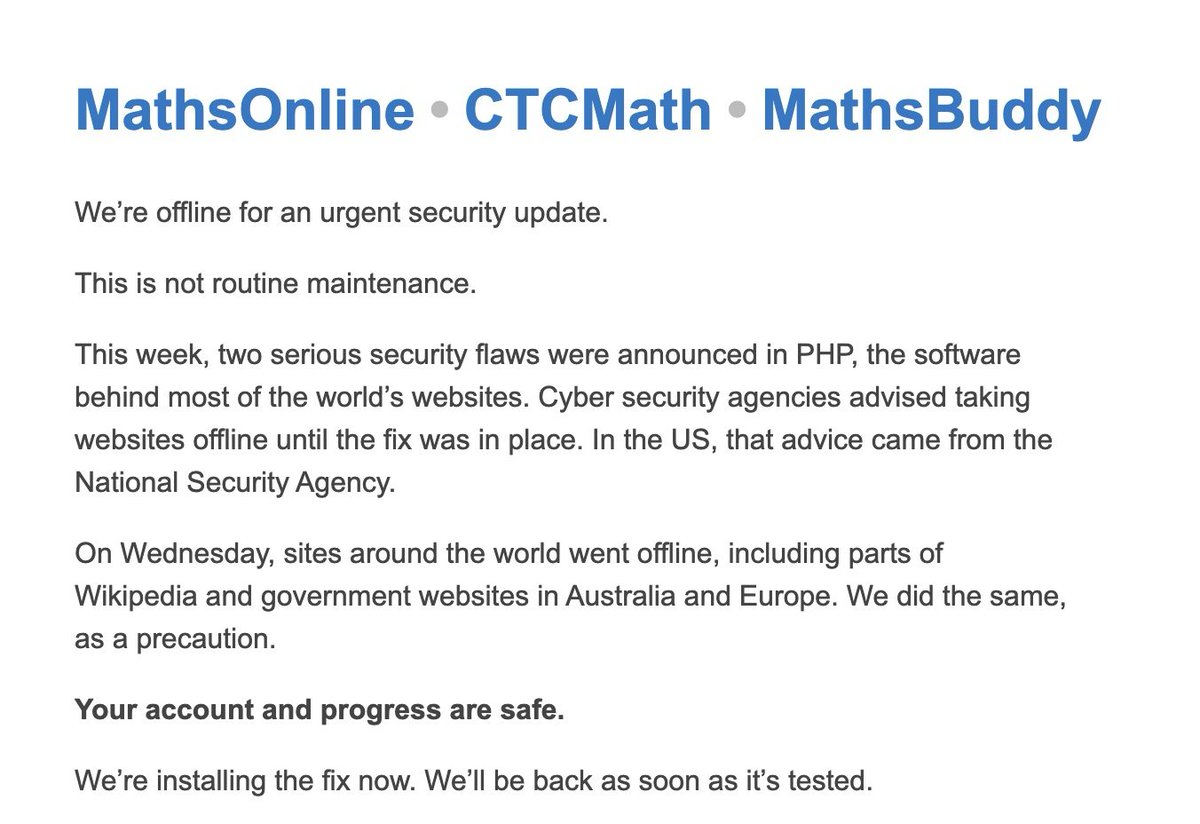
Mudit Gupta @Mudit__Gupta🚨 Nightmare day for cybersecurity Multiple major security incidents, active exploits, supply chain compromises... If you run production systems, start patching NOW. PHP: Two critical unauthenticated RCEs. Attackers already exploiting them. Patch NOW LiteLLM: v1.107.0 on PyPI and Docker is BACKDOORED. Steals cloud, SSH, and AI credentials. Pin 1.106.2. Rotate secrets. eMudhra: A certificate authority's keys were crackable. Update your browsers, systems, and trust stores. Node.js / Next.js / React: Security releases for Brotli RCE, TLS bypasses, and TWO critical Next.js RCEs. TiDB Cloud: PingCAP breached through stolen credentials. Customer information and other sensitive data exfiltrated. Read the attacker's release, fun stuff. Plex2Shell: Weaponized within HOURS of the PoC. Attackers already deploying cryptominers and proxy backdoors. BeyondTrust / Ivanti: Actively exploited zero-days added to CISA's KEV catalog. BeyondTrust attacks linked to a China-nexus campaign. And that's not even the full list. Patch. Audit. Rotate. NOW.