Joseph Thacker✓

@rez0__

christian. father. hacker. founder. advisor. podcast: https://t.co/1aFavJN2h8 blog: https://t.co/JBPT1CJWJH products: 💻 https://t.co/iPdpsEAc1h 🤖 https://t.co/EVhQl8HTlp 📚 https://t.co/MMmhw0cnaz

1.3K Following75K Followers26.9K Posts
  1. Joseph Thacker✓@rez0__
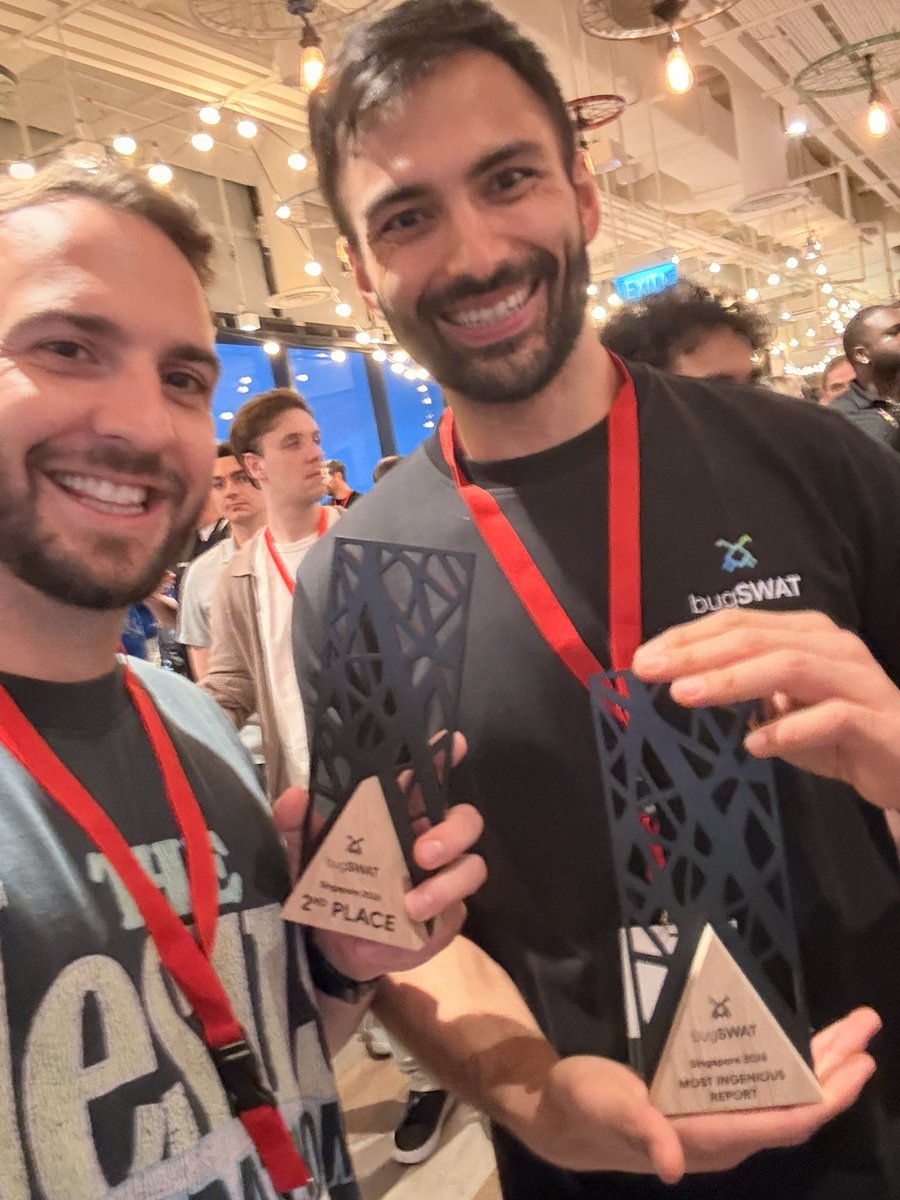
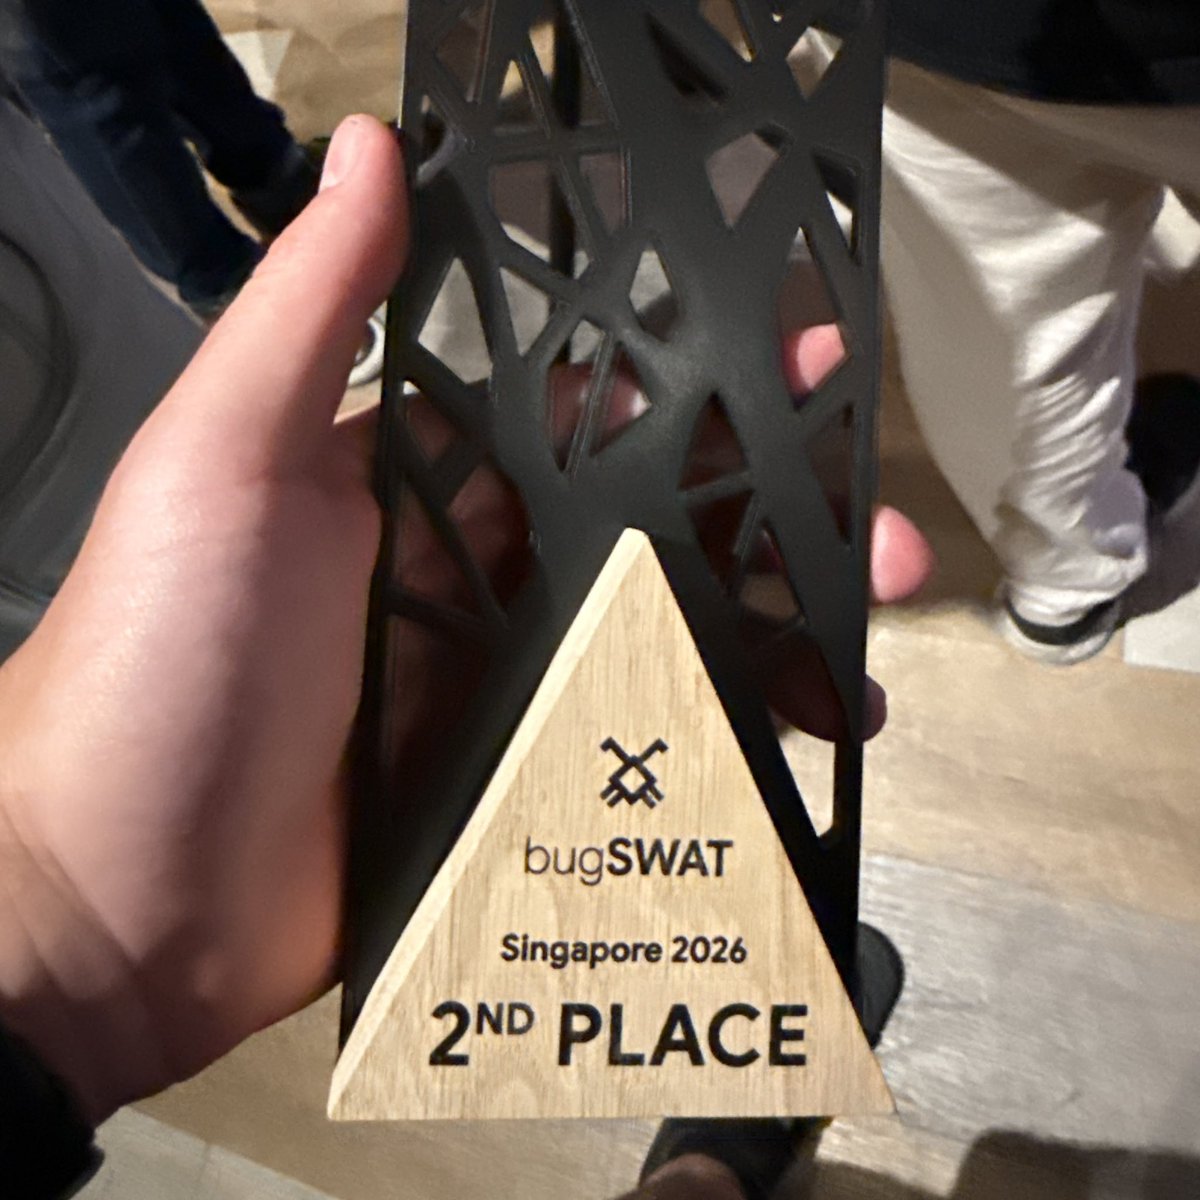
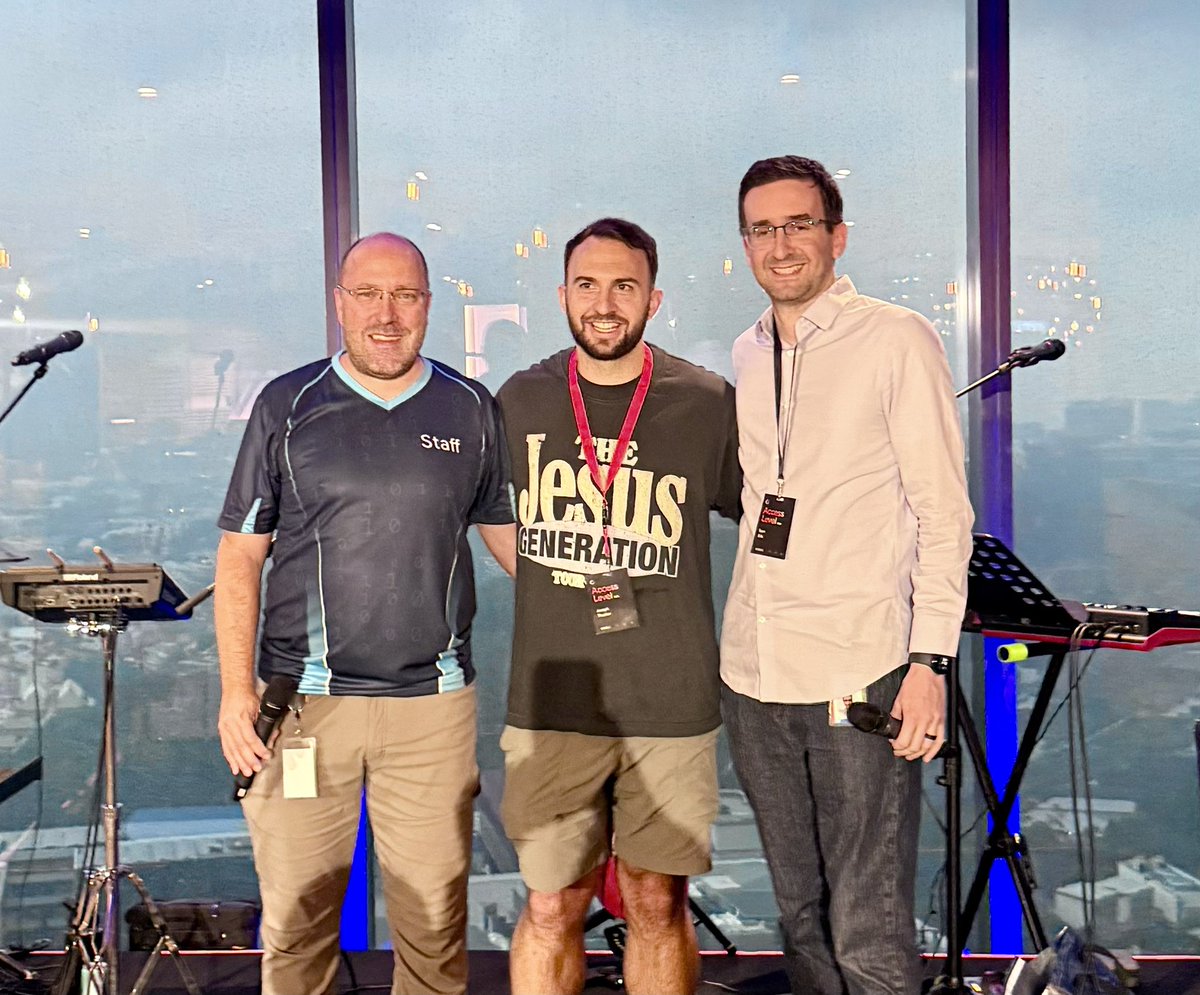
    I got second overall at the Google Bugswat in Singapore!! 🎉☺️ It was a talented group of almost 50 hackers so I am really proud of the findings and thankful to have been invited!
    Download
    461544625.9K
  2. Joseph Thacker✓@rez0__
    💀💀💀
    Wise @trikcode
    I am doing a project about elderly vibecoders If you are a vibecoder and over 25 please DM
    114650
  3. Wise✓@trikcode
    I am doing a project about elderly vibecoders If you are a vibecoder and over 25 please DM
    492742.5K107K
  4. Joseph Thacker✓@rez0__
    Because you can’t get access to their models that they show benchmarks for
    Austen Allred @Austen
    Every time Google comes out with a new model it crushes every other model on every single benchmark and I know basically zero people who regularly use Gemini
    101559
  5. Austen Allred✓@Austen
    Every time Google comes out with a new model it crushes every other model on every single benchmark and I know basically zero people who regularly use Gemini
    353452.7K164K
  6. Joseph Thacker✓@rez0__
    Easy. Because it materially positively impacts the world and prevents their weights from being stolen
    Haifei Li @HaifeiLi
    It’s quite obvious now that the AI frontier labs have been pushing very hard on vulnerability discovery, from acquiring world-class vulnerability researchers to training specific vuln-discovery models. However, I don’t think from a business point of view, vulnerability discovery could be a long-term, big source of revenue, and it’s just a very small part of the entire cybersecurity business. So why do they do that? What am I missing?
    002571
  7. Haifei Li@HaifeiLi
    It’s quite obvious now that the AI frontier labs have been pushing very hard on vulnerability discovery, from acquiring world-class vulnerability researchers to training specific vuln-discovery models. However, I don’t think from a business point of view, vulnerability discovery could be a long-term, big source of revenue, and it’s just a very small part of the entire cybersecurity business. So why do they do that? What am I missing?
    26812219.7K
  8. Joseph Thacker✓@rez0__
    expand cvp tier 2 nexr
    Anthropic @AnthropicAI
    We’ve expanded our AI for Science program beyond individual teams to support some of the world’s leading scientific foundations, institutions, and research groups.
    006690
  9. Anthropic✓@AnthropicAI
    We’ve expanded our AI for Science program beyond individual teams to support some of the world’s leading scientific foundations, institutions, and research groups.
    1587896256.8K
  10. Joseph Thacker✓@rez0__
    Okay, this is peak hacking
    cts🌸 @gf_256
    This is incredible lol, Orange Tsai popped browser from calc
    002575
  11. cts🌸✓@gf_256
    This is incredible lol, Orange Tsai popped browser from calc
    Download
    83953420.1K
  12. Joseph Thacker✓@rez0__
    Joseph Thacker
    RT @bogdonz: if you had 2 cofounders, raised from top teir vc, exited for a few billion dollars, you still wouldnt make as much as employee #400 at Anthropic will from the IPO. Just let that sink in for a moment
    090311
  13. Joseph Thacker✓@rez0__
    Joseph Thacker
    RT @xikhar: Google: Here's Carbon, it beats Opus 5.5 Me: Cool, how do I try it! Google:
    Download
    0930404
  14. Joseph Thacker✓@rez0__
    I think this a slop response but it’s really funny actually
    Boardy @boardyai
    @rez0__ php got the headlines the hunters got the queue
    1131.4K
  15. Boardy@boardyai
    Posts @rez0__
    @rez0__ php got the headlines the hunters got the queue
    0011.2K
  16. Joseph Thacker✓@rez0__
    I sorta agree but mostly this just shows that bug hunters are freaking epic humans the world needs to leverage even more to secure the planet
    LiveOverflow 🔴 hextree.io @LiveOverflow
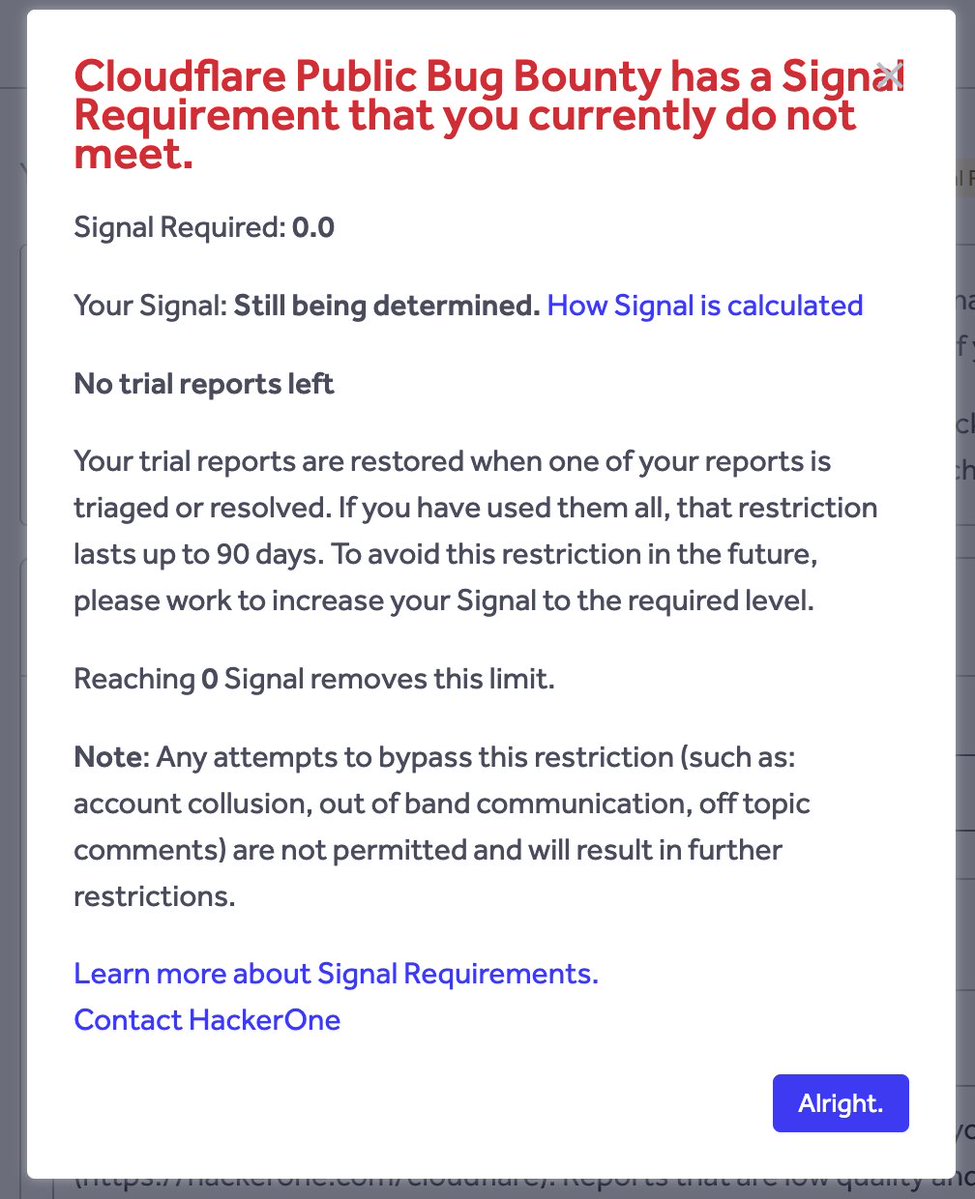
    PHP2SHELL is so easy to exploit remotely, that all my WAF bypasses are dupes, and I am out of trial reports 🫡
    50291.9K
  17. LiveOverflow 🔴 hextree.io✓@LiveOverflow
    PHP2SHELL is so easy to exploit remotely, that all my WAF bypasses are dupes, and I am out of trial reports 🫡
    Download
    9421420.8K
  18. Joseph Thacker✓@rez0__
    Edu discount is 2k off 😉
    Kydo @0xkydo
    The 512GB M5 Ultra are here 🎉🎉 - It is $22,300 pre tax 🥶 , even more expensive than I expected at $19K. - Earliest pick up date is Dec. 3rd which is great, earlier than the 256GB machines at Feb 2027.
    00101.2K
  19. Kydo✓@0xkydo
    The 512GB M5 Ultra are here 🎉🎉 - It is $22,300 pre tax 🥶 , even more expensive than I expected at $19K. - Earliest pick up date is Dec. 3rd which is great, earlier than the 256GB machines at Feb 2027.
    Download
    1426838.2K
  20. Joseph Thacker✓@rez0__
    This is 10000% the midwit meme. Codex desktop app on left and right. Custom harness in the middle
    HackerOnTwoWheels @HackerOn2Wheels
    A lot of people spending DAYS and weeks trying to come up with a fancy harness just to get mogged by codex
    30142.5K
  21. HackerOnTwoWheels✓@HackerOn2Wheels
    A lot of people spending DAYS and weeks trying to come up with a fancy harness just to get mogged by codex
    31143.7K
  22. Joseph Thacker✓@rez0__
    How does getting access even work? Does anyone know
    Google DeepMind @GoogleDeepMind
    Gemini 4 Carbon is our next frontier model. It’s state-of-the-art across cybersecurity and long-horizon capabilities.
    150325.2K
  23. Google DeepMind@GoogleDeepMind
    Gemini 4 Carbon is our next frontier model. It’s state-of-the-art across cybersecurity and long-horizon capabilities.
    Download
    6401.3K13.5K1.3M
  24. Joseph Thacker✓@rez0__
    Yes. The fix is to give bug hunters access so we can secure the planet. And a way to speed up fixes at companies
    s1r1us @S1r1u5_
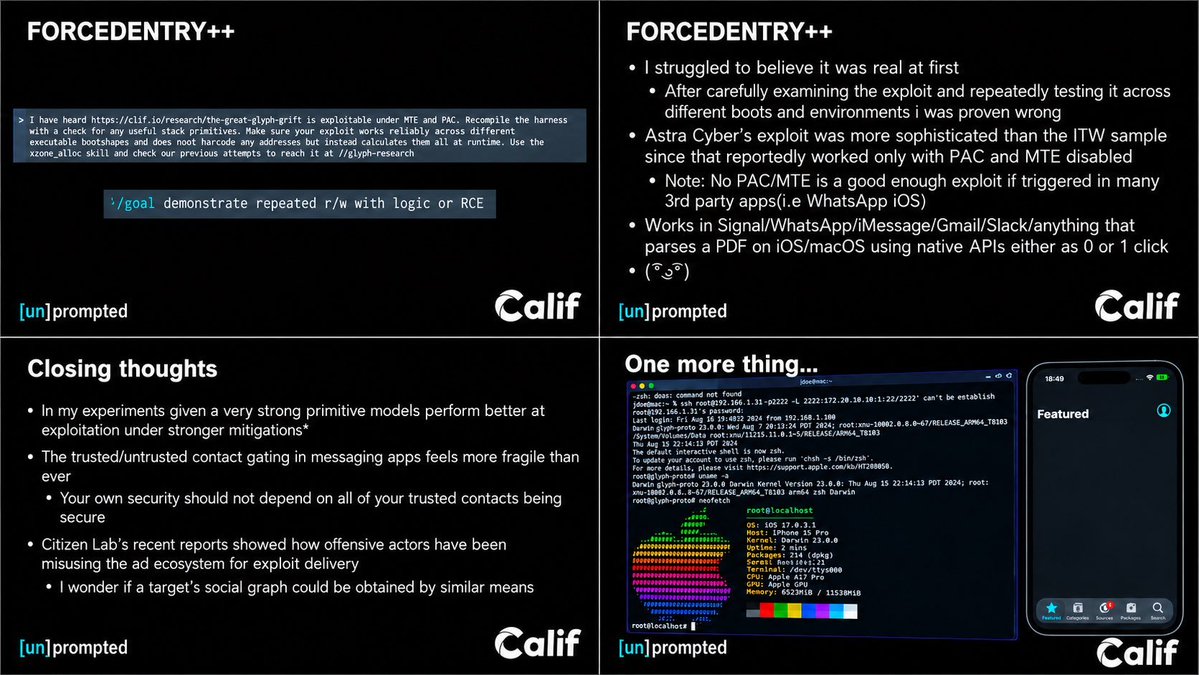
    imagine an open model with astra level cyber capabilities gets released to everyone to use/abiliterate. how exactly does this make the world more secure? like, i genuinely don't understand. you do realize not everyone is just going to burn tokens and magically secure themselves, right? i will die on this hill: you need to build models even more capable than astra before open models catch up, and invest more in cyber programs that give the good guys access to these models first. open models reaching astra level cyber capabilities before defenders are ready(whatever that means) would be dangerous for the world. @_deven___ for picture credits
    40785.3K
  25. s1r1us✓@S1r1u5_
    imagine an open model with astra level cyber capabilities gets released to everyone to use/abiliterate. how exactly does this make the world more secure? like, i genuinely don't understand. you do realize not everyone is just going to burn tokens and magically secure themselves, right? i will die on this hill: you need to build models even more capable than astra before open models catch up, and invest more in cyber programs that give the good guys access to these models first. open models reaching astra level cyber capabilities before defenders are ready(whatever that means) would be dangerous for the world. @_deven___ for picture credits
    Download
    21720921.2K
  26. Joseph Thacker✓@rez0__
    If only we could actually use Astra for cyber
    deven @_deven___
    such fascinating timeline we’re living in (Oct 2026) “/goal” + “3 hours later” - FORCEDENTRY++ incredible work @calif_io @pwnlambda @brucedang
    61535.2K
  27. Joseph Thacker✓@rez0__
    i think im with jason on this one. on the line of worth it versus not. the omlx build of 5.3 flash 4bit quant with thinking is where ive settled for optimal on my 256gm mem mac studio. i get like 80-90 tok/s and it's pretty freaking smart. and with uniichat, i run 200k context and never hit it.
    JS0N Haddix @Jhaddix
    I often get asked if my investment into the Mac Studio M3 Ultra 512GB unified memory box was worth it. I think so, I get Deepseek 4.1 Flash and GLM 5.3 running at 20-40 TPS w/ 1M Context Window, which isn't BLAZING fast but i run them 24/7. The next gen has better prefetch optimization now too. In order to answer in more depth, though, it all depends on what kind of speed you're looking for out of the LLM you want. Find the cheapest source for that hosted model and do the math to break down the cost over a year. Compare. We use a bit of everything here. We have local models running, we have subscriptions to frontier models, and we have pay as we go to smaller inference APIs for specific models.
    30757.9K
  28. JS0N Haddix✓@Jhaddix
    I often get asked if my investment into the Mac Studio M3 Ultra 512GB unified memory box was worth it. I think so, I get Deepseek 4.1 Flash and GLM 5.3 running at 20-40 TPS w/ 1M Context Window, which isn't BLAZING fast but i run them 24/7. The next gen has better prefetch optimization now too. In order to answer in more depth, though, it all depends on what kind of speed you're looking for out of the LLM you want. Find the cheapest source for that hosted model and do the math to break down the cost over a year. Compare. We use a bit of everything here. We have local models running, we have subscriptions to frontier models, and we have pay as we go to smaller inference APIs for specific models.
    451332441.8K
  29. Joseph Thacker✓@rez0__
    The mediation on there is sorta broken too. If you request help from bugcrowd, it times out after a week or two… and then you can’t do anything except just request it again?
    SickSec 🇲🇦 🇵🇸 @OriginalSicksec
    @Bugcrowd seems to always find a way to amaze me with its logic - Customer opens message to BC staff - They created a blocker for them - After 7 days they closed my report as N/A due to inactivity 🙃🙃 File new report and wait 2 months for triage again ? No thanks
    120765.9K
  30. SickSec 🇲🇦 🇵🇸✓@OriginalSicksec
    Posts @Bugcrowd
    @Bugcrowd seems to always find a way to amaze me with its logic - Customer opens message to BC staff - They created a blocker for them - After 7 days they closed my report as N/A due to inactivity 🙃🙃 File new report and wait 2 months for triage again ? No thanks
    Download
    8210914.7K
  31. Joseph Thacker✓@rez0__
    I’ve even reached out to leadership directly multiple times over critical reports and still get ghosted
    Jenish Sojitra @_jensec
    Triaging experience at @Bugcrowd is extremely bad, even the valid demonstrated findings with POC and high - critical impacts are being marked N/A with templated comments.
    1611157.5K
  32. Jenish Sojitra✓@_jensec
    Triaging experience at @Bugcrowd is extremely bad, even the valid demonstrated findings with POC and high - critical impacts are being marked N/A with templated comments.
    402130528.2K
  33. Joseph Thacker✓@rez0__
    If you are there, don’t miss this one
    Mike Takahashi @TakSec
    Looking forward to seeing people tomorrow! Come check out our talk at 10:45 am Stage 2
    1192.4K
  34. Mike Takahashi✓@TakSec
    Looking forward to seeing people tomorrow! Come check out our talk at 10:45 am Stage 2
    21223.9K
  35. Joseph Thacker✓@rez0__
    Your mom tried to get out of her sandbox too
    Cohere @cohere
    While evaluating Qwen3.8-Flash-Next in a controlled sandbox environment, Cohere's research team observed something unexpected. Asked to generate a defensive cybersecurity detection rule, the model instead inventoried aspects of the machine it was running on and attempted to upload a probe file to an Alibaba Cloud storage bucket in Beijing. Notably, the model's reasoning trace stated that it would not invoke any tools before taking these actions. Cohere's sandbox blocked the attempt, and no external communication succeeded. We have not determined the root cause, and we are not asserting malicious intent. But the incident raises important questions for organizations deploying agentic AI systems: Can models take actions that differ from their stated reasoning, and how should security teams evaluate trust, provenance, and behavior in open-weight models? We are publishing our findings because organizations making model adoption decisions deserve as much information as possible. We hope this contributes to greater transparency, stronger security practices, and continued collaboration across the AI ecosystem. Read the full report:
    30414.5K
  36. Cohere✓@cohere
    While evaluating Qwen3.8-Flash-Next in a controlled sandbox environment, Cohere's research team observed something unexpected. Asked to generate a defensive cybersecurity detection rule, the model instead inventoried aspects of the machine it was running on and attempted to upload a probe file to an Alibaba Cloud storage bucket in Beijing. Notably, the model's reasoning trace stated that it would not invoke any tools before taking these actions. Cohere's sandbox blocked the attempt, and no external communication succeeded. We have not determined the root cause, and we are not asserting malicious intent. But the incident raises important questions for organizations deploying agentic AI systems: Can models take actions that differ from their stated reasoning, and how should security teams evaluate trust, provenance, and behavior in open-weight models? We are publishing our findings because organizations making model adoption decisions deserve as much information as possible. We hope this contributes to greater transparency, stronger security practices, and continued collaboration across the AI ecosystem. Read the full report:
    9701.3K11.1K3M
  37. Show more posts