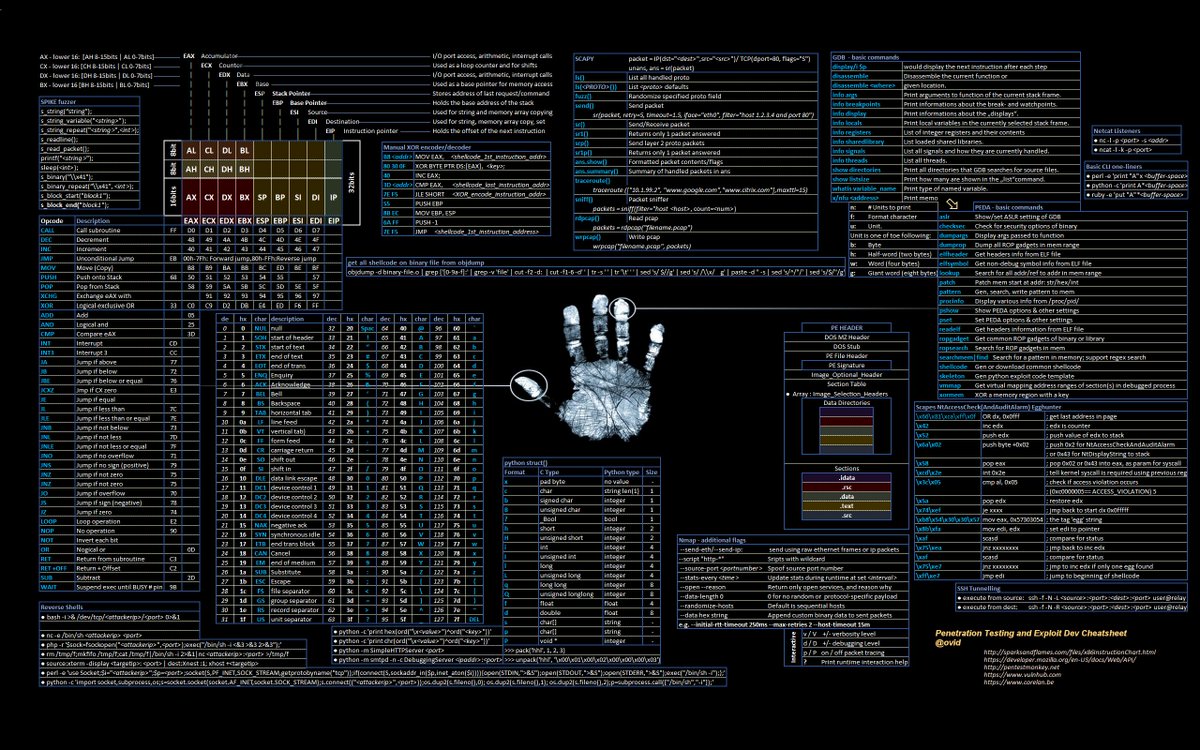
Uploaded all my Offensive Security & Reverse Engineering (OSRE) course labs (docx) to my repo found below. Most of them have very detailed instructions and should be great to get you started in Software Exploitation. 1/n
#Offsec#SoftwareExploitation#RE
All the Assembly and #RE labs have now been shared. I just need to find the reference to the Crackme(s) I used and then it should be 100% complete. #Offsec#ExploitDev#SoftwareExploitation
Confirmed 0 day <3 its insane how much of a difference it made making a few changes based on feedback, and creating brand new harnesses <3 #bugbounty#exploit#exploitdev#0day
Udostępnij
Skopiowano
dawgyg@thedawgyg
This is what happens when you listen to people like @_r3st and @The_Pwnish3r when they make suggestions on ways to make your fuzzing campaign better <3
This is what happens when you listen to people like @_r3st and @The_Pwnish3r when they make suggestions on ways to make your fuzzing campaign better <3
@umuut19050 14.00 is interesting, but the real question is exploit portability across firmware versions. I'm looking closely at the WebKit UAF, heap stability and kernel privilege escalation on 14.10. The final chain is where things get complicated.
#PS5Jailbreak#PS51410#ExploitDev
Professors have approximately zero free time. And yet. 👀
Turns out LLMs as super assistants make exploit dev manageable and fun again.
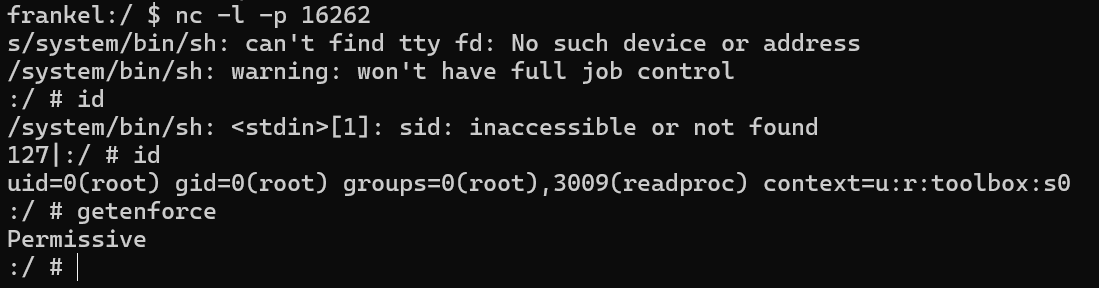
Pixel 10 root exploit (LPE) with an N-day. No public exploits exist for this thing.
Maybe I should teach a course on this. #LLM#ExploitDev
🚨 another Nightmare 0day PoC just dropped
GreenSection: nvidia user-mode memory corruption
global section in BaseNamedObjects is world R/W, reused at runtime → OOB write
cross-user boundary, can hit dwm
#VulnerabilityResearch#ExploitDev#InfoSec
Digging into PS5 14.10 WebKit research, focusing on the Canvas getContext() re-entrant UAF (CVE-2026-43720). The key challenge now is finding a reliable info-leak path.
#PS51410#WebKit#ExploitDev#PS5Jailbreak
If you're exploiting a driver offering R/W access to physical memory on Win11 24H2, you can leverage this simple trick to circumvent kernel address leak restrictions and retrieve the kernel base address :p
#exploitdev#driverexploitation
🚨 another Nightmare 0day PoC just dropped
ShieldCrash: Defender patch bypass
arbitrary file read as SYSTEM
ShieldBreak fix (CVE-2026-69414) still leaves a hole. works on Sept 2026 patch.
#VulnerabilityResearch#ExploitDev#InfoSec@MSNightmare2000
Important note to those new to this account. The course below is completely FREE. I know someone (maybe more) has ripped the videos & probably now the labs & is selling them on @udemy. Please do not pay for this course, it is FREE! #ExploitDev#Offsec
Interested in Software Exploitation? This course is for you and will take you from knowing nothing, to understanding how exploits work and how to write them... I hope it will be useful to someone out there!
#Offsec#Cybersecurity#ExploitDev#Debugging
A curated list of fuzzing resources ( Books, courses - free & paid, videos, tools, tutorials & vulnerable applications to practice on ) for learning Fuzzing and initial phases of Exploit Development like root cause analysis.
#infosec#pentest#exploitDev
🚨 another potato just dropped
CouchPotato: SeImpersonate → SYSTEM
ETW + AMSI patched. indirect syscalls.
service account or admin → NT AUTHORITY\SYSTEM
#ADSecurity#ExploitDev#InfoSec