Keycard✓

@KeycardAI

Keycard puts users, developers and companies in control of AI agents with real-time, adaptive permissions and complete transparency.

43 A seguir4.7K Seguidores284 Publicações
  1. Keycard✓@KeycardAI
    Keycard made the 2027 Fortune Cyber 60. @lightspeedvp's CISO survey found only a third of companies give agents their own scoped identities, and a quarter of them hand them human credentials. Agents need their own identities, scoped to the task. Full list in the reply.
    4311826
  2. Keycard✓@KeycardAI
    "The trick for anyone building these systems is how do I ensure that I don't bring the user into the loop except when absolutely required" @ianlivingstone explained how intent can help combat consent fatigue during our Intent Based Auth panel at AI Engineer NYC.
    Baixar
    209687
  3. Keycard✓@KeycardAI
    Publicações @KeycardAI
    Watch the full panel
    00170
  4. Keycard✓@KeycardAI
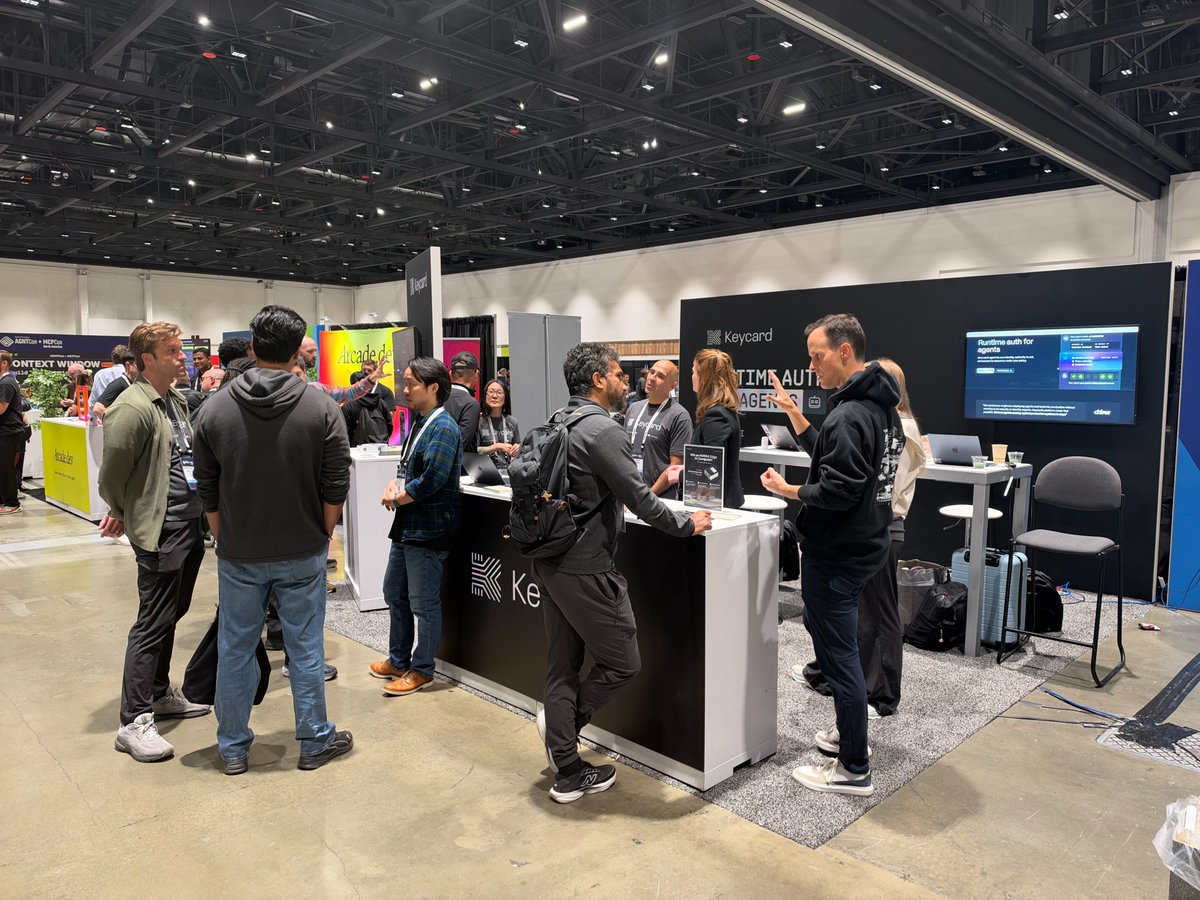
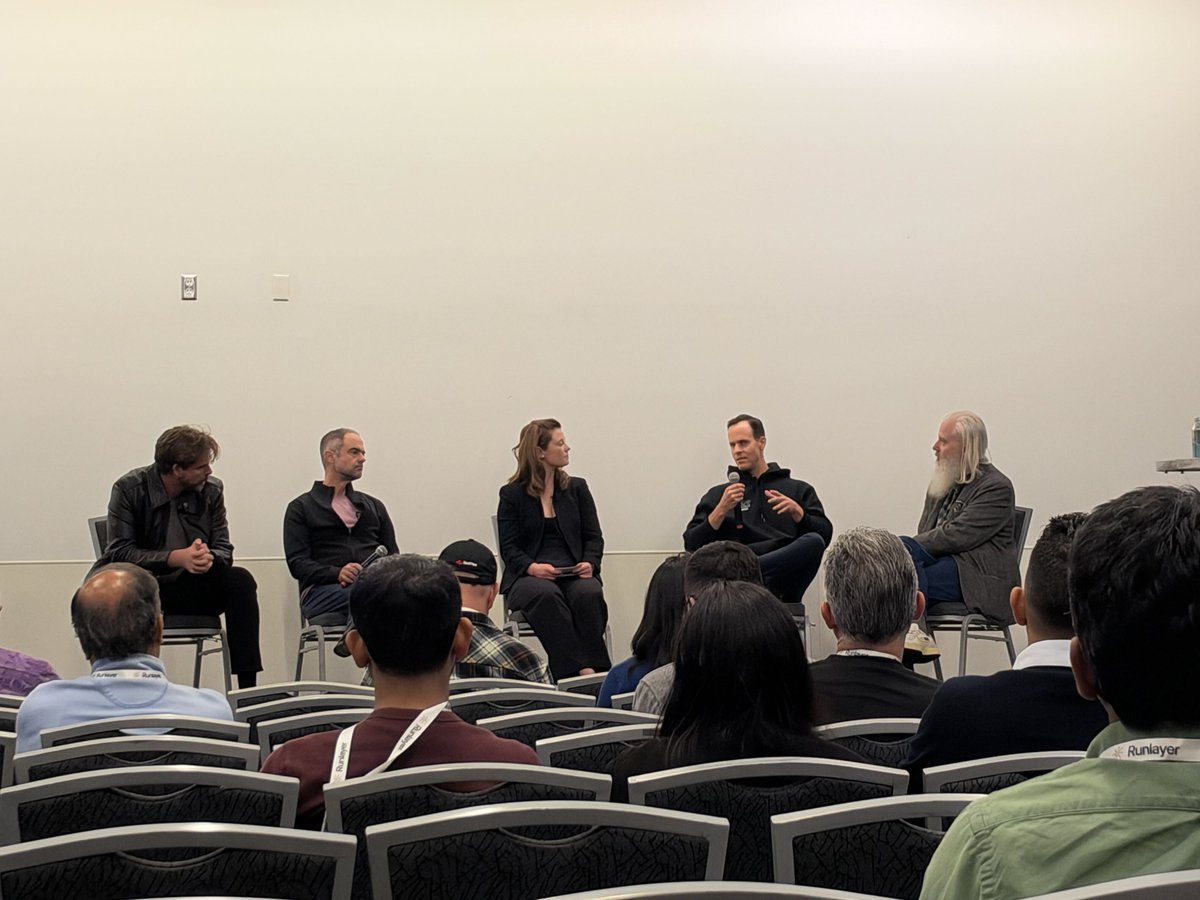
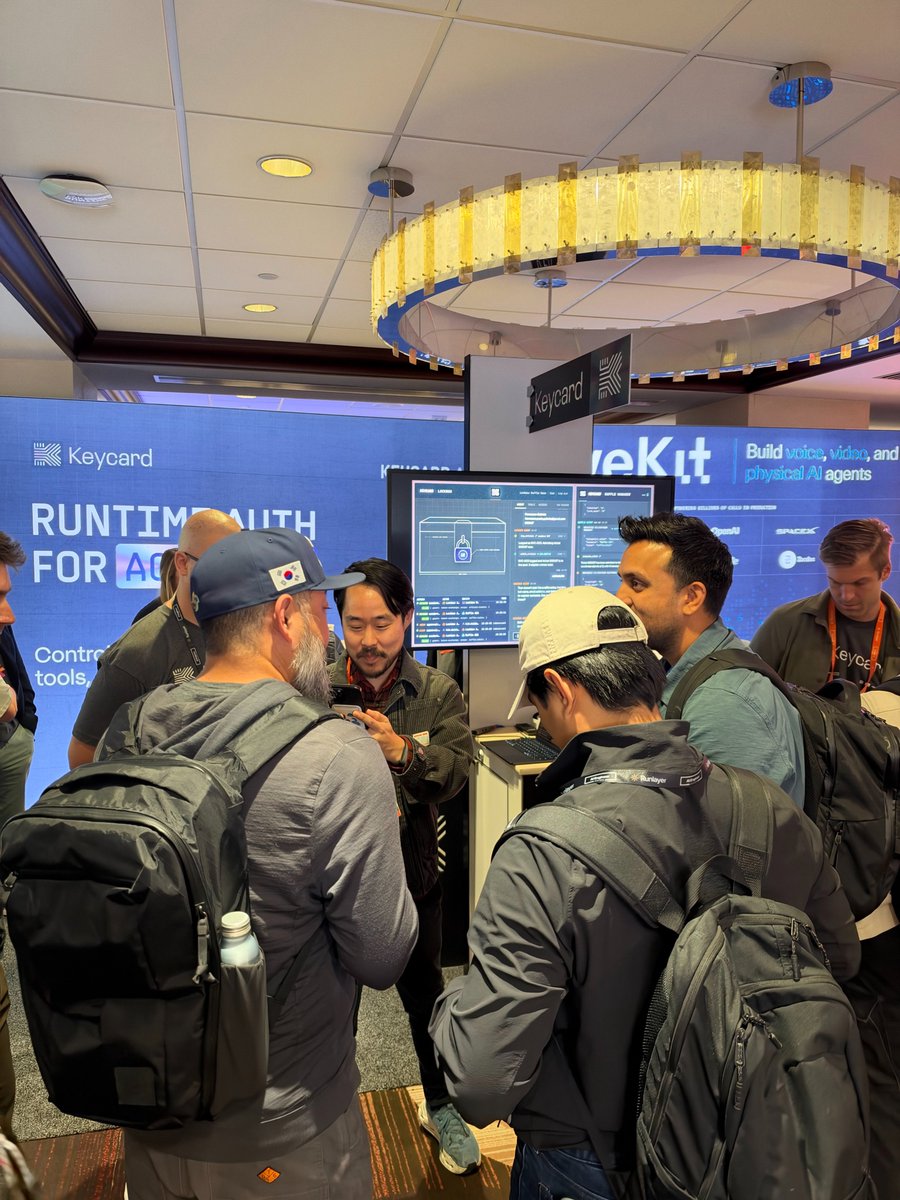
    We're having fun talking to everyone at AGNTCon this week about runtime auth for agents. We led a debate on if security is ready for a headless future and gave a talk on how to give agents autonomy, capability, and security. Today is our last day, come say hi and see a demo!
    Baixar
    006509
  5. Keycard✓@KeycardAI
    It was great to see so many folks interested in agentic runtime security yesterday at AARM Intercept Night. @jaredhanson @jankytweet @DickHardt gave a panel on Intent Based Auth and @filearts demo'd intent based auth in Keycard!
    Baixar
    1015813
  6. Keycard✓@KeycardAI
    Publicações @KeycardAI
    To learn more about intent based auth watch our full panel from @aiDotEngineer NYC
    001109
  7. Keycard✓@KeycardAI
    Your best coding agent lives on one developer’s laptop. A software factory is when the whole team can share and learn from it. Here’s how to get there:
    118562
  8. Keycard✓@KeycardAI
    Publicações @KeycardAI
    Read more about the Secure Software Factory reference architecture, in partnership with @Docker, @SocketSecurity, and others as part of Agent Baseline:
    001154
  9. Keycard✓@KeycardAI
    Our panel on Intent Based Auth @aiDotEngineer NYC is LIVE on YouTube @ianlivingstone CEO Keycard, Michael Davis Global Chief Security Architect @jpmorgan, and @DickHardt Founder of AAuth discuss why we must have runtime auth for agents based on intent.
    Baixar
    2071.2K
  10. Keycard✓@KeycardAI
    Publicações @KeycardAI
    Watch it on YouTube:
    000129
  11. Keycard✓@KeycardAI
    What an amazing week! We spent the first half @aiDotEngineer NYC and the second half in SF for @AISecSummit and AAuth Night. We enjoyed meeting all of you and talking about runtime auth for agents, intent-based auth, and the new software factory reference architecture.
    Baixar
    1051.1K
  12. Keycard✓@KeycardAI
    Publicações @KeycardAI
    Read the Software Factory Reference Architecture
    Ian Livingstone @ianlivingstone
    Today we're publishing the first draft of the Agent Baseline Software Factory Reference Architecture! An opinionated blueprint for securing increasingly autonomous software factories, built with folks across the community. It's open for feedback and contributions!
    000134
  13. Keycard✓@KeycardAI
    An agent's access for a task should be the overlap of what it can do and what the task needs, all inside what the org allows. More on how that works below.
    Ian Livingstone @ianlivingstone
    We've spent a lot of time at @KeycardAI thinking about how authentication and authorization need to evolve as agents take on more work. API keys and OAuth scopes were never designed to account for tasks, delegation between agents, or agents acting on their own. I wrote about how we're approaching this and what we think needs to change.
    405523
  14. Ian Livingstone✓@ianlivingstone
    We've spent a lot of time at @KeycardAI thinking about how authentication and authorization need to evolve as agents take on more work. API keys and OAuth scopes were never designed to account for tasks, delegation between agents, or agents acting on their own. I wrote about how we're approaching this and what we think needs to change.
    28393.7K
  15. Keycard✓@KeycardAI
    Publicações @KeycardAI
    00031
  16. Keycard✓@KeycardAI
    Publicações @KeycardAI
    Then access is enforced as the work happens: short-lived credentials per task, denied by default, and escalated only when policy allows. Task done, access gone.
    00016
  17. Keycard✓@KeycardAI
    Publicações @KeycardAI
    That context has to come from the trigger and the handoff chain, never from the agent's own description of its task. Otherwise an agent can talk its way into more access.
    00019
  18. Keycard✓@KeycardAI
    Publicações @KeycardAI
    Who's acting matters as much as what. An incident agent woken by an alert acts as itself. When it hands log analysis to another agent, that agent gets only what that piece of work needs.
    00057
  19. Keycard✓@KeycardAI
    Keycard
    RT @ianlivingstone: Today we're publishing the first draft of the Agent Baseline Software Factory Reference Architecture! An opinionated blueprint for securing increasingly autonomous software factories, built with folks across the community. It's open for feedback and contributions!
    0320238
  20. Keycard✓@KeycardAI
    We're hosting Secure Software Factory Show and Tell Oct 13 during @aiDotEngineer NYC with @braintrust, @SocketSecurity, and @Docker Learn how to constrain, observe, and authorize your agents, validate their inputs, and respond when something goes wrong.
    Baixar
    0291.4K