ahmia-site — Django-based search engine and crawler stack that indexes .onion hidden services on the Tor network, providing searchable metadata for dark web content discovery.
darc — Darkweb crawler that uses requests and Selenium workers to fetch pages, capture headers and cookies, extract links, and save rendered screenshots for OSINT collection.
xmir-patcher — Patches Xiaomi router firmware images to enable SSH access and install custom firmware, with automated Windows and Linux/macOS launcher scripts.
osint_stuff_tool_collection — Curated collection of 1000+ online OSINT tools and services for geolocation, social media, domain/IP, email, image and archive investigations.
TorBot — Crawls .onion sites over Tor to collect page titles, hostnames, and link relationships, exporting JSON trees and visualizations for dark web OSINT investigations.
C2IntelFeeds — Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning for SIEM, EDR, and threat hunting.
shannon v3.5.0 — Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes real exploits to prove vulnerabilities before they reach production.
dshield — Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to the DShield portal.
advisory-database — Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
MeshCentral — A complete web-based remote monitoring and management web site. Once setup you can install agents and perform remote desktop session to devices on the local network or over the Internet.
malware-iocs — Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and incident response use.
cvmimage — Builds a hermetic, reproducible confidential VM image for secure inference and custom compute on AMD SEV-SNP and Intel TDX, with auditable source-to-measurement builds.
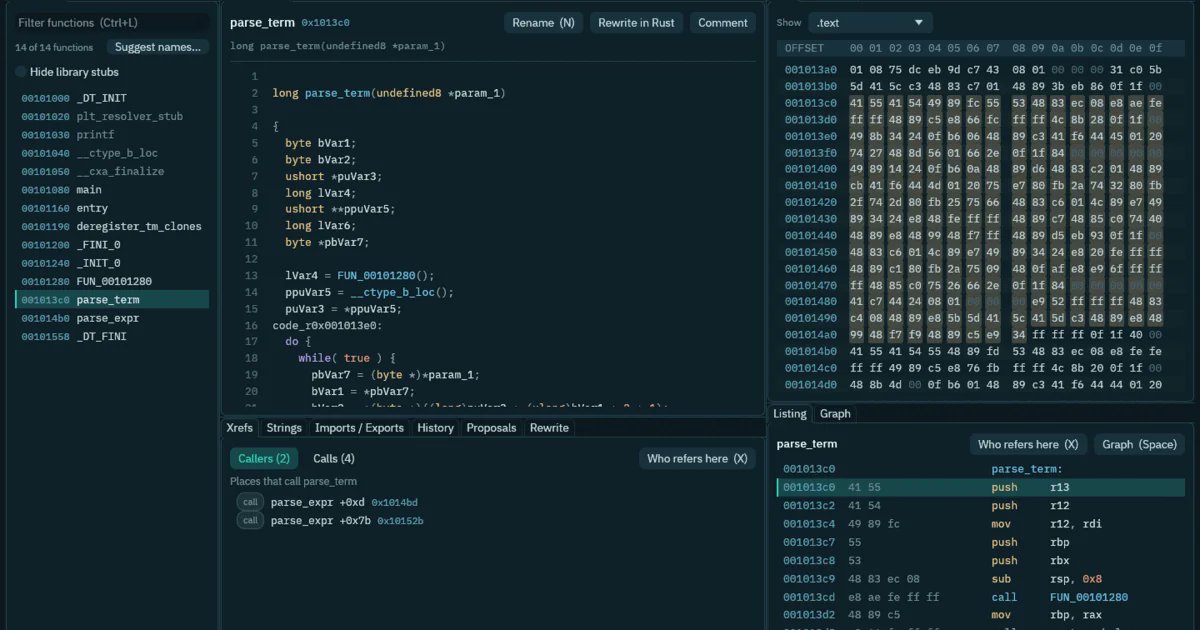
kraken — Reverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed emulation, and CLI/MCP automation.
nuclei — Updated! — Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and cloud infrastructure.
Esp32-Blue-Ducky — ESP32 firmware that emulates a Bluetooth HID keyboard to auto-pair with Android phones and inject scripted keystrokes for authorized security testing.
mtk-imei-switcheroo — Read and write IMEI records and WiFi/Bluetooth addresses in MediaTek NVRAM files or partition images. Includes interactive ADB tools for rooted devices and separate, version-specific modem/LK patchers for biloba.
xss-payload-list — Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty hunting.
honeypot-data — Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt analyses.
remove-ai-watermarks — Updated! — Remove visible and invisible AI watermarks from images and video, and AI provenance metadata from images, video, and audio...