Let's not mince words:
* If you don't support trans people, you're a bad human
* If you have to add caveats to your support (e.g. "as long as my kids don't see"), you're one of the worst kinds of human
* Trans deserve your *unconditional* support for their humanity
There's zero question in my mind that organizations employing Anthropic's "team usage" feature without specific policies around it will be sued by employees (and probably rightfully so). We discuss why in today's episode of Breach Please.
In short, you should be thinking about employee interaction with Claude like email or chat logs. If you don't have "summarize my team's email usage" then you shouldn't have this either (for much the same reason).
RT @mikecloppert: I came to appreciate today something I do as a leader that's maybe novel. Maybe not. Probably others do it without realizing it. I call it the Strategic Bad Idea: Nothing gets your team to solve a problem faster than their boss proposing a bad idea as the solution.
RT @TecFlack: Met Walter Koenig in 2015 at a pop culture show; he was gracious speaking to my daughter about her desire to pursue a career in the entertainment industry. Rest in peace Mr. Chekov -- you lived long and prospered
The "S" in MCP doesn't stand for Security.
Bryson Bort and Jake Williams break down the Model Context Protocol on Unicorn Dispatch LIVE: a live purple team demo, plus how to use its power without handing attackers the keys.
Recap:
The "S" in MCP doesn't stand for Security.
Bryson Bort and Jake Williams break down the Model Context Protocol on Unicorn Dispatch LIVE: a live purple team demo, plus how to use its power without handing attackers the keys.
Recap:
RT @JFrogSecurity: 🚨 Brotli2Shell goes beyond HTTP2Shell.
CVE-2026-111497 is a CVSS 9.2 out-of-bounds write in Google’s Brotli decoder that has been exploited for RCE and impacts far beyond HTTP.
JFrog reproduced RIP control in FFmpeg via a crafted JPEG XL file and identified additional attack paths in ClickHouse, .NET, and Apache Arrow, where some fixes were still unavailable at the time of writing.
We’ve also released an open-source scanner to uncover potential exposure beyond vulnerable package versions.
Full research and technical details in our blog 👇
I explicitly decided to avoid sharing that post because it's written in an extremely weird way. The article is basically a giant non-sequitur. It starts with "we saw a proof of concept" then immediately jumps into "agentic AI post-exploitation", without making any claim that A led to B.
It's a very strange structure for a threat intelligence report, and none of the segments of the article logical follow each other. I tried asking for clarification about what/why that is, but the response I got was extremely cagy, so I didn't feel comfortable risking my reputation on it.
I explicitly decided to avoid sharing that post because it's written in an extremely weird way. The article is basically a giant non-sequitur. It starts with "we saw a proof of concept" then immediately jumps into "agentic AI post-exploitation", without making any claim that A led to B.
It's a very strange structure for a threat intelligence report, and none of the segments of the article logical follow each other. I tried asking for clarification about what/why that is, but the response I got was extremely cagy, so I didn't feel comfortable risking my reputation on it.
RT @RayRedacted: LIVE... Watch Sam Watson go for gold in the final international Speed Climbing event of 2026. Despite a recent injury, Sam wants to finish 2026 strong. (629 days until the Olympics)
Link: Sam Watson dot live
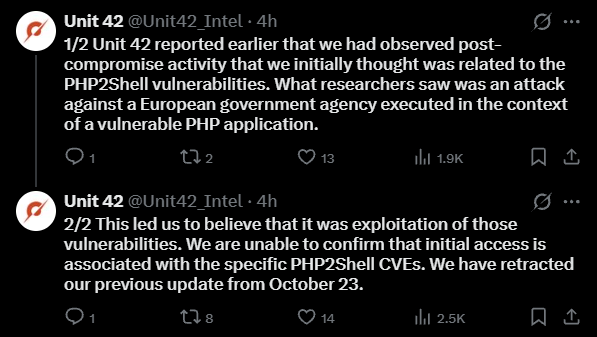
Today's Breach Please is out. We talk about how Chainguard unilaterally broke the embargo on the PHP vulnerability and what that likely means for coordinated disclosure going forward.
It is BY FAR the spiciest episode we've recorded to date. 1/3
We also dive into the question of whether AI labs are actively hurting security (yes, they are. They just are).
Jess has some pretty strong opinions about the message in this tweet specifically. We don't 100% agree, but the discussion is valuable. 2/3
Compartilhar
Copiado
Jason D. Clinton 🔸@JasonDClinton
as bad as things have gotten in the past 4 days, they are going to get a lot worse before they get better. security leaders, never let a crisis go to waste: please go to your boards and ask for help right now. not for ai, for the basics. (we need to hold on for ~18 months.)
as bad as things have gotten in the past 4 days, they are going to get a lot worse before they get better. security leaders, never let a crisis go to waste: please go to your boards and ask for help right now. not for ai, for the basics. (we need to hold on for ~18 months.)
Not all heroes wear capes.
Some carry tentacles...
Compartilhar
Copiado
Cthulhu ( ;,;)@Cthulhu_Answers
In the past I worked with NCMEC, I built a tool for mining EXIF data from images and had a database of camera serial numbers they could query. If they had the serial number of a camera used to take CSAM they could map it to other photos on the internet that mapped to user accounts.
Join me at 1100 ET today to discuss the current vulnerabilities in PHP, Node.js, GitLab, and the eMudhra certificate signing key debacle. We'll provide actionable advice and cut through the noise in our hour together.
RT @IANS_Security: PHP2Shell (CVSS 9.2) disclosed, and eight eMudhra certs could let anyone mint trusted certs for any site.
Thursday, Oct. 22, 11 a.m. ET: @MalwareJake, IANS Faculty, on what your security team should do now.
Register now:
ConnectWise has an incident with compromise this weekend where they disabled backups in customer M365 environments.
Even if you're not a ConnectWise customer, you likely have third party risk management concerns here for those you do business with who are.
In most cases, ConnectWise won't be able to see into the customer environments to identify who was compromised - those logs live in the customer tenant.
If you missed my two day AI Risk Assessment course at Wild West Hackin' Fest in Deadwood last week, I'm teaching it again in Denver in February and we're offering it virtually too. Hope to see you there!
In the past I worked with NCMEC, I built a tool for mining EXIF data from images and had a database of camera serial numbers they could query. If they had the serial number of a camera used to take CSAM they could map it to other photos on the internet that mapped to user accounts.