Who signs open source? Stefan Wenig (SignPath) and Mikaël Barbero (@EclipseFdn) on trustworthy software releases.
(1) A signature alone is not enough. It only counts if the build behind it is protected.
(2) Prove how it was built, because no attestation means no code signature.
What are the essential elements for #codesign & #coproduction?
🎬 A 2 min summary
Masterson et al. (2024) Mechanisms for #codesigning and #coproducing health and social care: a realist synthesis. Reseach Involvement & Engagement 10, 103.
We're excited to announce our partnership with @ReversingLabs, a leader in software #supplychainsecurity, to enhance software security by combining their advanced binary analysis and threat detection with our enterprise-grade secure #codesigning solution.
🎙️ Last Webinar Week session today: who can sign open source software? Stefan Wenig, SignPath, and Mikaël Barbero, @EclipseFdn, cover keys vs. certificates, packaged releases and the XZ Utils lesson.
Register for webinars:
#CodeSigning#OCX27
Announcing DigiCert Keylocker: A convenient, easy to access, inexpensive way to comply with new CA/B Forum changes for code signing private keys 🔑
Learn more:
#compliance#codesigning
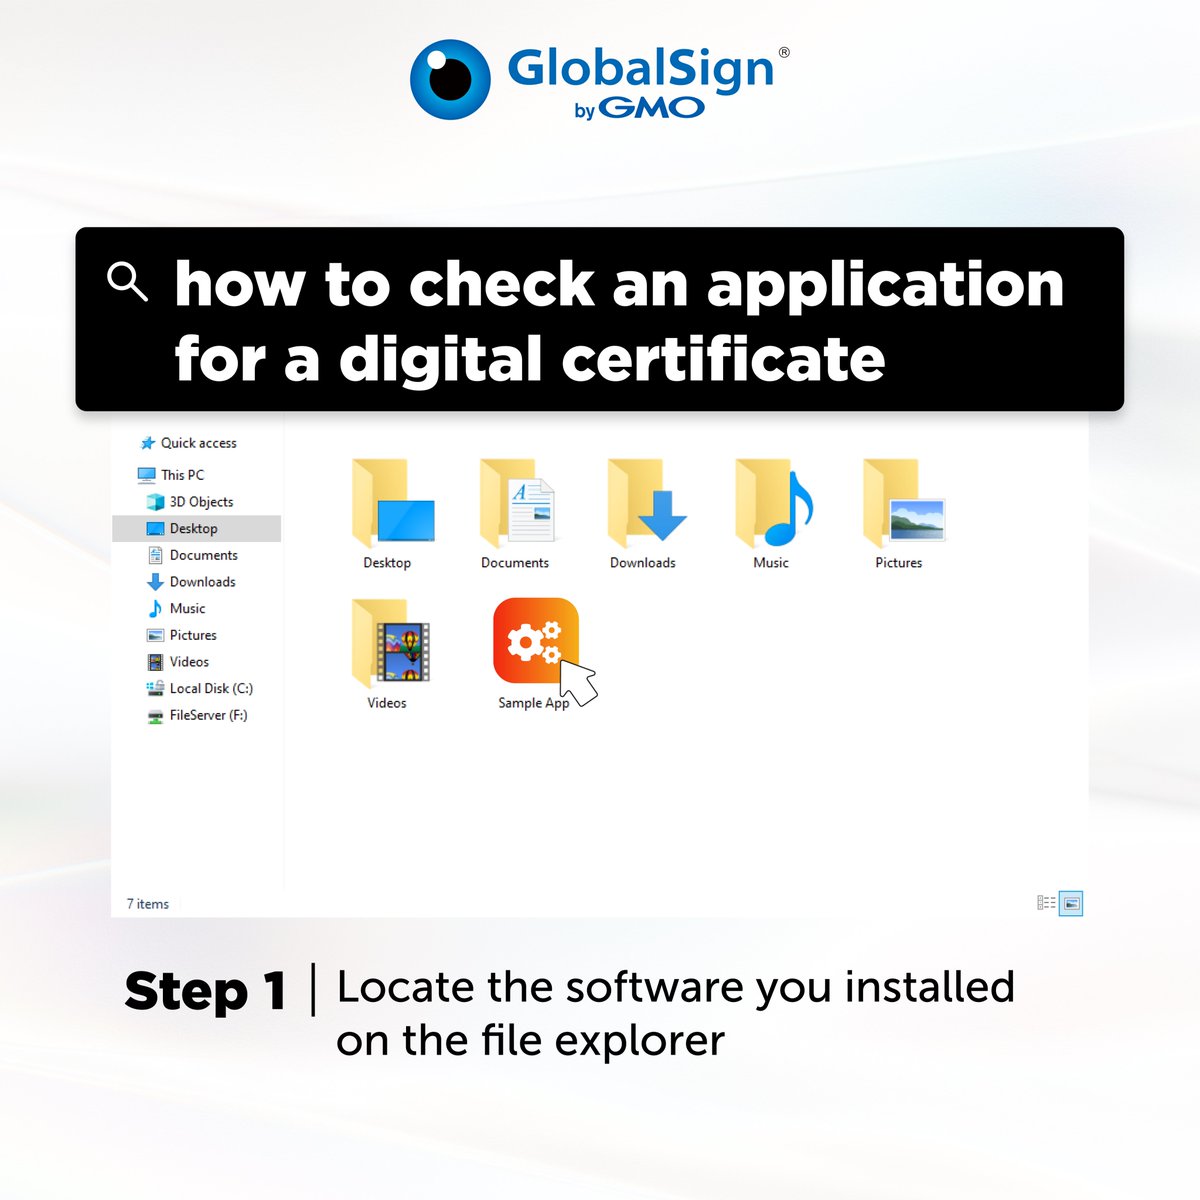
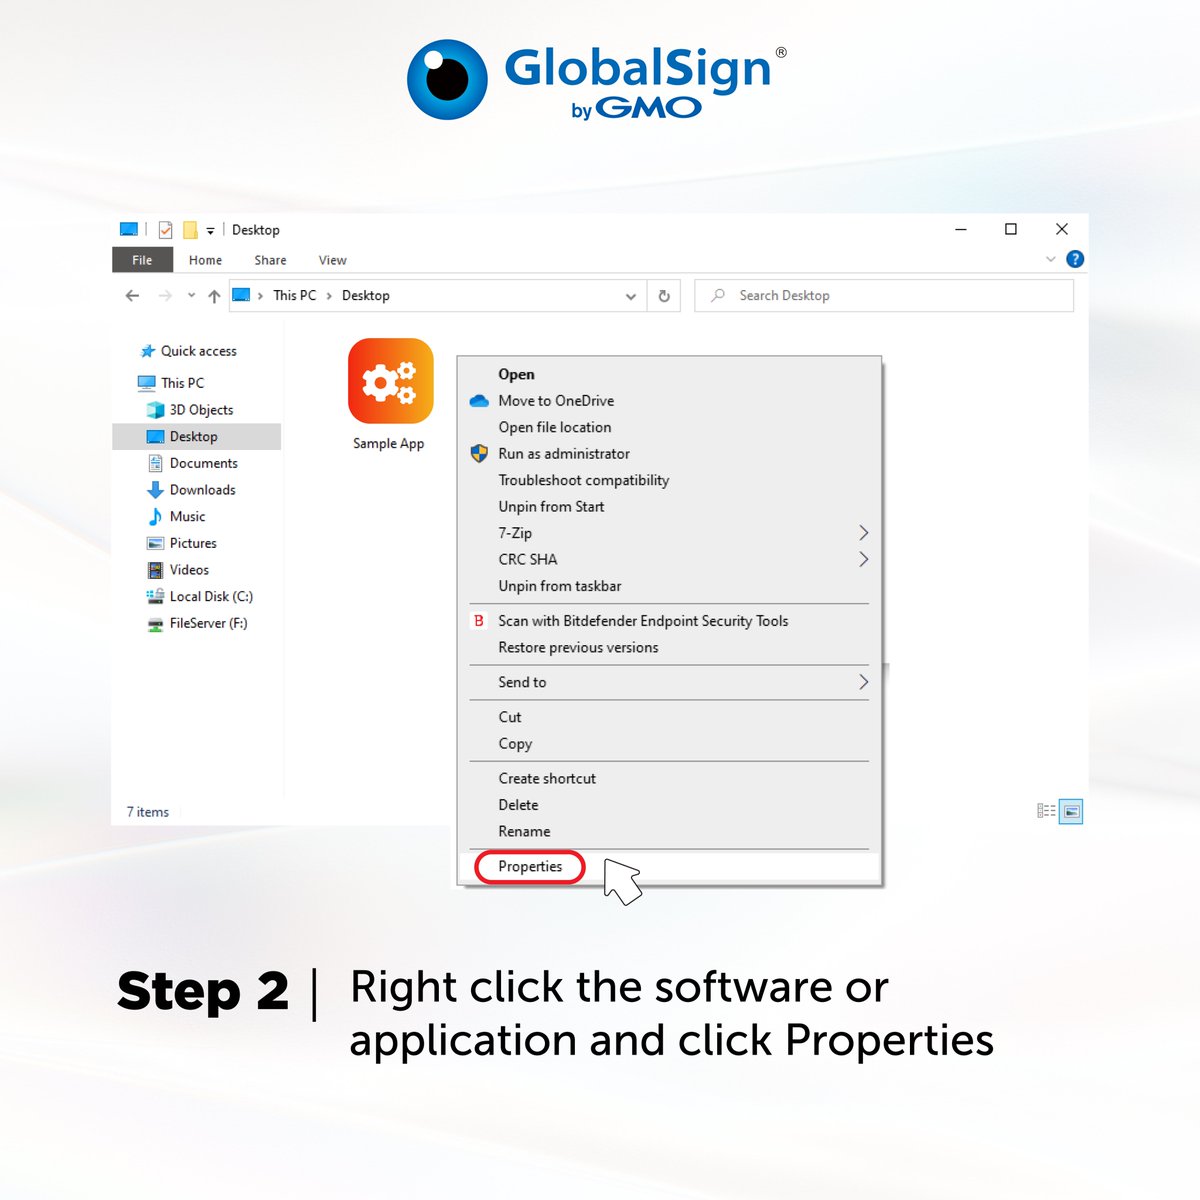
Here's a step-by-step guide on how to check if your software has a valid and legitimate digital certificate.
Click here to know more about Code Signing:
#CodeSigning
Published Magick·NET 13.5.0 for .NET Standard and .NET Framework: The NuGet packages can be found here:
The binaries of this release and the @NuGet packages are signed with @Azure#CodeSigning.
More and more, researchers & practitioners are finding value in co-designing research, but it's not always easy. In a new paper in @ICES_ASC, we share our honest experiences - the good, the bad, & the ugly - #codesigning#research between the Global North & Global South. 🧵 (1/5)