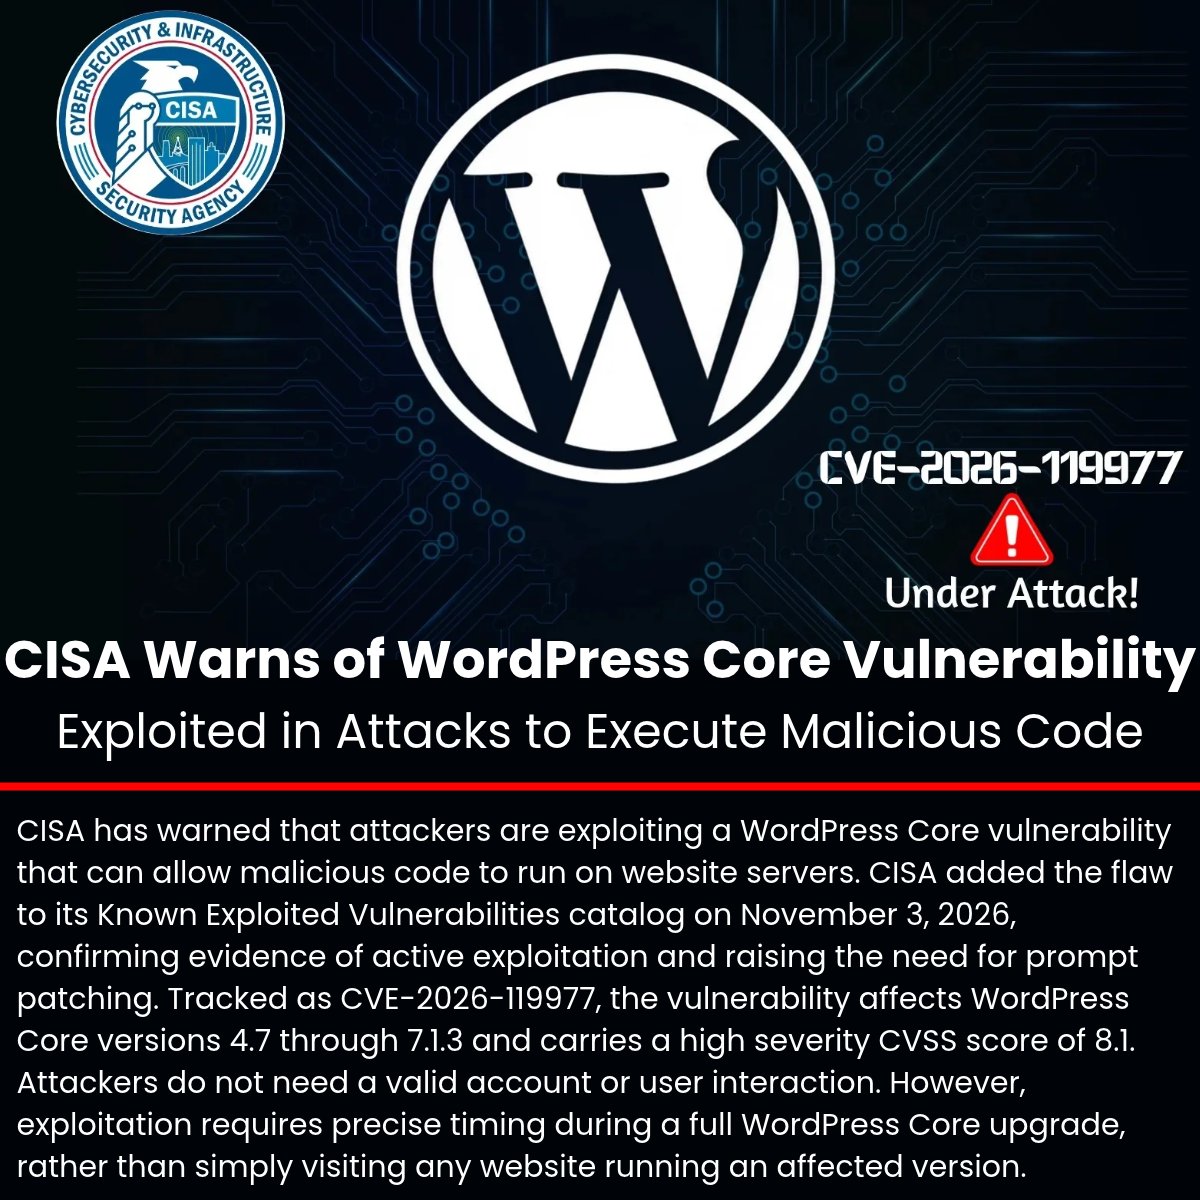
‼️ CISA Warns of WordPress Core Vulnerability Exploited in Attacks to Execute Malicious Code
Details:
CISA has warned that attackers are exploiting a WordPress Core vulnerability that can allow malicious code to run on website servers.
CISA added the flaw to its Known Exploited Vulnerabilities catalog on November 3, 2026, confirming evidence of active exploitation and raising the need for prompt patching.
Tracked as CVE-2026-119977, the vulnerability affects WordPress Core versions 4.7 through 7.1.3 and carries a high severity CVSS score of 8.1. Attackers do not need a valid account or user interaction.
However, exploitation requires precise timing during a full WordPress Core upgrade, rather than simply visiting any website running an affected version.
#cybersecurityNews
73814214.4K