Beiträge mit #nodeJS

#nodeJS

Öffentliche Beiträge auf X, die #nodeJS verwenden.

Verwandte Hashtags

  1. Node.js✓@nodejs
    Node.js 24.22.2 “Krypton” (LTS) is here! 🚀 Includes V8 backports and a fix that keeps async context in parked stream writes. 🔗 Full changelog and download links:
    125548337.8K
  2. Node.js✓@nodejs
    Node.js 26 “Lithium” is now Long Term Support 🎉 v26.13.0 is out, with updates through April 2029. Heads-up for Linux users coming from an earlier LTS: libatomic may need to be installed separately.
    233412.1K131K
  3. The Hacker News@TheHackersNews
    🚨 UPDATE: Node2Shell (CVE-2026-111497) has moved from PoC to the wild. Scanning is live and the first exploit attempts are out. The RCE is now confirmed on STOCK x86-64 Node.js, not just arm64. Patch now → 22.23.4 / 24.22.1 / 26.12.1 Read ↓
    Herunterladen
    2617685594.1K
  4. Rafael Gonzaga✓@_rafaelgss
    Node.js 27 Alpha is out! 💚 First release of the new model: Alpha until April, Current on 2027-04 and LTS on 2027-10. What's new: * V8 15.6 🚀 * OpenSSL 4.1, npm 12.1 * --allow-env permission 🔍 * Native fs.glob, net/promises ⚡ * domain deprecated
    73225044.3K
  5. Node.js✓@nodejs
    📝The largest #nodejs best practices list. Curated from the top ranked articles and consistently updated:
    5189407
  6. NestJS@nestframework
    🚀 Introducing the Node adapter, new in NestJS 12.3. Nest has always stood on Express or Fastify. Now it stands on its own, right on node:http: the fastest way to run Nest. Nest is the fast part of your requests. NestJS Observe shows you the rest.
    Herunterladen
    295068036K
  7. Node.js✓@nodejs
    Node.js 27 Alpha is out! 🚀 Check it out:
    Rafael Gonzaga @_rafaelgss
    Node.js 27 Alpha is out! 💚 First release of the new model: Alpha until April, Current on 2027-04 and LTS on 2027-10. What's new: * V8 15.6 🚀 * OpenSSL 4.1, npm 12.1 * --allow-env permission 🔍 * Native fs.glob, net/promises ⚡ * domain deprecated
    61527232K
  8. Node.js✓@nodejs
    🔐 Node.js security updates are now available! New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues. Review the details and update your systems to stay secure. 🔗 #NodeJS #Security
    1363K12.6K1.3M
  9. Dark Coder✓@dark_coderz
    Your backend needs to handle 100,000 requests per second. Which framework are you trusting? A. Node.js + Express B. Python + FastAPI C. Go + Gin D. Java + Spring Boot
    101816843.8K
  10. The Hacker News@TheHackersNews
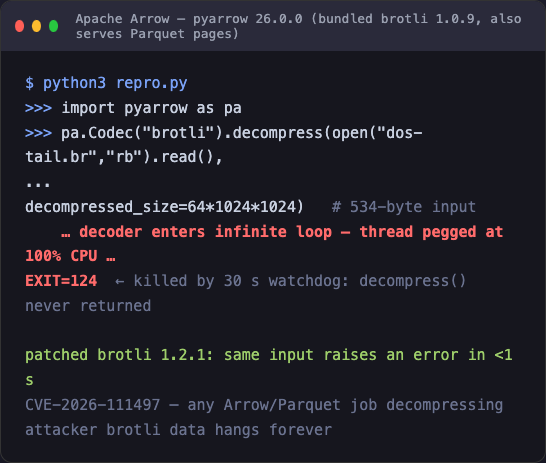
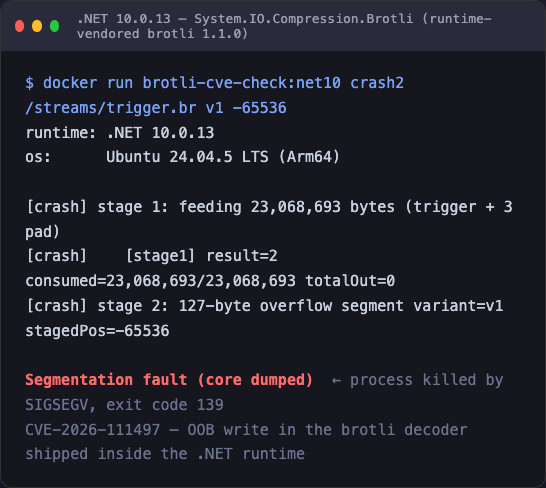
    🚨 UPDATE: The Brotli flaw (CVE-2026-111497) goes beyond Node.js and web traffic. • .NET: patched by Microsoft • FFmpeg: hit via a crafted JPEG XL image • ClickHouse: one request crashes it, fix not yet released • Apache Arrow: no fix yet Details ↓
    Herunterladen
    3518386388.6K
  11. kritika✓@vibeonX69
    Backend developers: Node.js or Go? Which one would you use for a new startup?
    382312.6K
  12. Mert Demirdelen✓@itsnotmyai
    Ankara’da ikamet eden deneyimli (min. 3 yıl) backend developer (node.js) arıyoruz. İlanın linkini yorumlarda bulabilirsiniz.
    Herunterladen
    1063816.9K
  13. TryHackMe✓@tryhackme
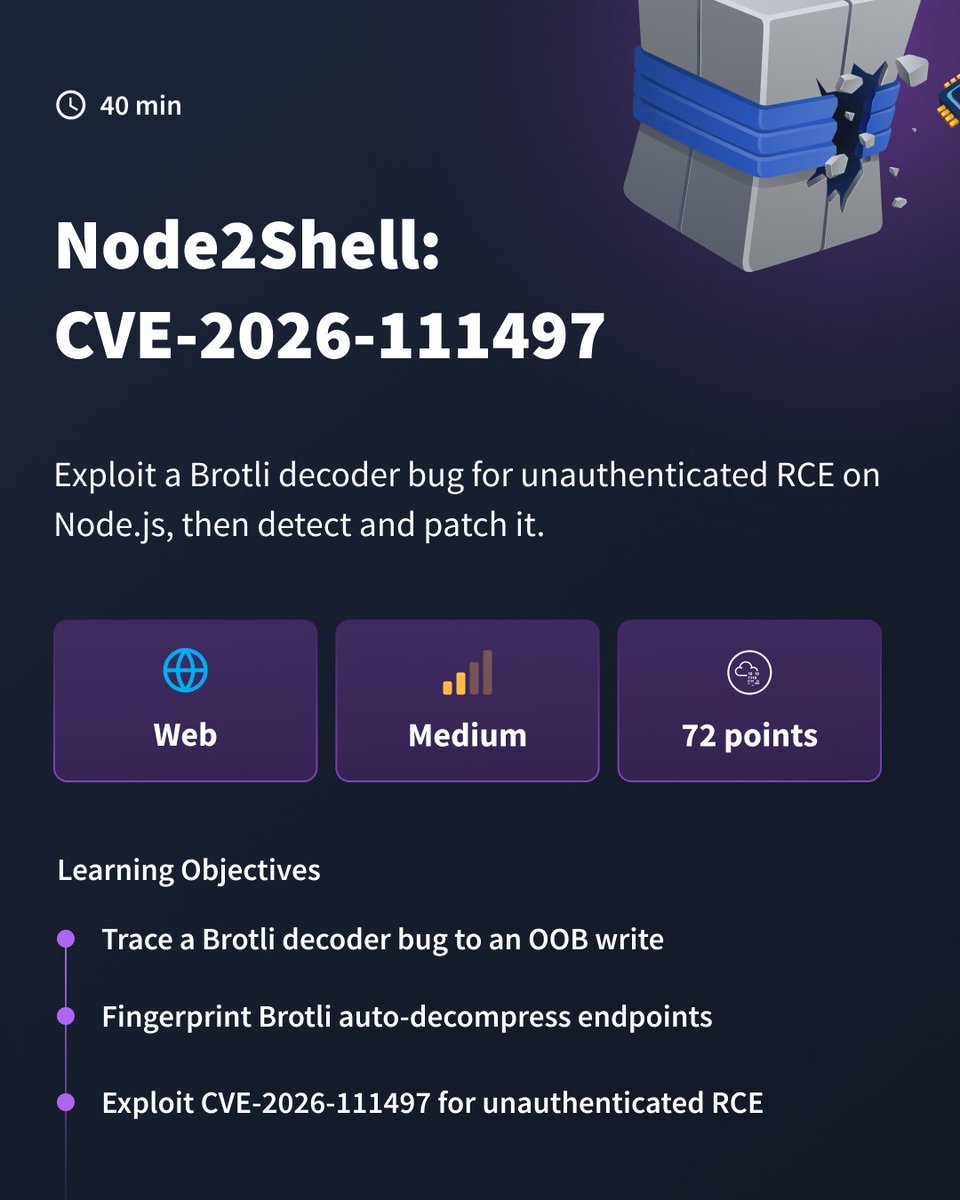
    🚨 Node2Shell (CVE-2026-111497) is here. We're ALREADY teaching you how to exploit it ⚡A Node.js Brotli decoder bug can lead to unauthenticated RCE. Our NEW threat room lets you exploit, detect & patch it yourself. 🔥 🔗
    Herunterladen
    21417911.8K
  14. Ritesh Roushan✓@devXritesh
    If you had to build a backend capable of handling 1 million requests/day, which tech stack would you choose? A) Java + Spring Boot B) Node.js + NestJS C) Python + FastAPI D) Go + Gin
    581769.4K
  15. dbugs✓@ptdbugs
    A PoC/exploit has been discovered for vulnerability CVE-2026-105482 PT ID: PT-2026-120548 Read on dbugs: Vendor: nodejs Product: node Description: A flaw in Node.js DNS resolution allows hostnames containing a NUL byte to be silently truncated by the dns.resolve*() functions and dns.reverse(). This is an incomplete fix of CVE-2026-48930, which only covered dns.lookup() and the net/tls host options. Because the name is passed to c-ares as a C string, resolving attacker.example\0.trusted.example queries attacker.example and returns its records without any error. Applications that validate a hostname, for example against a domain allowlist, and then resolve it with dns.resolve*() can act on records for a different name than the one they validated. This vulnerability affects Node.js 26.x, 24.x, and 22.x. Link:
    04364.1K
  16. Guillermo Rauch✓@rauchg
    I love how quickly our team works to bring the latest LTS and security upgrades for @nodejs. Should be a nice performance boost given 𝚏𝚎𝚝𝚌𝚑 now uses HTTP/2 by default, and agents produce a lot of network traffic
    Vercel Developers @vercel_dev
    Node.js 26 LTS is now available on Vercel. ▪︎ Default for all new projects ▪︎ HTTP/2 by default for built-in 𝚏𝚎𝚝𝚌𝚑 ▪︎ Temporal API for dates and time zones ▪︎ V8 14.6 JavaScript engine
    61638836.5K
  17. Vercel Developers✓@vercel_dev
    Node.js 26 LTS is now available on Vercel. ▪︎ Default for all new projects ▪︎ HTTP/2 by default for built-in 𝚏𝚎𝚝𝚌𝚑 ▪︎ Temporal API for dates and time zones ▪︎ V8 14.6 JavaScript engine
    42340854.8K
  18. Kashaf✓@noor36758
    If you were starting backend development in today's tech market which stack would you choose 👀 A) Node.js + Express + MongoDB B) Java + Spring Boot + PostgreSQL C) Python + FastAPI + PostgreSQL D) Go + PostgreSQL
    84513320K
  19. Mehr Beiträge anzeigen