Berichten met #nodeJS

#nodeJS

Openbare berichten op X die #nodeJS gebruiken.

Gerelateerde hashtags

  1. Node.js✓@nodejs
    Node.js 24.22.2 “Krypton” (LTS) is here! 🚀 Includes V8 backports and a fix that keeps async context in parked stream writes. 🔗 Full changelog and download links:
    125548337.7K
  2. The Hacker News@TheHackersNews
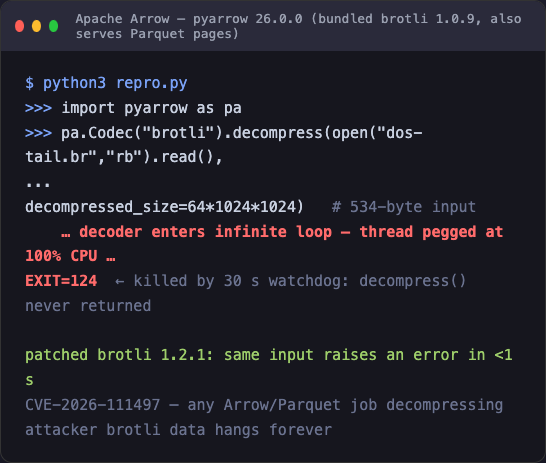
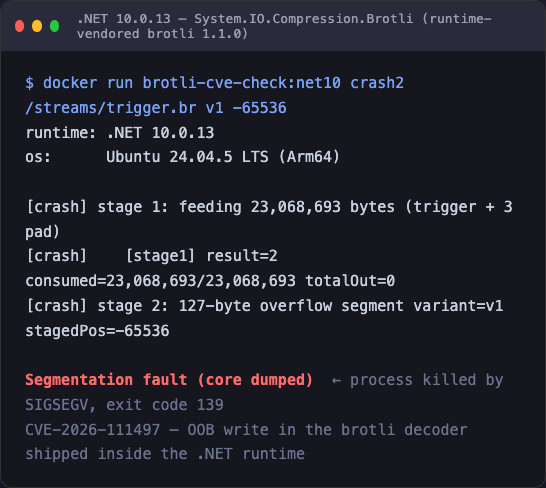
    🚨 UPDATE: The Brotli flaw (CVE-2026-111497) goes beyond Node.js and web traffic. • .NET: patched by Microsoft • FFmpeg: hit via a crafted JPEG XL image • ClickHouse: one request crashes it, fix not yet released • Apache Arrow: no fix yet Details ↓
    Downloaden
    3518386388.5K
  3. The Hacker News@TheHackersNews
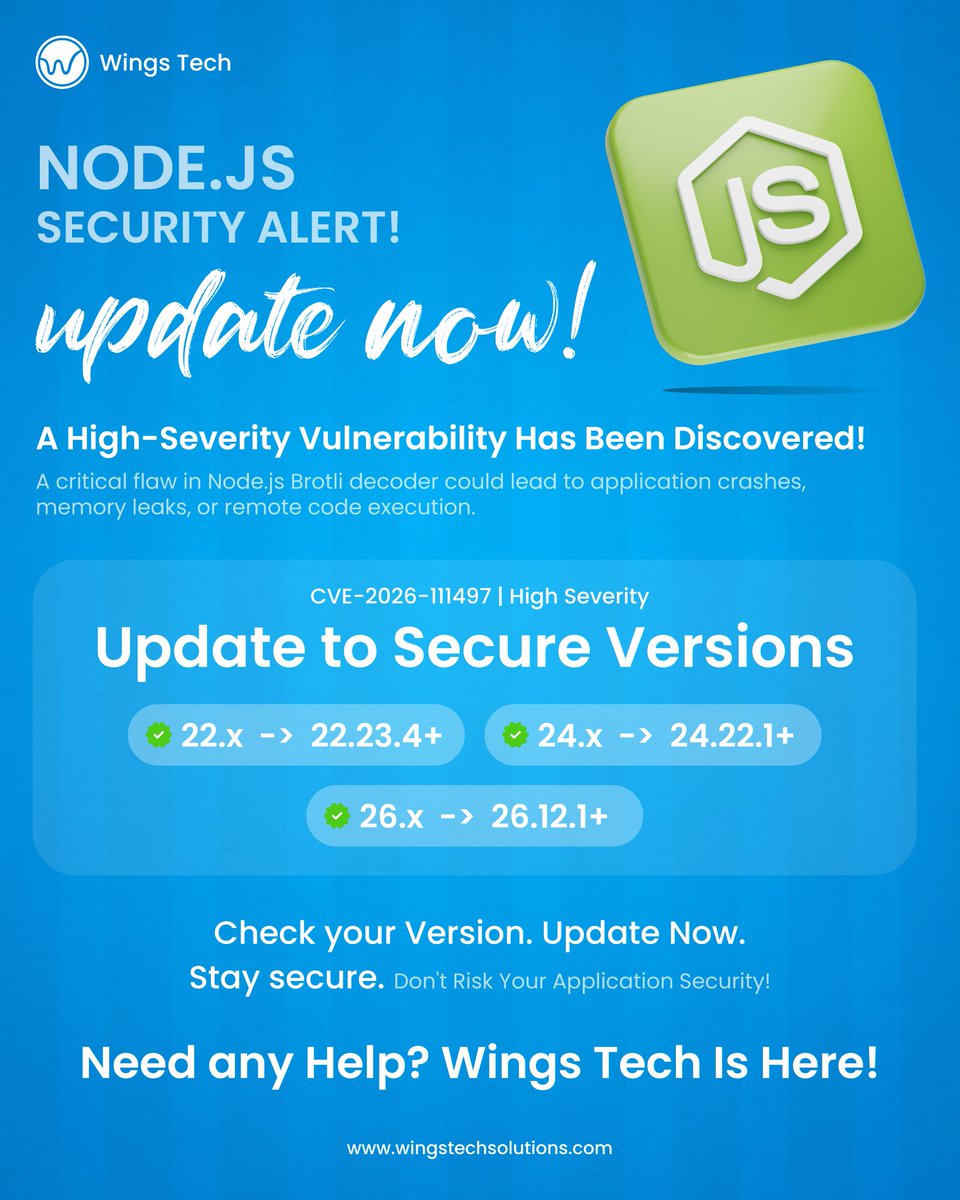
    🚨 UPDATE: Node2Shell (CVE-2026-111497) has moved from PoC to the wild. Scanning is live and the first exploit attempts are out. The RCE is now confirmed on STOCK x86-64 Node.js, not just arm64. Patch now → 22.23.4 / 24.22.1 / 26.12.1 Read ↓
    Downloaden
    2617685593.9K
  4. Node.js✓@nodejs
    Node.js 26 “Lithium” is now Long Term Support 🎉 v26.13.0 is out, with updates through April 2029. Heads-up for Linux users coming from an earlier LTS: libatomic may need to be installed separately.
    233422.1K131K
  5. Node.js✓@nodejs
    🔐 Node.js security updates are now available! New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues. Review the details and update your systems to stay secure. 🔗 #NodeJS #Security
    1363K12.6K1.3M
  6. Evolu✓@evoluhq
    0042.4K
  7. Rafael Gonzaga✓@_rafaelgss
    Node.js 27 Alpha is out! 💚 First release of the new model: Alpha until April, Current on 2027-04 and LTS on 2027-10. What's new: * V8 15.6 🚀 * OpenSSL 4.1, npm 12.1 * --allow-env permission 🔍 * Native fs.glob, net/promises ⚡ * domain deprecated
    73225044.2K
  8. NestJS@nestframework
    🚀 Introducing the Node adapter, new in NestJS 12.3. Nest has always stood on Express or Fastify. Now it stands on its own, right on node:http: the fastest way to run Nest. Nest is the fast part of your requests. NestJS Observe shows you the rest.
    Downloaden
    294967936K
  9. Abdullah@Abdulla_data_ai
    Ever wonder why your Node.js app chokes under heavy load while your multi-core CPU sits almost completely idle? Most devs treat single-threaded limits as just part of the deal. They aren't. Read more here: #nodejs #SoftwareEngineering #javascript
    00151
  10. Guillermo Rauch✓@rauchg
    I love how quickly our team works to bring the latest LTS and security upgrades for @nodejs. Should be a nice performance boost given 𝚏𝚎𝚝𝚌𝚑 now uses HTTP/2 by default, and agents produce a lot of network traffic
    Vercel Developers @vercel_dev
    Node.js 26 LTS is now available on Vercel. ▪︎ Default for all new projects ▪︎ HTTP/2 by default for built-in 𝚏𝚎𝚝𝚌𝚑 ▪︎ Temporal API for dates and time zones ▪︎ V8 14.6 JavaScript engine
    61638836.4K
  11. Vercel Developers✓@vercel_dev
    Node.js 26 LTS is now available on Vercel. ▪︎ Default for all new projects ▪︎ HTTP/2 by default for built-in 𝚏𝚎𝚝𝚌𝚑 ▪︎ Temporal API for dates and time zones ▪︎ V8 14.6 JavaScript engine
    42340854.7K
  12. Rapid7@rapid7
    🚨 On 10/21/26, the Node.js Project published a security advisory for CVE-2026-111497, an out-of-bounds write in the Brotli decoder bundled with Node.js. The vuln has the potential to disclose memory or enable RCE. More in our blog:
    Downloaden
    01103.1K
  13. Liberty Jnr 👩‍🍳✓@libertyjnr18
    I spent time trying to build with Node.js without constantly looking at a tutorial. And honestly, it humbled me. 😂 So far, I've built: A simple server A digital business card A quote API But getting them to work wasn't as smooth as I imagined. I tried writing code from memory. I forgot things. Bugs showed up. I had to Google errors, revisit things I'd learned, and figure out what I was doing wrong. One mistake I won't forget anytime soon? I forgot to add res.end() to my response. My API wasn't returning anything, and I had to figure out why. 😅 It was a small mistake, but it reminded me that sometimes, you can understand a concept while learning it and still forget an important detail when you're building on your own. But I kept debugging, searching, and trying again until I got the result I wanted. And that feeling when your code finally works after you've been struggling with it? Sweet. 😂 I'm learning that the goal isn't to remember every line of code perfectly. It's to understand what I'm building, know how to investigate problems, and keep improving when things don't work. I'm still at the beginning of this backend journey, but at least I'm no longer just watching someone else build. I'm building too. And I'm learning along the way. 🚀 For the developers here, what's one small bug or mistake that taught you a lesson you never forgot?
    Downloaden
    12430330
  14. FranCode 🧑‍💻@FidelisUkwuani
    Your zero-downtime reload is dropping payments if Nginx routes traffic before Node warms up its DB pool. Use a real health check first. How do you handle zero-downtime deploys? #backend #nodejs
    Downloaden
    00023
  15. chaos✓@konig0000
    Hiring Alert ! Full Stack AI Engineer urgently needed. ( To Resume Immediately ) Pay: $3500/month Tech Stack: Node.js, TypeScript, NestJS, Express.js, React.js, Next.js, OpenAI API, LangChain.js, RAG, Vector Databases, PostgreSQL, MongoDB, Redis, Docker, Kubernetes, AWS, GitHub Actions, Jenkins, Git, GitHub. Job Mode: Full Time Remote Role Share your best project link and resume link in the comments. J
    85514318.2K
  16. TryHackMe✓@tryhackme
    🚨 Node2Shell (CVE-2026-111497) is here. We're ALREADY teaching you how to exploit it ⚡A Node.js Brotli decoder bug can lead to unauthenticated RCE. Our NEW threat room lets you exploit, detect & patch it yourself. 🔥 🔗
    Downloaden
    21417811.8K
  17. WolfNoLies@Wolfboy_24
    Neue Sicherheitslücke: Broccoli2Shell Eine kritische RCE-Sicherheitslücke im Brotli-Decoder betrifft Node.js, Python & Co. Angreifer können über präparierte Daten Remote Code Execution ausführen! 💥 #CyberSecurity #NodeJS #DevOps #InfoSec #Broccoli2Shell
    204249
  18. Dark Coder✓@dark_coderz
    Your backend needs to handle 100,000 requests per second. Which framework are you trusting? A. Node.js + Express B. Python + FastAPI C. Go + Gin D. Java + Spring Boot
    101816743.8K
  19. Meer berichten tonen