Node.js 24.22.2 “Krypton” (LTS) is here! 🚀
Includes V8 backports and a fix that keeps async context in parked stream writes.
🔗 Full changelog and download links:
Node.js 26 “Lithium” is now Long Term Support 🎉
v26.13.0 is out, with updates through April 2029.
Heads-up for Linux users coming from an earlier LTS: libatomic may need to be installed separately.
🔐 Node.js security updates are now available!
New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues.
Review the details and update your systems to stay secure.
🔗
#NodeJS#Security
Node.js 27 Alpha is out! 💚
First release of the new model: Alpha until April, Current on 2027-04 and LTS on 2027-10.
What's new:
* V8 15.6 🚀
* OpenSSL 4.1, npm 12.1
* --allow-env permission 🔍
* Native fs.glob, net/promises ⚡
* domain deprecated
🚀 Introducing the Node adapter, new in NestJS 12.3.
Nest has always stood on Express or Fastify. Now it stands on its own, right on node:http: the fastest way to run Nest.
Nest is the fast part of your requests. NestJS Observe shows you the rest.
⚠️ Compartimos desde la Agencia Nacional de Ciberseguridad (#ANCI) información de parches de seguridad publicados para resolver vulnerabilidades en #NodeJS 26.x, 24.x y 22.x.
Más información:
🚨 UPDATE: Node2Shell (CVE-2026-111497) has moved from PoC to the wild.
Scanning is live and the first exploit attempts are out. The RCE is now confirmed on STOCK x86-64 Node.js, not just arm64.
Patch now → 22.23.4 / 24.22.1 / 26.12.1
Read ↓
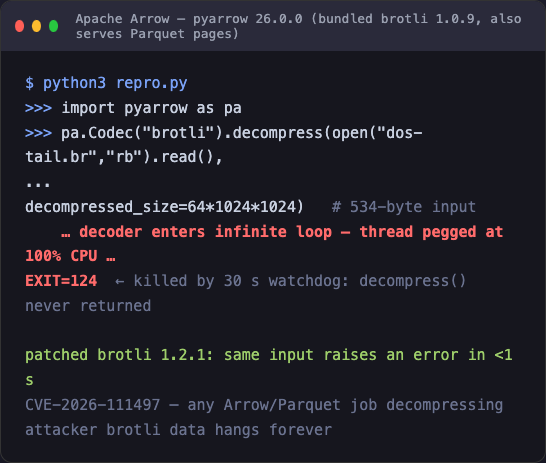
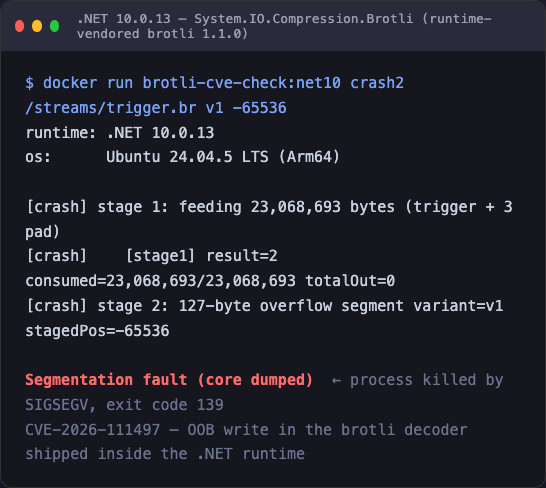
🚨 UPDATE: The Brotli flaw (CVE-2026-111497) goes beyond Node.js and web traffic.
• .NET: patched by Microsoft
• FFmpeg: hit via a crafted JPEG XL image
• ClickHouse: one request crashes it, fix not yet released
• Apache Arrow: no fix yet
Details ↓
Node2Shell, HTTP2Shell, Broccoli2Shell : une seule faille Brotli (CVE-2026-111497), et après Node.js, Python, .NET et Linux publient leurs correctifs.
Voici l'essentiel à savoir :
👉
#cybersécurité#python#dotnet
HIRING
Full Stack Developer (React.js + Node.js) | Sagegrey Tech
📍 Location: Lagos (Remote)
Job Type: Remote
Job Field: Software Development / IT
About the Role
Sagegrey Tech is seeking a Full Stack Developer to build and maintain web applications, develop user interfaces and APIs, manage databases, optimise performance, and support deployment throughout the software development lifecycle.
Key Responsibilities
• Develop responsive user interfaces using React.js and modern JavaScript/TypeScript.
• Build and maintain backend applications and APIs using Node.js, NestJS, or Express.js.
• Design, manage, and optimise databases.
• Integrate REST APIs and implement secure authentication systems.
• Write clean, maintainable code following software architecture and design principles.
• Troubleshoot, debug, and optimise application performance.
• Use Git and collaborative development workflows.
Requirements
• Strong experience with React.js and JavaScript/TypeScript.
• Solid knowledge of Node.js and NestJS and/or Express.js.
• Proficiency in Tailwind CSS and responsive design.
• Experience with MongoDB, PostgreSQL, and MySQL.
• Understanding of REST APIs, database design, query optimisation, and ORM tools.
• Knowledge of JWT, OAuth, and session management.
• Familiarity with Git, software architecture, clean code, and design patterns.
• Strong debugging and problem-solving skills.
How to Apply
Interested candidates should send their CV to:
📧 Apply via: hr@sagegreytech.com
Your backend needs to handle 100,000 requests per second.
Which framework are you trusting?
A. Node.js + Express
B. Python + FastAPI
C. Go + Gin
D. Java + Spring Boot
You're building a video platform for 20 million users.
What's your backend stack?
(A) Go + Kubernetes + Redis
(B) Java + Spring Boot + Kafka
(C) Node.js + NestJS + PostgreSQL
(D) Python + FastAPI + Celery
Which one scales best in your opinion?
🚨 Node2Shell (CVE-2026-111497) is here. We're ALREADY teaching you how to exploit it ⚡A Node.js Brotli decoder bug can lead to unauthenticated RCE. Our NEW threat room lets you exploit, detect & patch it yourself. 🔥
🔗
🚨 On 10/21/26, the Node.js Project published a security advisory for CVE-2026-111497, an out-of-bounds write in the Brotli decoder bundled with Node.js.
The vuln has the potential to disclose memory or enable RCE. More in our blog: