Beiträge mit #patch
#patch
Öffentliche Beiträge auf X, die #patch verwenden.
Verwandte Hashtags


Had to figure this was coming! Pure speculation, but I think this could be one of the biggest balance patches Deadlock has ever had. TONS of potential changes could come through on this one.Deadlock Intel @IntelDeadlockThere will be a balance patch soon, per Yoshi16877329.3K
There will be a balance patch soon, per Yoshi13454717.7K1M
Critical 'HTTP2Shell' Brotli vulnerability triggers emergency patches53111416.6K
CVE-2020-1350 represents significant risk to Windows DNS servers. #Patch or apply the mitigation steps today, you should expect adversaries are hard at work writing exploits for this #vulnerability. Check out our detailed guidance:10118172
1325527K923K
lemon@childe_loveeEnjoy your low cost dps they will die in a 5 patches but my e2 merchants will die in 6 !!1013316
Yikes a hardware issue could have been better. If I'm not mistaken it's probably bc of the Ruby RCE issue from the past week. It corrupts memory and injects code so happy to know that the data is intact but they are probably better closing the site until future patchesAO3 Status @AO3_StatusEarlier today, we detected evidence of a security incident on #AO3. We are still in the early stages of investigating. No AO3 data has been deleted. All your works, bookmarks, kudos, etc., are safe. Learn more at9851.1K40.4K
AO3 Status@AO3_StatusEarlier today, we detected evidence of a security incident on #AO3. We are still in the early stages of investigating. No AO3 data has been deleted. All your works, bookmarks, kudos, etc., are safe. Learn more at2.4K21.6K226K9.3M
FYI I've not seen any proof of an in the wild victim exists for #PHP2SHELL I've seen claims but zero proof. That doesn't mean it hasn't occurred.... I believe it WILL OCCUR to a level (I don't believe this will be a major internet/world ending event, I even blogged last week on why I don't, and I bloody hate having to do that!) But that aside... keep patching, config hardening, improving! remember back ports exist! you can be running version x.y.z and if it's back ported it it will have the fixes. 618/619) and the other CVE needs a config change! I feel this weeks been insane! not totally unlike weeks from years ago in some respects, this is nothing new to the cyber world (thematically) except this week we've had the MOST batshit insane: > AI SLOP > AI POC SLOP > AI Analysis ----- what has gone well: > Notification on Tuesday (due to the leak) > Great work getting patches out early > Great work on initial assessments >> this part is hard, but I think Wednesdays morning/day the analysis was reasonably ok (I won't say good till a few weeks time at least) > Good comms and intel sharing > Good response from community people who use science not FUD > Patching (hard to tell, but me and friends all went to work fast and the vibe I've got from people (ignoring vendor % claims because I think they are wrong!) is that they have been doing the work > Research, intel, monitoring, collab... (so same as normal, the 'security' process: WORKS!) what has been insane: > AI SLOP everywhere > THE FUD.. has been ridiculous > The HYPE has been insane > The wrong analysis (at least one vendor got it wrong, then at least said later, we got it wrong, kudos for being honest!) ------ and probably more ------- the insane part has been exhausting, the insane parts I believe are MORE of a THREAT than the actual technical exploitation parts! Bad intel, bad decision making, bad investments, bad prioritisation etc. is something that can create NATSEC risks etc. (let alone org specific risks!) ==== ok back to the pews! I've got to travel today so I'm probably going to be quiet on this mostly. Other than monitoring the sizzle (unless I'm driving!) Thanks to friends far and wide! This is a team sport, the madness doesn't help, cool, calm heads do!80422.9K
Tanya Janca | Shehackspurple@shehackspurplePatching a vulnerability doesn't kick an attacker out of your system. We've been talking about PHP2Shell for almost a week now. The patches are available, and hopefully everyone has been updating. But there's an important new development. 1/941610830.2K
Sam Stepanyan@securestep9#Linux zero-click root - CVE-2026-98432 - Claude wrote an exploit that gives a remote attacker root access on Linux servers running a multipath TCP listener. It needs no login and no user action. Patches released: 👇82212123.3K
Michele Media@MikeleMediaThe latest revision of HyperHEN featuring a few minor additions and all the patches applied for each firmware profile is set to be released shortly.71524.9K
🦇 v1.1.0: Tiny Update 🤏 🦇 Available on all platforms on Nov 24th! - 2 Extra Achievements ✅ - 1 new Power Up 💪 - 1 new Challenge Stage 🌉 - 1 new Secret 🤫 #VampireSurvivors #patch #newcontent #Steam #GamePass952821.7K
82969
Apple backports CoreGraphics zero-day patches to older iPhones129539.3K
Senumy@senumy_ipa🚀 3105 IPA is HERE! 🔥 Customize & Manage Your iPhone Like Never Before! 📱 iOS 17–18, 26–27 Dev Beta 2 • Content Marketplace • Dialer Themes & Wallpapers • App Patches • File Manager + Plist Editor • Backup & Restore • Cleaner Tool 📥51010720.8K
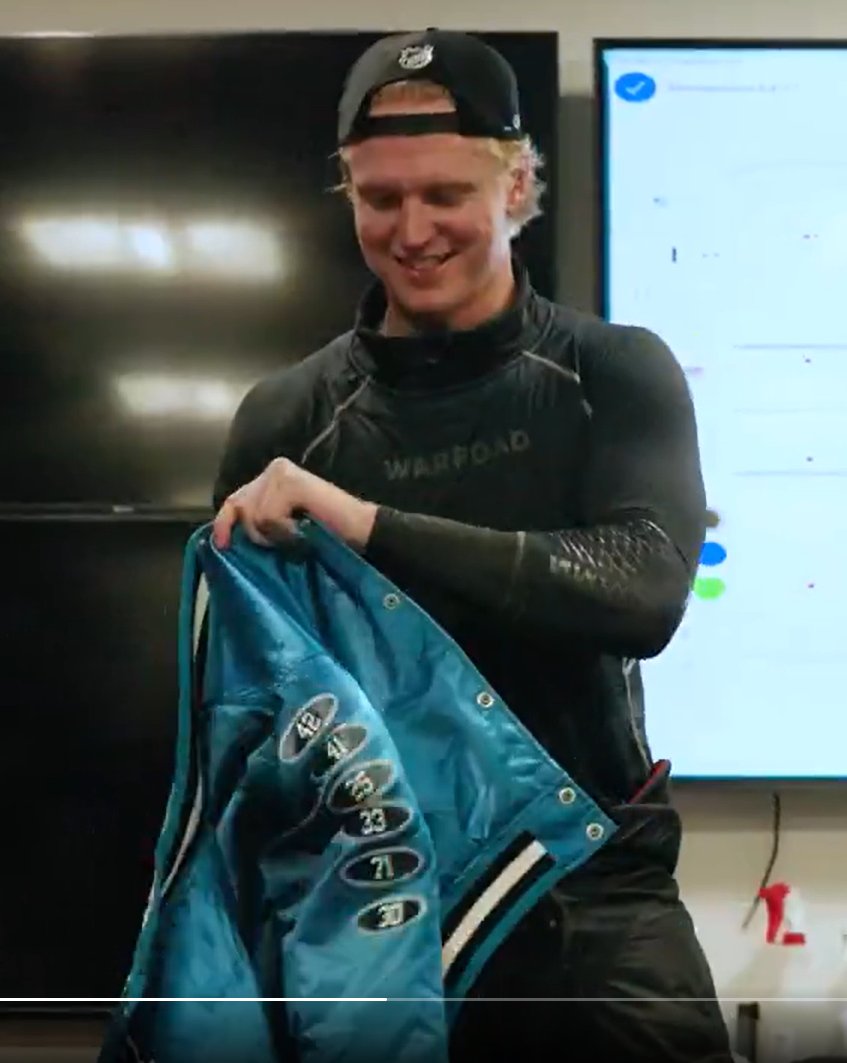
Sky Atled@Sky_Atled@SanJoseSharks@SanJoseSharks Are they adding patches with the number of the player that gets it?🥹🥹0131675.5K- Mehr Beiträge anzeigen