Berichten met #Spring4Shell

#Spring4Shell

Openbare berichten op X die #Spring4Shell gebruiken.

Gerelateerde hashtags

  1. Pentester Academy@SecurityTube
    🧵 #Spring4Shell Vulnerability Explained Learn how a Java 9 architectural change led to a critical RCE vulnerability affecting millions of Spring applications. Includes technical deep dive, impact analysis, and actionable mitigation strategies.
    128969
  2. Snyk@snyksec
    ⚠️ While #Spring4Shell doesn't appear to have the same impact as #Log4Shell, it should still be evaluated and prioritized by every organization using the Spring Framework. This post explores how the #ZeroDay #RCE vulnerability works and how to mitigate.
    0615
  3. LunaSec (@[email protected])@LunaSecIO
    We've published an analysis of the #Spring4Shell RCE to help provide better "facts" about what we know so far. There are 2 vulnerabilities and people are confusing them. Note: This post is Markdown on GitHub if you'd like to add anything (link in thread).
    3127261
  4. Sonatype✓@sonatype
    ⛔️ Early this morning we started seeing buzz about a new remote code execution flaw that affects #SpringCore. Our Field CTO @llkkaT provides all the info on #Spring4Shell: 💭 What it is 💭 Everything you need to know 💭 Where to go from here ⛓️
    Downloaden
    11146
  5. Alvaro Muñoz@pwntester
    #Spring4Shell details are now public, It is an old ClassLoader Manipulation. Actually, CVE-2022-22965 is just a bypass of the 12 years old CVE-2010-1622 (
    581205
  6. LetsDefend✓@LetsDefendIO
    We created #Spring4Shell SIEM alert on LetsDefend, you can investigate it as an Incident Responder right now.
    Downloaden
    01247
  7. Pentester Academy@SecurityTube
    🧵 New Blog: Spring4Shell Vulnerability Explained Learn how a Java 9 architectural change led to a critical RCE vulnerability affecting millions of Spring applications. Must-read for #Java devs & #AppSec teams #Spring4Shell #InfoSec
    0371.1K
  8. Snyk@snyksec
    🚨 A fixed version for CVE-2022-22965 (#Spring4Shell) has been issued. At this time, we recommend upgrading to spring-beans version 5.2.20, 5.3.18, or higher and have updated our advisory published on Mar. 30:
    Downloaden
    0715
  9. DFN-CERT | @[email protected]@DFNCERT
    Nach Gerüchten früher am Tag gibt es jetzt (weiterhin unbestätigte) Informationen zu #SpringShell / #Spring4Shell (0Day RCE in Spring Framework). Wir gucken. src 🍿 übersetzung 🧐 YARA (WebShells) ☕️
    vx-underground @vxunderground
    A Java Springcore RCE 0day exploit has been leaked. It was leaked by a Chinese security researcher who, since sharing and/or leaking it, has deleted their Twitter account. We have not verified the exploit. tl;dr big if true Download the 0day POC here:
    158
  10. vx-underground✓@vxunderground
    A Java Springcore RCE 0day exploit has been leaked. It was leaked by a Chinese security researcher who, since sharing and/or leaking it, has deleted their Twitter account. We have not verified the exploit. tl;dr big if true Download the 0day POC here:
    293891K
  11. INE@ine
    #Spring4Shell (CVE-2022-22965) Remote Code Execution (RCE) was discovered in Spring Core running JDK version 9 (or later). We’ve created a lab to show you how to exploit the #vulnerability. Watch, then get more exploits here: #demo #java .
    Downloaden
    21543
  12. Alvaro Muñoz@pwntester
    This is the patch for #Spring4Shell preventing access to Module.getClassLoader() I used a similar technique to bypass Apache Velocity SecureUberspector (CVE-2020-13936), and the fix was identical Account for class hierarchies!
    2947
  13. Sebastian Bicchi✓@secresDoge
    "#Spring4Shell" facts Thread. (1) It is not Log4Shellv2. (2) "Spring4Shell" has nothing to do with CVE-2022-22963 (which is a valid RCE in apps that use spring cloud) (3) The posted fix (#28075) about insecure deserialization has nothing to do with this claimed vulnerability.
    31325
  14. Alvaro Muñoz@pwntester
    Do not understand people overhyping some vulns but underhyping #spring4shell. Just run a #CodeQL query on 9340 spring projects hosted on GitHub. 7203 are vulnerable (if depoyed as WARs on Tomcat). Thats 3 out of 4 projects!
    251192
  15. Checkmarx✓@Checkmarx
    @Checkmarx
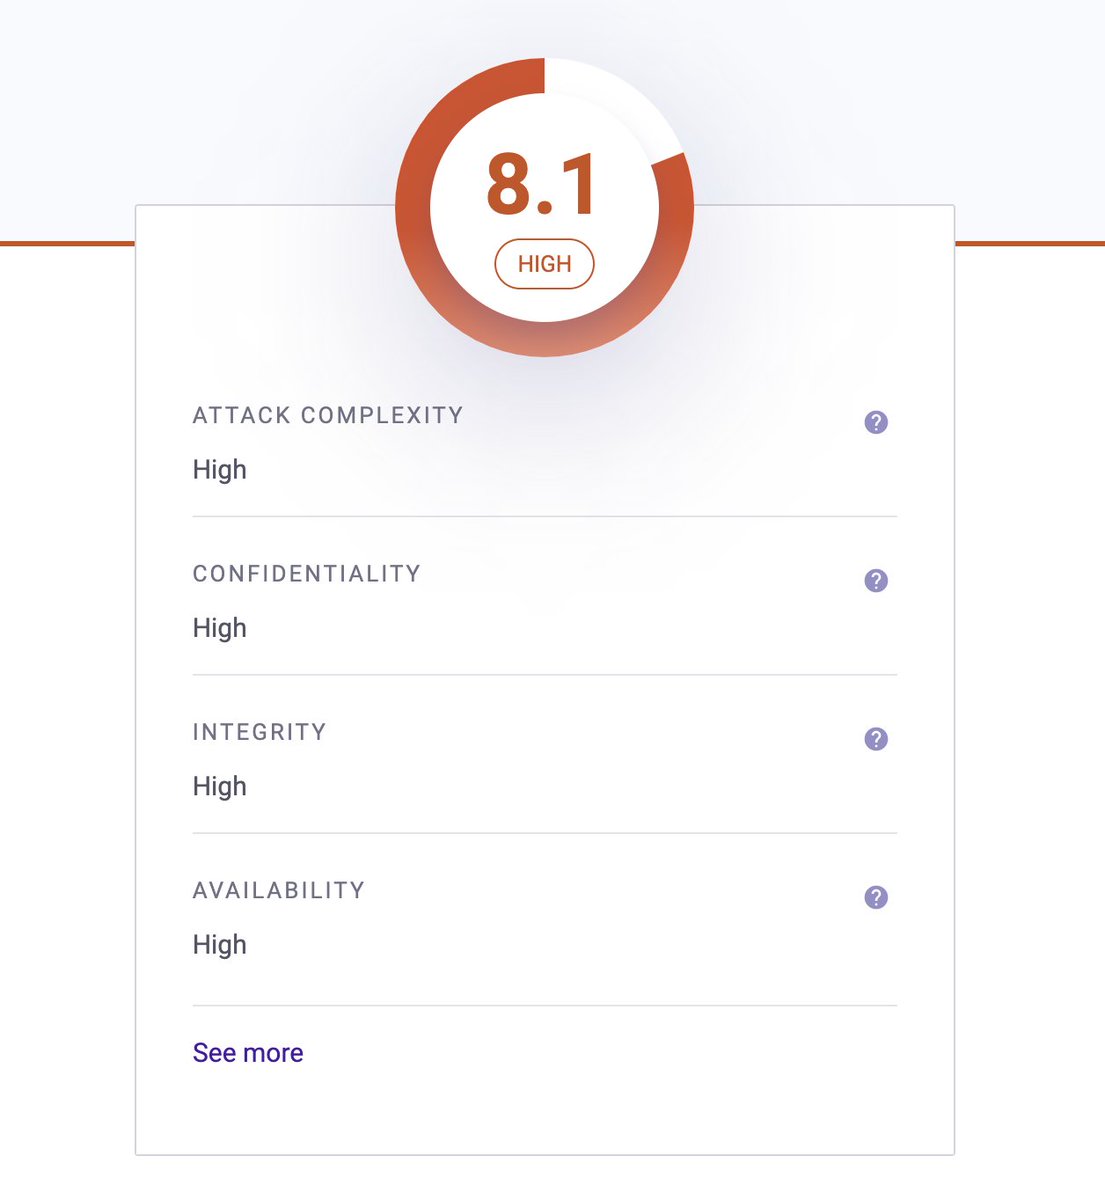
    Update: #Spring4Shell is now CVE-2022-22965, with a HIGH CVSS score of 8.1
    215
  16. GreyNoise✓@GreyNoiseIO
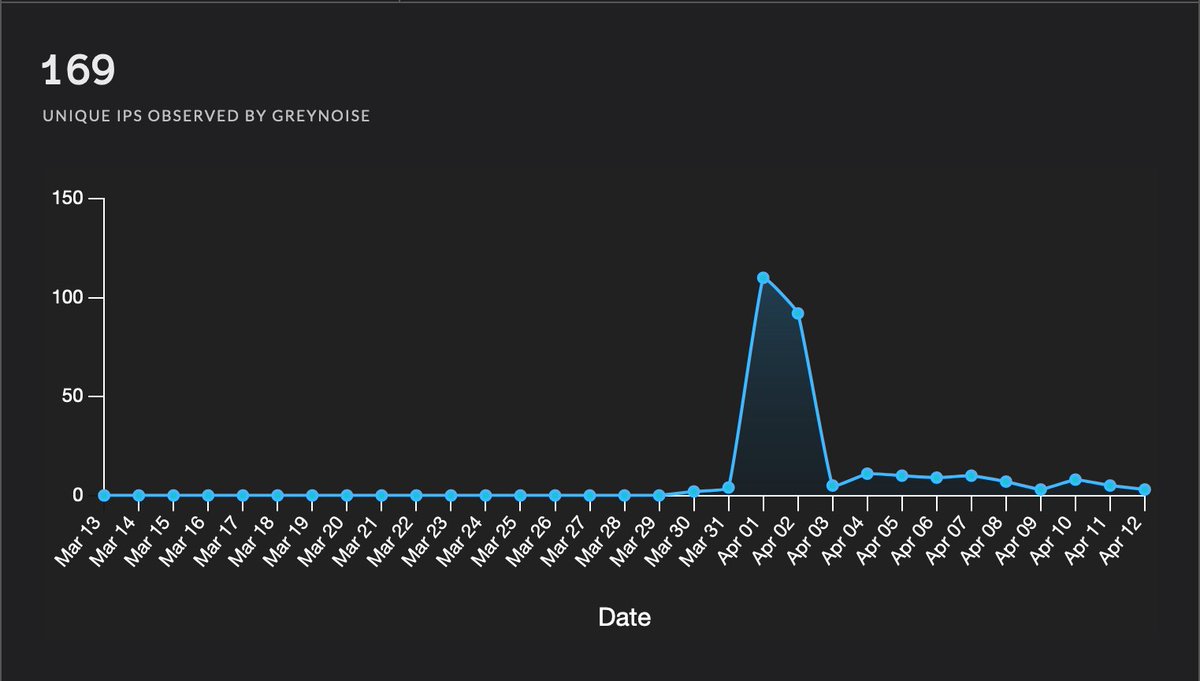
    GreyNoise has not observed significant activity related to CVE-2022-22965, colloquially known as #Spring4Shell, since April 2, 2022.
    Downloaden
    0316
  17. Meer berichten tonen