Posty z #Spring4Shell

#Spring4Shell

Publiczne posty w X, które używają #Spring4Shell.

Powiązane hashtagi

  1. Ax Sharma@Ax_Sharma
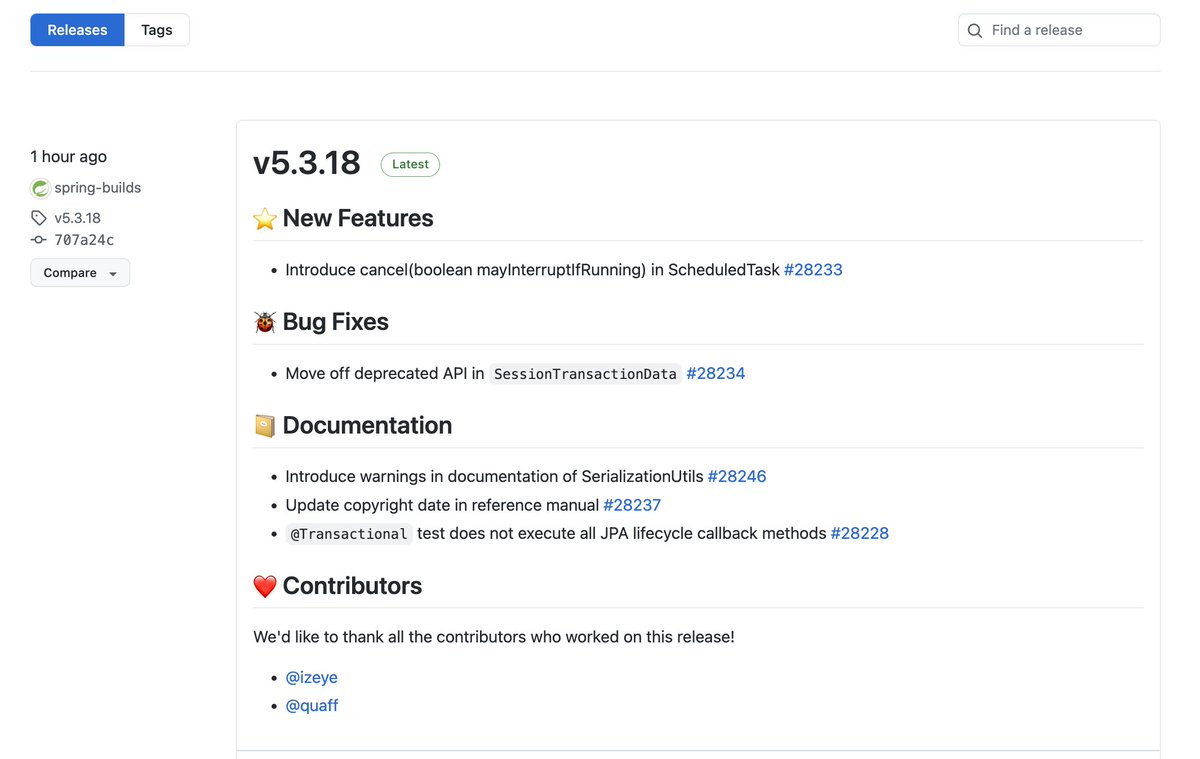
    📢 AFTER much commotion and speculation Spring has *CONFIRMED* #SpringShell and in addition to a new release 5.3.18, also backported fix into 5.2.20. CVE pending. h/t @llkkaT #Spring4Shell
    Ax Sharma @Ax_Sharma
    🆕 Spring has a NEW 5.3.18 release today (h/t @madpah @sonatype) that just hit Maven Central. Release touches the 'CachedIntrospectionResults' class—after 2 years. The same class that's stated to be responsible for #SpringShell and older CVE-2010-1622 💥
    139
  2. Ax Sharma@Ax_Sharma
    @Ax_Sharma
    🆕 Spring has a NEW 5.3.18 release today (h/t @madpah @sonatype) that just hit Maven Central. Release touches the 'CachedIntrospectionResults' class—after 2 years. The same class that's stated to be responsible for #SpringShell and older CVE-2010-1622 💥
    Pobierz
    034
  3. Checkmarx✓@Checkmarx
    Checkmarx is closely monitoring #Spring4Shell and all other Spring vulnerabilities (CVE-2022-22963, CVE-2022-22950). Checkmarx SCA customers can scan their code for those vulnerabilities and get the latest remediation solutions. #springshell
    156
  4. LunaSec (@[email protected])@LunaSecIO
    We've published an analysis of the #Spring4Shell RCE to help provide better "facts" about what we know so far. There are 2 vulnerabilities and people are confusing them. Note: This post is Markdown on GitHub if you'd like to add anything (link in thread).
    3127262
  5. Pentester Academy@SecurityTube
    🧵 #Spring4Shell Vulnerability Explained Learn how a Java 9 architectural change led to a critical RCE vulnerability affecting millions of Spring applications. Includes technical deep dive, impact analysis, and actionable mitigation strategies.
    128969
  6. Sonatype✓@sonatype
    ⛔️ Early this morning we started seeing buzz about a new remote code execution flaw that affects #SpringCore. Our Field CTO @llkkaT provides all the info on #Spring4Shell: 💭 What it is 💭 Everything you need to know 💭 Where to go from here ⛓️
    Pobierz
    11146
  7. Snyk@snyksec
    ⚠️ While #Spring4Shell doesn't appear to have the same impact as #Log4Shell, it should still be evaluated and prioritized by every organization using the Spring Framework. This post explores how the #ZeroDay #RCE vulnerability works and how to mitigate.
    0615
  8. TrendAI™ Research✓@trendai_RSRCH
    Our blog entry looks at the technical details behind attempts to exploit the #Spring4Shell vulnerability, including how they create web shells to deploy cryptocurrency miners. More details in our post:
    Pobierz
    1331
  9. Checkmarx✓@Checkmarx
    @Checkmarx
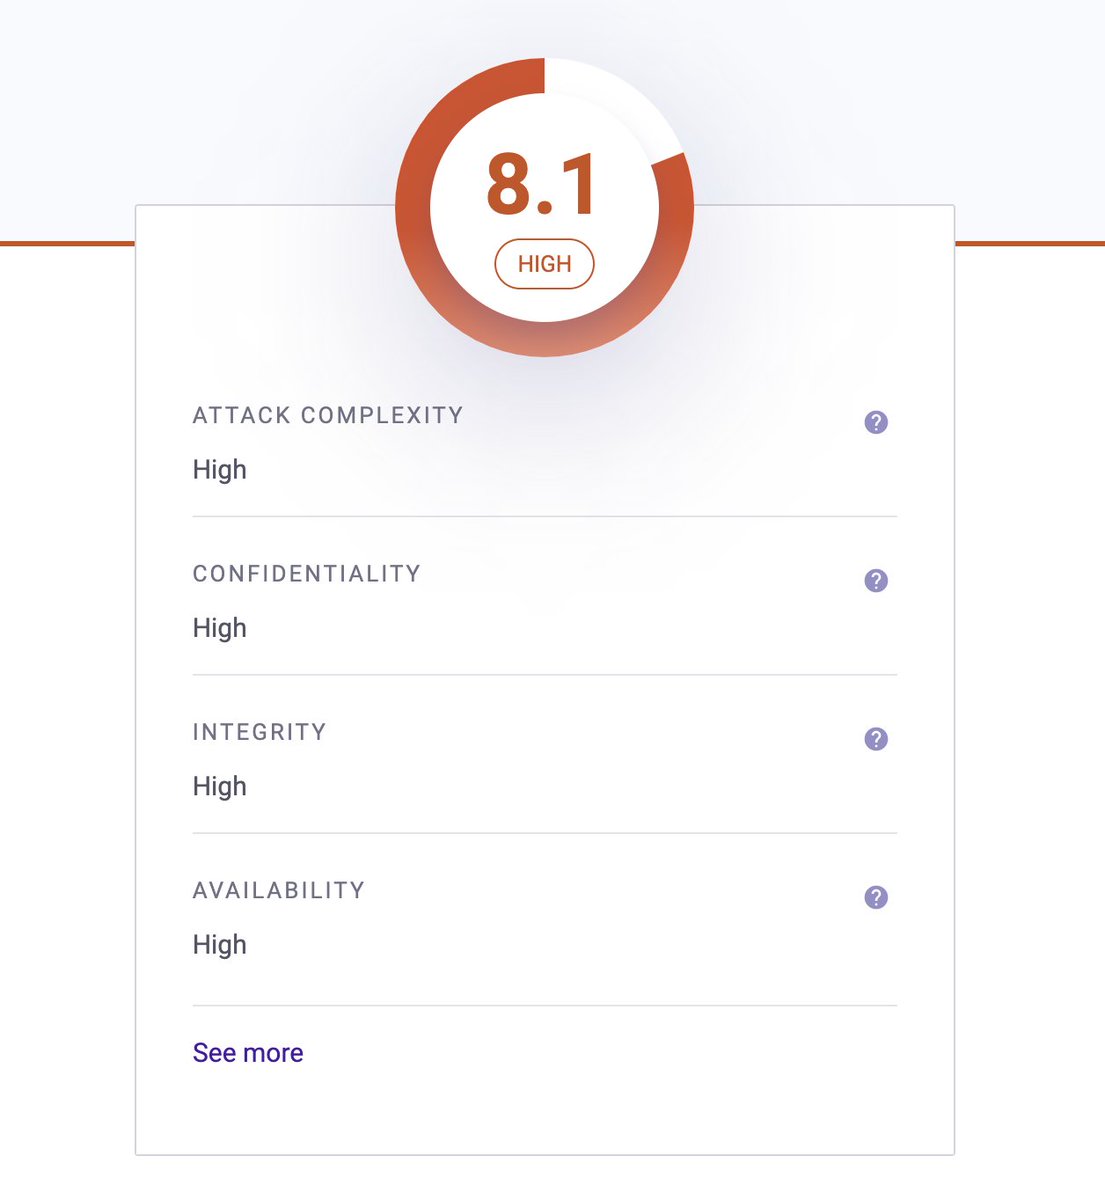
    Update: #Spring4Shell is now CVE-2022-22965, with a HIGH CVSS score of 8.1
    215
  10. Snyk@snyksec
    🚨 A fixed version for CVE-2022-22965 (#Spring4Shell) has been issued. At this time, we recommend upgrading to spring-beans version 5.2.20, 5.3.18, or higher and have updated our advisory published on Mar. 30:
    Pobierz
    0715
  11. GreyNoise✓@GreyNoiseIO
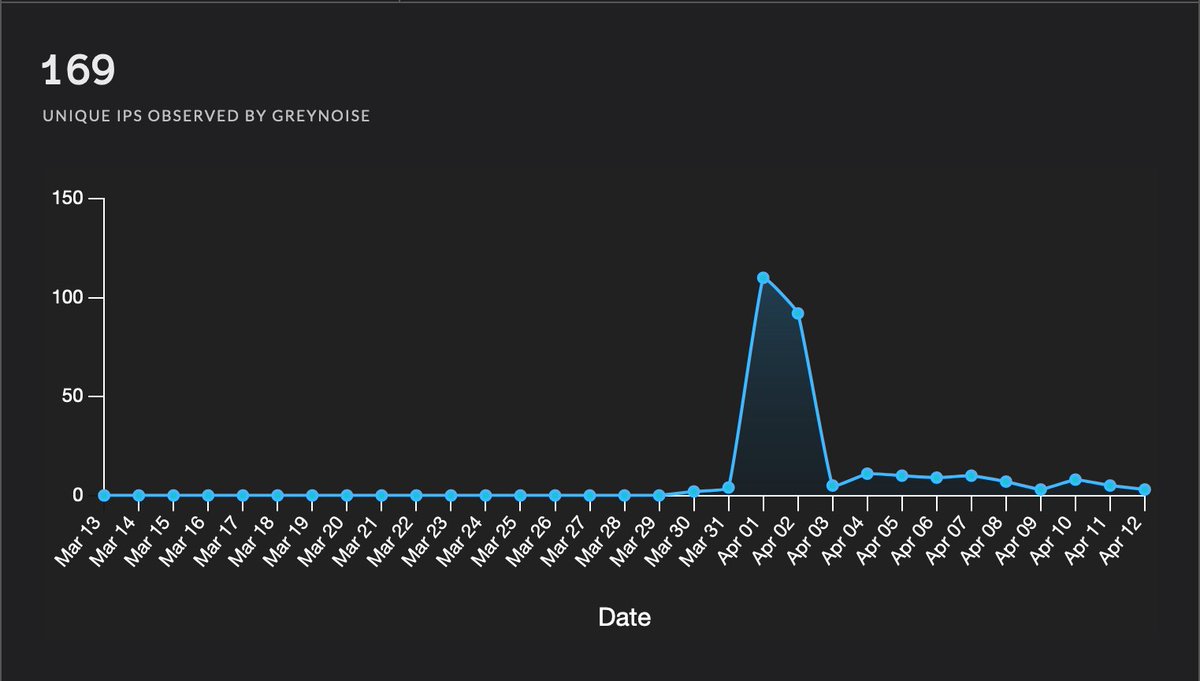
    GreyNoise has not observed significant activity related to CVE-2022-22965, colloquially known as #Spring4Shell, since April 2, 2022.
    Pobierz
    0316
  12. LetsDefend✓@LetsDefendIO
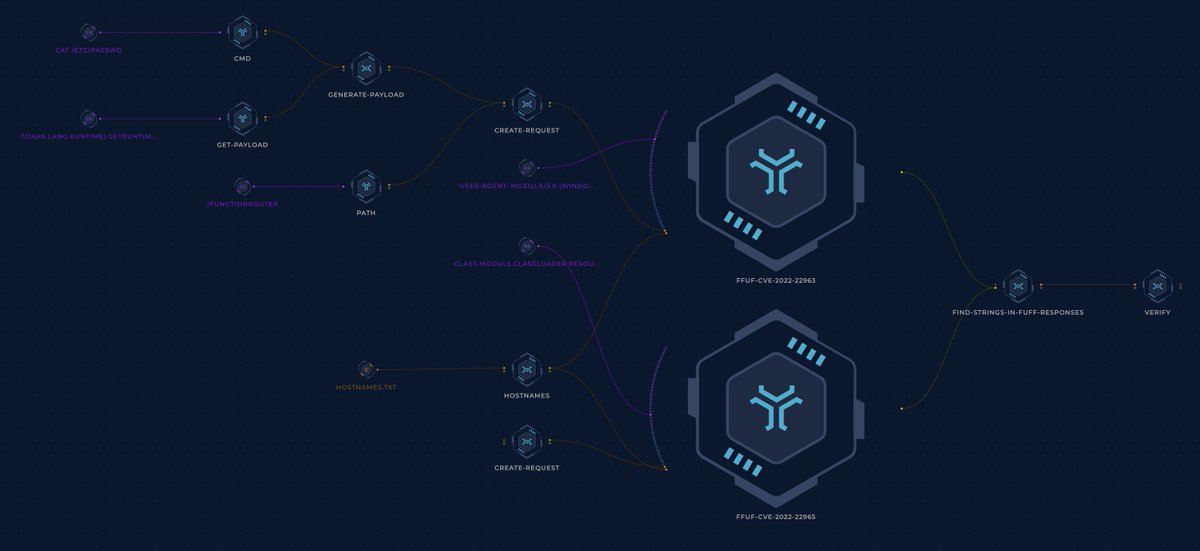
    We created #Spring4Shell SIEM alert on LetsDefend, you can investigate it as an Incident Responder right now.
    Pobierz
    01247
  13. Checkmarx✓@Checkmarx
    @Checkmarx
    Update: Confused about the various #spring vulnerabilities out there? Check out our latest blog with technical analysis of all three CVEs, their affected versions, and mitigations. #spring4shell #springshell
    058
  14. Rapid7@rapid7
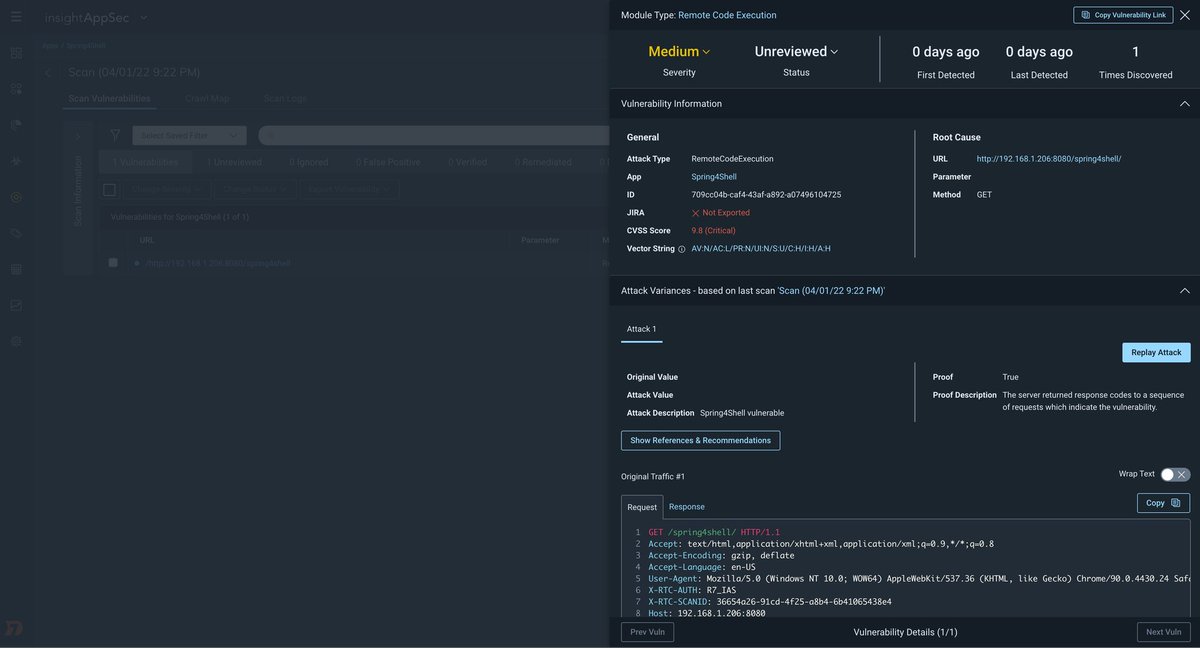
    On our blog, we have a quick walk through of recent product enhancements across our application security portfolio to help customers test and secure their apps against #Spring4Shell. 🔐 Read more:
    Pobierz
    116
  15. Pentester Academy@SecurityTube
    🧵 New Blog: Spring4Shell Vulnerability Explained Learn how a Java 9 architectural change led to a critical RCE vulnerability affecting millions of Spring applications. Must-read for #Java devs & #AppSec teams #Spring4Shell #InfoSec
    0371.1K
  16. Rapid7@rapid7
    New emergent threat response: “#Spring4Shell: Zero-Day Vulnerability in Spring Framework (CVE-2022-22965).” Read our blog overview of what you need to know ⤵️ Note: we will continue to update this blog as more information becomes available.
    039
  17. Pokaż więcej postów