Posts with #Spring4shell

#Spring4shell

Public posts on X that use #Spring4shell.

Related hashtags

  1. LunaSec (@[email protected])@LunaSecIO
    We've published an analysis of the #Spring4Shell RCE to help provide better "facts" about what we know so far. There are 2 vulnerabilities and people are confusing them. Note: This post is Markdown on GitHub if you'd like to add anything (link in thread).
    3127262
  2. Alvaro Muñoz@pwntester
    #Spring4Shell details are now public, It is an old ClassLoader Manipulation. Actually, CVE-2022-22965 is just a bypass of the 12 years old CVE-2010-1622 (
    581205
  3. Pentester Academy@SecurityTube
    🧵 #Spring4Shell Vulnerability Explained Learn how a Java 9 architectural change led to a critical RCE vulnerability affecting millions of Spring applications. Includes technical deep dive, impact analysis, and actionable mitigation strategies.
    128969
  4. Florian Roth ⚡️✓@cyb3rops
    #Spring4shell - good news and bad news Good: It's less prevalent than initially expected Bad: It's not up to the administrators. They can't solve the problem with a patch. It seems to be the developers task to find vulnerable apps and deploy a fix in form of code.
    746147
  5. Florian Roth ⚡️✓@cyb3rops
    There’s a significant number of prerequisites for #Spring4Shell We don’t know how many applications are vulnerable but it’s far less serious than initially expected
    Download
    242130
  6. INE@ine
    #Spring4Shell (CVE-2022-22965) Remote Code Execution (RCE) was discovered in Spring Core running JDK version 9 (or later). We’ve created a lab to show you how to exploit the #vulnerability. Watch, then get more exploits here: #demo #java .
    Download
    21543
  7. Sonatype✓@sonatype
    ⛔️ Early this morning we started seeing buzz about a new remote code execution flaw that affects #SpringCore. Our Field CTO @llkkaT provides all the info on #Spring4Shell: 💭 What it is 💭 Everything you need to know 💭 Where to go from here ⛓️
    Download
    11146
  8. Amitai Cohen✓@AmitaiCo
    I think many early publications about #Spring4Shell / CVE-2022-22965 slightly glossed over the relationship between the underlying bug in Spring Beans and the exploitation path of this vulnerability through WebMVC / WebFlux (1/5) 🧵
    12253
  9. DFN-CERT | @[email protected]@DFNCERT
    Nach Gerüchten früher am Tag gibt es jetzt (weiterhin unbestätigte) Informationen zu #SpringShell / #Spring4Shell (0Day RCE in Spring Framework). Wir gucken. src 🍿 übersetzung 🧐 YARA (WebShells) ☕️
    vx-underground @vxunderground
    A Java Springcore RCE 0day exploit has been leaked. It was leaked by a Chinese security researcher who, since sharing and/or leaking it, has deleted their Twitter account. We have not verified the exploit. tl;dr big if true Download the 0day POC here:
    158
  10. vx-underground✓@vxunderground
    A Java Springcore RCE 0day exploit has been leaked. It was leaked by a Chinese security researcher who, since sharing and/or leaking it, has deleted their Twitter account. We have not verified the exploit. tl;dr big if true Download the 0day POC here:
    293891K
  11. Greg Linares (Laughing Mantis)✓@Laughing_Mantis
    There appears to be a yet another critical deserialization RCE flaw this time in Java Spring Core that has the potential to be weaponized rather easily. This is *NOT* CVE-2022-22963 (Thanks for the correction @DennisF ) #SpringShell #Spring4Shell
    356130
  12. Florian Roth ⚡️✓@cyb3rops
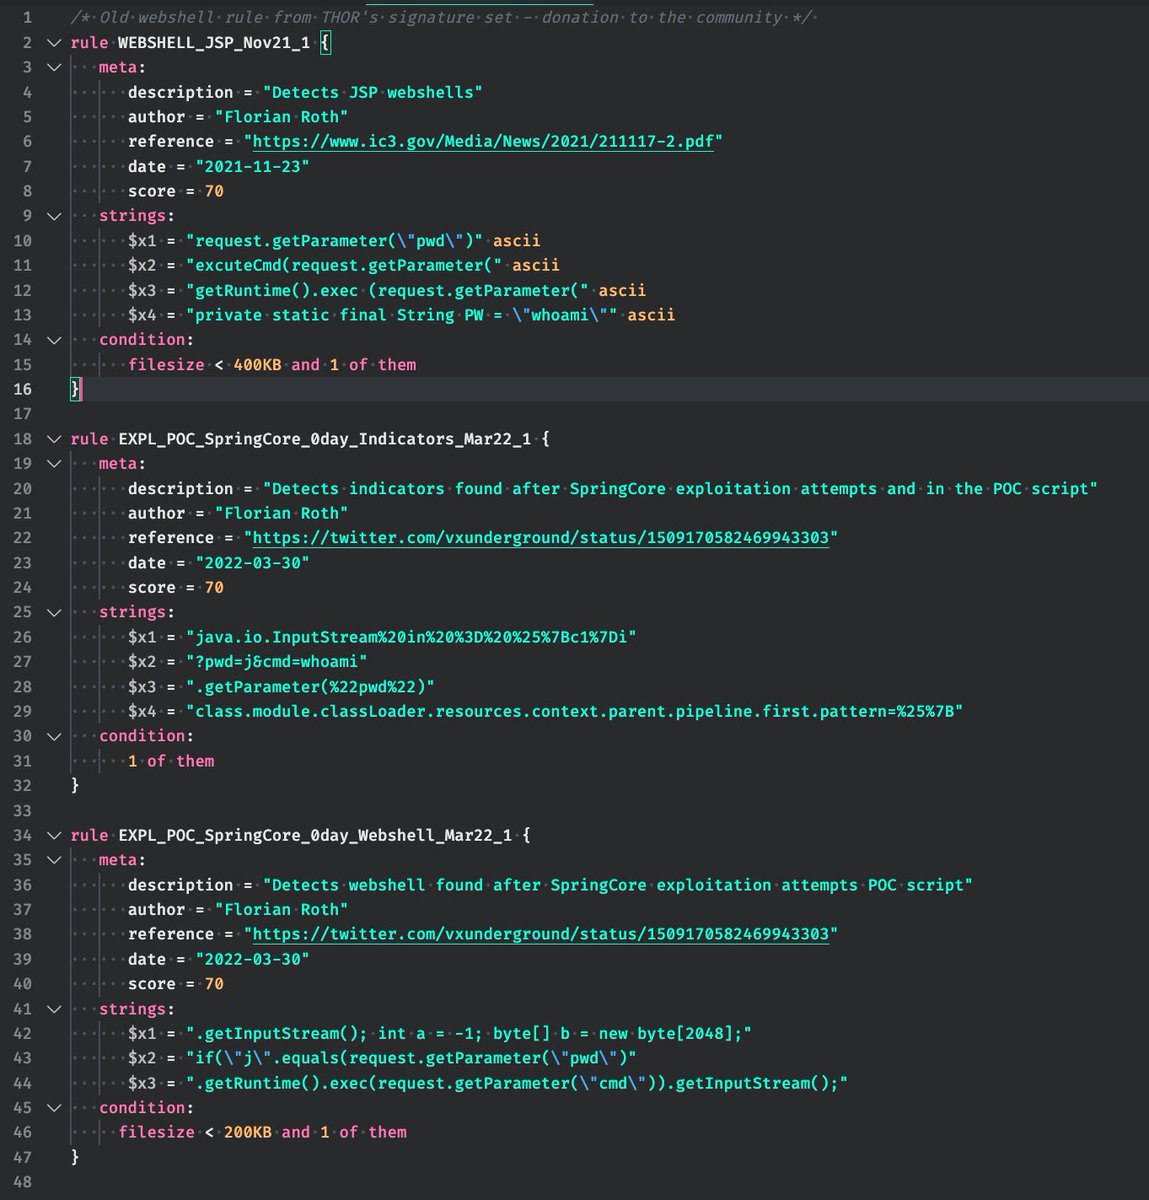
    First YARA rules to detect the PoC code and webshells dropped by the public POC exploiting the #Spring4Shell vulnerability Signature set of THOR Lite should be updated in a minute Thx to @xyantix @testanull Next step: log file based detection
    Download
    1162308
  13. しゅーと@shutingrz
    #spring4shell サンプルアプリを作成して成功を確認。Spring開発経験がないので実際に脆弱な作りをするのかはよくわからない。ただ攻撃者は脆弱性があるAPIを知っていればクエリパラメータなどの他の情報を知らなくても良いため、スキャンを行うモチベーションはありそう
    Download
    02977
  14. Alvaro Muñoz@pwntester
    Do not understand people overhyping some vulns but underhyping #spring4shell. Just run a #CodeQL query on 9340 spring projects hosted on GitHub. 7203 are vulnerable (if depoyed as WARs on Tomcat). Thats 3 out of 4 projects!
    251192
  15. Show more posts