Posty z #SpringShell
#SpringShell
Publiczne posty w X, które używają #SpringShell.
Powiązane hashtagi

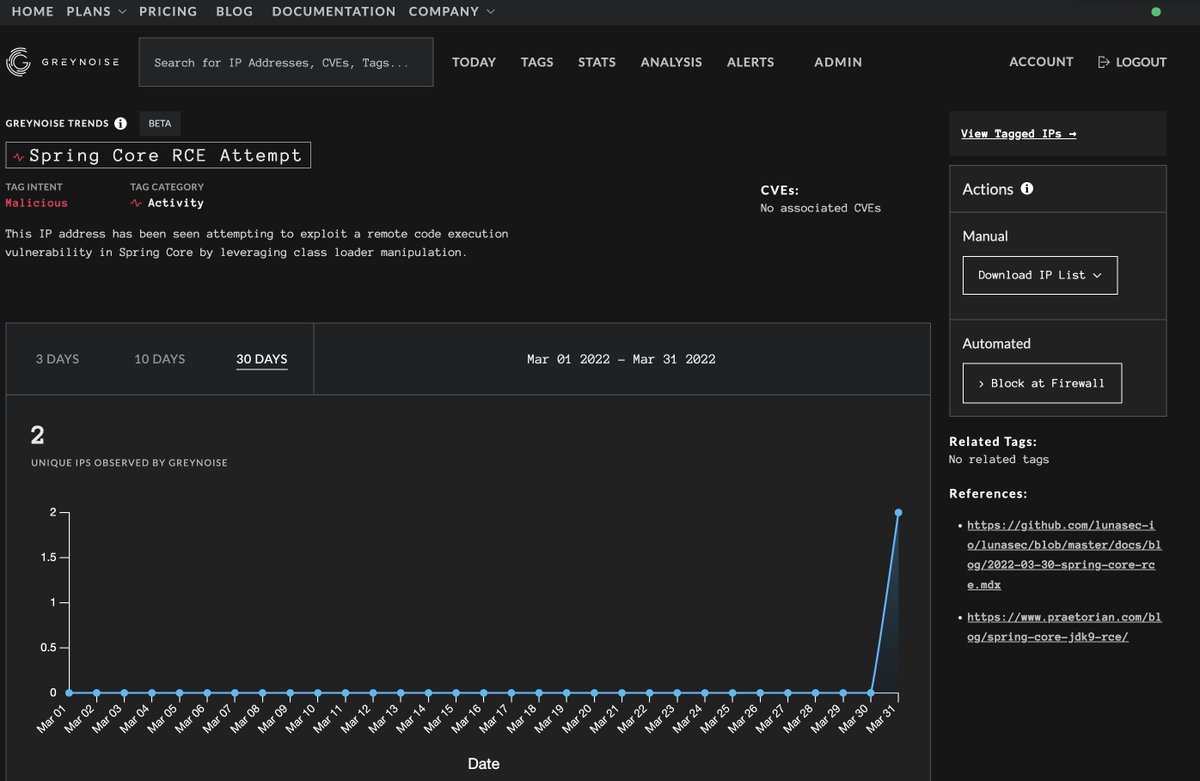
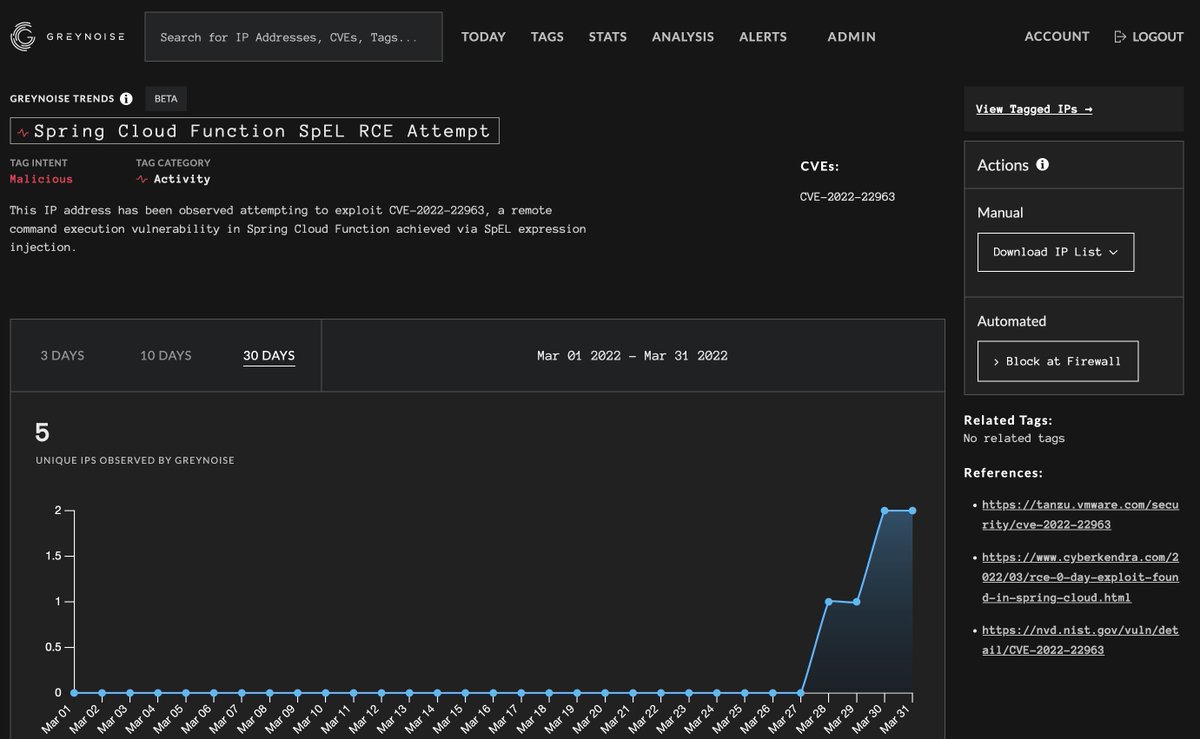
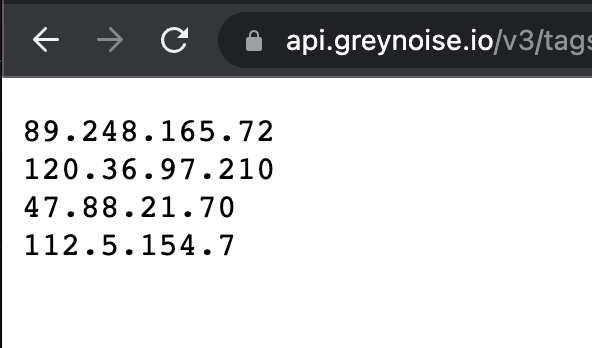
GreyNoise is tracking, has tags available for, and HAS observed exploitation of 2 different "Spring" vulnerabilities in the wild, including #SpringShell. Time series / free dynamic custom block list URLs here:34889
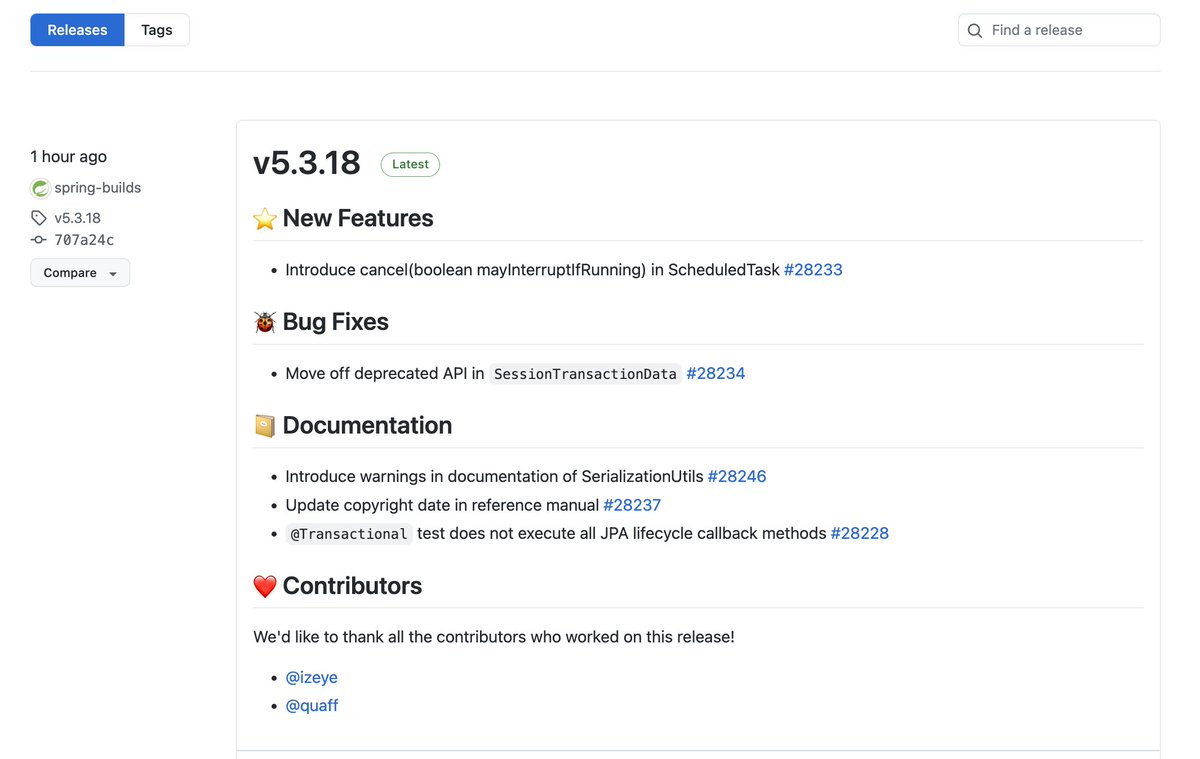
Ilkka Turunen@llkkaTSpring have acknowledged #springshell / #spring4shell - patched versions 5.3.18 and 5.2.20 are released012
Cyber Kendra@cyberkendra#SpringShell: Spring Core RCE 0-day Vulnerability #bugbounty #security @80vul #vulnerability #Log4Shell43897
Checkmarx is closely monitoring #Spring4Shell and all other Spring vulnerabilities (CVE-2022-22963, CVE-2022-22950). Checkmarx SCA customers can scan their code for those vulnerabilities and get the latest remediation solutions. #springshell156
Orit Goren@GorenOritNew #SpringShell / #Spring4Shell zero-day vulnerability remediation cookbook outlining how you can use the @JFrog Platform to find, fix and fortify against the SpringShell threat within your organization. Learn #developers #DevSecOps #cybersecurity001
@CheckmarxUpdate: Confused about the various #spring vulnerabilities out there? Check out our latest blog with technical analysis of all three CVEs, their affected versions, and mitigations. #spring4shell #springshell058
Ax Sharma@Ax_Sharma📢 AFTER much commotion and speculation Spring has *CONFIRMED* #SpringShell and in addition to a new release 5.3.18, also backported fix into 5.2.20. CVE pending. h/t @llkkaT #Spring4ShellAx Sharma @Ax_Sharma🆕 Spring has a NEW 5.3.18 release today (h/t @madpah @sonatype) that just hit Maven Central. Release touches the 'CachedIntrospectionResults' class—after 2 years. The same class that's stated to be responsible for #SpringShell and older CVE-2010-1622 💥139
Ax Sharma@Ax_Sharma@Ax_Sharma🆕 Spring has a NEW 5.3.18 release today (h/t @madpah @sonatype) that just hit Maven Central. Release touches the 'CachedIntrospectionResults' class—after 2 years. The same class that's stated to be responsible for #SpringShell and older CVE-2010-1622 💥034
New #SpringShell / #Spring4Shell zero-day vulnerability remediation cookbook outlining how you can use the JFrog platform to detect, block, and remediate the SpringShell threat within your organization. Learn more: #developers #DevSecOps005
Ilkka Turunen@llkkaTGot together with @Ax_Sharma on a quick live stream to discuss what we know and don’t know about #springshell / #spring4shell037
For all our customers - the JFrog platform is not affected by #SpringShell (CVE-2022-22965) or the recent Spring Cloud Function vulnerability (CVE-2022-22963)035
DFN-CERT | @[email protected]@DFNCERTNach Gerüchten früher am Tag gibt es jetzt (weiterhin unbestätigte) Informationen zu #SpringShell / #Spring4Shell (0Day RCE in Spring Framework). Wir gucken. src 🍿 übersetzung 🧐 YARA (WebShells) ☕️vx-underground @vxundergroundA Java Springcore RCE 0day exploit has been leaked. It was leaked by a Chinese security researcher who, since sharing and/or leaking it, has deleted their Twitter account. We have not verified the exploit. tl;dr big if true Download the 0day POC here:158
A Java Springcore RCE 0day exploit has been leaked. It was leaked by a Chinese security researcher who, since sharing and/or leaking it, has deleted their Twitter account. We have not verified the exploit. tl;dr big if true Download the 0day POC here:293891K
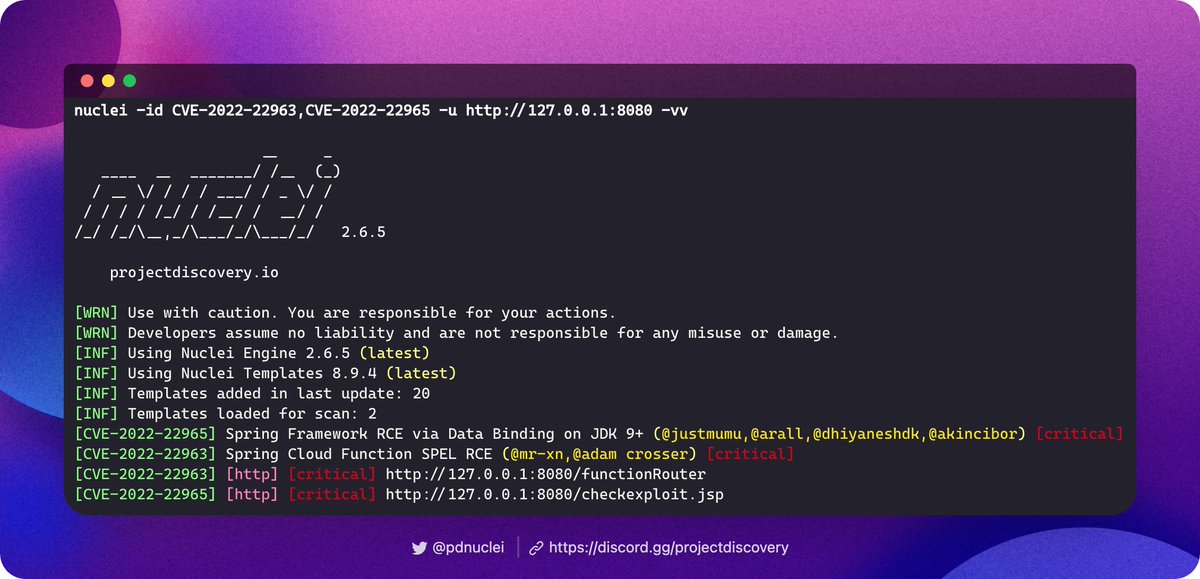
Scan for the most recent Spring vulnerabilities using nuclei templates shared by the community. GitHub: #hackwithautomation #springshell #security #pentest2122371
002
Heike Ritter@HeikeRitterThis blog is for customers looking for protection against exploitation & ways to detect vulnerable installations of the critical remote code execution vulnerability CVE-2022-22965 (referred to in the security community as #SpringShell or #Spring4Shell)047
New #SpringShell / #Spring4Shell zero-day vulnerability remediation cookbook outlining how you can use the JFrog platform to detect, block, and remediate the SpringShell threat within your organization. Learn more: #developers #DevSecOps02023
Greg Foss@35Foss#Java #SpringShell is indeed legit and successful exploitation results in a JSP webshell (default is tomcatwar.jsp but this is trivial to change). Check your web logs for POST requests and look for new jsp filemods. #Spring4Shell564163
📢 Spring has *CONFIRMED* #SpringShell and in addition to a new release 5.3.18, also backported fix into 5.2.20. CVE pending. *Our team will be providing real time #Spring4Shell updates at ⛓Sonatype @sonatype⛔️ Early this morning we started seeing buzz about a new remote code execution flaw that affects #SpringCore. Our Field CTO @llkkaT provides all the info on #Spring4Shell: 💭 What it is 💭 Everything you need to know 💭 Where to go from here ⛓️004
⛔️ Early this morning we started seeing buzz about a new remote code execution flaw that affects #SpringCore. Our Field CTO @llkkaT provides all the info on #Spring4Shell: 💭 What it is 💭 Everything you need to know 💭 Where to go from here ⛓️11146
FullHunt@FullHuntFullHunt developed spring4shell, an open-source tool for discovering spring4shell and Spring Cloud RCE at scale. The new developed payloads within spring4shell-scan bypasses several WAF vendors. Blog Post: #spring4shell #infosec #springshell0816- Pokaż więcej postów