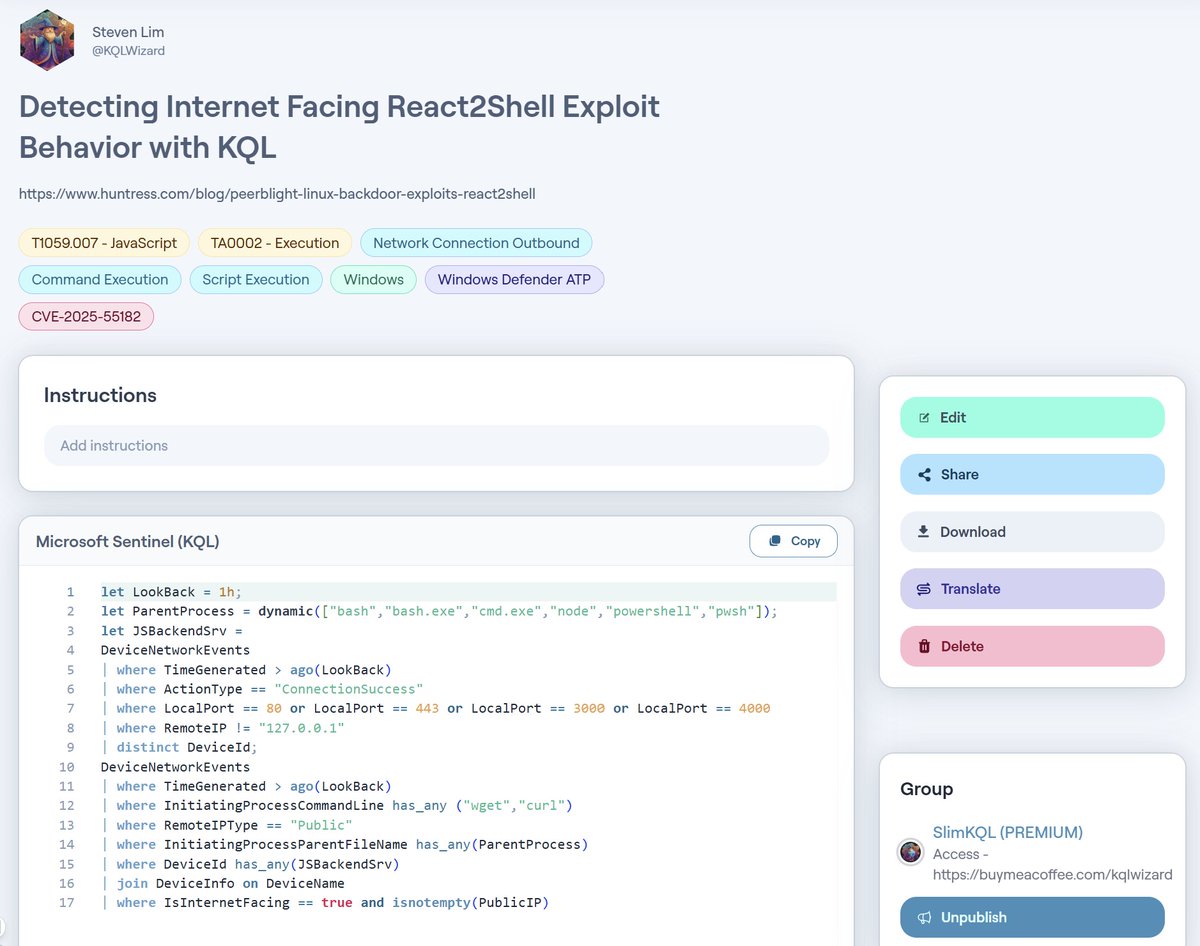
Posty z #react2shell

#react2shell

Publiczne posty w X, które używają #react2shell.

Powiązane hashtagi

  1. FortiGuard Labs✓@FortiGuardLabs
    🚨 New Outbreak Alert: Critical unauthenticated RCE (#React2Shell) actively exploited in the wild, impacting React Server Components and vulnerable Next.js implementations (CVE-2025-55182, CVE-2025-66478). 🔗 Get full details and mitigation guidance: #FortiGuardLabs
    Pobierz
    016711
  2. Phith0n@phithon_xg
    try this WAF bypass trick for rsc&&next.js CVE-2025-55182 All fields can use utf16le charset #React2Shell
    Pobierz
    47047248.5K
  3. Pulsedive Threat Intelligence✓@pulsedive
    Exploitation attempts for #React2Shell (CVE-2025-55182) have been widespread over the last week. Three resources that outline exploitation are: Recommendation: Deploy patches as soon as possible
    023414
  4. ZoomEye✓@zoomeye_team
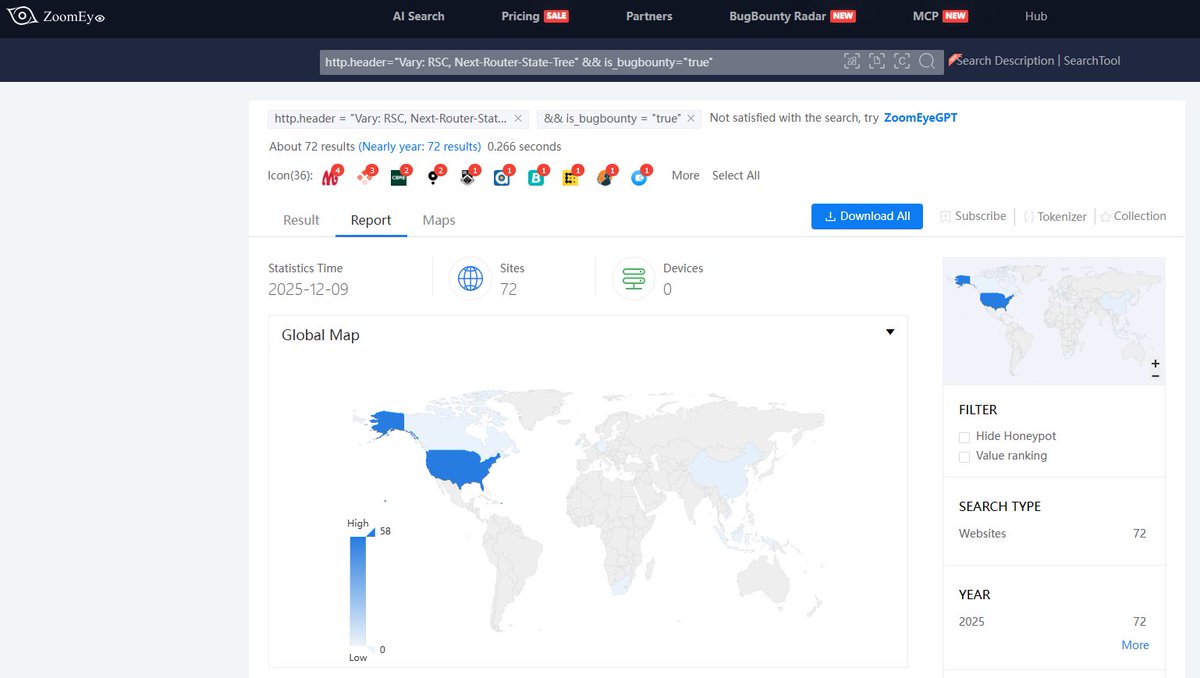
    🚨🚨 #React2Shell (CVE-2025-55182) continues to heat up globally — and what's really sending bounty hunters' heart rates through the roof is: • RCE + no auth + super short exploit chain • Hunters already landing successful exploits in high-value bounty programs • Massive exposure across Next.js / React SSR assets ⚡Want to skip the "needle in a haystack" phase and jump straight to likely-vulnerable targets? Use this dork: http.header="Vary: RSC, Next-Router-State-Tree" && is_bugbounty="true" ZoomEye Link: 🚀ZoomEye BugBounty Radar: zero-in on potentially risky bounty domains and spot the $$$ opportunities before everyone else. 👇 Want to learn how to use BugBounty Radar effectively? 1. 2. 💰 Happy hunting — and may your inbox be full of "Bounty awarded" today! #BugBounty #bugbountytipl #CyberSec #OSINT
    Pobierz
    32716916.1K
  5. Checkmarx Zero✓@CheckmarxZero
    #React2Shell is not to be underestimated: this RCE vulnerability in React also impacts Next.js, and can result in attackers executing arbitrary commands on your servers. It can be hard to be sure that you're not using the affected components, so upgrade as soon as you possibly can! More information:
    022366
  6. an0n@an0n_r0
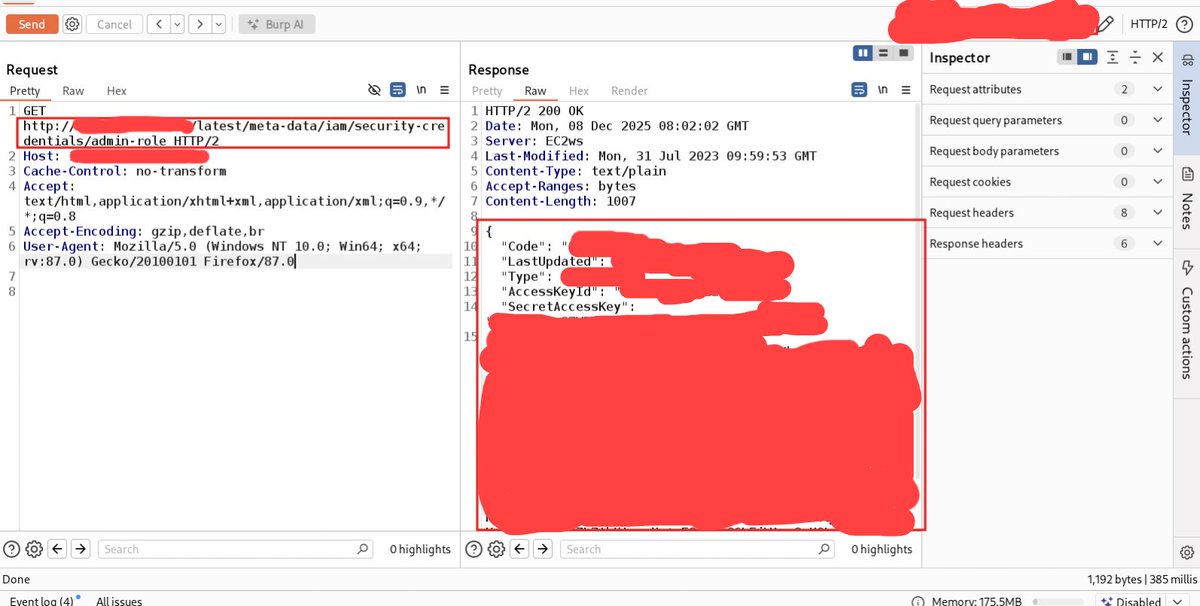
    just tested this in-memory backdoor via #React2Shell, this is crazy. I don't have time to set up a honeypot right now, but I'm pretty sure it would catch these kind of requests within minutes. :)
    Pobierz
    12514121.5K
  7. Netlify@Netlify
    #React2Shell is a good reminder: platform mitigations help, but patching still matters. If you run Next.js / React Server Components, upgrade to a non-vulnerable version and rotate any secrets exposed to your app.
    2351.3K
  8. Ben Canning✓@benhackshealth
    We looked at the data, HRV is down across the board, energy levels compromised, what are you doing to patch it? #wehackhealth #React2Shell
    0171.5K
  9. Dan Perez✓@MrDanPerez
    🇨🇳 and 💰 actors exploiting #React2Shell 👀👀
    114609
  10. Prem Lingayat @PremLingayat
    Released my first blog "Debugging React2Shell (CVE-2025-55182)". In this blog, I have analysed and explained the backend source code of React which caused the React2Shell vulnerability. #cybersecurity #pentesting #react2shell
    0031.2K
  11. André Baptista✓@0xacb
    Some #React2Shell targets are relying in WAFs but can still be exploited with this 🚨
    shubs @infosec_au
    Pushed a new update to -- it now scans for the RCE payload via reflection. Use the --waf-bypass flag to bypass WAFs, works well for Cloudflare/AWS. Other WAFs might need tinkering with the payload, depending on whether they don't have a max context limit.
    33439.8K
  12. shubs✓@infosec_au
    Pushed a new update to -- it now scans for the RCE payload via reflection. Use the --waf-bypass flag to bypass WAFs, works well for Cloudflare/AWS. Other WAFs might need tinkering with the payload, depending on whether they don't have a max context limit.
    1412661883.4K
  13. CrowdSec✓@Crowd_Security
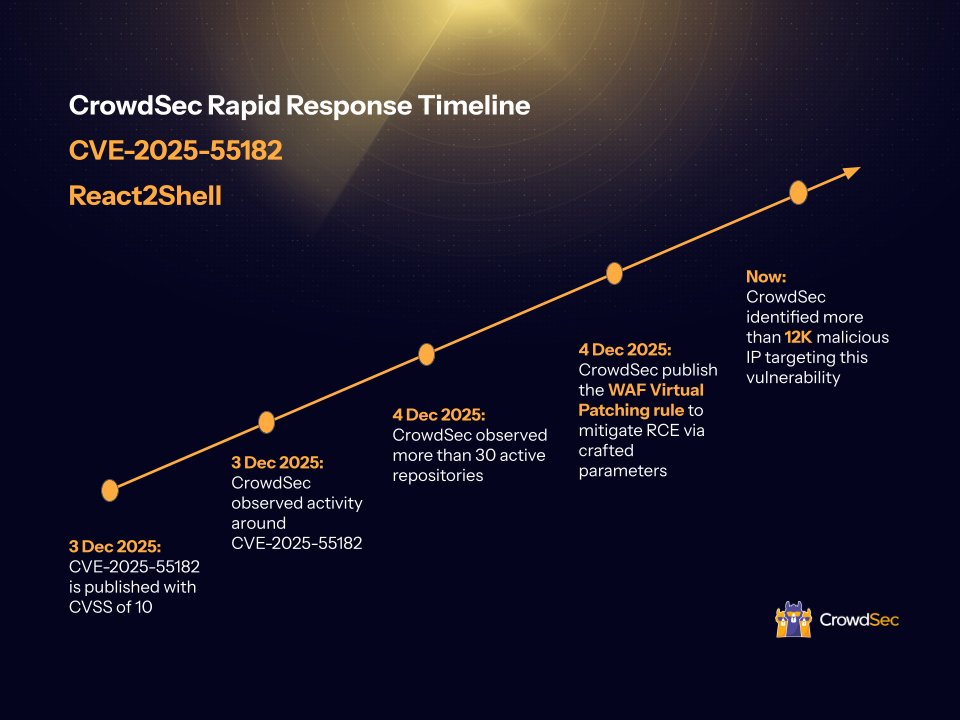
    From CVE disclosure to protection in under 24 hours, a practical example of collaborative security in action. On 3 December 2025, CVE-2025-55182 (#React2Shell) was published with a CVSS score of 10. Within hours, CrowdSec Security Engines worldwide began detecting exploitation attempts. By the next day, the network had: - Identified significant attack activity targeting the vulnerability - Released a WAF Virtual Patching rule to mitigate the RCE - Started automatically blocking attacks through community-driven blocklists Today, more than 12K malicious IPs targeting this CVE have been flagged, with protections continuously updated as new threats emerge. This demonstrates the value of a global, crowdsourced intrusion detection and prevention network. If your workloads are exposed to the internet, you can benefit from this rapid, collective response: 👉 To keep your systems protected, deploy the CrowdSec WAF: 👉 And, enable the free React2Shell blocklist to secure your exposed services immediately: #CVE #CVE202555182 #cybersecurity
    Pobierz
    134757
  14. pyn3rd✓@pyn3rd
    #CVE-2025-55182 #React2Shell Let me walk you through the technical path of the WAF bypass. When a request is sent as multipart/form-data, Next.js hands the raw body stream to Busboy. The bypass comes from Busboy’s charset logic: it cleanly accepts UTF‑16LE (and legacy UCS‑2) and forwards the decoded bytes straight into the RSC payload deserializer. charset=base64 is a dead route — that path hits base64Slice(), which encodes instead of decodes, corrupting the payload and killing the exploit chain. So the only viable encodings for smuggling malicious RSC payloads past WAF normalization are UTF‑16LE and UCS‑2. And if the WAF isn’t performing proper normalization on non‑UTF8 charsets, it will miss the payload entirely.
    Pobierz
    1612355271K
  15. Germán Fernández✓@1ZRR4H
    🚩 #React2Shell 🌐📡 → Censys (+270K assets): services.http.response.headers: (key: `Vary` and value.headers: `RSC, Next-Router-State-Tree`) → Shodan (+380K assets): "Vary: RSC, Next-Router-State-Tree"
    Pobierz
    07741267.4K
  16. Pokaż więcej postów