#react2shell içeren gönderiler
#react2shell
X'te #react2shell kullanan herkese açık gönderiler.
İlgili etiketler

an0n@an0n_r0just tested this in-memory backdoor via #React2Shell, this is crazy. I don't have time to set up a honeypot right now, but I'm pretty sure it would catch these kind of requests within minutes. :)12514121.5K
Phith0n@phithon_xgtry this WAF bypass trick for rsc&&next.js CVE-2025-55182 All fields can use utf16le charset #React2Shell47047248.5K
ThreatRecon@nshcthreatreconWe published "Analysis of #React2Shell RCE Vulnerability (CVE-2025–55182)" #APT #Malware #cybercrime #threatintel #ThreatIntelligence #threathunting #vulnerability0442K
Just in: Watch #React2Shell exploitation unfold over time in the map below (geo of source IPs attempting to exploit CVE-2025-55182). #GreyNoise #ThreatIntel #CVE202555182 #Nextjs #Cybersecurity55027723.7K
Some #React2Shell targets are relying in WAFs but can still be exploited with this 🚨shubs @infosec_auPushed a new update to -- it now scans for the RCE payload via reflection. Use the --waf-bypass flag to bypass WAFs, works well for Cloudflare/AWS. Other WAFs might need tinkering with the payload, depending on whether they don't have a max context limit.33439.8K
Pushed a new update to -- it now scans for the RCE payload via reflection. Use the --waf-bypass flag to bypass WAFs, works well for Cloudflare/AWS. Other WAFs might need tinkering with the payload, depending on whether they don't have a max context limit.1412661883.4K
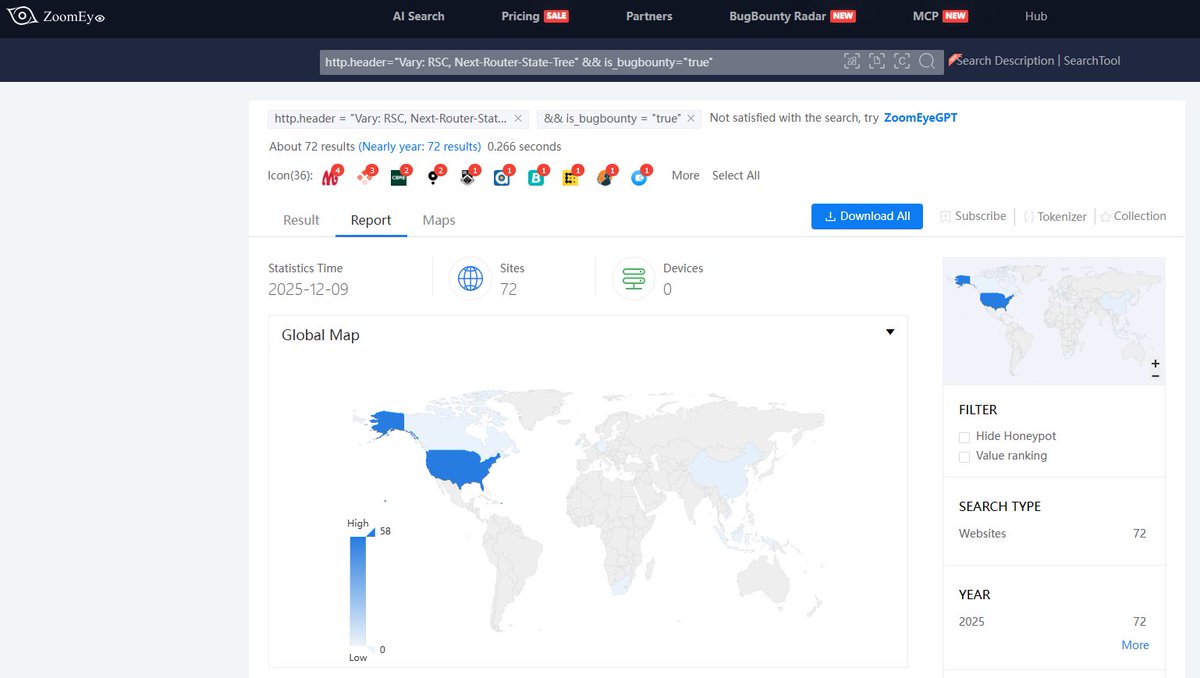
🚨🚨 #React2Shell (CVE-2025-55182) continues to heat up globally — and what's really sending bounty hunters' heart rates through the roof is: • RCE + no auth + super short exploit chain • Hunters already landing successful exploits in high-value bounty programs • Massive exposure across Next.js / React SSR assets ⚡Want to skip the "needle in a haystack" phase and jump straight to likely-vulnerable targets? Use this dork: http.header="Vary: RSC, Next-Router-State-Tree" && is_bugbounty="true" ZoomEye Link: 🚀ZoomEye BugBounty Radar: zero-in on potentially risky bounty domains and spot the $$$ opportunities before everyone else. 👇 Want to learn how to use BugBounty Radar effectively? 1. 2. 💰 Happy hunting — and may your inbox be full of "Bounty awarded" today! #BugBounty #bugbountytipl #CyberSec #OSINT32716916.1K
🚨 The top #CVEs of #2025 weren’t just severe - they were exploited fast. From #React2Shell to #ToolShell & #CitrixBleed2, attackers weaponized flaws before many orgs could #patch. 📊002171
Super hyped to share that @HuntressLabs published a Rapid Response blog on the recent #React2Shell post-exploitations observed. We discovered and analyzed a few payloads that were named #PeerBlight, #CowTunnel and #ZinFoq. We also observed a variant of #Kaiji malware. 3 Modelo's 🍺 in and the malware started making sense. By the 4th one I was naming them like Pokémon except way more unhinged. PeerBlight, I choose you! Thank you for your contributions @sudo_Rem, @LindseyOD123, @_JohnHammond, @bumbucha, and @aaron_deal. Couldn’t have done it without your support ❤️114116378.7K
Link Technologies@LinkTechnlogiesA critical React2Shell flaw is being exploited to breach servers worldwide. Over 77,000 vulnerable IPs and more than 30 organizations have already been compromised with state-linked attacks underway. Patch. Rebuild. Redeploy. Now. #CyberSecurity #React2Shell #InfoSec #RCE #ThreatIntel #WebSecurity #CVE20255518200590
🇮🇷 Arshiya🇮🇷@arshiyaihaDetecting #React2Shell (CVE-2025-55182), Safe probe for Flight parser error with Curl and without harmful execution. Indicators of vulnerability: ✅ Response Code = 500 ✅ Word "digest" appears in response body #React2Shell #CVE202555182 #BugBounty43823721.1K
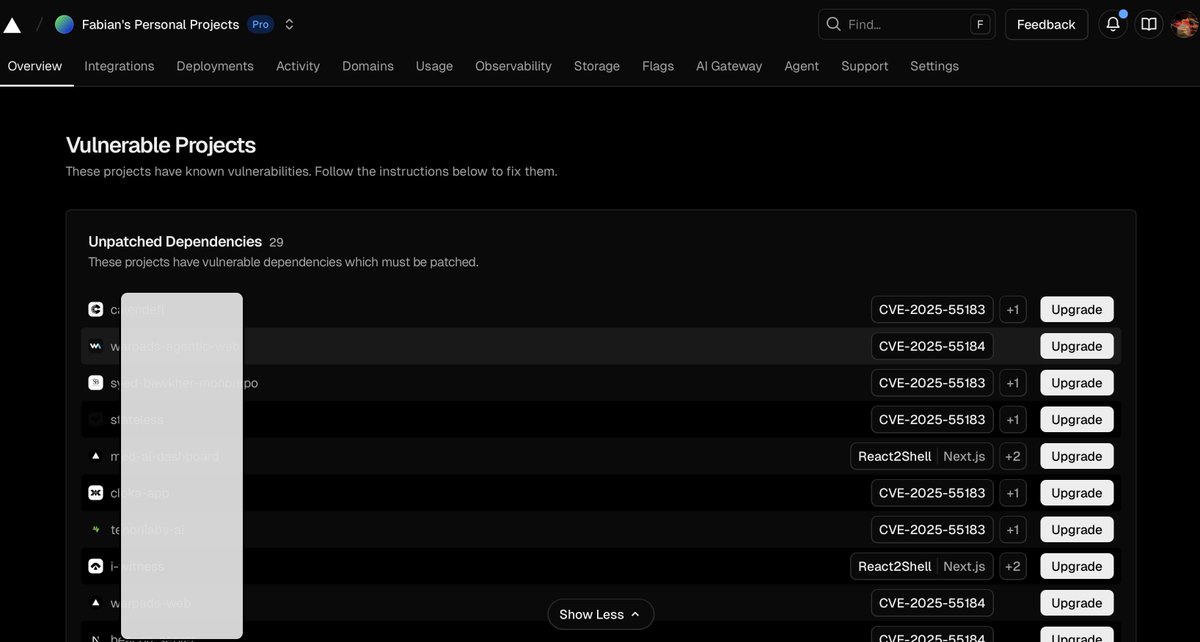
fabianferno@fabianfernolast week's react oopsie left me fixing 30 projects with maximum-severity vulnerability - thanks for making my week 🙂 #react2shell0011373
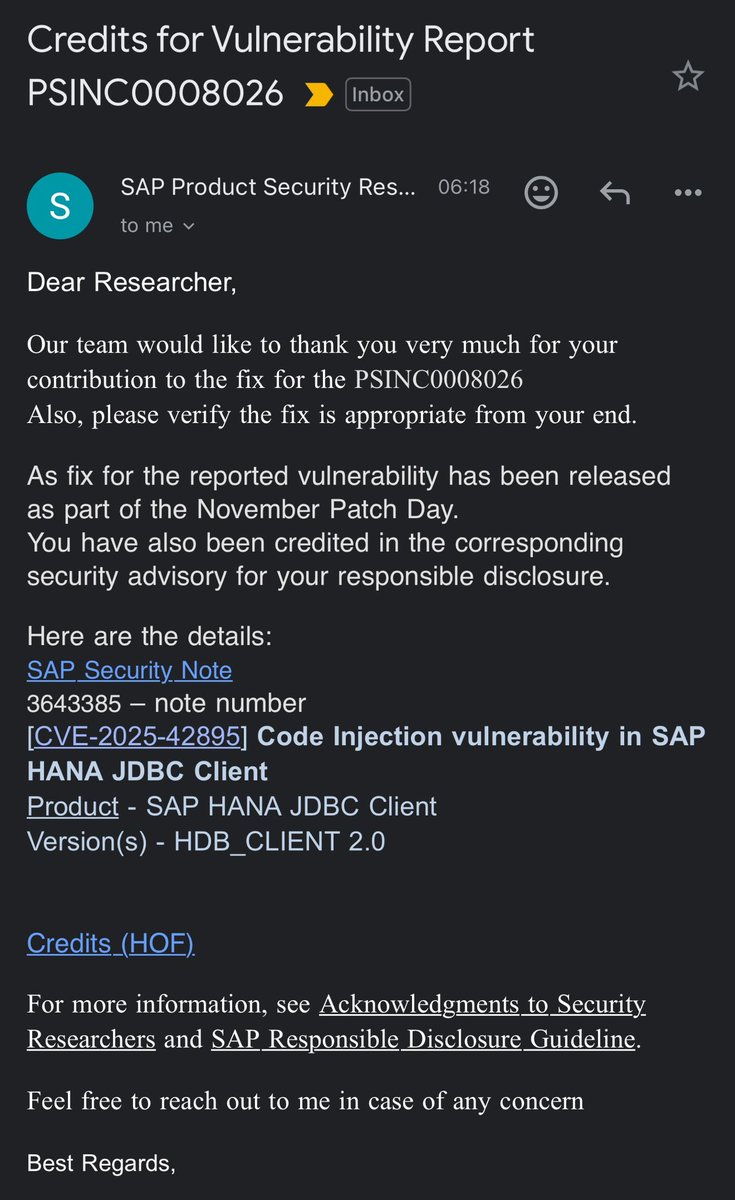
The #React2Shell exploit bypassing WAF is clever, but let’s not forget—the #JDBC attack story is far from over.😁271048.5K
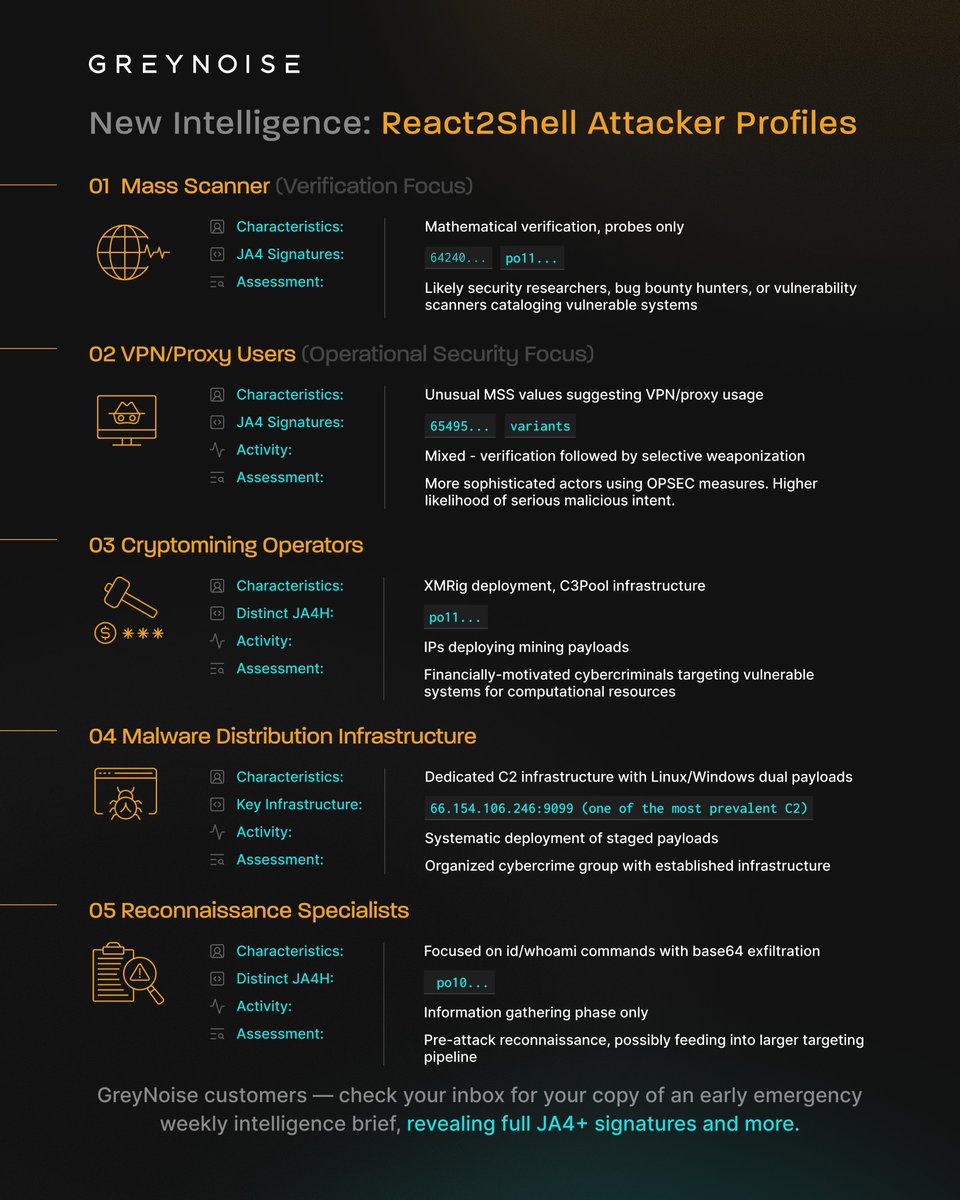
👀 React2Shell attacker profiles fresh from GreyNoise telemetry: don't miss the latest contribution from GreyNoise Labs on React2Shell: #React2Shell #Nextjs #CVE202555182 #CVE #GreyNoise1226510.4K
Exploitation of recent React RCE vul (CVE-2025-55182 - #React2Shell) leading to #Mirai infection ⤵️ Botnet Mirai C2 domains 📡: effeminate.fuckphillipthegerman .ru trap.fuckphillipthegerman .ru tranny.fuckphillipthegerman .ru Botnet Mirai C2 servers , all hosted at FORTIS 🇷🇺: 138.124.72.251:52896 138.124.69.154:60328 5.144.176.19:60328 Mirai #malware sample 🤖: Payload delivery host 🌐: Releated IOCs 🦊:3238618.6K
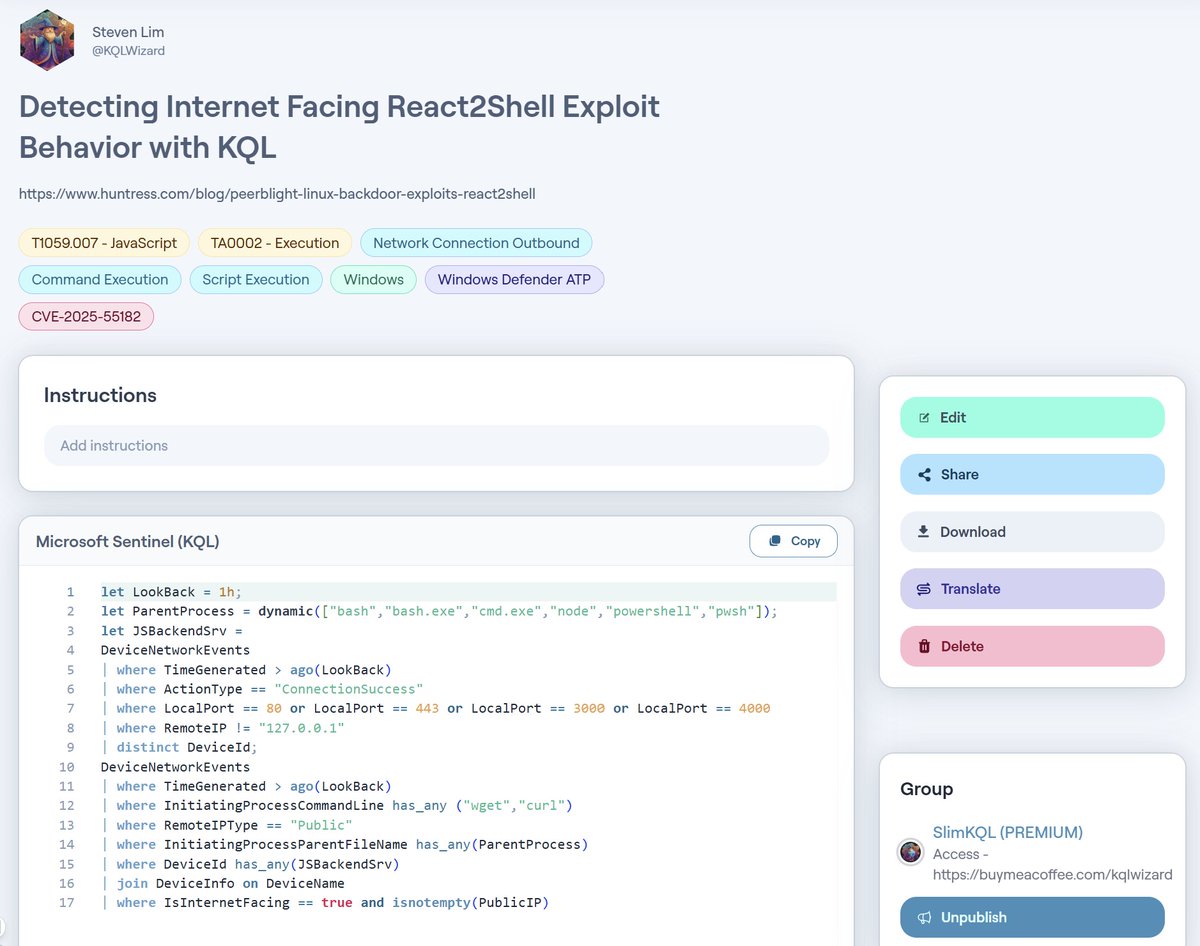
🛡️Strengthening Detection Against React2Shell Exploits Refined my KQL behavioral detection for internet‑facing React2Shell exploits leveraging Huntress’ latest customer‑base insights. #Cybersecurity #React2Shell #ThreatDetection #DefenderXDR #KQL16535K
We’re seeing up to 14.5 million attempts per hour to exploit the #React2Shell vulnerability across @Cloudflare’s network. This is a very bad exploit. While our WAF is helping protect customers, it’s critical to update your React and Next.js instances as soon as possible.191341.1K95.2K
🚩 #React2Shell 🌐📡 → Censys (+270K assets): services.http.response.headers: (key: `Vary` and value.headers: `RSC, Next-Router-State-Tree`) → Shodan (+380K assets): "Vary: RSC, Next-Router-State-Tree"07741267.4K- Daha fazla gönderi göster