Post con #SpringShell
#SpringShell
Post pubblici su X che usano #SpringShell.
Hashtag correlati

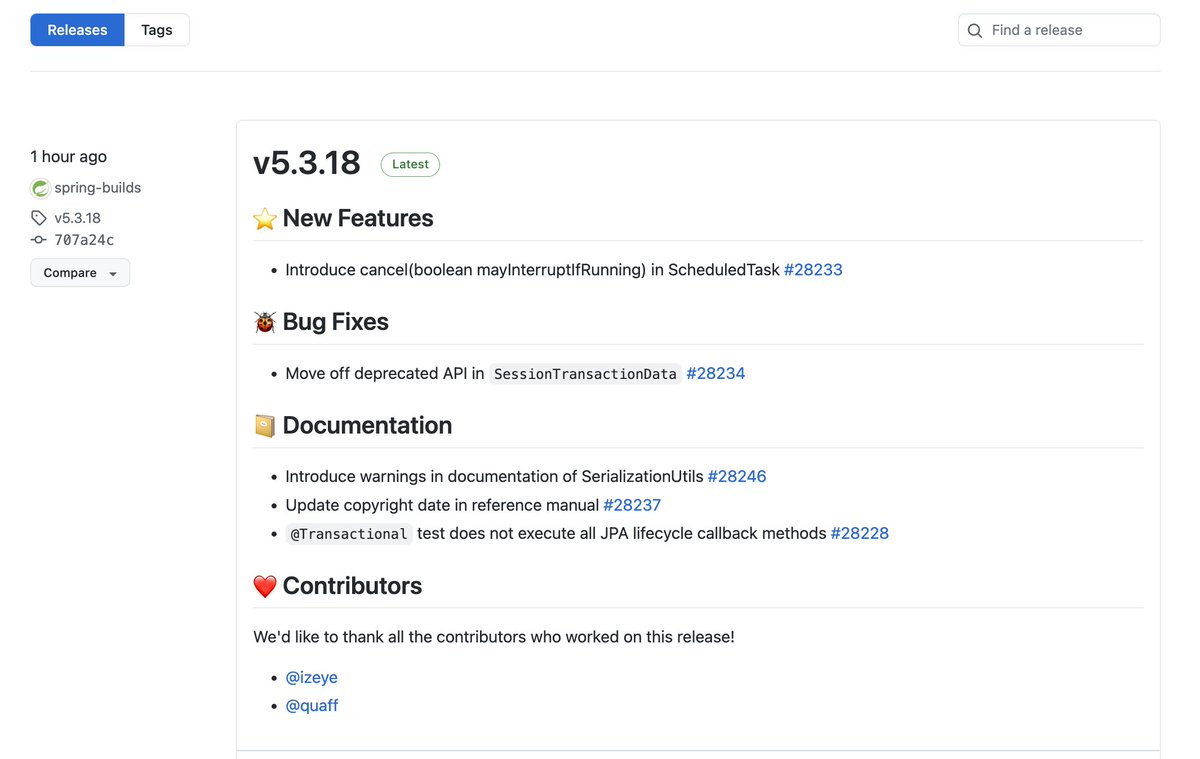
Ax Sharma@Ax_Sharma📢 AFTER much commotion and speculation Spring has *CONFIRMED* #SpringShell and in addition to a new release 5.3.18, also backported fix into 5.2.20. CVE pending. h/t @llkkaT #Spring4ShellAx Sharma @Ax_Sharma🆕 Spring has a NEW 5.3.18 release today (h/t @madpah @sonatype) that just hit Maven Central. Release touches the 'CachedIntrospectionResults' class—after 2 years. The same class that's stated to be responsible for #SpringShell and older CVE-2010-1622 💥139
Ax Sharma@Ax_Sharma@Ax_Sharma🆕 Spring has a NEW 5.3.18 release today (h/t @madpah @sonatype) that just hit Maven Central. Release touches the 'CachedIntrospectionResults' class—after 2 years. The same class that's stated to be responsible for #SpringShell and older CVE-2010-1622 💥034
FullHunt@FullHuntFullHunt developed spring4shell, an open-source tool for discovering spring4shell and Spring Cloud RCE at scale. The new developed payloads within spring4shell-scan bypasses several WAF vendors. Blog Post: #spring4shell #infosec #springshell0816
002
If you are looking for building #Java, #SpringShell, #GraalVM based CLI tools, I would recommend to take a look at: 1. ttcli 2. arconia-cli15222.2K
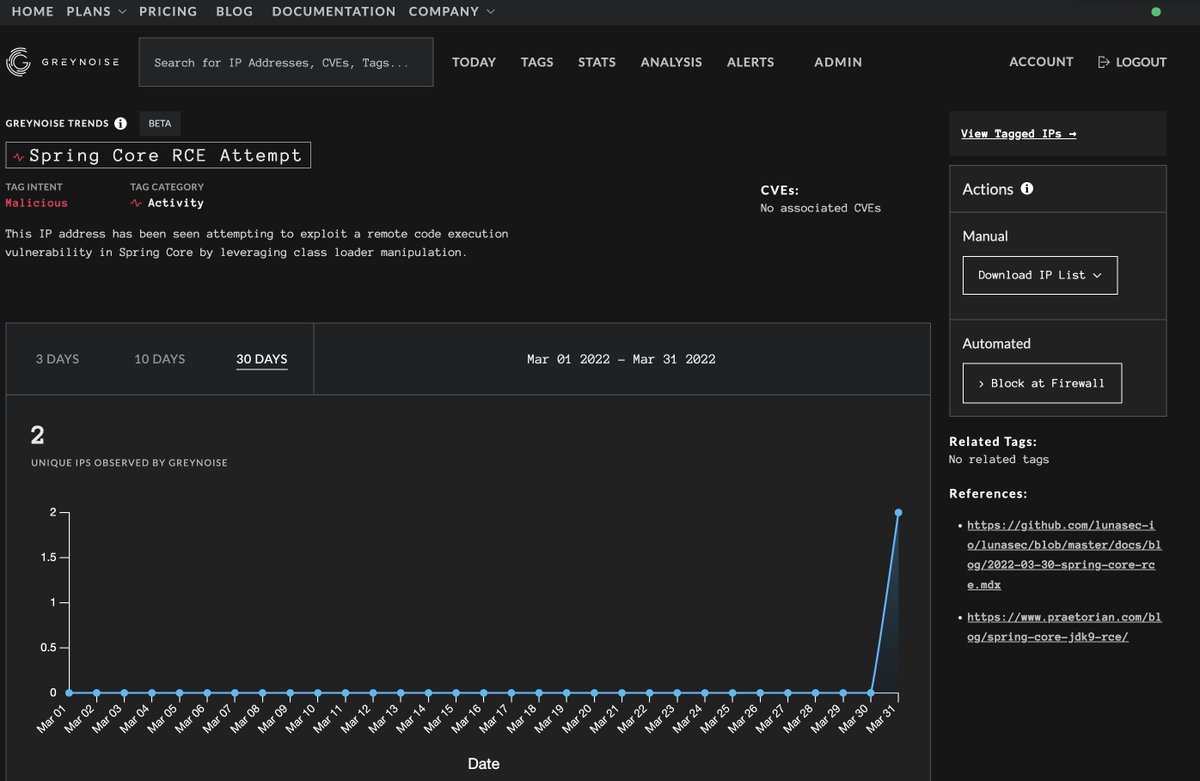
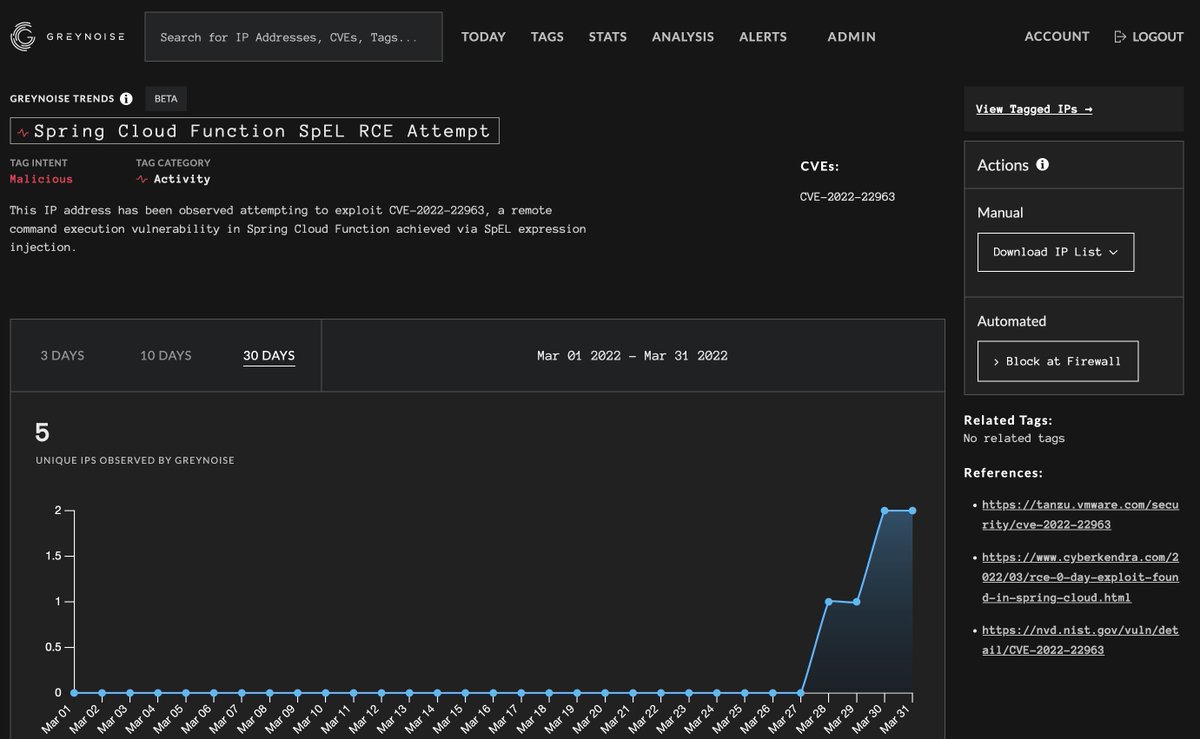
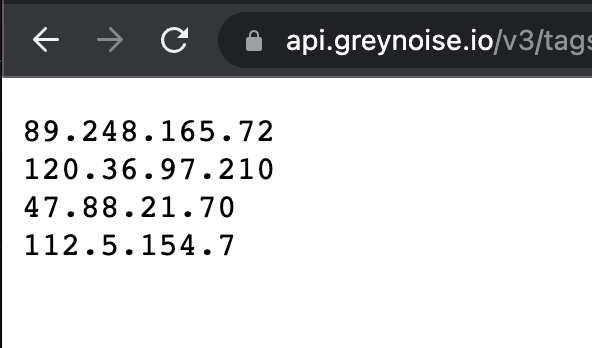
GreyNoise is tracking, has tags available for, and HAS observed exploitation of 2 different "Spring" vulnerabilities in the wild, including #SpringShell. Time series / free dynamic custom block list URLs here:34889
New #SpringShell / #Spring4Shell zero-day vulnerability remediation cookbook outlining how you can use the JFrog platform to detect, block, and remediate the SpringShell threat within your organization. Learn more: #developers #DevSecOps005
Sander Maas@__RetrospectJava keeps me up at night… pushed a quick&dirty repo to help you replicate the spring core rce that got published: #spring4shell #springshell32998
Greg Foss@35Foss#Java #SpringShell is indeed legit and successful exploitation results in a JSP webshell (default is tomcatwar.jsp but this is trivial to change). Check your web logs for POST requests and look for new jsp filemods. #Spring4Shell564163
🔥Did #Spring4Shell set the internet on fire again? ✋🏽Not so fast. 🆕In a special episode of "Wicked Good Development" we dissect 🔎 the zero-day RCE vulnerability in the Spring Framework dubbed Spring4Shell or #Springshell. 🎧91465
Snyk@snyksec🚨 There’s a credible #RCE vulnerability in spring-beans package, which is part of Spring Core. This is a key enabler of the inversion of control (IoC) capabilities of Spring — often referred to as dependency injection. #Spring4Shell #SpringShell (1/2) 👇21220
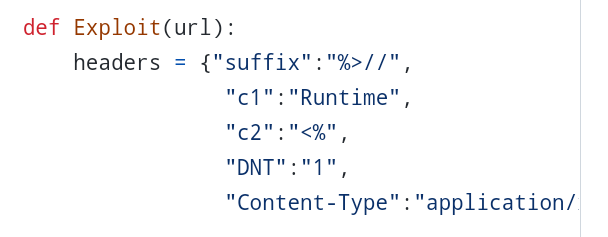
Jonas Vestberg@bugch3ckWhat's the purpose of these headers in the leaked #SpringShell exploit? They are included in the POST payload using "{headername}". Required to get around some non-security encoding context? Avoid double URL-encoding? WAF bypass (cant see any other reason for "Runtime")?102
Do you maintain a folder of scripts you’ve written that you take with you from one operating system to another? What are they?3045.2K
@starbuxman@starbuxman Yep, I keep moving things into a #SpringShell My 'conventions' for Spring workloads.0132.7K
For #SpringOfficeHours episodes, a native-image version of this #SpringShell CLI can send our transcriptions to @ForeFrontAI for summarization. #GitOpsForDevRel124568
🦋 codepilot.bsky.social@n0fhgAnother Java RCE on the horizon? Potentially a #Log4j redeux ... are we prepared for this? I hope folks didn't have weekend plans... We should call this bug "SpringBreak". I'll petition @GossiTheDog #InfoSec #BlueTeam #SpringBreak2213
🦋 codepilot.bsky.social@n0fhg@n0fhgFurther reading. Folks are calling it #SpringShell but I like SpringBreak better; more reflective of the issue (breaking the Spring Framework's rules, rather than relying on a flaw in Spring Framework; that how I'm reading it, anyway).106
Nicolas Fränkel 🇪🇺🇺🇦🇬🇪@nicolas_frankelI overlooked #SpringShell to interact with my demo applications It seems it could be a great fit 🤔015
NetSPI@NetSPIStill grappling with Spring4Shell remediation? Our Attack Surface Management platform can help you identify vulnerable instances of Spring. Plus, our experts can help get you on the right path to remediation. #springshell #spring4shell001
📢 Spring has *CONFIRMED* #SpringShell and in addition to a new release 5.3.18, also backported fix into 5.2.20. CVE pending. *Our team will be providing real time #Spring4Shell updates at ⛓Sonatype @sonatype⛔️ Early this morning we started seeing buzz about a new remote code execution flaw that affects #SpringCore. Our Field CTO @llkkaT provides all the info on #Spring4Shell: 💭 What it is 💭 Everything you need to know 💭 Where to go from here ⛓️004
⛔️ Early this morning we started seeing buzz about a new remote code execution flaw that affects #SpringCore. Our Field CTO @llkkaT provides all the info on #Spring4Shell: 💭 What it is 💭 Everything you need to know 💭 Where to go from here ⛓️11146
Expertos Tech@ExpertosTech📌 🚀Video novo lá no canal ExpertosTech, falando da vulnerabilidade SpringShell ou Spring4Shell descoberta no Spring Framework no último dia 30 de março. #Spring4Shell #SpringShell #ExpertosTech002
EcuCERT@EcuCERT_EC#CiberAlertas_EcuCERT vulnerabilidades #Spring4Shell #SpringShell que afectan al framework de #Spring @springcentral, permitirían tomar remotamente el control de aplicaciones. Detalles y recomendaciones en:011- Mostra altri post