Posts avec #SpringShell
#SpringShell
Les posts publics sur X qui utilisent #SpringShell.
Hashtags associés

Orit Goren@GorenOritNew #SpringShell / #Spring4Shell zero-day vulnerability remediation cookbook outlining how you can use the @JFrog Platform to find, fix and fortify against the SpringShell threat within your organization. Learn #developers #DevSecOps #cybersecurity001
New #SpringShell / #Spring4Shell zero-day vulnerability remediation cookbook outlining how you can use the JFrog platform to detect, block, and remediate the SpringShell threat within your organization. Learn more: #developers #DevSecOps005
Get the details on the latest #zero-day vulnerability - #SpringShell / #Spring4Shell - + recommended remediation strategies on Tuesday, April 5, 2022 @ 7am PT / 10am ET / 4pm CET. Register today: #CyberSecurity #developers015
FullHunt@FullHuntFullHunt developed spring4shell, an open-source tool for discovering spring4shell and Spring Cloud RCE at scale. The new developed payloads within spring4shell-scan bypasses several WAF vendors. Blog Post: #spring4shell #infosec #springshell0816
DevTalles@DevTalles🍃🔧 ¡#SpringShell 4.0.2 disponible! Esta versión corrige problemas de alineación respecto a la v3; trae varias correcciones además de mejoras de estabilidad y rendimiento. Ya disponible en Maven Central; consulta las notas de la release para más detalles:0312504
We've just published an OSS tool that searches compiled code (JAR/WAR binaries) for web apps potentially vulnerable to #SpringShell. Feedback is welcome!03544
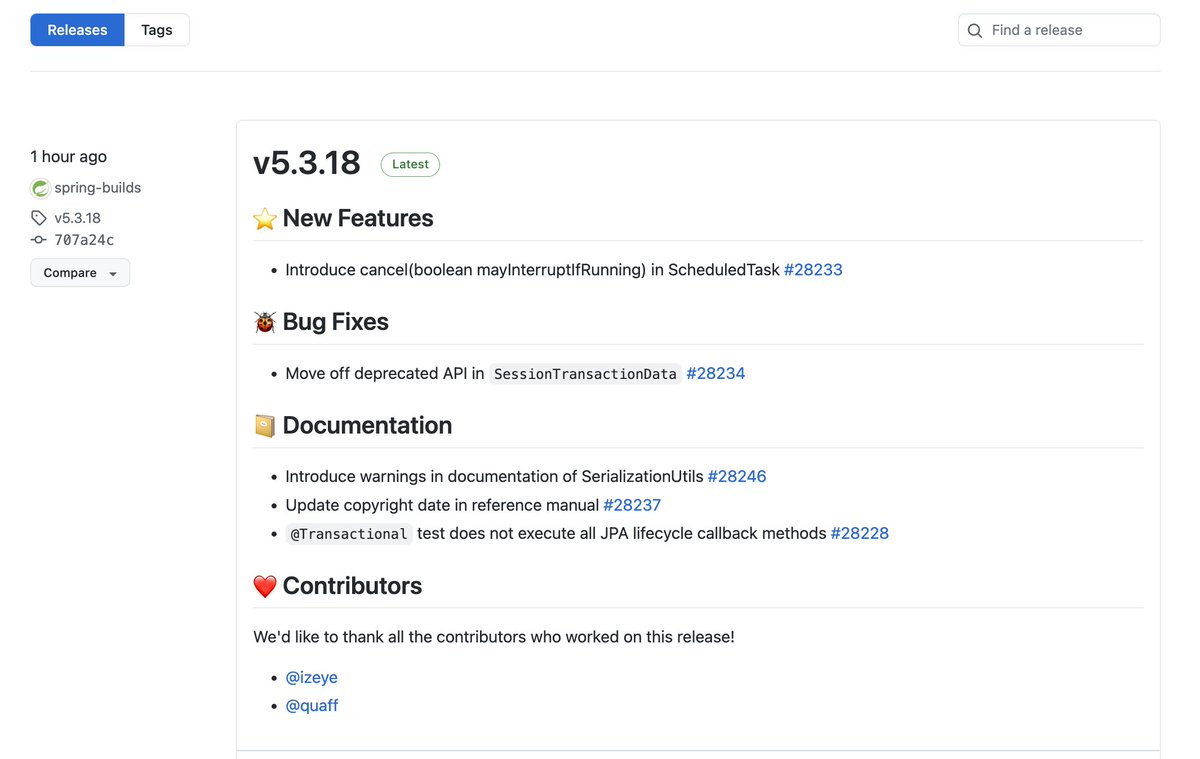
Ax Sharma@Ax_Sharma📢 AFTER much commotion and speculation Spring has *CONFIRMED* #SpringShell and in addition to a new release 5.3.18, also backported fix into 5.2.20. CVE pending. h/t @llkkaT #Spring4ShellAx Sharma @Ax_Sharma🆕 Spring has a NEW 5.3.18 release today (h/t @madpah @sonatype) that just hit Maven Central. Release touches the 'CachedIntrospectionResults' class—after 2 years. The same class that's stated to be responsible for #SpringShell and older CVE-2010-1622 💥139
Ax Sharma@Ax_Sharma@Ax_Sharma🆕 Spring has a NEW 5.3.18 release today (h/t @madpah @sonatype) that just hit Maven Central. Release touches the 'CachedIntrospectionResults' class—after 2 years. The same class that's stated to be responsible for #SpringShell and older CVE-2010-1622 💥034
If you are looking for building #Java, #SpringShell, #GraalVM based CLI tools, I would recommend to take a look at: 1. ttcli 2. arconia-cli15222.2K
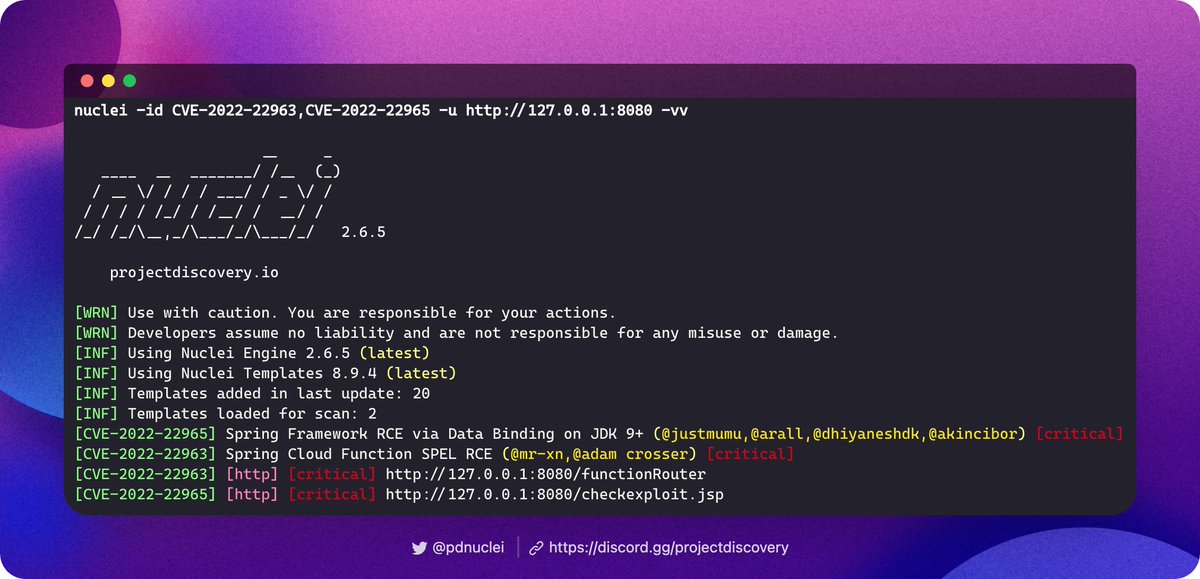
Scan for the most recent Spring vulnerabilities using nuclei templates shared by the community. GitHub: #hackwithautomation #springshell #security #pentest2122371
🔥Did #Spring4Shell set the internet on fire again? ✋🏽Not so fast. 🆕In a special episode of "Wicked Good Development" we dissect 🔎 the zero-day RCE vulnerability in the Spring Framework dubbed Spring4Shell or #Springshell. 🎧91465
DFN-CERT | @[email protected]@DFNCERTNach Gerüchten früher am Tag gibt es jetzt (weiterhin unbestätigte) Informationen zu #SpringShell / #Spring4Shell (0Day RCE in Spring Framework). Wir gucken. src 🍿 übersetzung 🧐 YARA (WebShells) ☕️vx-underground @vxundergroundA Java Springcore RCE 0day exploit has been leaked. It was leaked by a Chinese security researcher who, since sharing and/or leaking it, has deleted their Twitter account. We have not verified the exploit. tl;dr big if true Download the 0day POC here:158
A Java Springcore RCE 0day exploit has been leaked. It was leaked by a Chinese security researcher who, since sharing and/or leaking it, has deleted their Twitter account. We have not verified the exploit. tl;dr big if true Download the 0day POC here:293891K
#GraalVM native-image #SpringShell CLI to convert markdown into a bookmarks.html file. Released with #GitHubAction workflow. (spring-office-hours/mdtohtml-cli) Setup another workflow, to use the native-image CLI, to update the repo, on push to main.2218847
Ilkka Turunen@llkkaTSpring have acknowledged #springshell / #spring4shell - patched versions 5.3.18 and 5.2.20 are released012
002
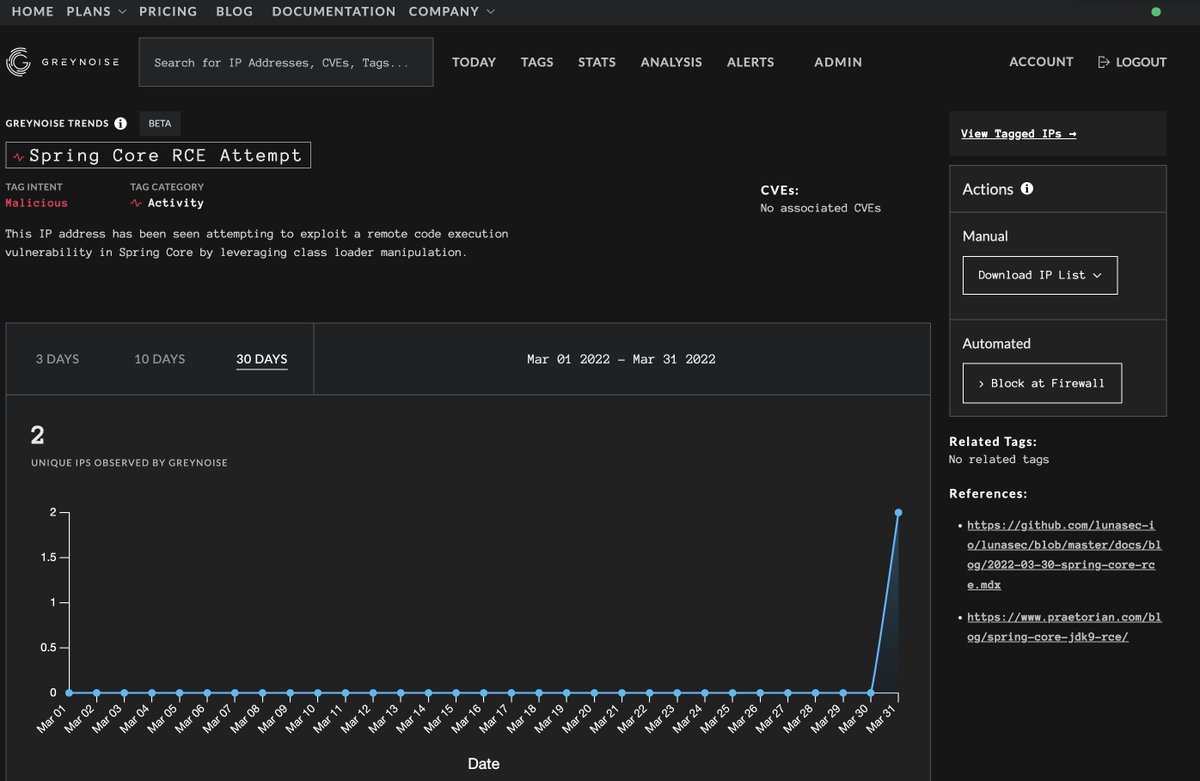
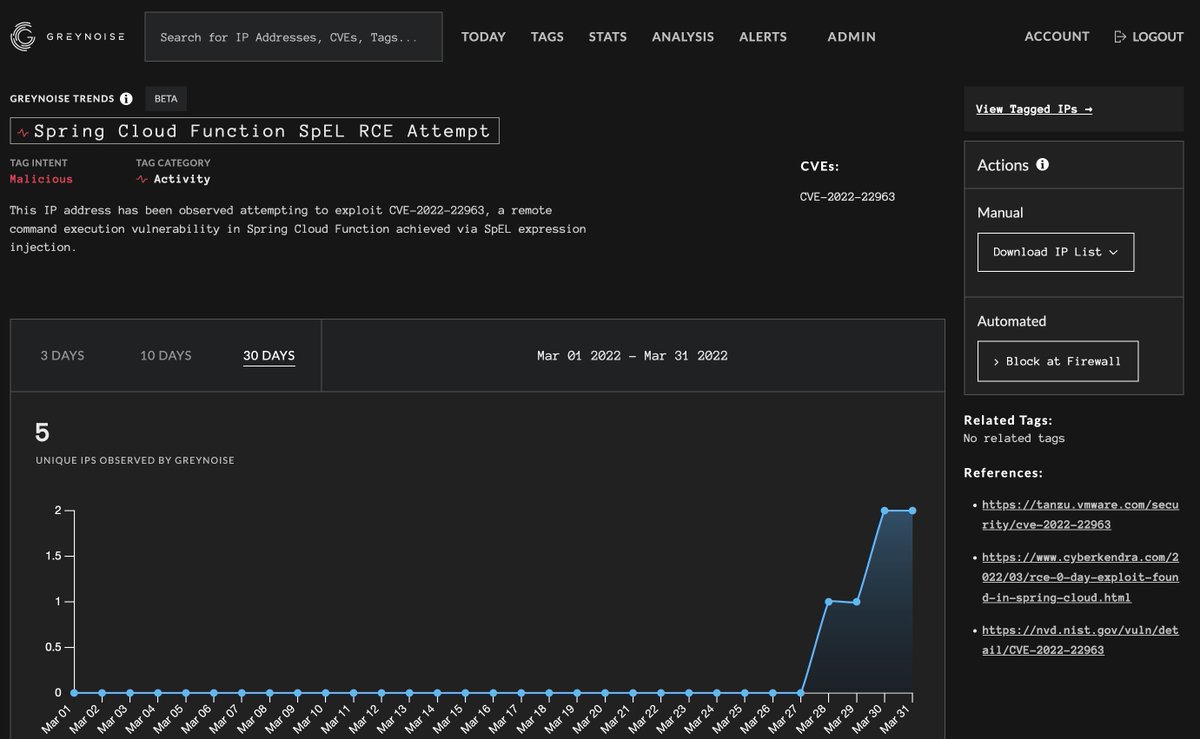
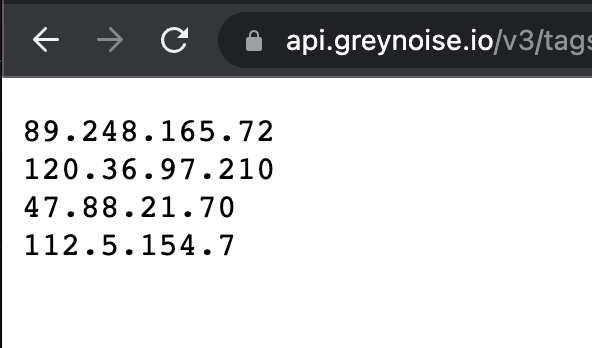
GreyNoise is tracking, has tags available for, and HAS observed exploitation of 2 different "Spring" vulnerabilities in the wild, including #SpringShell. Time series / free dynamic custom block list URLs here:34889
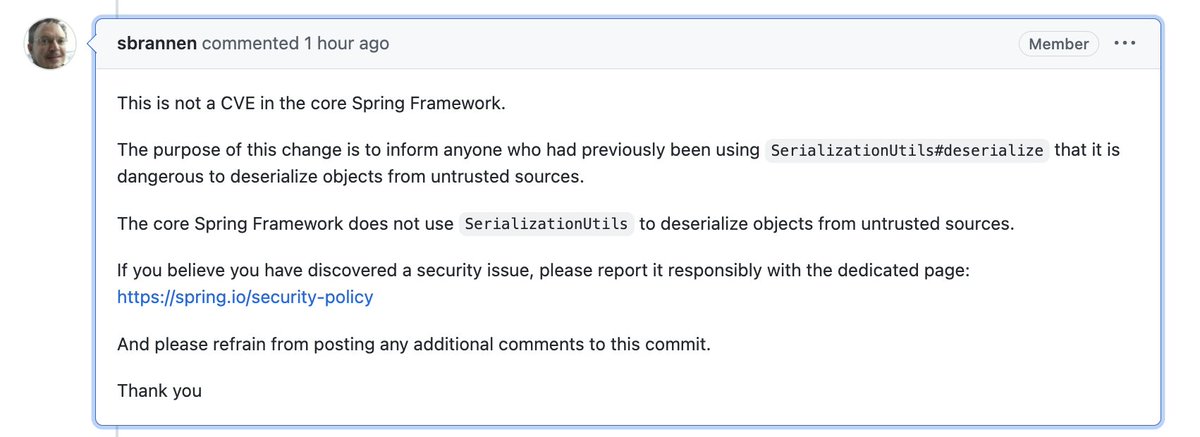
Ax Sharma@Ax_SharmaToo much chatter about an *unconfirmed* RCE in Spring Core — based on 1 minor commit that deprecates Java deserialization in one of the classes. Spring Core dev @Sam_Brannen confirms this is NOT a flaw, but a mere warning to anyone practicing untrusted deseriazation.21335
Ax Sharma@Ax_Sharma@Ax_SharmaAnother PoC for SPEL Expression Injection 🙃 once again CVE-2022-22963, that does NOT impact Spring core:bytehx @bytehx343Spring Cloud Function Spel RCE aka CVE-2022-22963 POC. payload T(java.lang.Runtime).getRuntime().exec("xcalc")313
Spring Cloud Function Spel RCE aka CVE-2022-22963 POC. payload T(java.lang.Runtime).getRuntime().exec("xcalc")6192573
Ax Sharma@Ax_Sharma@Ax_SharmaUPDATE: Thus far, @praetorianlabs, @pwntester, @testanull and few others have confirmed the #SpringShell PoC working. Would be nice to get an official update from @springframework 🕙⏳116
Don't miss this analysis of the #Spring4Shell vulnerability to learn what it is & how to mitigate any potential risk. Check it out at @SaltSecurity ▶️ #springshell #cybersecurity005
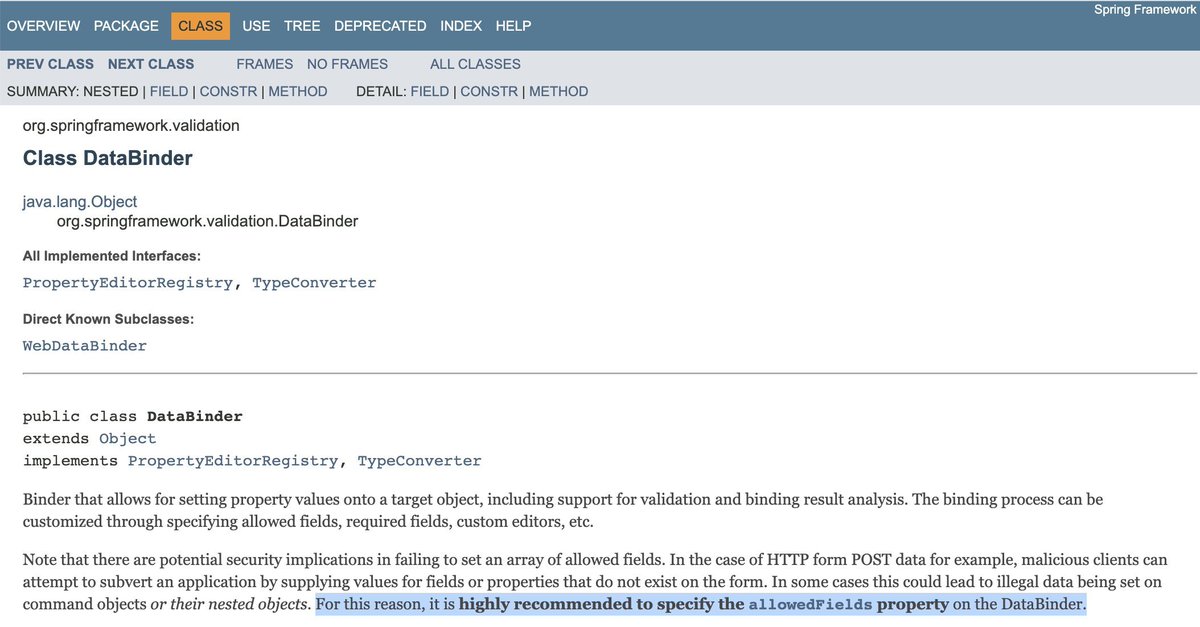
Ax Sharma@Ax_Sharma👀 Re: #SpringShell that's still awaiting a CVE: Spring's documentation explicitly stresses to use "allowedFields" on DataBinder h/t @ryotkak105
Ax Sharma@Ax_Sharma@Ax_SharmaA non-intrusive way to test if SpringShell RCE impacts your setup. HTTP 400 = yes.Randori Attack Team @RandoriAttackThe following non-malicious request can be used to test susceptibility to the @springframework 0day RCE. An HTTP 400 return code indicates vulnerability. $ curl host:port/path?class.module.classLoader.URLs%5B0%5D=0 #SpringShell #Spring4Shell #infosec102
Randori Attack Team@RandoriAttackThe following non-malicious request can be used to test susceptibility to the @springframework 0day RCE. An HTTP 400 return code indicates vulnerability. $ curl host:port/path?class.module.classLoader.URLs%5B0%5D=0 #SpringShell #Spring4Shell #infosec10192531
Checkmarx is closely monitoring #Spring4Shell and all other Spring vulnerabilities (CVE-2022-22963, CVE-2022-22950). Checkmarx SCA customers can scan their code for those vulnerabilities and get the latest remediation solutions. #springshell156- Afficher plus de posts