Posty z #https

#https

Publiczne posty w X, które używają #https.

Powiązane hashtagi

  1. pilvar (Philippe Dourassov)✓@pilvar222
    We made a website to check if your http client is vulnerable to CVE-2026-111497 (Node2Shell/HTTP2Shell) Also open-source: Some examples:
    Pobierz
    63120516.4K
  2. Cyber Security News✓@The_Cyber_News
    ‼️ PHP Releases New Windows Build Security Updates to Fix Critical HTTP2Shell Vulnerability Details: The PHP team has released updated Windows builds to fix a serious flaw known as HTTP2Shell. The new packages are PHP 8.5.12-1, 8.4.27-1, 8.3.36-1, and 8.2.35-1, and PHP announced them on October 26, 2026. Each build now includes Brotli 1.2.1, which fixes CVE-2026-111497. Windows users who run PHP should install these packages without delay. The flaw sits in Google’s Brotli library, a compression tool that many programs use to unpack data. It is an out-of-bounds write, which means the code writes data past the memory area it was meant to use. PHP’s own advisory explains how the flaw reaches PHP on Windows. The vulnerable decoder can be reached through the cURL extension when automatic HTTP response decompression is turned on. #CybersecurityNews
    Pobierz
    1311744635.8K
  3. HKEPC✓@hkepcmedia
    【緊急通知 ⚠️】起身打「丁」 !! 「HTTP2Shell」世紀級漏洞登場,這個漏洞原本是 Node.js 中引發的「Node2Shell」9.2 分高危漏洞(CVE-2026-111497)。隨著調查深入後發現越來越「大件事」,原來該漏洞背後是源自 Google Brotli 資料壓縮解碼器中的記憶體越界寫入缺陷。這項技術廣泛應用於現代 HTTP 流量壓縮與解壓縮架構,全球包含 Node.js、Bun、C++、Python……(不能盡錄)開發軟體、反向代理伺服器及大量 HTTP 應用與程式庫皆受到波及,全球網絡將面臨極嚴峻的遠端代碼執行(RCE)及阻斷服務(DoS)攻擊。 根據資安情報團隊 Aikido Intel 指出,CVE-2026-111497 最初由 Node.js 官方於安全性更新中釋出修補,並由安全研究團隊命名為「Node2Shell」。然而,經過逆向工程與跨平台相依性比對後發現,問題核心並非 Node.js 本身的邏輯錯誤,而是其內建由 Google 開發的開源壓縮程式庫 Brotli(版本 1.0.3 至 1.2.0)存在嚴重的解碼邊界處理缺陷。 由於 Brotli 是目前網際網路標準中用於最佳化傳輸頻寬的核心技術之一,大量伺服器與中介軟體均預設啟用該壓縮演算法。資安機構確認其「爆炸半徑」(Blast Radius)遠超預期,正式將威脅升級為「HTTP2Shell」,警告任何處理 HTTP 壓縮內容的相關服務皆可能暴露於危險中。 根據 CVE 漏洞通報,「HTTP2Shell」仍會沿用 CVE-2026-111497,原本 CVSS 9.2 評分可能會進一步上修,它是屬於緩衝區溢位與越界寫入漏洞(CWE-787、CWE-252),存在於 Brotli 解碼器的 c/dec/decode.c 核心代碼中。 當目標伺服器或客戶端應用程式接收到特製的惡意 Brotli 壓縮資料流(例如帶有 Content-Encoding: br 的 HTTP 請求或回應)時,解碼器在未能正確校驗回傳值的狀態下展開資料,將導致記憶體堆疊毀損,攻擊者可利用此漏洞達成以下後果: ◾遠端代碼執行(RCE): 資安研究人員已在特定架構的 Linux 環境下完成概念驗證(PoC),能藉由惡意 HTTP 封包取得底層主機執行權限。 ◾阻斷服務(DoS): 觸發核心分段錯誤(Segmentation Fault),造成常駐程序崩潰重啟,中斷連線服務。 ◾敏感資訊外洩: 記憶體殘留讀取可能導致暫存於 Heap 中的 Token、加密金鑰或未授權資料外洩。 目前仍無法估計完整的受影響範圍,只知道受影響的開源生態系與執行環境相當龐大,包括︰ ◾Node.js 執行環境: 22.x、24.x 與 26.x 之未修補版本,以及已終止支援(EOL)的舊版本(如 Node.js 20.x 及更早版本,官方不再釋出開源更新修補)。 ◾Bun 執行環境: 1.4.4 之前版本。 ◾Python 生態系: PyPI 上的 Brotli(<=1.2.0)與 brotlicffi(<=1.2.0.x)套件。相依於上述套件的常見 HTTP 請求庫(如 requests、urllib3、httpx、aiohttp 及 Scrapy 等爬蟲框架)在解析 Brotli 回應時均會觸發。 ◾反向代理與閘道器: Envoy(1.40.0 以前特定版本)、Istio 服務網格等。 ◾原生系統函式庫: 系統內建的 libbrotli(1.0.3 ~ 1.2.0)以及動態/靜態鏈結 Brotli 的 curl / libcurl 工具。 資安專家呼籲企業與網站管理者立即作出緊急防護與修補,採取的措施如下︰ ◾升級 Node.js 與 Bun: 立即將 Node.js 更新至 22.23.4、24.22.1 或 26.12.1 安全版本;Bun 需升級至 1.4.4 以上。使用 Node.js EOL 版本的用戶應盡速評估遷移架構或採用擴展維護方案。 ◾升級 C++ 版本至 1.0.10、1.1.1 及 1.2.1 安全版本或以上。 ◾立即更新 Python 相依套件至 1.2.1.0 版本或以上,並且在更新後務必重新建置容器映像檔(Container Images)與鎖定檔(Lockfile)。 ◾檢查 Linux 發行版的安全修補通告,升級 libbrotli 至 1.2.1(舊維護分支為 1.0.10 / 1.1.1),並同步更新 API Gateway、Envoy 與反向代理伺服器。 ◾以上這個修補清單只是暫時的,預期這份清單將會越來越長。 由於「HTTP2Shell」漏洞詳情已經公開,致使未修補伺服器的受攻擊風險大幅飆升,各位管理員必須作出緊急維護,以免成為攻擊目標。
    Pobierz
    Aikido @AikidoSecurity
    Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.” A significant blast radius. This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression. Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
    22619916.4K
  4. Aikido✓@AikidoSecurity
    Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.” A significant blast radius. This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression. Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
    Pobierz
    1188533.5K813K
  5. Movez✓@0xMovez
    i reverse engineered my Wi-Fi router with Claude and found a f*cking scary privacy problem... my provider could see every website I looked up. in plain text. so I built an open-source app where AI agents guard my network: Claude, ChatGPT or Grok. → it runs on your Claude or ChatGPT subscription. Mac & Windows here’s the build step by step: • step 1 → open Claude Code on Opus 5.5 in an empty folder, paste the prompt below • step 2 → stack: one Electron codebase for macOS and Windows. Node does the network checks, no admin rights needed • step 3 → Opus split the build across 9 parallel agents. one built the router scanner, one the Wi-Fi + speed test, one the AI agents, one the device list, one the installers every agent got a reviewer. every reviewer got a fixer. 27 agents before I saw the first screen • step 4 → the scanner checks 12 doors: provider remote control (TR-069, port 7547), UPnP port-forwards, Telnet, SSH, plain-HTTP admin page, unencrypted DNS, Wi-Fi security, location-map opt-out • step 5 → first real scan of my network: provider sees all my DNS lookups, SSH open on the router, UPnP on, 22 neighbour networks fighting for my channel. score 77/100 • step 6 → the AI agents. they read the scan and answer “what should I fix first?” or “is anything on my network suspicious?” before anything leaves my PC, Bastion strips MAC addresses, device names, Wi-Fi names and the last part of my IP watch mode re-checks the network every 5–60 min and only wakes the agent when something changed • step 7 → no API key. Bastion talks to Claude through Claude Code and to ChatGPT through Codex, using the login I already had • step 8 → a separate security agent attacked every line of it and found 11 holes. all fixed: the CLIs run with zero tools, read-only, in an empty folder. my question goes in through stdin, so nothing can be injected into a command. it refuses to start if Codex’s shell tool is on • step 9 → real bugs only real hardware shows: my Windows is in Russian, so Opus taught the parser Russian netsh labels. Windows 11 hides Wi-Fi info until you allow Location. Cloudflare rate-limited the speed test (HTTP 429), so Opus switched to fewer, bigger requests. next run: works • step 10 → before the repo went public, Opus checked that none of my IPs, MAC addresses or network names were in the code one evening. zero lines written by me. that’s it... agents suggest, you decide. Bastion never logs in to your router, never tries a password and never changes a setting on its own Find the GitHub repo and the full prompt below ↓ Then read the article on how to reverse engineer anything with Opus 5.5 ↓
    Pobierz
    Movez @0xMovez
    4171117.3K
  6. Movez✓@0xMovez
    224041.6K1.8M
  7. Cyber Security News✓@The_Cyber_News
    ‼️ Hackers Launch 8,200 DDoS Attacks Every Hour, Cloudflare’s Latest Report Reveals Details: Cloudflare blocked an average of more than 8,200 network-layer DDoS attacks every hour during the third quarter of 2026, showing how attackers are using frequent, short bursts to disrupt online services rather than relying only on record-breaking traffic floods. The hourly figure reflects attacks detected across Cloudflare's network, not a complete worldwide total. Its systems filtered 272.6 petabytes of network-layer traffic and another 95.1 petabytes of HTTP attack traffic. Network-layer attack numbers increased 208% compared with the same quarter in 2025. About 96% ended within ten minutes, while 98% stayed below one gigabit per second. That traffic can still overwhelm a website or server without enough protection. #cybersecuritynews
    Pobierz
    47230114.5K
  8. The Hacker News@TheHackersNews
    ‼️ PHP patches Windows builds AGAIN, just 5 days after the PHP2Shell fixes. This time, a Brotli flaw could allow code execution when cURL automatically decompresses crafted HTTP responses. Updated builds cover PHP 8.2–8.5. Full details:
    Pobierz
    1512552168.4K
  9. ab@airbon2015
    HTTP2Shell 脆弱性 10月21日(水):Node.jsの修正公開で表面化 PHPに続き来週も大混乱?銀行証券などなども緊急リリース? 問題:Brotli(圧縮データ)の展開処理 影響:HTTPで受け取るだけで乗っ取りの恐れ 対応:開発環境のアップデート、ビルド、リリース 個人開発はAIで問題把握も対策もDONE!
    Pobierz
    GrEarl @Iamwonderingif
    お~ん...PHPどころじゃねえや HTTP2Shell(CVE-2026-111497)出てるし... 個人にできる対策は"通信するすべて"の更新しかない eMud問題で更新祭りだったけどもう一回です ブラウザ・Node.js・Python・Bun・Curl等Brotil使うものすべて更新必須
    2269219.9K
  10. GrEarl✓@Iamwonderingif
    お~ん...PHPどころじゃねえや HTTP2Shell(CVE-2026-111497)出てるし... 個人にできる対策は"通信するすべて"の更新しかない eMud問題で更新祭りだったけどもう一回です ブラウザ・Node.js・Python・Bun・Curl等Brotil使うものすべて更新必須
    111.5K4.8K466K
  11. Freddy Montes✓@fmontes
    Hoy el Internet amaneció en llamas: un agujero en PHP (70% de los sitios web) y certificados HTTPS falsos. Europa está recomendando apagar los servidores que no se puedan parchar. Lo que sí podés hacer: actualizar tu browser. #ciberseguridad #PHP #HTTPS
    Pobierz
    419157436.2K
  12. GGSec@GGASecDe
    Research: we reproduced CVE-2026-109618/109619 on php:8.4.26-apache (aarch64). Pure HTTP - no gdb, no /proc on target. 4 requests: arm -&gt; 819,200-byte disclosure -&gt; addresses -&gt; system() as www-data. 6/6 runs, ASLR different every time. Tonight: every step
    Pobierz
    42313716.6K
  13. GeekNews✓@GeekNewsHada
    HTTP2Shell - Node․js에서 Python까지, Brotli 의존성으로 퍼진 원격 코드 실행 취약점 공격자가 조작한 Brotli 압축 데이터를 해제하면 메모리 유출, 프로세스 충돌, 원격 코드 실행으로 이어질 수 있음. 서버로 들어오는 요청뿐 아니라 외부 서버에서 받아 오는 응답도 공격 경로가 됨 Python에서는 다른 패키지를 통해 설치된 Brotli를 HTTP 클라이언트가 자동 사용하므로, 코드에서 직접 불러오지 않았어도 영향받을 수 있음 Brotli 1.2.1 또는 brotlicffi 1.2.1.0 이상으로 업데이트하고, 이를 포함한 컨테이너와 애플리케이션도 다시 빌드해 배포 필요. 요청의 Accept-Encoding: br만 제거하는 것으로는 방어가 충분하지 않음
    014394.3K
  14. GGSec@GGASecDe
    Closing out #php2shell: a universal black-box PoC for PHP's session upload-progress bug. One pure-HTTP chain - arm the allocator, spray fake refs, leak the heap, beat ASLR, turn a destructor into system(). Verified blind on Debian 13 PHP 8.4.24, x86-64 + arm64: RCE as www-data.
    Pobierz
    32212.3K
  15. 歯磨きしても臭かった人✓@koushu_selfcare
    【Google Chrome必須】パソコン版セキュリティ最強設定|フィッシング・不正サイトから身を守る Google Chromeをパソコンで使っている人は、これをやっていないと危険です。 証券口座や銀行アプリと同じくらい、ここを固めてください。 ■今すぐやるべき設定(優先順) ① セーフブラウジングを「保護強化機能」にする(最重要) Chrome右上の「⋮」→ 設定 → プライバシーとセキュリティ → セキュリティ 「セーフブラウジング」で「保護強化機能」を選択 フィッシングやマルウェアサイトをより強力にブロックします。 ② 「常に安全な接続を使用する」をオンにする 同じセキュリティ画面で「安全な接続」→「常に安全な接続を使用する」をオン HTTPの危険なサイトにアクセスする前に警告が出ます。 ③ パスワード漏洩警告をオン セキュリティ画面の詳細設定で「データ侵害によりパスワードが漏洩した場合に警告する」をオン ④ 拡張機能を見直す 右上「⋮」→ 拡張機能 → 管理 使っていないもの・怪しいものは削除。信頼できるものだけ残す。 ⑤ Chromeを常に最新に保つ 右上「⋮」→ ヘルプ → Google Chromeについて 自動更新を確認し、最新版にする。 ■追加でやっておくと安心 ・Googleアカウント自体にパスキーや2段階認証を設定(別途必須) ・不要なサイト権限(位置情報・カメラ・通知)を制限 ・シークレットモードを適切に使う ・怪しいリンクは絶対にクリックしない 保護強化機能+HTTPS強制が現時点の実践的な最強寄り設定です。 設定した人はリプで「完了」と教えてください!
    Pobierz
    214490563K
  16. ahhhhfs✓@abskoop
    MediaGo 是一款跨平台开源视频下载器,支持 M3U8 / HLS 资源提取,也把 yt-dlp、N_m3u8DL-RE、BBDown、aria2 这些工具整到了一套界面里。 支持 Windows、macOS、Linux,还能用 Docker 部署到 NAS 或服务器,通过 Web UI 跨设备管理下载任务。 比较有意思的是它还提供 HTTP API 和 OpenClaw Skill,可以让 Claude Code、Cursor 这类 AI Agent 直接把任务交给 MediaGo 处理。 平时要处理自己保存的 M3U8 / HLS 资源,又不想每次开终端敲 yt-dlp,可以看看它。 👉 #M3U8 #Docker
    Pobierz
    1888722.5K
  17. Edward✓@EdwardTWinz
    ⚠️🚨 THIS IS NOT A DRILL 🚨⚠️ Google has officially declared a bug in Brotli, its tool that shrinks web traffic, CRITICAL: 9.2 out of 10. Last night "Node2Shell" evolved into HTTP2SHELL. A formal CVE record has been issued citing CVE-2026-111497 -- a hole in versions 1.0.3 to 1.2.0 that can hit any app unpacking data from strangers, and could let them take it over. What this means: ▪️ This is not a Node.js problem anymore. This is an HTTP PROBLEM. ▪️ Every unpatched app across Node.js, Python, Bun, and Envoy that unpacks Brotli now has a hole attackers need no login to use ▪️ Istio. curl. Python's requests and httpx. All at risk under one CVE. ▪️ EVERY project that bundles Brotli must ship its own fix, and not all are out yet This changes everything. A normal bug can be fixed in one place. A 9.2 bug inside a shared tool cannot. We just entered the most dangerous phase of this crisis. If you're not paying attention - start now. Save this. Share this. This is the moment it escalated beyond return.
    Pobierz
    593571.7K203K
  18. Riya Pal✓@itsriyapal
    As a dev, can you explain the difference between: &gt;HTTP &gt;HTTPS Why do we need HTTPS if both can transfer data over the internet? 🤔
    Pobierz
    324354.1K
  19. Ed✓@ed__marquez
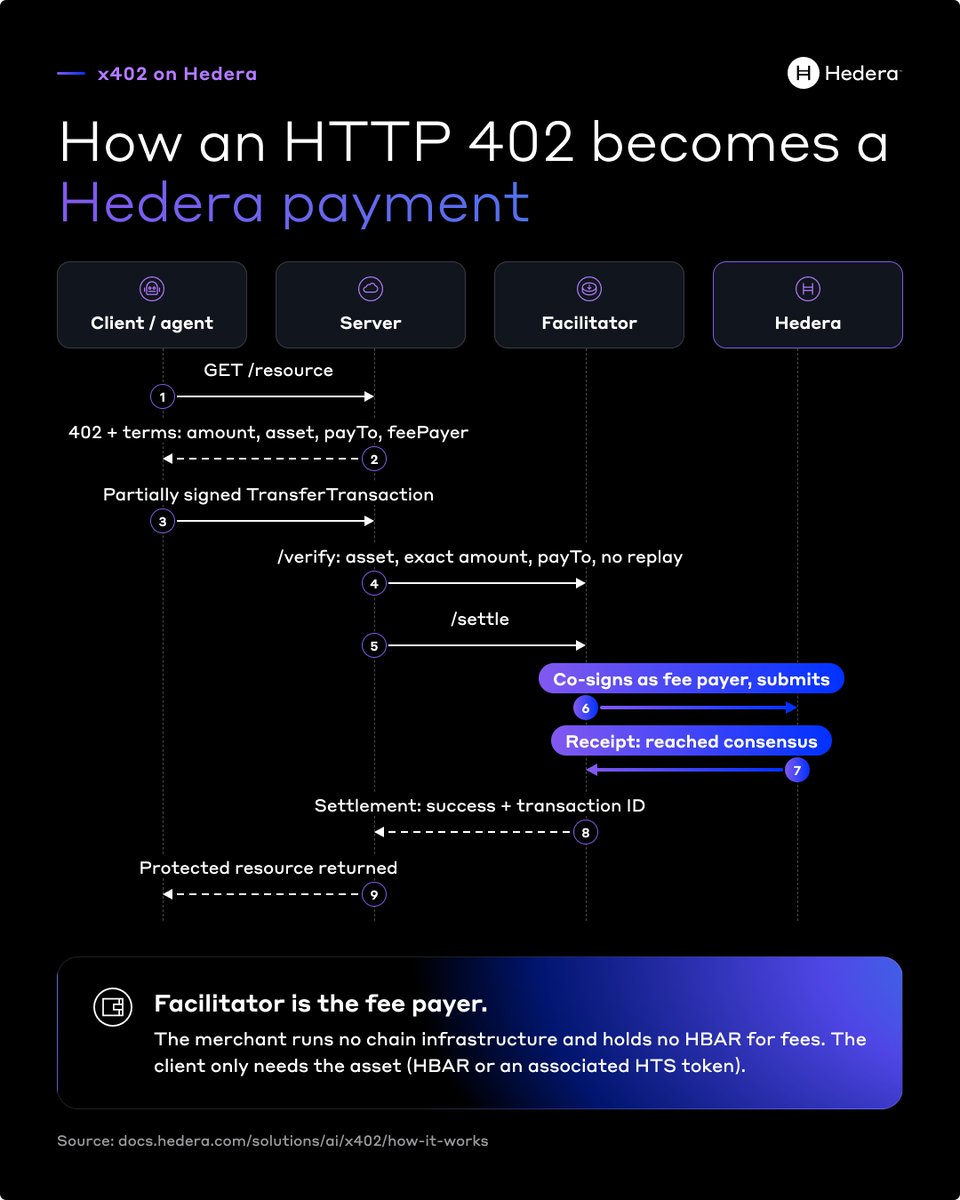
    1/ HTTP has a status code for payments that was never really used: 402 Payment Required x402 is an open standard that puts it to work A server asks for payment inside a normal request, and a client, like an AI agent, pays without a checkout page or an account... kinda genius
    Pobierz
    417693.4K
  20. Paranoid✓@paranoiddotred
    Introducing IP Shield on PARANOID. Your IP address can give away your city, your home and, through your internet provider, your name. Until now it traveled with every question you asked. Turn on IP Shield and the server that reads your questions never sees your IP address, so what you ask can no longer be traced back to where you are. How is that possible? Your browser does the work before anything leaves your computer. When you ask a question, your browser takes PARANOID’s public key and seals the entire request with HPKE, the modern encryption standard that pairs an X25519 key exchange with AES-GCM. Every question gets a brand new one-time key, so even two questions from the same person look like strangers to each other. The sealed request goes to a relay first. The relay sees your IP address next to a block of bytes it cannot read, and it passes those bytes on under its own address. Only PARANOID’s private key can open them, and inside it finds your question with the relay’s address on it instead of yours. The answer travels back the same way, sealed with a key that only your browser holds, so the relay never reads that either. This is Oblivious HTTP, the IETF standard published as RFC 9458. It is the same design that sits in front of Apple’s Private Cloud Compute and Chrome’s Safe Browsing checks, and now it sits in front of your AI chats. It is one switch above the chat, with nothing to install. Live today at
    Pobierz
    109412.9K
  21. cozy📷コスプレ撮る人✓@cozy1215
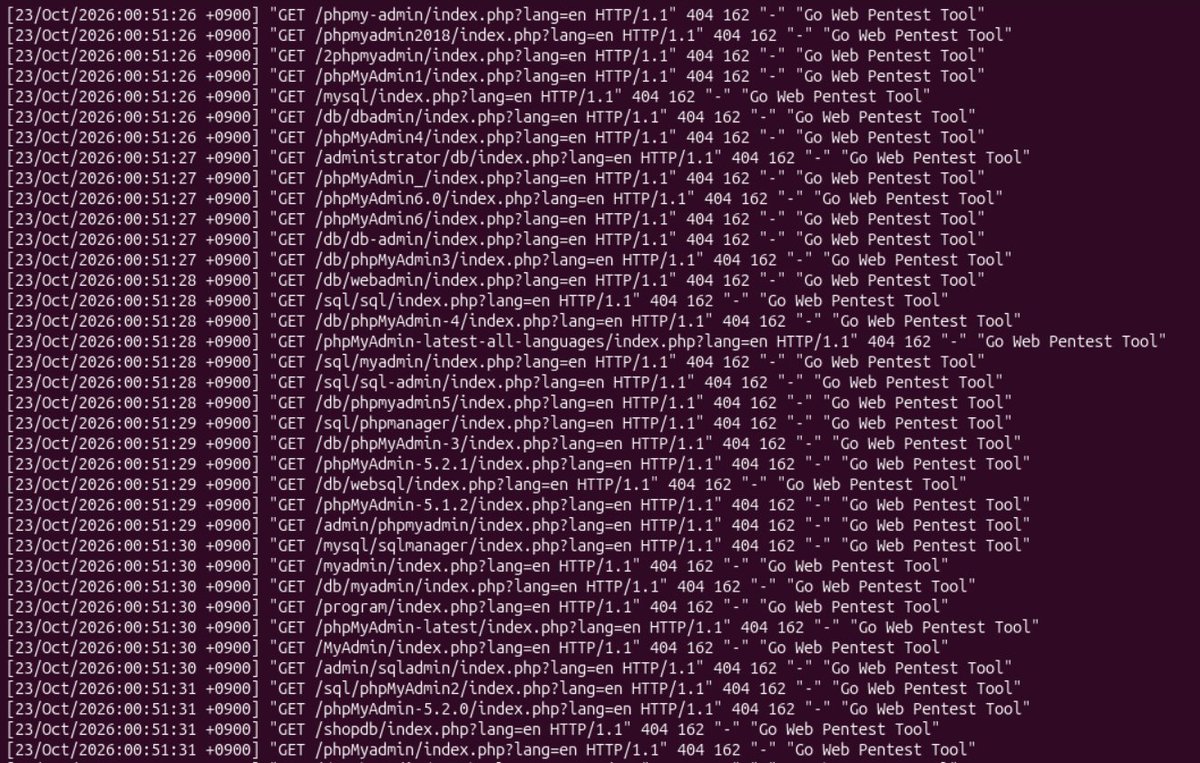
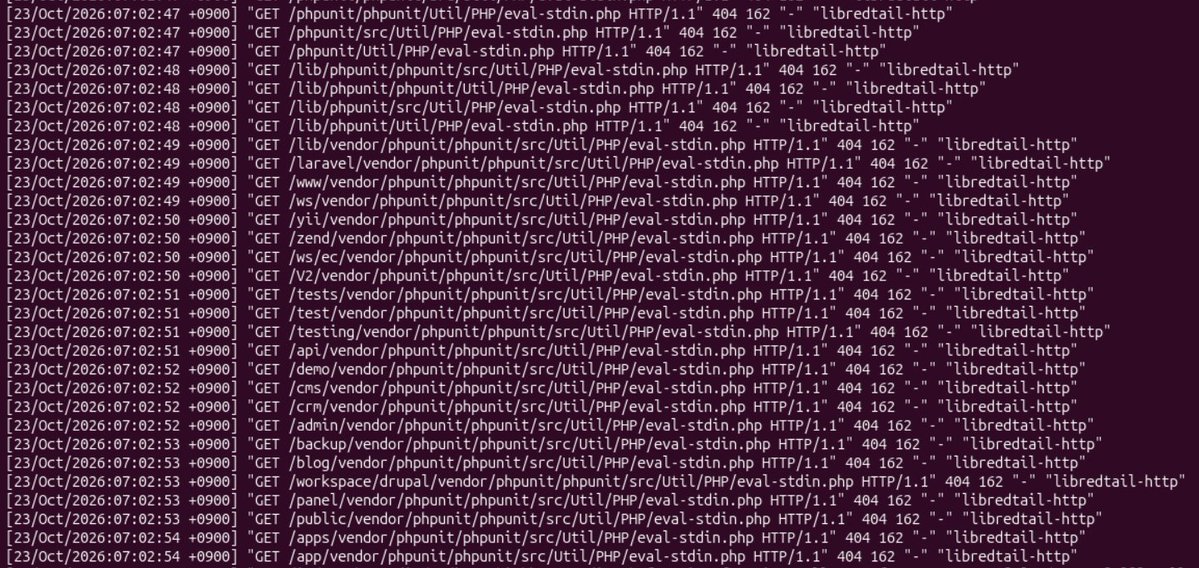
    まだ何もコンテンツを置いていないVPSサーバーのアクセスログ見たらめっちゃ攻撃されてた phpmyadmin、wordpress、laravel、.gitとか総当たりで試されてる Go Web Pentest Toolやlibredtail-httpなどのUser-Agentからの攻撃が多かった チャッピーにログをしてもらった結果は3枚目
    Pobierz
    5114393121K
  22. Pokaż więcej postów