Postări cu #https

#https

Postări publice de pe X care folosesc #https.

Hashtaguri înrudite

  1. MSR🌶🍫@monikafilefan
    well guess this is a good time to reshare some of my fave fics that aren’t on ao3 in case y’all are already slowly suffering withdrawals and need that fic fix
    5141715.2K
  2. pilvar (Philippe Dourassov)✓@pilvar222
    We made a website to check if your http client is vulnerable to CVE-2026-111497 (Node2Shell/HTTP2Shell) Also open-source: Some examples:
    Descarcă
    63120616.5K
  3. Cruz✓@ViC305
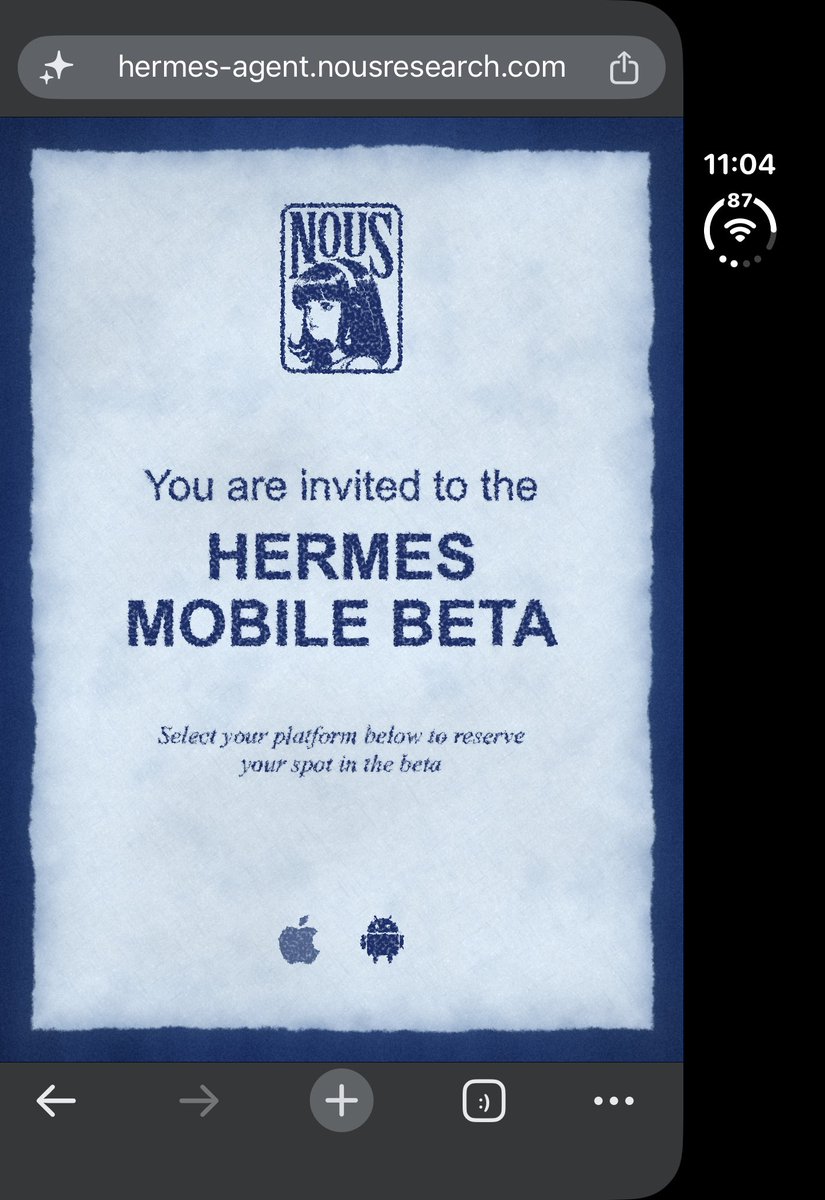
    🚨 𝗛𝗘𝗥𝗠𝗘𝗦 𝗠𝗢𝗕𝗜𝗟𝗘 𝗕𝗘𝗧𝗔 — 𝗦𝗘𝗟𝗙-𝗛𝗢𝗦𝗧𝗘𝗗 𝗦𝗘𝗧𝗨𝗣 𝗚𝗨𝗜𝗗𝗘! 📱🔥 I've spent over a DECADE in systems engineering, and somehow getting the new Hermes Mobile Beta connected to my own self-hosted @NousResearch Hermes Agent still gave me a little trouble! 😂 So here's a quick guide to save everyone else the headache! ━━━━━━━━━━━━━━━━━━━━ 🖥️ 𝗦𝗧𝗘𝗣 𝟭 — 𝗦𝗧𝗔𝗥𝗧 𝗧𝗛𝗘 𝗗𝗔𝗦𝗛𝗕𝗢𝗔𝗥𝗗 On the machine running Hermes: hermes dashboard --host 0.0.0.0 --port 9119 --no-open On first interactive setup, Hermes can prompt you to create a username and password. SAVE THOSE! 🔒 𝗣𝗥𝗘𝗙𝗘𝗥 𝗧𝗔𝗜𝗟𝗦𝗖𝗔𝗟𝗘? (Recommended) Bind directly to your machine's Tailscale IP instead: hermes dashboard --host 100.x.x.x --port 9119 --no-open ━━━━━━━━━━━━━━━━━━━━ 📱 𝗦𝗧𝗘𝗣 𝟮 — 𝗚𝗥𝗔𝗕 𝗧𝗛𝗘 𝗕𝗘𝗧𝗔 ⚙️ 𝗦𝗧𝗘𝗣 𝟯 — 𝗦𝗘𝗟𝗘𝗖𝗧 𝗦𝗘𝗟𝗙-𝗛𝗢𝗦𝗧𝗘𝗗 NOT Nous Portal! You're connecting to your OWN Hermes instance. 🌐 𝗦𝗧𝗘𝗣 𝟰 — 𝗘𝗡𝗧𝗘𝗥 𝗬𝗢𝗨𝗥 𝗚𝗔𝗧𝗘𝗪𝗔𝗬 𝗨𝗥𝗟 🏠 Home Wi-Fi: http://192.168.x.x:9119 🔐 Tailscale: http://100.x.x.x:9119 Replace the example IP with your Hermes machine's actual address. 🔑 𝗦𝗧𝗘𝗣 𝟱 — 𝗘𝗡𝗧𝗘𝗥 𝗬𝗢𝗨𝗥 𝗖𝗥𝗘𝗗𝗘𝗡𝗧𝗜𝗔𝗟𝗦 Use the dashboard username and password you configured earlier. ✅ 𝗦𝗧𝗘𝗣 𝟲 — 𝗧𝗔𝗣 𝗖𝗢𝗡𝗡𝗘𝗖𝗧! That's it. Your self-hosted Hermes Agent, accessible from your phone! 🙌 ━━━━━━━━━━━━━━━━━━━━ 💡 𝗧𝗪𝗢 𝗜𝗠𝗣𝗢𝗥𝗧𝗔𝗡𝗧 𝗧𝗜𝗣𝗦: • Your phone must be on the same reachable network or connected through Tailscale. • Never expose port 9119 directly to the public internet with basic password authentication. I recommend Tailscale! Hopefully this saves someone else the troubleshooting session I went through! 😂 Enjoy Hermes Mobile! 📱💚 This thing packs a punch and even connects to your Hermes desktop sessions, something I’ve been in DESPERATE need of!! 🔥
    Descarcă
    302131426.7K
  4. GGSec@GGASecDe
    Closing out #php2shell: a universal black-box PoC for PHP's session upload-progress bug. One pure-HTTP chain - arm the allocator, spray fake refs, leak the heap, beat ASLR, turn a destructor into system(). Verified blind on Debian 13 PHP 8.4.24, x86-64 + arm64: RCE as www-data.
    Descarcă
    37516.1K
  5. http@http_yap
    ハッピ~ハロウィンらくがき
    Descarcă
    0861K11.4K
  6. The Hacker✓@theprocracker
    Why cleartext HTTP is a security nightmare 🕵️‍♂️🔒 Quick tutorial at how network protocols handle data if it isn’t encrypted with SSL/TLS • 127.0.0.1 •
    Descarcă
    2211424.9K
  7. 小能猫✓@n7wb1l
    一键反编译 Android 应用并逆向提取全套 HTTP API 的 AI 技能扩展:Android Reverse Engineering Skill 📱🔓 告别繁琐的静态分析,让 Claude 帮你秒级分析 APK/XAPK、恢复混淆类名并提取完整 API 接口与鉴权逻辑 👥 【适用人群】 适合需要快速逆向分析 Android 应用、提取第三方服务 API 接口、分析应用安全漏洞或重构代码逻辑的移动端开发者与安全研究人员 🎯 【核心 3 大杀手级功能与架构亮点】 1️⃣ 快速指纹识别与智能反编译:秒级检测 Flutter/RN 框架与混淆层,内置 jadx 及 Fernflower 引擎双向比对 2️⃣ Kotlin 混淆恢复与 API 提取:利用 Kotlin 元数据还原被 R8 混淆的 ViewModel/Repository 类名,自动提取 Retrofit/Ktor 接口与 HMAC 签名逻辑 3️⃣ 端到端调用流链路追踪:从 Manifest 页面交互层追踪至 ViewModel 并下钻到底层 HTTP 网络请求,透视完整架构 💡 架构亮点:采用跨平台 Shell 与 PowerShell 脚本封装底层 JADX 工具链,作为 Claude Code 插件无缝嵌入 AI 驱动的命令行逆向工作流 ⚡️【极速安装与挂载指令】 在 Claude Code 中直接执行命令即可添加该 Skill: /plugin marketplace add SimoneAvogadro/android-reverse-engineering-skill ⭐ Star 数:约 8.2k 🔗 开源仓库: #Android #ReverseEngineering #ClaudeCode #JADX #APK #API #开源项目 #开发者工具 #安全工具
    1810863023.2K
  8. Hanny Butter💕@hannytomi
    I no go lie, Fury of Anubis and Henhouse hustle don hold me hostage😅. But when you hear say 400k dey drop for 50 people daily from 7pm-9pm? You go understand why I no fit commot. Play responsibly ooo #BetwayDailyJackpots Join here: http//betwayplay.org/bwx
    Descarcă
    14121411.3K
  9. Codez✓@0xCodez
    i reverse engineered my Wi-Fi router with Claude Opus 5.5 and found a f*cking scary privacy problem... every site I opened, my provider saw it. no encryption. just a readable list. so I built a free open-source app that puts AI agents on watch over my network: Claude, ChatGPT or Grok. → works on Mac & Windows, powered by the Claude or ChatGPT subscription you already pay for here’s exactly how I built it: • step 1 → empty folder, Claude Code, Opus 5.5. paste the prompt from below and hit enter • step 2 → the stack: a single Electron codebase that ships to both macOS and Windows. all network checks run in Node, so no admin rights required • step 3 → Opus broke the work into 9 agents running in parallel. router scanner, Wi-Fi + speed test, AI agents, device list, installers. each piece had its own agent on top of that, each agent had a reviewer, and each reviewer had a fixer. 27 agents were running before the first screen even appeared • step 4 → the scanner probes 12 entry points: provider remote access (TR-069, port 7547), UPnP port-forwards, Telnet, SSH, admin page over plain HTTP, unencrypted DNS, Wi-Fi security, location-map opt-out • step 5 → the first scan on my own network came back with: all DNS lookups visible to my provider, SSH open on the router, UPnP enabled, 22 neighbour networks crowding my channel. score: 77/100 • step 6 → the AI agents. they take the scan results and answer questions like “what do I fix first?” or “does anything on my network look suspicious?” nothing leaves my PC raw. Bastion removes MAC addresses, device names, Wi-Fi names and the last part of my IP first watch mode rescans every 5–60 min and only calls the agent when something actually changed • step 7 → no API keys anywhere. Claude is reached through Claude Code, ChatGPT through Codex, with the logins I already had • step 8 → then a dedicated security agent went after every line of code. it found 11 holes. all closed: the CLIs run read-only, with zero tools, inside an empty folder. questions are passed through stdin, so there’s no way to inject anything into a command and if Codex’s shell tool is enabled, Bastion won’t start at all • step 9 → the bugs you only hit on real hardware: Windows 11 hides Wi-Fi details until Location is allowed. Cloudflare rate-limited the speed test (HTTP 429), so Opus switched to fewer, larger requests. next run: clean • step 10 → before making the repo public, Opus scanned it to make sure none of my IPs, MAC addresses or network names had slipped into the code one evening. not a single line written by me. that’s it... the agents advise, you make the call. Bastion never logs in to your router, never guesses a password and never touches a setting on its own GitHub repo + the full prompt below ↓ Then read the article on how to reverse engineer anything with Opus 5.5
    Descarcă
    Movez @0xMovez
    2410947.4K
  10. Movez✓@0xMovez
    234111.6K1.9M
  11. Movez✓@0xMovez
    i reverse engineered my Wi-Fi router with Claude and found a f*cking scary privacy problem... my provider could see every website I looked up. in plain text. so I built an open-source app where AI agents guard my network: Claude, ChatGPT or Grok. → it runs on your Claude or ChatGPT subscription. Mac & Windows here’s the build step by step: • step 1 → open Claude Code on Opus 5.5 in an empty folder, paste the prompt below • step 2 → stack: one Electron codebase for macOS and Windows. Node does the network checks, no admin rights needed • step 3 → Opus split the build across 9 parallel agents. one built the router scanner, one the Wi-Fi + speed test, one the AI agents, one the device list, one the installers every agent got a reviewer. every reviewer got a fixer. 27 agents before I saw the first screen • step 4 → the scanner checks 12 doors: provider remote control (TR-069, port 7547), UPnP port-forwards, Telnet, SSH, plain-HTTP admin page, unencrypted DNS, Wi-Fi security, location-map opt-out • step 5 → first real scan of my network: provider sees all my DNS lookups, SSH open on the router, UPnP on, 22 neighbour networks fighting for my channel. score 77/100 • step 6 → the AI agents. they read the scan and answer “what should I fix first?” or “is anything on my network suspicious?” before anything leaves my PC, Bastion strips MAC addresses, device names, Wi-Fi names and the last part of my IP watch mode re-checks the network every 5–60 min and only wakes the agent when something changed • step 7 → no API key. Bastion talks to Claude through Claude Code and to ChatGPT through Codex, using the login I already had • step 8 → a separate security agent attacked every line of it and found 11 holes. all fixed: the CLIs run with zero tools, read-only, in an empty folder. my question goes in through stdin, so nothing can be injected into a command. it refuses to start if Codex’s shell tool is on • step 9 → real bugs only real hardware shows: my Windows is in Russian, so Opus taught the parser Russian netsh labels. Windows 11 hides Wi-Fi info until you allow Location. Cloudflare rate-limited the speed test (HTTP 429), so Opus switched to fewer, bigger requests. next run: works • step 10 → before the repo went public, Opus checked that none of my IPs, MAC addresses or network names were in the code one evening. zero lines written by me. that’s it... agents suggest, you decide. Bastion never logs in to your router, never tries a password and never changes a setting on its own Find the GitHub repo and the full prompt below ↓ Then read the article on how to reverse engineer anything with Opus 5.5 ↓
    Descarcă
    Movez @0xMovez
    5943423111K
  12. freeCodeCamp.org✓@freeCodeCamp
    If you want to improve your beginner Python skills, try building something that gets data from the internet. That's what Sameer helps you do here. You'll build a weather app and learn about APIs, HTTP requests, error handling, and more.
    Descarcă
    43434516.2K
  13. Roro⁷🦊𐙚. ݁@heyst0bi1t
    🚨All the important votings going on currently: ● MAMA ● MMA ● AAA ● Kids’ Choice Awards ● ARIA Awards THE VOTING LINKS ARE ATTACHED BELOW:-
    92.3K3K28.3K
  14. Roro⁷🦊𐙚. ݁@heyst0bi1t
    @heyst0bi1t
    AAA - On Idolchamp App Category: POPULARITY AWARD: BTS
    135603.3K
  15. Roro⁷🦊𐙚. ݁@heyst0bi1t
    @heyst0bi1t
    ARIA AWARDS (Website) Category: MOST POPULAR INTERNATIONAL ARTIST: BTS
    337613.4K
  16. Cyber Security News✓@The_Cyber_News
    ‼️ PHP Releases New Windows Build Security Updates to Fix Critical HTTP2Shell Vulnerability Details: The PHP team has released updated Windows builds to fix a serious flaw known as HTTP2Shell. The new packages are PHP 8.5.12-1, 8.4.27-1, 8.3.36-1, and 8.2.35-1, and PHP announced them on October 26, 2026. Each build now includes Brotli 1.2.1, which fixes CVE-2026-111497. Windows users who run PHP should install these packages without delay. The flaw sits in Google’s Brotli library, a compression tool that many programs use to unpack data. It is an out-of-bounds write, which means the code writes data past the memory area it was meant to use. PHP’s own advisory explains how the flaw reaches PHP on Windows. The vulnerable decoder can be reached through the cURL extension when automatic HTTP response decompression is turned on. #CybersecurityNews
    Descarcă
    1311744736K
  17. ☣ KitPloit - Hacker Tools✓@KitPloit
    honeypot-data — Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt analyses.
    Descarcă
    05313K
  18. The Hacker News@TheHackersNews
    ‼️ PHP patches Windows builds AGAIN, just 5 days after the PHP2Shell fixes. This time, a Brotli flaw could allow code execution when cURL automatically decompresses crafted HTTP responses. Updated builds cover PHP 8.2–8.5. Full details:
    Descarcă
    1512552169.4K
  19. Abdelrhman Allam✓@sl4x0
    In this article, I break down how I built OSA, the architecture behind it, the tools I use, and the lessons I’ve learned along the way.
    136943915.2K
  20. Rıdvan Yağlı✓@ridvanyagli
    Node2Shell güvenlik açığını tespit etmek amacıyla Node.js HTTP uygulamalarını uzaktan test eden bir tarama aracı.
    10252.2K
  21. Foxymop@marcelatorresar
    ✅️ FIC REC ✅️ #Kanthonween You say Goodbye, I say Hello By ArtemisFreed Kate is a medium. Visited by her mother, her father and tonight a man who needs her to pass along a message to his son and perhaps nudge her towards romance. Art by @Tehremy_
    Descarcă
    Kanthony Crave 🦇🕸️ @KanthonyCrave
    It's Deathony Sunday! Let's explore Kate & Anthony’s love across time and the boundary between life & death 💀🪦 How would they react to the other dying? To flashbacks of past lives? To searching for each other in the afterlife? Share art, edits, and headcanons. #Kanthoween
    0323456
  22. Kanthony Crave 🦇🕸️@KanthonyCrave
    It's Deathony Sunday! Let's explore Kate & Anthony’s love across time and the boundary between life & death 💀🪦 How would they react to the other dying? To flashbacks of past lives? To searching for each other in the afterlife? Share art, edits, and headcanons. #Kanthoween
    Descarcă
    011462.9K
  23. Arată mai multe postări