Post con #https

#https

Post pubblici su X che usano #https.

Hashtag correlati

  1. pilvar (Philippe Dourassov)✓@pilvar222
    We made a website to check if your http client is vulnerable to CVE-2026-111497 (Node2Shell/HTTP2Shell) Also open-source: Some examples:
    Scarica
    5181068K
  2. ☣ KitPloit - Hacker Tools✓@KitPloit
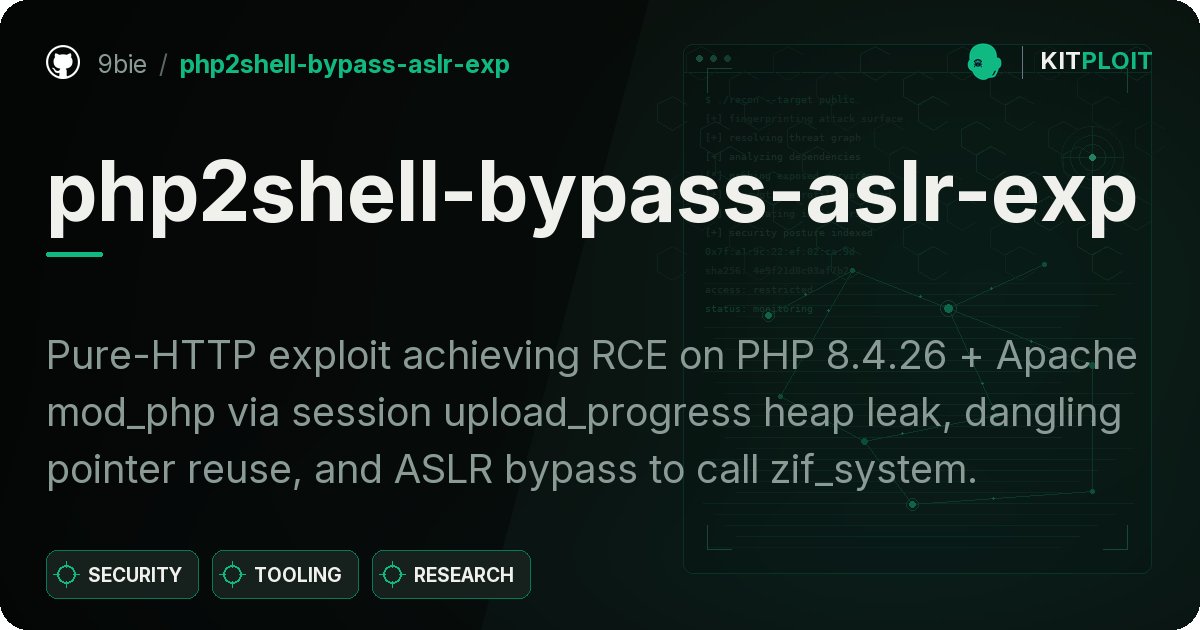
    php2shell-bypass-aslr-exp — Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call zif_system.
    Scarica
    18685.3K
  3. Ed✓@ed__marquez
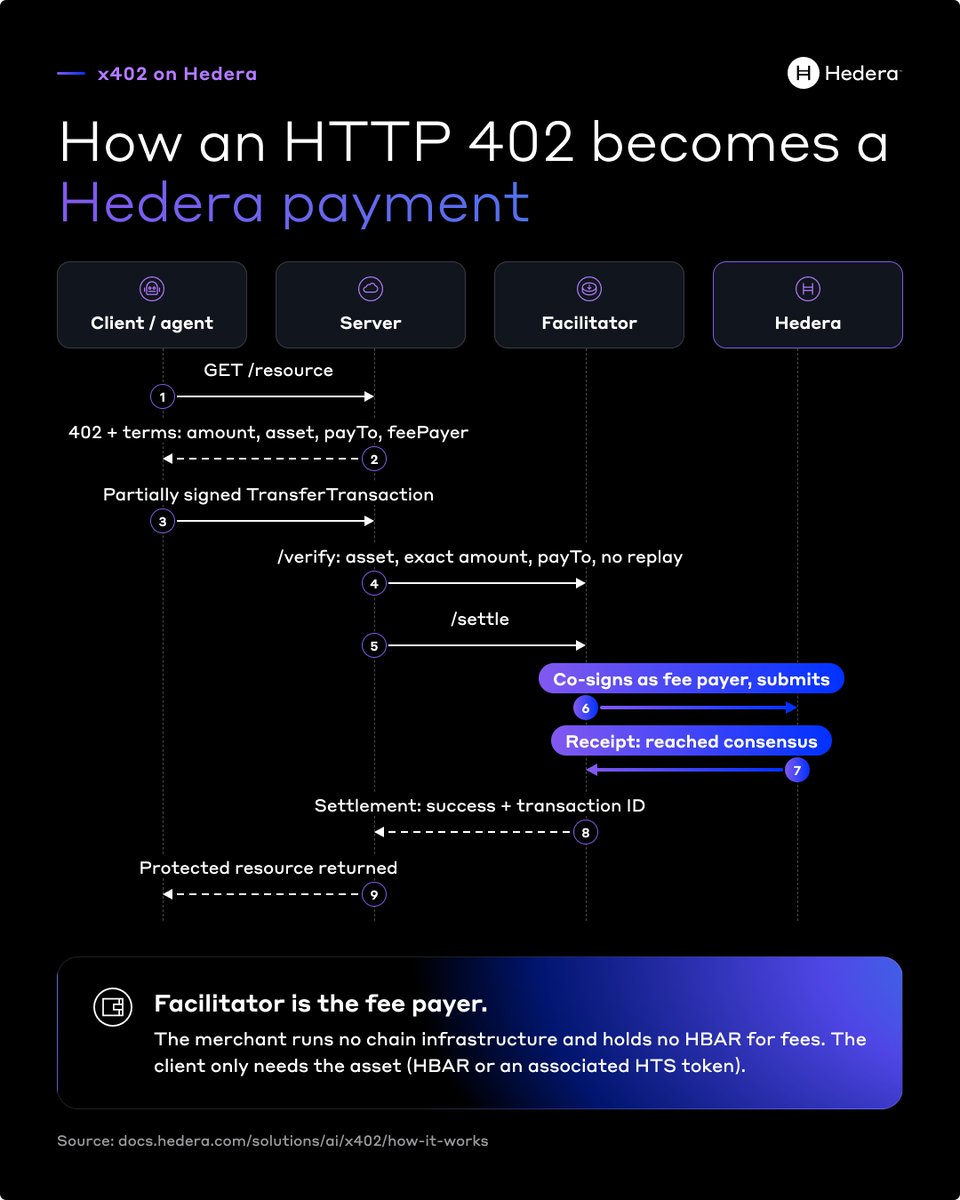
    1/ HTTP has a status code for payments that was never really used: 402 Payment Required x402 is an open standard that puts it to work A server asks for payment inside a normal request, and a client, like an AI agent, pays without a checkout page or an account... kinda genius
    Scarica
    417693.3K
  4. Sagar Giri@SagarGiri1707
    How HTTPS Actually Works: The Padlock, Explained (TLS 1.3) Every time the padlock appears, two machines that have never met agree on a secret in plain sight, in a fraction of a second. #HTTPS #TLS
    Scarica
    00017
  5. Sodi✓@sodi_trade
    rx402: private x402 payments for agents, on Sodi. rx402 lets an agent pay for an API with an HTTP 402 response and a stablecoin transfer. The catch: every payment comes from the agent’s wallet, so anyone can link every call it makes back to its owner. rx402 breaks that link. The owner deposits USDG into a privacy pool on Robinhood Chain, and an approval service screens deposits before they can be spent. The agent opens a session: a zero-knowledge proof that it owns funds in the pool, and a withdrawal of a small budget to a brand-new address. A relayer pays the gas, so nothing funds that address traceably. From there the agent pays x402 endpoints (data feeds, APIs, inference) like any other wallet, and rotates to a fresh address when the budget runs out. Merchants see an ordinary payment. Nobody can link a session to the owner, or to the next session. SDK (@sodi/rx402), MCP server and contracts, open source:
    Scarica
    193372K
  6. Bun@bunjavascript
    Bun v1.4.4 - Fixes 271 issues, addressing 544 👍 - `bun fmt` is a fast Prettier-compatible code formatter - `bun check` gets 1.4x - 7.8x faster - New in Bun.SQL & WebSocket - Security fixes, including for Brotli, TLS certs, HTTP/3, and more
    48761.3K91.4K
  7. Neplox✓@neploxaudit
    We found multiple ways to bypass the 402 paywalls 💸 :~$ "402 Payment Required" sat unused for 30-ish years - Now, the protocols reviving it let us skip the paying part; Here's how paywalls in TypeScript / Go / Java served paid content for free: [1] - x402 verify() checked the amount, the asset and the network; but not the recipient. What if we rewrite payTo in the console and payTo ourselves? 👀 [2] - MPP credential proved an invoice was paid, not what for. What if we pay 1 sat for /cheap, but spend it on the 100 sat /expensive? 👀 [3] - The middleware priced one path, the server served another; & here is just 1 example out of many: → GET HTTP/1.1 Host: app.example ← HTTP/1.1 200 OK { "served":"PREMIUM CONTENT" } <!-- READ MORE: "Breaking HTTP (pay)walls" --> 👉
    10142.1K
  8. Mark Maunder✓@mmaunder
    StealMyBitcoin is solved! This is the absolute best explanation you’ll see on how hard #php2shell is to exploit. The author had to trigger a precise memory corruption condition, leak internal memory addresses, bypass aslr, reverse engineer php’s internal memory structures, forge structures to hijack execution, and account for php build differences, worker behavior and timing to get RCE. 20 http requests with a 7 out of 10 success rate. What an amazingly successful CTF. Impressive the creator was able to keep the server up during all the attempts. With all the BS around it’s nice to see something concrete that moves the art forward.
    Mark Maunder @mmaunder
    Love this. The💰is still in the wallet. Finally we get some ground truth around how hard php2shell is to exploit. The amount of bullshit flying around from vendors capitalizing on the moment is staggering, And the alert fatigue they’re creating is really going to hurt when a mass exploitable RCE emerges. We still haven’t seen a production site hacked via #php2shell at Wordfence.
    341621.7K143K
  9. Mark Maunder✓@mmaunder
    Love this. The💰is still in the wallet. Finally we get some ground truth around how hard php2shell is to exploit. The amount of bullshit flying around from vendors capitalizing on the moment is staggering, And the alert fatigue they’re creating is really going to hurt when a mass exploitable RCE emerges. We still haven’t seen a production site hacked via #php2shell at Wordfence.
    1016202149K
  10. 0xMarioNawfal✓@RoundtableSpace
    10 GitHub repos to automate work, not just generate answers. Trading research, ad campaigns, email, browsing and video production:  1.⁠ ⁠AutoHedge An AI-agent framework for automated trading research and execution. ⁠ ⁠  2.⁠ ⁠Vibe-Trading Build your own AI trading agent. ⁠ ⁠  3.⁠ ⁠Claude Ads Audit and optimize ad campaigns with Claude Code. ⁠ ⁠  4.⁠ ⁠TopRank Automate SEO and Google Ads workflows. ⁠ ⁠  5.⁠ ⁠Fincept Terminal Financial research and market analytics in one terminal. ⁠ ⁠  6.⁠ ⁠Agentic Inbox Use AI agents to manage email workflows. ⁠ ⁠  7.⁠ ⁠ClawRouter Route context for AI agents. ⁠ ⁠  8.⁠ ⁠Camofox Browser A browser built for agent automation, with anti-detection features. ⁠ ⁠  9.⁠ ⁠Open Higgsfield AI An open-source interface for AI video generation. ⁠ ⁠ 10.⁠ ⁠HyperFrames Let your agent write HTML and render it into video. ⁠ ⁠ These automate workflows, not guarantee income. Hosting and model costs can still apply. Save this before building your next automation from scratch.
    2559149.2K
  11. Sebastian Steineke✓@SteinekeCDU
    Partei scheitert mit Klage: CDU-Politiker #Hagel darf Linke „Clan-Bürgermeisterin“ nennen
    168691.1K
  12. Dhiyaneshwaran@DhiyaneshDK
    Detect PHP-powered websites &amp; IPs using the updated php-detect nuclei template Link :
    Scarica
    Florian Roth ⚡️ @cyb3rops
    Okay, since the news is already out: an RCE vulnerability in PHP core, CVSS 10.0. Further details are scheduled for release on October 20. Only PHP 8 will receive patches.
    65038036.5K
  13. Florian Roth ⚡️✓@cyb3rops
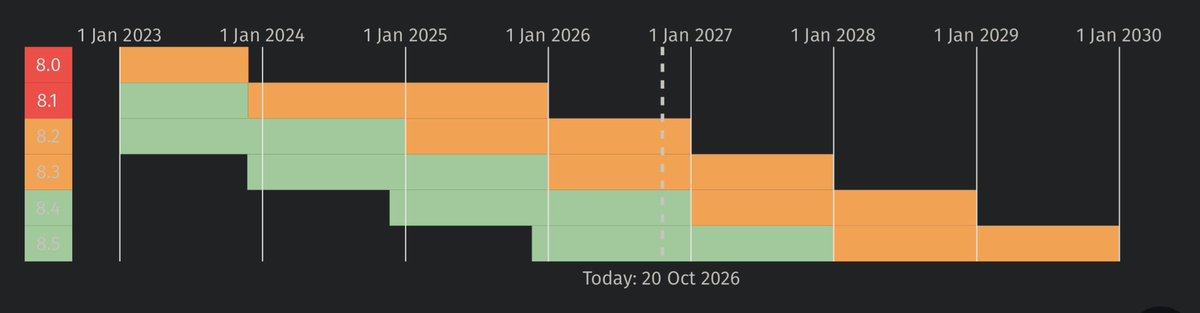
    Okay, since the news is already out: an RCE vulnerability in PHP core, CVSS 10.0. Further details are scheduled for release on October 20. Only PHP 8 will receive patches.
    Scarica
    363201.4K478K
  14. Juan Sebastián Henao✓@juanhenaoparra
    just open sourced a gateway for herdr: an HTTP API + task queue for running coding agents on your own VPS. i’m a big herdr fan, and wanted to automate coding tasks from apps, scripts, or other agents, not just from my terminal. send a repo + prompt, and it: - queues the task - creates a dedicated git worktree + branch - opens a herdr tab and starts claude code or pi - reports progress through polling or webhooks you can send follow ups to the same agent with its context intact, or jump into its terminal and take over. use it to trigger bug fixes from your app, investigate failing tests from CI, or let one agent delegate coding work to another. how i built it: a small node.js + express service wrapping the herdr CLI. FIFO queue with configurable concurrency, state persisted to disk, and automatic cleanup of old sessions and worktrees. no redis or database required. herdr handles the terminals and agents. the gateway makes them accessible over HTTP.
    14321367
  15. shubs✓@infosec_au
    You can now perform content discovery at 100k requests per second with h3fuzz on http/3 hosts (fork of ffuf with http/3 support). Tool here: Research post here:
    Scarica
    1010651122.2K
  16. The Hacker News@TheHackersNews
    ‼️ PHP patches Windows builds AGAIN, just 5 days after the PHP2Shell fixes. This time, a Brotli flaw could allow code execution when cURL automatically decompresses crafted HTTP responses. Updated builds cover PHP 8.2–8.5. Full details:
    Scarica
    1612351062.8K
  17. ESET España@ESET_ES
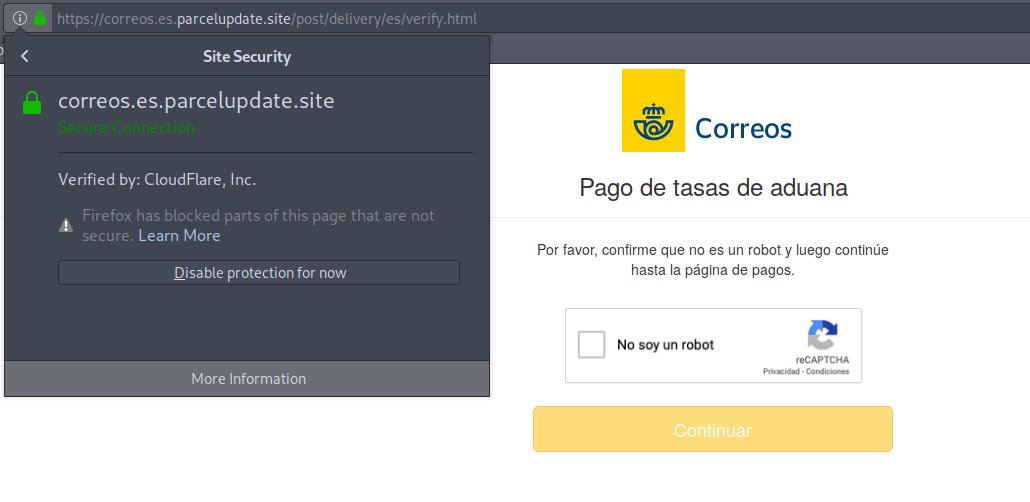
    Si recibes un SMS supuestamente de @Correos avisándote de la recepción de un paquete junto con un enlace acortado, desconfía. Se trata de un nuevo caso de #Phishing que te redirige a una web fraudulenta (por mucho que utilice #HTTPS)
    Scarica
    49250
  18. portbuster@portbuster1337
    Enter NetSnitch. a channel for harvesting live credentials and session cookies on Windows engagements. It drives HTTP Debugger's headless capture engine from PowerShell Article: Repo:
    214493.1K
  19. Assetnote✓@assetnote
    Our research team has released h3fuzz: a fork of ffuf with HTTP/3 support and a web UI for content discovery, based on PortSwigger's Turbo Intruder research. It reaches 120k requests per second on local benchmarks, and we cover why that rarely holds up against real targets. You can read more here: Repository:
    Scarica
    34216510.6K
  20. Mostra altri post