#https içeren gönderiler

#https

X'te #https kullanan herkese açık gönderiler.

İlgili etiketler

  1. pilvar (Philippe Dourassov)✓@pilvar222
    We made a website to check if your http client is vulnerable to CVE-2026-111497 (Node2Shell/HTTP2Shell) Also open-source: Some examples:
    İndir
    63120616.5K
  2. Cruz✓@ViC305
    🚨 𝗛𝗘𝗥𝗠𝗘𝗦 𝗠𝗢𝗕𝗜𝗟𝗘 𝗕𝗘𝗧𝗔 — 𝗦𝗘𝗟𝗙-𝗛𝗢𝗦𝗧𝗘𝗗 𝗦𝗘𝗧𝗨𝗣 𝗚𝗨𝗜𝗗𝗘! 📱🔥 I've spent over a DECADE in systems engineering, and somehow getting the new Hermes Mobile Beta connected to my own self-hosted @NousResearch Hermes Agent still gave me a little trouble! 😂 So here's a quick guide to save everyone else the headache! ━━━━━━━━━━━━━━━━━━━━ 🖥️ 𝗦𝗧𝗘𝗣 𝟭 — 𝗦𝗧𝗔𝗥𝗧 𝗧𝗛𝗘 𝗗𝗔𝗦𝗛𝗕𝗢𝗔𝗥𝗗 On the machine running Hermes: hermes dashboard --host 0.0.0.0 --port 9119 --no-open On first interactive setup, Hermes can prompt you to create a username and password. SAVE THOSE! 🔒 𝗣𝗥𝗘𝗙𝗘𝗥 𝗧𝗔𝗜𝗟𝗦𝗖𝗔𝗟𝗘? (Recommended) Bind directly to your machine's Tailscale IP instead: hermes dashboard --host 100.x.x.x --port 9119 --no-open ━━━━━━━━━━━━━━━━━━━━ 📱 𝗦𝗧𝗘𝗣 𝟮 — 𝗚𝗥𝗔𝗕 𝗧𝗛𝗘 𝗕𝗘𝗧𝗔 ⚙️ 𝗦𝗧𝗘𝗣 𝟯 — 𝗦𝗘𝗟𝗘𝗖𝗧 𝗦𝗘𝗟𝗙-𝗛𝗢𝗦𝗧𝗘𝗗 NOT Nous Portal! You're connecting to your OWN Hermes instance. 🌐 𝗦𝗧𝗘𝗣 𝟰 — 𝗘𝗡𝗧𝗘𝗥 𝗬𝗢𝗨𝗥 𝗚𝗔𝗧𝗘𝗪𝗔𝗬 𝗨𝗥𝗟 🏠 Home Wi-Fi: http://192.168.x.x:9119 🔐 Tailscale: http://100.x.x.x:9119 Replace the example IP with your Hermes machine's actual address. 🔑 𝗦𝗧𝗘𝗣 𝟱 — 𝗘𝗡𝗧𝗘𝗥 𝗬𝗢𝗨𝗥 𝗖𝗥𝗘𝗗𝗘𝗡𝗧𝗜𝗔𝗟𝗦 Use the dashboard username and password you configured earlier. ✅ 𝗦𝗧𝗘𝗣 𝟲 — 𝗧𝗔𝗣 𝗖𝗢𝗡𝗡𝗘𝗖𝗧! That's it. Your self-hosted Hermes Agent, accessible from your phone! 🙌 ━━━━━━━━━━━━━━━━━━━━ 💡 𝗧𝗪𝗢 𝗜𝗠𝗣𝗢𝗥𝗧𝗔𝗡𝗧 𝗧𝗜𝗣𝗦: • Your phone must be on the same reachable network or connected through Tailscale. • Never expose port 9119 directly to the public internet with basic password authentication. I recommend Tailscale! Hopefully this saves someone else the troubleshooting session I went through! 😂 Enjoy Hermes Mobile! 📱💚 This thing packs a punch and even connects to your Hermes desktop sessions, something I’ve been in DESPERATE need of!! 🔥
    İndir
    211115512.6K
  3. The Hacker✓@theprocracker
    Why cleartext HTTP is a security nightmare 🕵️‍♂️🔒 Quick tutorial at how network protocols handle data if it isn’t encrypted with SSL/TLS • 127.0.0.1 •
    İndir
    2171214.4K
  4. D3 Bytes✓@D3bytes
    4213447
  5. MSR🌶🍫@monikafilefan
    well guess this is a good time to reshare some of my fave fics that aren’t on ao3 in case y’all are already slowly suffering withdrawals and need that fic fix
    5141715K
  6. GGSec@GGASecDe
    Closing out #php2shell: a universal black-box PoC for PHP's session upload-progress bug. One pure-HTTP chain - arm the allocator, spray fake refs, leak the heap, beat ASLR, turn a destructor into system(). Verified blind on Debian 13 PHP 8.4.24, x86-64 + arm64: RCE as www-data.
    İndir
    37505.9K
  7. http@http_yap
    ハッピ~ハロウィンらくがき
    İndir
    0697227.8K
  8. Grant Benson@GrantBenson08
    MORE FILM - yards and TDs = passing + rushing Week 3 - 315 yards 4 TDs Week 4 - 362 yards 3 TDs ( c/o 2026 6'4 205 dual threat QB + full eligibility )
    İndir
    1722972
  9. etugen.io✓@etugenio
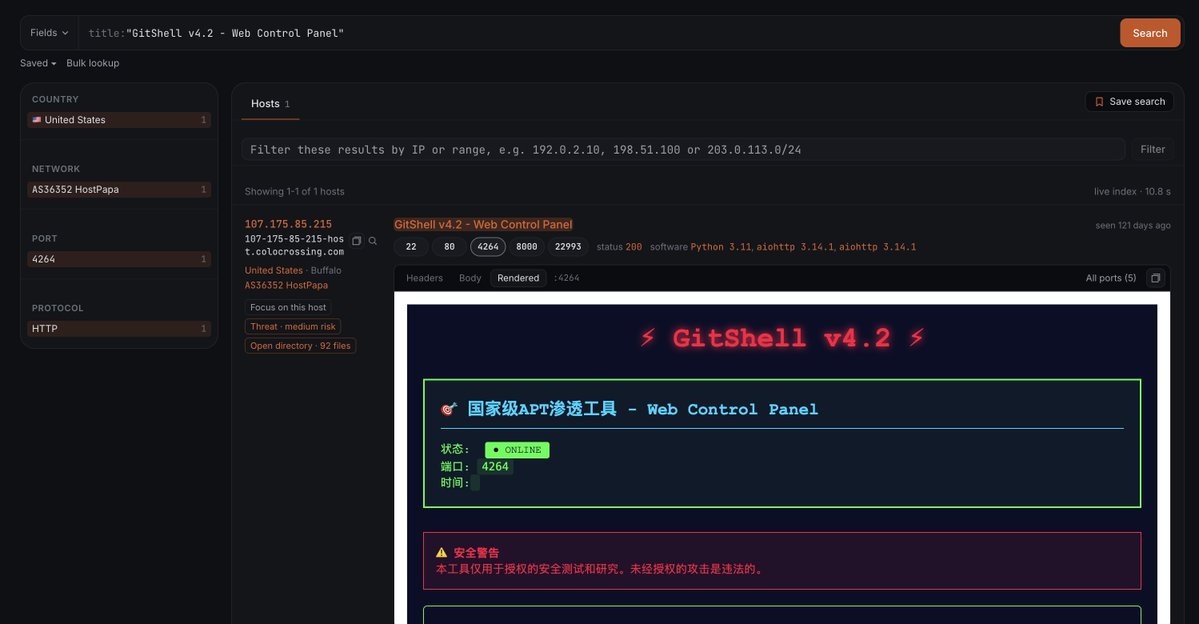
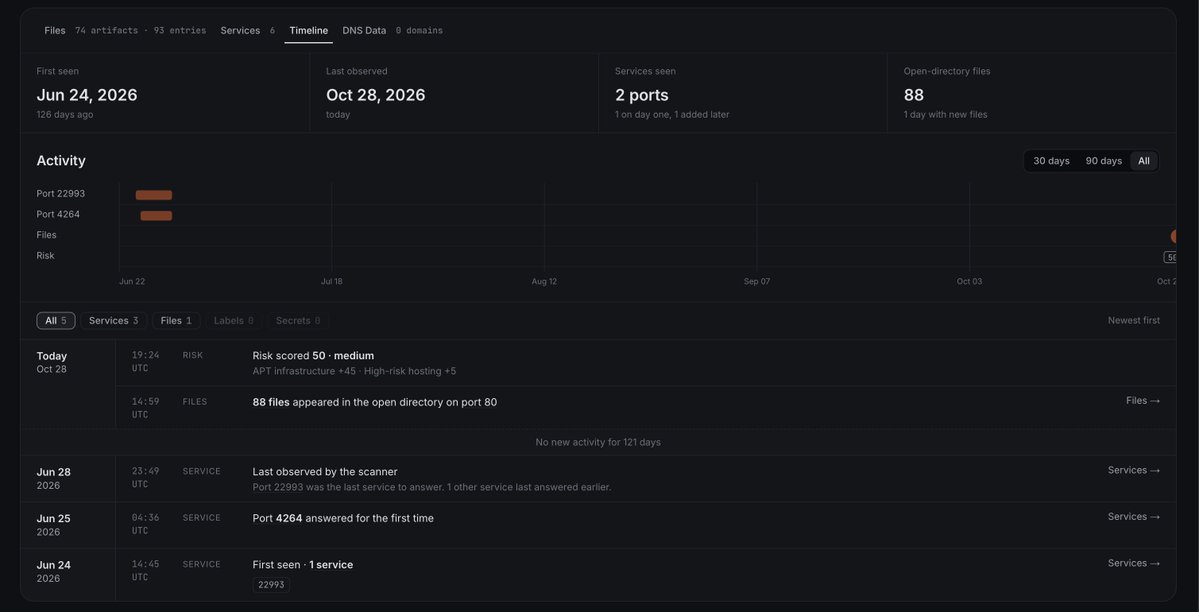
    Apt Team 107[.]175.85.215 "GitShell v4.2 - Web Control Panel" - Webshell management. - HTTP/SOCKS proxy validation. - Attack-task orchestration. Platform: #apt #aptteam #malware #exploit #etugen
    İndir
    05181.5K
  10. ☣ KitPloit - Hacker Tools✓@KitPloit
    wafmeow — wafw00f's fingerprints. Go speed. Pipeline-native. WAF detection from live HTTP and offline captures.
    İndir
    017812
  11. GeekNews✓@GeekNewsHada
    HTTP2Shell - Node․js에서 Python까지, Brotli 의존성으로 퍼진 원격 코드 실행 취약점 공격자가 조작한 Brotli 압축 데이터를 해제하면 메모리 유출, 프로세스 충돌, 원격 코드 실행으로 이어질 수 있음. 서버로 들어오는 요청뿐 아니라 외부 서버에서 받아 오는 응답도 공격 경로가 됨 Python에서는 다른 패키지를 통해 설치된 Brotli를 HTTP 클라이언트가 자동 사용하므로, 코드에서 직접 불러오지 않았어도 영향받을 수 있음 Brotli 1.2.1 또는 brotlicffi 1.2.1.0 이상으로 업데이트하고, 이를 포함한 컨테이너와 애플리케이션도 다시 빌드해 배포 필요. 요청의 Accept-Encoding: br만 제거하는 것으로는 방어가 충분하지 않음
    014394.3K
  12. Juan Sebastián Henao✓@juanhenaoparra
    just open sourced a gateway for herdr: an HTTP API + task queue for running coding agents on your own VPS. i’m a big herdr fan, and wanted to automate coding tasks from apps, scripts, or other agents, not just from my terminal. send a repo + prompt, and it: - queues the task - creates a dedicated git worktree + branch - opens a herdr tab and starts claude code or pi - reports progress through polling or webhooks you can send follow ups to the same agent with its context intact, or jump into its terminal and take over. use it to trigger bug fixes from your app, investigate failing tests from CI, or let one agent delegate coding work to another. how i built it: a small node.js + express service wrapping the herdr CLI. FIFO queue with configurable concurrency, state persisted to disk, and automatic cleanup of old sessions and worktrees. no redis or database required. herdr handles the terminals and agents. the gateway makes them accessible over HTTP.
    14321436
  13. abraxas✓@abraxas_null
    On this Halloween, I am humbled. I've just been accredited 57 brand new CVEs! Thank you to all my friends and lovers! CVE-2026-119146   proftpd/proftpd: ProFTPD before 1.3.9e and 1.3.10rc5 Buffer Overflow via mod_rewrite utf8trans RewriteMap   Affected: ProFTPD < 1.3.9e; >= 1.3.10rc1, < 1.3.10rc5   CVE-2026-119147   proftpd/proftpd: ProFTPD before 1.3.9e and 1.3.10rc5 mod_sftp Copy-File Authorization Bypass   Affected: ProFTPD < 1.3.9e; >= 1.3.10rc1, < 1.3.10rc5   CVE-2026-119364   proftpd/proftpd: ProFTPD through 1.3.9e and 1.3.10rc4 mod_copy Symlink Following Write Bypass   Affected: ProFTPD <= 1.3.9e; >= 1.3.10rc1, < 1.3.10rc5   CVE-2026-119371   sqlite/sqlite: SQLite before 3.54.0 Stack Exhaustion via CTE Chain in selectExpander()   Affected: SQLite < 3.54.0   CVE-2026-119372   sqlite/sqlite: SQLite before 3.54.0 Use-After-Free in FTS3 fts3BestSnippet() via snippet()   Affected: SQLite < 3.54.0   CVE-2026-119373   sqlite/sqlite: SQLite before 3.54.0 FTS5 Heap Buffer Overflow via fts5MergeRowidLists()   Affected: SQLite < 3.54.0   CVE-2026-119374   sqlite/sqlite: SQLite before 3.54.0 Heap Buffer Overflow via FTS5 fts5DoSecureDelete()   Affected: SQLite < 3.54.0   CVE-2026-119375   sqlite/sqlite: SQLite before 3.54.0 Information Disclosure via WAL Page Size Mismatch   Affected: SQLite < 3.54.0   CVE-2026-119376   sqlite/sqlite: SQLite before 3.54.0 Stack Exhaustion via COLLATE Operator Chain   Affected: SQLite < 3.54.0   CVE-2026-119377   sqlite/sqlite: SQLite before 3.54.0 Authorizer Bypass via RIGHT or FULL JOIN USING   Affected: SQLite < 3.54.0   CVE-2026-119378   sqlite/sqlite: SQLite before 3.54.0 Use-After-Free in R-Tree nodeWrite()   Affected: SQLite < 3.54.0   CVE-2026-119379   sqlite/sqlite: SQLite before 3.54.0 Heap Buffer Overflow via Session Extension sessionUpdateFind()   Affected: SQLite < 3.54.0   CVE-2026-119591   sqlite/sqlite: SQLite before 3.54.0 Stack Exhaustion via countOfViewOptimization() in VALUES Clause   Affected: SQLite < 3.54.0   CVE-2026-119407   element-hq/element-web: Element Web and Element Desktop before 1.12.32 Forced Logout via Guest Credential URL Parameters   Affected: Element Web < 1.12.32; Element Desktop < 1.12.32   CVE-2026-119408   n8n-io/n8n: n8n before 2.42.6, 2.43.3 and 3.0.1 Code Execution Outside Task Runner Isolation via Deprecated Function Nodes   Affected: n8n < 2.42.6; >= 2.43.0, < 2.43.3; >= 3.0.0, < 3.0.1   CVE-2026-119409   opnsense/core: OPNsense before 26.7.8 Root Command Injection via Firmware Mirror Setting   Affected: OPNsense < 26.7.8   CVE-2026-119414   bitwarden/server: Bitwarden Server before 2026.10.1 Authorization Bypass via POST /api/ciphers/create   Affected: Bitwarden Server < 2026.10.1   CVE-2026-119415   cakephp/cakephp: CakePHP through 5.4.3 MIME Header Injection via FormDataPart Content-Type   Affected: CakePHP <= 5.4.3   CVE-2026-119416   cakephp/cakephp: CakePHP through 5.4.3 Cookie Leakage via HTTP Client CookieCollection Domain Matching   Affected: CakePHP <= 5.4.3   CVE-2026-119417   cakephp/cakephp: CakePHP through 5.4.3 Email Header Injection via Bare CR/LF in SmtpTransport and MailTransport   Affected: CakePHP 4.5.12, 4.6.5, 5.1.8 to 5.1.10, 5.2.14 to 5.2.15, 5.3.7, 5.4.0 to 5.4.3   CVE-2026-119418   cakephp/cakephp: CakePHP through 5.4.3 SQL Injection via WindowExpression range() and frame()   Affected: CakePHP <= 5.4.3   CVE-2026-119419   cakephp/cakephp: CakePHP through 5.4.3 SQL Injection via StringExpression and IdentifierExpression Collation   Affected: CakePHP <= 5.4.3   CVE-2026-119420   getlago/lago-api: Lago through 1.55.0 Authentication Bypass via acceptInvite GraphQL Mutation   Affected: Lago <= 1.55.0   CVE-2026-119421   juspay/hyperswitch: Hyperswitch through 1.128.0 Missing Authorization in Payout Confirmation   Affected: Hyperswitch <= 1.128.0; date-tagged builds < 2026.10.19.0   CVE-2026-119422   juspay/hyperswitch: Hyperswitch before 1.128.0 Webhook Authentication Bypass via Worldpayxml Connector   Affected: Hyperswitch < 1.128.0; date-tagged builds < 2026.10.01.0   CVE-2026-119423   opnsense/core: OPNsense core before 26.7.8 Lockout IP Planting via WebGUI Login Username   Affected: OPNsense < 26.7.8   CVE-2026-119424   opnsense/core: OPNsense before 26.7.8 Wireless WPA Configuration Line Injection via Identity   Affected: OPNsense < 26.7.8   CVE-2026-119425   opnsense/core: OPNsense 26.1.6 through 26.7.7 Captive Portal Session Takeover via Forged ARP   Affected: OPNsense >= 26.1.6, <= 26.7.7   CVE-2026-119426   phpmyadmin/phpmyadmin: phpMyAdmin through 5.2.3 CSRF Token Bypass via Non-AJAX POST to /sql   Affected: phpMyAdmin <= 5.2.3   CVE-2026-119427   phpmyadmin/phpmyadmin: phpMyAdmin through 5.2.3 SQL Injection via Designer saveSetting   Affected: phpMyAdmin <= 5.2.3   CVE-2026-119428   phpmyadmin/phpmyadmin: phpMyAdmin through 5.2.3 SSRF via setup/validate.php After Setup Disabled   Affected: phpMyAdmin <= 5.2.3   CVE-2026-119429   phpmyadmin/phpmyadmin: phpMyAdmin through 5.2.3 Two-Factor Authentication Removal via /config/set   Affected: phpMyAdmin <= 5.2.3   CVE-2026-119545   forgejo/forgejo: Forgejo through 15.0.11, 16.0.7, and 17.0.1 SSRF via OpenID Discovery   Affected: Forgejo <= 15.0.11; >= 16.0.0, <= 16.0.7; >= 17.0.0, <= 17.0.1   CVE-2026-119546   forgejo/forgejo: Forgejo through 15.0.11, 16.0.7, and 17.0.1 Path Traversal via restore-repo   Affected: Forgejo <= 15.0.11; >= 16.0.0, <= 16.0.7; >= 17.0.0, <= 17.0.1   CVE-2026-119547   forgejo/forgejo: Forgejo through 15.0.11, 16.0.7, and 17.0.1 Information Disclosure via /api/v1/user/keys/{id}   Affected: Forgejo <= 15.0.11; >= 16.0.0, <= 16.0.7; >= 17.0.0, <= 17.0.1   CVE-2026-119548   getlago/lago-api: Lago through 1.55.0 Cross-Organization Invoice Payment Manipulation via Stripe Webhook   Affected: Lago <= 1.55.0   CVE-2026-119549   jellyfin/jellyfin: Jellyfin through 12.4 SSRF via Gzip-Compressed Data URI in SVG Profile Images   Affected: Jellyfin <= 12.4   CVE-2026-119550   jellyfin/jellyfin: Jellyfin through 12.4 Information Disclosure via GET /Playlists/{playlistId}   Affected: Jellyfin <= 12.4   CVE-2026-119551   jellyfin/jellyfin: Jellyfin through 12.4 Authorization Bypass via GET /Items/Suggestions   Affected: Jellyfin <= 12.4   CVE-2026-119552   louislam/uptime-kuma: Uptime Kuma through 2.5.8 Race Condition Admin Creation via Setup Handler   Affected: Uptime Kuma <= 2.5.8   CVE-2026-119553   moodle/moodle: Moodle through 5.3.0, 5.2.4, 5.1.8, 5.0.11 and 4.5.15 Blackboard Import Path Traversal   Affected: Moodle 5.3.0; >= 5.2.0, <= 5.2.4; >= 5.1.0, <= 5.1.8; >= 5.0.0, <= 5.0.11; <= 4.5.15   CVE-2026-119554   moodle/moodle: Moodle through 5.3.0, 5.2.4, 5.1.8, 5.0.11 and 4.5.15 SQL Injection via enrol_database Course idnumber   Affected: Moodle 5.3.0; >= 5.2.0, <= 5.2.4; >= 5.1.0, <= 5.1.8; >= 5.0.0, <= 5.0.11; <= 4.5.15   CVE-2026-119555   moodle/moodle: Moodle through 5.3.0, 5.2.4, 5.1.8, 5.0.11 and 4.5.15 Information Disclosure via core_grades_get_feedback   Affected: Moodle 5.3.0; >= 5.2.0, <= 5.2.4; >= 5.1.0, <= 5.1.8; >= 5.0.0, <= 5.0.11; >= 4.2.0, <= 4.5.15   CVE-2026-119556   moodle/moodle: Moodle through 5.3.0, 5.2.4, 5.1.8, 5.0.11 and 4.5.15 Missing Authorization via core_grades_get_gradeitems   Affected: Moodle 5.3.0; >= 5.2.0, <= 5.2.4; >= 5.1.0, <= 5.1.8; >= 5.0.0, <= 5.0.11; >= 4.2.0, <= 4.5.15   CVE-2026-119557   n8n-io/n8n: n8n from 2.14.0 through 2.46.3 Path Traversal via Databricks Node   Affected: n8n >= 2.14.0, <= 2.46.3   CVE-2026-119558   opencart/opencart: OpenCart through 4.1.0.4 Payment Bypass via Free Checkout Reward Points   Affected: OpenCart <= 4.1.0.4   CVE-2026-119559   litespeedtech/openlitespeed: OpenLiteSpeed through 1.9.4 mTLS Bypass via HTTP/3 SNI and Host Mismatch   Affected: OpenLiteSpeed <= 1.9.4   CVE-2026-119560   opnsense/core: OPNsense core through 26.7.8 NTP Configuration Injection via GPS and PPS Fudge Fields   Affected: OPNsense <= 26.7.8   CVE-2026-119561   phpmyadmin/phpmyadmin: phpMyAdmin through 5.2.3 WebAuthn Two-Factor Authentication Bypass via CustomServer   Affected: phpMyAdmin <= 5.2.3   CVE-2026-119562   phpmyadmin/phpmyadmin: phpMyAdmin through 5.2.3 SQL Injection via Central Columns col_extra and col_attribute   Affected: phpMyAdmin <= 5.2.3   CVE-2026-119563   phpmyadmin/phpmyadmin: phpMyAdmin through 5.2.3 Stored XSS via Designer Query History Table Name   Affected: phpMyAdmin <= 5.2.3   CVE-2026-119564   plausible/analytics: Plausible Analytics through 3.2.1 Site Takeover via Exposed Invitation IDs   Affected: Plausible Analytics <= 3.2.1   CVE-2026-119565   plausible/analytics: Plausible Analytics through 3.2.1 Mass Assignment via Traffic Change Notification Update   Affected: Plausible Analytics <= 3.2.1   CVE-2026-119566   prometheus/prometheus: Prometheus through 3.15.1 Credential Leak via remote_write Cross-Host Redirects   Affected: Prometheus <= 3.15.1   CVE-2026-119567   vsftpd: vsftpd through 3.0.5 cmds_denied Bypass via RFC 775 Command Aliases   Affected: vsftpd <= 3.0.5   CVE-2026-119568   vsftpd: vsftpd through 3.0.5 require_ssl_reuse Bypass via FTPS Data Channel Hijacking   Affected: vsftpd <= 3.0.5   CVE-2026-119586   sqlite/sqlite: SQLite CLI through 3.54.1 Command Injection via .recover Output   Affected: SQLite <= 3.54.1
    İndir
    51201.8K
  14. Luca Shaffer✓@lucabuildsx
    IF YOU USE REA, SAVE THIS REVERSE-ENGINEERING WORKBENCH: 20 REPOS, 5 JOBS. “What does this app actually do?” needs different tools depending on whether you're looking at an APK, a native binary, a .NET assembly or a network capture. I grouped 20 repository links into five tool families. Keep the map beside the REA course and choose the part your investigation needs. 01 / AGENT + NATIVE ANALYSIS REA — agent-facing analysis workflows and evidence. Ghidra — a software reverse-engineering framework. GhidraMCP — an MCP bridge for Ghidra. ida-pro-mcp — connect an existing IDA Pro setup to an agent; IDA needs its own license. 02 / ANDROID + .NET jadx — DEX-to-Java decompilation. Apktool — Android resources and APK packaging. ILSpy — inspect and decompile .NET assemblies. dnSpyEx — .NET debugging and assembly editing. 03 / OBSERVE RUNTIME BEHAVIOR Frida — dynamic instrumentation for an authorized target. x64dbg — Windows user-mode debugging. RAD Debugger — native graphical debugging. mitmproxy — inspect HTTP traffic in a controlled test setup. 04 / THE BINARY WORKBENCH radare2 — command-line reverse-engineering tools. Rizin — a binary-analysis framework. Cutter — a graphical interface powered by Rizin. ImHex — inspect bytes and structured binary data. 05 / STRUCTURE + EVIDENCE angr — symbolic execution and binary analysis. capa — identify executable capabilities with rules. LIEF — parse and inspect executable formats programmatically. Wireshark — packet analysis; this GitHub repo mirrors the upstream project. The useful starting point is one target and one question: follow an export, explain a file format, compare a changed feature or test a reconstruction. Pick the tool for that question. Record the evidence. Turn observed behavior into a spec. Check your implementation against it. These are documentation-checked options, not a claim that all twenty integrate with REA or were benchmarked together. Model access, providers and commercial dependencies have their own requirements. Use software you're allowed to inspect. A decompiler doesn't grant access to a private backend or permission to bypass a paid feature. The quoted REA course covers the setup. This map helps you choose the next tool instead of installing the whole workshop.
    İndir
    codila @0xCodila
    REA is most dangerous thing on the internet right now... It lets your AI agent reverse engineer any app, down to the binary If you use it correctly, you can rebuild any feature you pay for, for FREE In this article, I show you how:
    16226547
  15. codila✓@0xCodila
    REA is most dangerous thing on the internet right now... It lets your AI agent reverse engineer any app, down to the binary If you use it correctly, you can rebuild any feature you pay for, for FREE In this article, I show you how:
    2697885.7K4.3M
  16. HKEPC✓@hkepcmedia
    【DLLM 🤬】昨日,有開發者公開挑釁全球黑白帽,稱「PHP2SHELL」漏洞根本沒那麼嚴重,更特意架設名為「Steal my Bitcoin」的資安挑戰網站,將存有約 0.025 枚比特幣(價值逾 2,017 美元)的加密錢包私鑰置於伺服器中,公開向全球黑客與資安研究人員叫陣,成功滲透並取得私鑰者即可全數奪走賞金。結果,很多高手研究過後都沒找到缺口,原來「DKLM 一開始根本沒放任何一個 PHP 檔案」,直至過了 15 小時後才補上了兩個 PHP 檔案,因此實際入侵其實僅花了 3 小時而已。 大家知道嗎?HKEPC 看到這個「Steal my Bitcoin」網站,為了寫篇新報道所以親自去查看了一下網站設定。雖然 HTTP 回應標頭(Response Headers)中顯示了 Server: nginx 以及 X-Powered-By: PHP/8.4.26,但背後卻只有一個 index.html 檔案,根本不存在可供參賽者觸發漏洞並利用的動態後端邏輯。怎料今早起床,就發現網站已經被攻破了。 起初還想說果然天外有天,沒有一個 PHP 檔案也能攻得入,實在太可怕了吧。要知道,PHP 伺服器在單純處理靜態檔案(如 HTML)時,並不會進入執行週期的 php_request_startup(),相關的記憶體解析機制(Zend executor / session / multipart parser)根本未初始化,因此當時的環境完全無法觸發該 CVE。 而且,其他研究員也揭發該主機是用 Nginx 反向代理至 PHP 單執行緒的內建開發伺服器(CLI server),並帶有 Nginx 預設的 1MB 請求限制,引來大量批評,認為這不是真實的 PHP 應用環境,既沒執行實際的 PHP 程式碼,亦非採用常見的 PHP-FPM / mod_php 架構。 著名安全研究員 LiveOverflow 亦出來踢爆,其實「Steal my Bitcoin」網站起初純粹只在傳送 index.html,從未觸發 PHP 易受攻擊的程式碼路徑。「KillaBoi」入侵後查看日誌,發現該網站是後來才追加 PHP 檔案進去。 隨後,「Steal my Bitcoin」的開發者也在 Hacker News 自行確認:在當天約 13:00 UTC 之前,伺服器純粹是用 PHP 的內建伺服器(CLI dev server)單純傳送靜態 HTML,之後為了平息質疑才補上了 /php-version.php 與 /ping.php。 更好笑的是,「Steal my Bitcoin」連放在伺服器內的錢包密鑰也是錯的,根本推算不出網站展示的獎金地址。事後開發者公開表示是自己放錯了,但由於「KillaBoi」確實成功讀取了伺服器上的「錢包密鑰」,最終開發者仍親自把 Bitcoin 轉給對方。 因此,這場鬧劇根本就沒有維持 19.28 小時,實際只需 3 小時就被攻破了。
    İndir
    52575K
  17. Alexween 🦇@disenchnted_
    http:// Happy Halloween .net ⠀ ̶̸̸ ━─ welcome back, Patrick Bateman... 𝄒𝄒
    İndir
    3137546
  18. Daha fazla gönderi göster