Tip: Stop setting RHOSTS for each of your modules and instead set it globally with 'setg RHOSTS x.x.x.x'. Use the 'tips' command in #Metasploit for more suggestions.
🔍 TCP Port Scanning with Metasploit
A quick look at how Metasploit helps researchers identify open TCP ports in an authorized lab environment. 🖥️🔐
🛡️ Authorized testing only.
#CyberSecurity#Metasploit#PortScanning#NetworkSecurity
Pentest-Cheat-Sheets
A collection of snippets of codes and commands to help our lives! The main purpose is not be a crutch, this is a way to do not waste our precious time! This repo also helps who trying to get OSCP. You'll find many ways to do something without #Metasploit Framework.
#infosec#pentesting#redteam
PoC to takeover Android using another Android by exploiting critical Bluetooth vulnerability to install #Metasploit payload without proper Bluetooth pairing (CVE-2023-45866)
It still affects Android 10 and bellow
#NetHunter
New write-up 🛡️
Metasploit: Scanning and Exploitation (TryHackMe)
Full offensive loop on a 2-host network:
→ EternalBlue (MS17-010) = SYSTEM on Windows
→ vsftpd 2.3.4 backdoor = root on Linux
Plus the payload & scan gotchas the room skips.
Read it here 👇
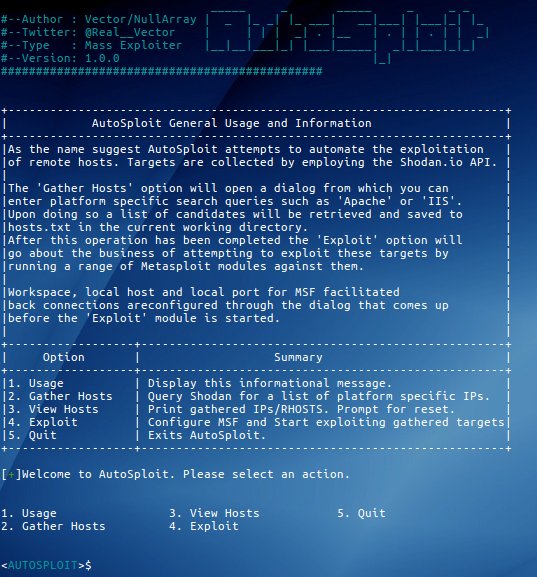
AutoSploit: Automated Mass Exploiter via @Real__Vector
It gathers targets via Shodan and automatically invokes selected #Metasploit modules to facilitate RCE attacks.
Wohooo! Kali Linux 2019.1 Released — Latest Version of Operating System for Hackers and #Cybersecurity Professionals.
The First 2019 version of Kali includes kernel up to version 4.19.13, various patches, and software updates like #Metasploit 5.0.
#KaliLinux & #Metasploit Tip:
You can now use "pattern_create.rb" & "pattern_offset.rb" without changing directories by doing "msf-pattern_create" / "msf-pattern_offset!
BONUS: "msf-<tab><tab>" for even more useful msf tools ;)