ActiveState✓

@ActiveState

ActiveState enables DevOps, InfoSec, and Development teams to improve their security posture while simultaneously increasing productivity and innovation.

1.6K Following4K Followers14.7K Posts
  1. ActiveState✓@ActiveState
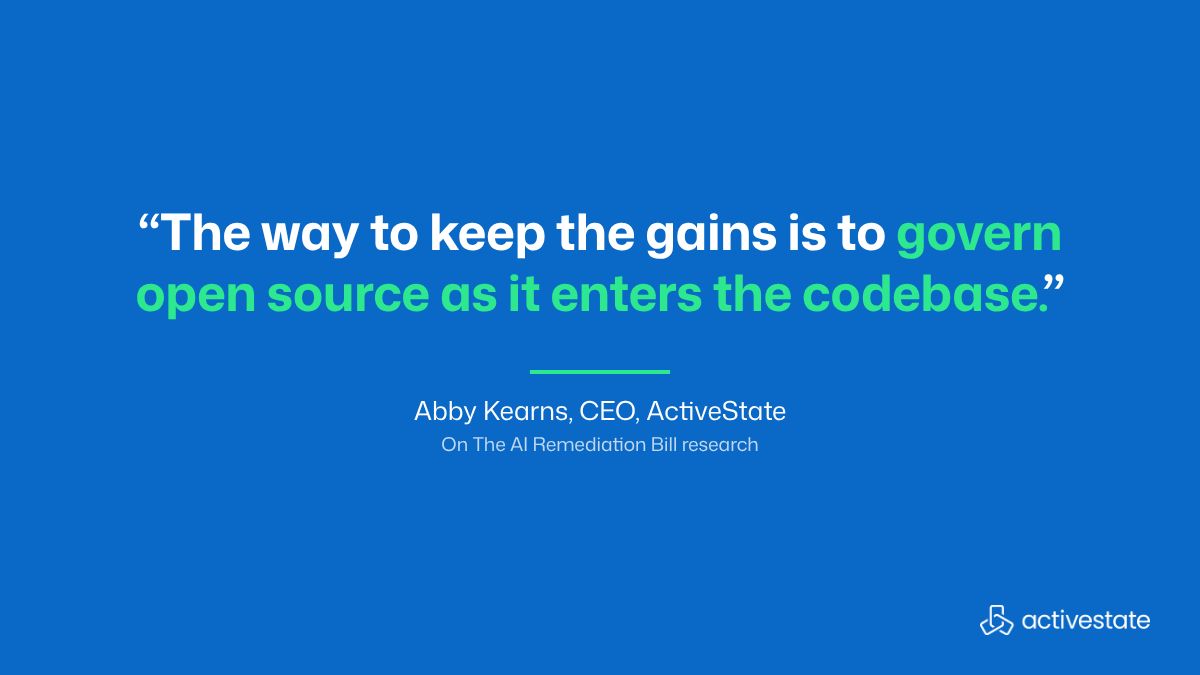
    “The way to keep the gains is to govern open source as it enters the codebase.” Abby Kearns, CEO of ActiveState, on The AI Remediation Bill.
    Download
    00153
  2. ActiveState✓@ActiveState
    The Docker and ActiveState partnership is a mutual reselling agreement. Enterprises can engage either company about hardened base images and vetted open source components. Security gets a trusted sourcing conversation; engineering keeps building. Read the partnership announcement:
    00168
  3. ActiveState✓@ActiveState
    94% of enterprise leaders say AI has increased open source consumption. Yet 63% address open source vulnerabilities only after a scanner finds them, and half say new dependencies can reach production without review. Decide what gets in before it arrives.
    00043
  4. ActiveState✓@ActiveState
    ActiveState partners with Docker to pair Docker Hardened Images with vetted open source components. A hardened foundation from Docker, trusted components from ActiveState, through a single vendor relationship. Control at the source. Keep development moving. Read the partnership announcement:
    Download
    00187
  5. ActiveState✓@ActiveState
    The AI remediation bill lands in four budgets. 76% had a release delayed by unmanaged open source dependencies. 58% received a compliance or audit finding. 32% traced a security incident to an unmanaged dependency. 83% say costs are rising. Only 31% added up the total.
    00174
  6. ActiveState✓@ActiveState
    New report: The AI Remediation Bill. 93% of 300+ enterprise leaders report higher engineering productivity with AI. Engineers also spend at least 139 hours a year fixing or revisiting AI-assisted work. And that's only engineering's share of the bill.
    00063
  7. ActiveState✓@ActiveState
    If a CVE lands on your team today, can you answer “are we exposed” in minutes, not days? A governed source with a contractual SLA (5 business days for critical, clock starting at upstream fix availability) turns that into a scheduled event instead of a fire drill. Worth checking before you need the answer.
    Download
    000117
  8. ActiveState✓@ActiveState
    A flaw just landed on CISA’s Known Exploited Vulnerabilities catalog. The remediation clock started the day it was listed, not the day your team got around to checking. Could you answer “are we exposed” right now, in minutes? Most teams can’t. That’s not a scanning problem. Read the full article:
    001132
  9. ActiveState✓@ActiveState
    319 of 639 packages carried it in May. 111 days dormant. Then it resurfaced in four new packages, straight past npm's own malware scanner. Same week: CVE remediation across 21 major vendors got slower, not faster. Link below for the full article
    Download
    100122
  10. ActiveState✓@ActiveState
    Posts @ActiveState
    Read the full article:
    00017
  11. ActiveState✓@ActiveState
    Famous last words right before production goes down on a Friday at 5PM 🙃
    Download
    000103
  12. ActiveState✓@ActiveState
    Anthropic, Google, and OpenAI's coding-agent tooling has critical flaws sitting in the permission and sandboxing code wrapped around it, not in the models themselves. Jonny Rivera on why the wrapper is the attack surface, not the agent:
    10194
  13. ActiveState✓@ActiveState
    Why did open source security stay an afterthought for so long? Our CEO Abby Kearns has an answer: 'It's a shortcut we were all happy to live with.' Via Alex Scroxton at @ComputerWeekly
    Download
    10069
  14. ActiveState✓@ActiveState
    Posts @ActiveState
    @ComputerWeekly Open source is in 98% of the software running today. Her read on why that finally matters: 'I'm hoping people are standing up and paying attention now, with just the pure number of attacks on the software supply chain that we've seen.'
    10018
  15. ActiveState✓@ActiveState
    Posts @ActiveState
    @ComputerWeekly Read the full conversation on where open source security is headed, and what actually closes the gap:
    0009
  16. ActiveState✓@ActiveState
    AI-assisted engineering teams: 63% say their scope grew in the past year. 45% are working longer hours. Both numbers point to time spent maintaining code that's already shipped, not time spent writing it.
    10093
  17. ActiveState✓@ActiveState
    Posts @ActiveState
    The fix: govern what comes in before it becomes next quarter's maintenance backlog, not slow AI down trying to catch up after the fact. Full breakdown in the reply below. Where does this show up first on your team: the roadmap, the backlog, or a Slack thread nobody's resolved yet?
    10012
  18. ActiveState✓@ActiveState
    Posts @ActiveState
    Full breakdown from Rebecca Banks:
    0008
  19. Show more posts