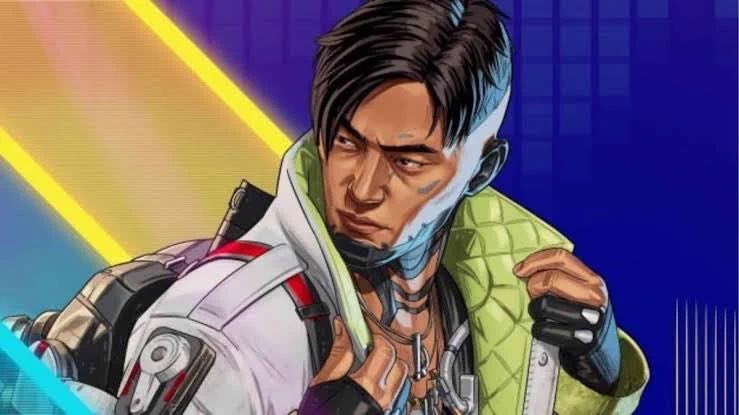
SEASON 31 CRYPTO REWORK 👀‼️
• Tactical: Drone uses a battery system and can be recalled and redeployed without long cooldowns
• New Feature: Sentinel Mode alerts Crypto and his team to detected enemies
• Ultimate: EMP can now be activated with a single button press.
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
tripleS
<SSS: Start with tripleS System> OPEN!
💾 SYSTEM UPDATE: tripleS 멤버 탐색을 시작합니다.
나의 취향에 맞는 tripleS 멤버는 누구일까요?
테스트를 완료하고 나만의 멤버를 찾아보세요!
▶ START TEST
KR :
EN :
JP :
CN :
☑️ SPECIAL QUEST: 결과 공유 이벤트
1. 이벤트 안내 게시글 RT
2. 필수 해시태그와 함께 테스트 결과를 X에 공유
* 필수 해시태그: #SSS_Start_with_tripleS_System#Andless
☑️ QUEST REWARD
이벤트 참여자 중 추첨을 통해 24분께 tripleS 멤버 친필 사인 폴라로이드를 드립니다!
☑️ RESULT ANNOUNCEMENT
2026.11.06(FRI)
*당첨자에게는 DM으로 개별 연락드릴 예정이니 DM 수신 설정을 확인해 주세요.
READY TO START?
지금 바로 tripleS 시스템에 접속하세요!
#tripleS#트리플에스
The FBI continues to warn about two critical security flaws in PHP, a programming language used to build many websites and online services. Attackers could exploit these vulnerabilities to break into systems, putting sensitive information and business operations at risk. Security updates are available and should be applied immediately.
If you are a business owner or website operator, check whether your systems are affected. Contact your IT support team, website developer, or hosting provider for help identifying vulnerable systems and applying the necessary updates.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information on these vulnerabilities (CVE-2026-109618 and CVE-2026-109619), follow PHP’s announcements on CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
Anthropic engineer:
“Anthropic hired me at $350K–$950K because I know how to build harnesses.
99% of people still hand-roll multi-agent systems and wonder why they break.
I build systems that run loops + sandbox tools + turn yesterday’s logs into new skills — same model, 10x more reliable agents that keep improving overnight.”
Opus 5.5 → Agents → Harness → Loops → Graphs
In a short workshop, he shows exactly how to build one from scratch.
step 1 → harness handles loops, context, and sandboxing
step 2 → brain and hands separated — 60% faster to first token
step 3 → runs server-side, resumes from the log after crashes
step 4 → failure is cheap — retry and replay instead of starting over
step 5 → yesterday’s logs become new memory — the system wakes up smarter
Anthropic calls this “dreaming”.
Most people spend weeks building this by hand.
You don’t have to.
Bookmark and watch it.
Then read the full Opus 5.5 harness engineering guide below ↓
Stop letting unfinished Opus 5.5 runs eat your budget
Set up the harness before your next long task
Save progress, verify results, reuse the workflow
The full 7-layer setup below ↓
Stop letting unfinished Opus 5.5 runs eat your budget
Set up the harness before your next long task
Save progress, verify results, reuse the workflow
The full 7-layer setup below ↓
ZERO DAY INCOMMING: Nations Issue Emergency Warnings, Telling Citizens To "Get Prepared" Before Coming Collapse & Resumption Of The Iran War!
Nick Fuentes Agrees That An AI Cyber Attack Is About To Crash The System & Encourages You To Be Ready!
"I Think It's Inevitable That There's Gonna Be Some Sort Of Epic Cyber Attack- Unprecedented & Devastating- That Will Take Out The Power Grid!"
🚨EMERGENCY REPORT: Pentagon Launches All Doomsday Planes For COG During A Nuclear War, Tells Public To Prep For WW3!
Learn Why The Government Is Warning Americans To Stock Up On 90 Days Of Food & Water For Potential Nuclear War / Cyber Attacks That Could Leave The US Without Power For Up To 90 Days!
Alex Jones Breaks Down The Converging Crises That Could Trigger Continuity Of Government Systems— Including Russia Threatening That If NATO Crosses Their Kaliningrad Red Line, They Will Launch Nuclear Attacks On Europe!
PLUS, As Israeli Election Deadlocked & Netanyahu In Panic Mode, Pentagon Tells Gulf States To Prepare For The US & Israel To Resume MASSIVE ATTACKS On Iran!
THIS IS MUST-WATCH/SHARE INFORMATION!
BREAKING: OpenAI says it found a critical flaw in Brotli, a widely used compression library built into software like Node.js, Bun and Envoy.
The bug could let an attacker take over a system just by sending it malicious compressed data, with no login needed. That works both ways: a hacker could hijack an unpatched server, or a malicious server could hijack an unpatched user’s device.
Let’s be real.
Obama dropped more than 26,000 bombs in a single year, 2016 alone, across seven countries: Afghanistan, Iraq, Libya, Pakistan, Somalia, Syria and Yemen.
He expanded the drone war to roughly ten times what Bush ran.
He did more for military industrial complex profits than almost anyone who campaigned on peace.
And Iran was the last name on the Wesley Clark memo: seven countries in five years, Iraq first, Iran last, with the Clean Break doctrine written for Netanyahu setting the table years before.
But here’s the reality underneath it.
War in Iran and Ukraine transfers wealth to bondholders, oil producers and refiners, from everyone who consumes energy and everyone who pays interest on debt.
That’s the financial industrial complex.
The FIC.
The technical industrial complex, the TIC, gets to justify a police and surveillance state at home off the back of the unrest, while field-testing new killing technology abroad.
The US, UK, EU and Israeli stock markets get a stimulus.
Governments become more subordinate to their lobbies through debt.
And the resulting inflation gets socialised onto you.
War is a wealth transfer.
It also drives liquidity into the bond market, which props up the backing of the world’s reserve currency.
In my view, that’s why Obama and Trump both end up at war.
Not left versus right, but the same complexes behind both of them.
Israel is a military industrial complex node, an MIC with a state of its own.
And right now, it’s privatising it: floating its state defence giants, IAI and Rafael, on the stock market at valuations inflated by two years of war.
The MIC is being absorbed into the FIC, cashing in the war premium, live on the Tel Aviv exchange.
War is a racket.
And when the Middle East runs out of road, the MIC needs a new revenue stream.
Which is why the war narratives are now escalating towards Europe, Latin America and a security state across the collective West.
Left and right are tools for real power.
As the power map shifts across BRICS, SCO, ASEAN and GCC, war becomes the tool for negotiating a new world order in a struggle between multiple nodes of power.
In my opinion, it’s not WW3.
It’s a renegotiation.
And burning your attention on culture war and identity politics is exactly how you’re kept from noticing who’s transferring your wealth and raising your prices.
It’s how the system was designed.
You’re just seeing it more clearly now because the MIC is bringing its covert warfare apparatus home and manufacturing the unrest here.
Don’t be a useful idiot in another election cycle of lies that changes none of it.
PS5 system software update 26.07-14.20.00 is available now✨
Please check our page for the latest system software features and how to update.
💡PS5 system software update
Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
🚨 WE COULD BE ENTERING THE ERA OF DIGITAL AND BANKING LOCKDOWNS
Two Warnings Just Came Today That Should Terrify the World.
🇮🇳 First, Indian Prime Minister Modi openly warned today that modern wars can destroy nations by targeting their economies and banking systems through cyberattacks.
🇯🇵 Meanwhile, Japan’s GMO Internet Group CEO reportedly warns of an internet collapse following claims of a massive cyberattack involving fraudulent trades across 70+ brokerage and FX platforms.
Even Japan’s @yutokanzakireal had warned weeks ago that they’d Time the Economic Collapse where AI and energy crisis can take the blame.
G7 countries announced that they are now preparing for a major AI cyberattack on the banking system while G7 governments and central banks have agreed to run simulated AI attacks to test how they would respond to a major incident.
Morgan Stanley, Bank of America, JPMorgan, and Wells Fargo detected unauthorized AI agents accessing customer accounts and attempting to act without user instructions.
Scott Bessent openly talked about a “grand economic reordering” on the scale of Bretton Woods and how AI and stablecoins will be used to grow out of the $40 Trillion debt.
The internet and the banking system will be shut off for the transition to the new stablecoin economy?
Imagine banks freezing, trading platforms shutting down and internet access being restricted overnight while blockchain is offered as the solution.
A new surveillance system is being opened without naming it CBDCs.
This is why @DNAOnChain is about to be the biggest privacy solution in the new on-chain financial system.
Private digital identities. Zero-knowledge proofs. A financial system where you can prove who you are without exposing who you are.
A future of complete on-chain financial privacy and almost nobody is paying attention.
During the crash, AI and cyberattack will be the excuse in how they restrict people’s ability to transfer funds to cover their margin calls.
Be prepared for the new financial system. It’s always followed by an engineered crisis.
A Chinese quant used Grok Bot to turn $1000 into $263,396.56.
He studies applied mathematics and builds algorithms between classes.
His account: BoneOhio.
At such a young age, he has already made over a quarter of a million simply by knowing the right formulas and knowing how to use Grok Bot.
Result:
$1000 → $263,396.56
Profile:
How to build a system like this:
Quant Flow Memory reads order flow and matches it against historical price movements. The other modules check risk and execution.
1. Multilevel Flow
Flowₜ = Σ wₖ × OFIₖ,ₜ
The bot tracks new orders, cancellations and fills across several order book levels.
One large buyer can disappear. Pressure across multiple levels gives you more information.
2. Flow Memory
Responseₕ = Σ gⱼ × Flowₜ₋ⱼ
The model identifies order sequences that preceded price moves. The weights are calibrated on historical data.
The order book gets a memory.
3. EV Gap
Edge = expected move − trading costs
Projected move: 3¢. Entry and exit: 1¢. That leaves a 2¢ edge per share.
If costs eat the difference, there is no trade.
4. Kelly Criterion
f* = (bp − q) / b
Win probability and payout determine the fraction of capital to risk.
Fractional Kelly reduces exposure to model error. One bad entry should not wipe out the account.
5. Bayesian Updates
P(H|D) ∝ P(D|H) × P(H)
New fills. Large orders cancelled. Pressure shifts.
The bot updates its probability estimate. If the signal disappears, the order is pulled.
6. KL-Divergence
Dₖₗ(P‖Q) = Σ Pᵢ ln(Pᵢ/Qᵢ)
Measures the divergence between comparable probability distributions. Flags an anomaly for review rather than calling every difference an arbitrage.
7. Stoikov Model
r = s − qγσ²(T − t)
Adjusts the reservation price for inventory, volatility and risk.
The more inventory already held, the more cautious the next entry.
8. LMSR
C(q) = b ln Σ exp(qᵢ/b)
An additional model for price simulations. Actual entries still need to be checked against Polymarket’s order book.
In practice:
→ Order flow generates a signal.
→ Memory estimates the move.
→ Costs and risk pass the checks.
→ Only then is an order placed.
The math is public.
The edge needs to be validated on data.
The difference is that most people never build the system.
Paste these formulas into Grok Bot and build your own bot. Start with simulated trades.
Copy him:
Bookmark this post so you don’t lose it.
Soon I’ll break down another bot and the formulas behind its strategy.
Grok Bot is the best AI agent right now
It gives you an army of agents that can do work for you 24/7
If you set it up correctly, you gain super powers
In this article, I cover how to turn Grok Bot into your own Bloomberg Terminal
Grok Bot is the best AI agent right now
It gives you an army of agents that can do work for you 24/7
If you set it up correctly, you gain super powers
In this article, I cover how to turn Grok Bot into your own Bloomberg Terminal
Anthropic engineer:
“Anthropic hired me at $350K–$950K because I know how to build harnesses.
99% of people still hand-roll multi-agent systems and wonder why they break.
I build systems that run loops + sandbox tools + turn yesterday’s logs into new skills — same model, 10x more reliable agents that keep improving overnight.”
Opus 5.5 → Agents → Harness → Loops → Graphs
In a short workshop, he shows exactly how to build one from scratch.
step 1 → harness handles loops, context, and sandboxing
step 2 → brain and hands separated — 60% faster to first token
step 3 → runs server-side, resumes from the log after crashes
step 4 → failure is cheap — retry and replay instead of starting over
step 5 → yesterday’s logs become new memory — the system wakes up smarter
Anthropic calls this “dreaming”.
Most people spend weeks building this by hand.
You don’t have to.
Bookmark and watch it.
🚨 This may be one of my last posts before things get real.
Reports are circulating that U.S. and European power grids are under active, coordinated attack right now.
At the same time, AI-driven campaigns are hitting critical systems worldwide, with claims of tens of thousands of machines already compromised.
Separately, there’s a growing push to prepare the public for an announcement that a massive UFO mothership has entered the solar system and is on course for Earth in early 2027.
If you’ve been tracking the NHI disclosure timeline, you know these kinds of developments don’t happen in isolation.
What comes next has the potential to make the COVID response look like a dress rehearsal.
Pay attention.
Prepare accordingly.
Correct.
Using Starlink, a civilian commercial service, for offensive drone strikes to kill people has never been allowed, nor should it be.
Starshield, a different system, is controlled by the US government. What they decide to do is up to them.
Ukraine military violated Starlink terms of service and used it for offensive drone strikes to kill people. That loophole was closed last week.
Starlink remains critical to the defense of Ukraine, as it is the only system that cannot be jammed or blown up, at least for now. Were Starlink to be turned off, the Ukrainian front line would collapse immediately. This is NOT a threat, it is simply a statement of fact.
Starlink was also crucial to preventing Russia from overrunning Ukraine in the early days of the war, as all other means of communication were destroyed or jammed by Russia.
SpaceX has done more to defend Ukraine than any private company on Earth BY FAR.
That said, I have nothing but UTTER CONTEMPT for the virtue-signaling evil warmongers who push for endless slaughter and offer no realistic solution to the conflict. May you burn in hell.
End of story.
Share
Copied
varifrank@varifrank
STARLINK WORKS THE SAME WAY ITS ALWAYS WORKED. ITS NOT A WEAPONS SYSTEM, NO MATTER HOW MUCH UKRAINE WANTS IT TO BE.
A 135K-star GitHub repo is built around one painfully obvious idea:
Your coding agent should map the codebase once, not grep it forever.
Graphify turns an entire project into a persistent, queryable knowledge graph that AI coding agents can use to understand how different parts of the system connect.
Functions, classes, files, SQL schemas, infrastructure configurations, documentation, PDFs, images and videos can become connected nodes instead of isolated pieces of context the agent has to rediscover.
So instead of:
→ Search for authentication
→ Open twelve files
→ Follow imports and function calls
→ Lose the trail as the context fills up
The agent can ask:
> What connects authentication to the database?
> Trace the path from UserService to DatabasePool.
> Explain RateLimiter.
> Which components are central to this architecture?
Graphify returns relevant graph relationships and paths, rather than another collection of keyword matches.
For source code, the implementation is particularly interesting.
It uses tree-sitter to parse approximately 40 programming languages locally, extracting functions, classes, imports, calls, inheritance and cross-file relationships.
No embeddings, vector database or LLM calls are needed to construct the code graph.
Document and media processing works differently. PDFs, images and other non-code content can go through an optional semantic extraction step using a configured model.
Every relationship carries a confidence label:
→ EXTRACTED: Explicitly present in the source
→ INFERRED: Derived through analysis or resolution
→ AMBIGUOUS: Uncertain and flagged for review
Graphify also uses community detection to identify related subsystems and highlights highly connected nodes that may be important to the overall architecture.
But the part that makes this useful for coding agents is what happens after the graph is built.
Graphify integrates with Claude Code, Codex, Cursor, Gemini CLI, GitHub Copilot and more than 20 other assistants.
Depending on the platform, it installs hooks or persistent instructions that encourage the agent to query the existing graph before repeatedly searching and reading source files.
The graph can be committed to Git, updated incrementally as files change, and exposed through MCP.
There's also support for examining pull requests against the graph, including identifying PRs that touch related graph communities and may need closer review.
The local tool produces three useful artifacts: an interactive HTML graph, a Markdown architecture report and a reusable graph.json.
Long context windows help coding agents read more code.
A persistent knowledge graph gives them a way to navigate what they've already analyzed.
And as coding agents spend more time working inside large repositories, avoiding repeated discovery of the same architecture becomes increasingly useful.
Here's the GitHub Repo:
An Anthropic engineer explains why he earns $350K–$950K:
“I know how to build harnesses.
99% of people still build multi-agent systems manually and wonder why they keep breaking.
I build systems that run loops, use sandboxed tools, and turn yesterday’s logs into new skills.
Same model. 10x more reliable agents that improve while you sleep.”
Opus 5.5 → Agents → Harnesses → Loops → Graphs
In a short workshop, he breaks down how to build one from scratch:
Step 1 → Manage loops, context, and sandboxing through a harness
Step 2 → Separate the brain from the tools to reach the first token 60% faster
Step 3 → Run agents server-side and recover from crashes using logs
Step 4 → Make failures recoverable with retries and replays instead of starting over
Step 5 → Turn past execution logs into new memories so the system gets smarter over time
Anthropic calls this process “dreaming.”
Most developers spend weeks building these systems manually.
This workshop shows you a faster way.
Bookmark this and watch it.