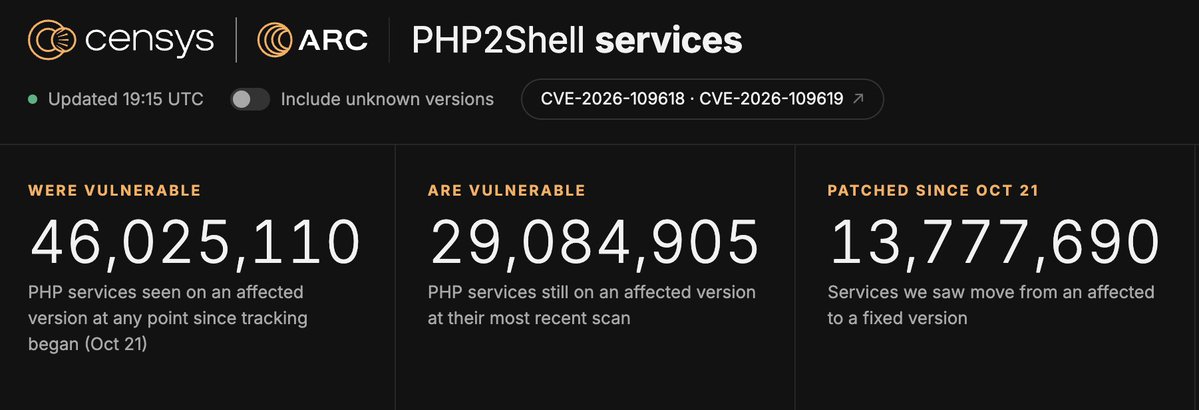
My theory for what happend to AO3:
They didn't hear about the PHP thing in time, someone got into the website and started changing/deleting stuff. They hoped it was a small hack and could restore it quickly. Turns out the entire website is vulnerable and have to rebuild much more
CRITICAL QUESTION EMERGES IN BINANCE HACK OVER HOW ATTACKERS GAINED CONTROL OF ITS WALLET
Attackers reportedly used EIP-7702 delegation to redirect Binance’s wallet to malicious code, allowing funds to be drained.
But how did they obtain authorization?
Two possibilities are being investigated:
1) a stolen private key or
2) a malicious authorization signature obtained through a compromised signing process.
Neither has been confirmed.
If the private key wasn’t stolen, the attack could expose a major vulnerability in how exchanges authorize transactions, rather than how they secure private keys.
CRITICAL QUESTION EMERGES IN BINANCE HACK OVER HOW ATTACKERS GAINED CONTROL OF ITS WALLET
Attackers reportedly used EIP-7702 delegation to redirect Binance’s wallet to malicious code, allowing funds to be drained.
But how did they obtain authorization?
Two possibilities are being investigated:
1) a stolen private key or
2) a malicious authorization signature obtained through a compromised signing process.
Neither has been confirmed.
If the private key wasn’t stolen, the attack could expose a major vulnerability in how exchanges authorize transactions, rather than how they secure private keys.
We’ve published a post-mortem on our response to the October PHP and Node.js security releases, covering the in-place patching of Laravel Cloud, the impact on Forge, Envoyer, and Vapor, and what we’re changing →
PHP vulnerability post-mortem reveals bug was known two years ago — Small team of maintainers knew of the issue before it was made public, as new PHP2Shell chained exploit ravages servers
Closing out #php2shell: a universal black-box PoC for PHP's session upload-progress bug. One pure-HTTP chain - arm the allocator, spray fake refs, leak the heap, beat ASLR, turn a destructor into system(). Verified blind on Debian 13 PHP 8.4.24, x86-64 + arm64: RCE as www-data.
Compiling PHP from source is coming along well 😃
So when the next PHP panic hits, we'll be able to deploy security updates within ~24 minutes instead of waiting on upstream dependencies (which took about 4 hours) ⚡️
The fact that the PHP vulnerability didn't immediately turn into mass chaos is only "surprising" to people who don't know anything about cybersecurity (or people trying to sell you something).
Updated WAF rules to block new PHP RCE attacks found via the 2026-11-03 CTF challenge. Keep your apps safe against CVE-2026-109618 and CVE-2026-115560.
Updated WAF rules to block new PHP RCE attacks found via the 2026-11-03 CTF challenge. Keep your apps safe against CVE-2026-109618 and CVE-2026-115560.
my turn , here is my poc for CVE-2026-109618 / CVE-2026-109619 ,exact build PHP 8.5.11 / Apache mod_php .
Includes fresh-leak validation, evidence handling and an execution diagram.
Exact-build only not a universal PHP exploit.
For authorized lab research.
#AppSec#PHPの脆弱性だと思うもの#infosec#PHP
The PHP situation has hit Japan's arcades pretty hard - lost revenue, many games not working.
No game should be inoperable if there isn't internet; I hope the industry learns from this quickly.
That says something for offline only games though, doesn't it?
Flock PHP 1.0 is here! 🥳
The free and open source local development environment for Laravel and PHP, native on macOS, Windows and Linux.
No paid tier, every feature included. Out of beta and ready for your projects.
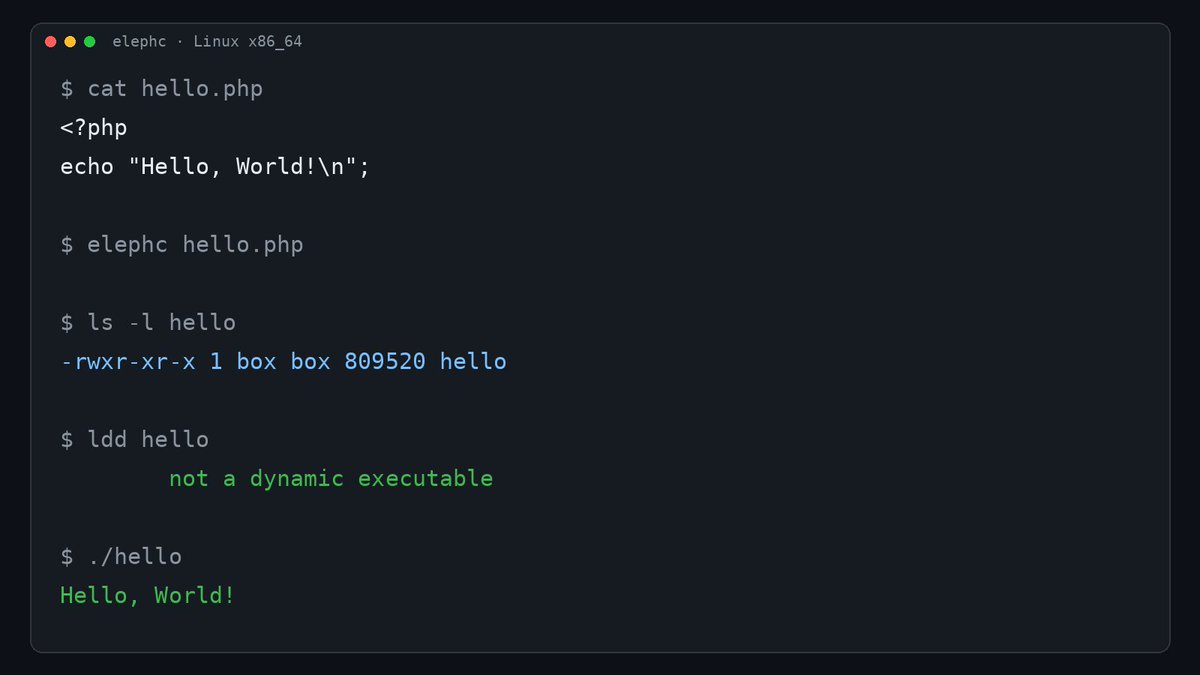
A PHP Hello World, compiled by elephc: one 791 KB static binary. 🐘
No PHP installed. No shared libraries: ldd says "not a dynamic executable".
Compiles in ~115 ms, runs in 0.5 ms.
Ship PHP as a single file.
PHP 8.6 arrive le 19 novembre, c'est une version mineure qui apporte de vraies avancées structurelles pour l'écosystème. Notre équipe a décortiqué les changements notables à prévoir, à découvrir sur notre blog :
ICYMI, the patched PHP packages for CVE-2026-109618 and CVE-2026-109619 have been rolled out to the production repositories for every PHP stream on AlmaLinux 8, 9, and 10.
Learn more about the CVEs and get the patched packages ⤵️