Posts with #php8

#php8

Public posts on X that use #php8.

Related hashtags

  1. Libu 🎃@LibuWangxian
    My theory for what happend to AO3: They didn't hear about the PHP thing in time, someone got into the website and started changing/deleting stuff. They hoped it was a small hack and could restore it quickly. Turns out the entire website is vulnerable and have to rebuild much more
    Download
    8917222.7K
  2. 𝖘𝖕𝖔𝖔𝖐𝖞 𝖘𝖙𝖆𝖗 💫🎃 | leyendo Hollanov ♡@amberhepburn_
    no entiendo, se cayó de la nada, no le avisaron a nadie y ahora dicen que tomara entre dos a CUATRO semanas restaurar el servicio? que pasa?!?? nos están atacando? se quemaron los servidores? no entiendo nada
    AO3 Status @AO3_Status
    We estimate that service restoration for #AO3 will take around 2 weeks but it could be up to 4 weeks. We are hopeful that we will be able to bring the site back up in a degraded state sooner. Refer to our status page for updates:
    8967017.4K496K
  3. AO3 Status@AO3_Status
    We estimate that service restoration for #AO3 will take around 2 weeks but it could be up to 4 weeks. We are hopeful that we will be able to bring the site back up in a degraded state sooner. Refer to our status page for updates:
    16K52.7K419K44.1M
  4. kenny 🍉@KenzieFive
    @amberhepburn_
    @amberhepburn_ Sounds like, with the PHP threat, they did the initial 12hrs to do an patch/update investigation but there was probably a discovery that lead to the need to rebuild the site. Probably not something they decided very easily but a necessity. The team are also volunteers
    7231.8K59K
  5. nunomaduro✓@enunomaduro
    PHP 8.6 ships november 19 partial function application, a duration type, clamp, readonly property defaults, stream errors as exceptions and a lot more all you need to know:
    91414510.6K
  6. ANSSI@ANSSI_FR
    MàJ ⚠️Vulnérabilités PHP. 🟡 Le risque se déplace des sites web vers de très nombreux produits tiers intégrant des versions de PHP. Ces équipements doivent également faire l’objet de mises à jour dès que possible. + d'infos dans l'alerte du @CERT_FR : ➡️
    Download
    613526354.4K
  7. The Hacker News@TheHackersNews
    UPDATE: Palo Alto Networks Unit 42 has retracted its earlier assessment linking the European government agency attack to PHP2Shell exploitation. The attack involved a vulnerable PHP application, but Unit 42 says it cannot confirm initial access was tied to the specific PHP2Shell CVEs. We've updated our report ↓
    The Hacker News @TheHackersNews
    🚨 PHP2Shell attackers accessed MFA secrets and password hashes at a European government entity in just 2 hours. That's not all. → Signs of agentic AI use in post-exploitation activity → Suspected Lazarus-linked operators scanning 216 targets worldwide Full details ↓
    174723241.9K
  8. The Hacker News@TheHackersNews
    🚨 PHP2Shell attackers accessed MFA secrets and password hashes at a European government entity in just 2 hours. That's not all. → Signs of agentic AI use in post-exploitation activity → Suspected Lazarus-linked operators scanning 216 targets worldwide Full details ↓
    Download
    532891.2K179K
  9. Daniel Púa✓@devploit
    PHP2Shell update 🚀 13 → 56 perfiles. 5 → 30 con RCE. Gracias a las aportaciones de la comunidad por ampliar la colección. Nuevos: stage-3 vessel 8.5.0–8.5.10, Debian 13/apxs2 y nginx+PHP-FPM.
    59446824.7K
  10. Roberto Bayardo | bayardo.eth✓@roberto_bayardo
    This is a lot worse than the PHP vulnerability from a few days ago. If you're running a Go based server (e.g. geth) you may be at risk.
    tobi lutke @tobi
    What a disaster
    7716436.3K
  11. tobi lutke✓@tobi
    What a disaster
    1533284.2K1.7M
  12. 国家サイバー統括室(注意・警戒情報)@cyber_forecast
    【更新】PHPの複数の脆弱性(PHP2Shell)に関する注意喚起を更新。あるファイアウォール製品で侵害の成功を示唆する痕跡を確認したと報告されています。引き続き、本脆弱性の対処に関しては利用製品への影響を確認し、速やかな対策と侵害調査をお願いします。
    151.6K4.8K2M
  13. Trail of Bits✓@trailofbits
    Our demo shows PHP2Shell giving a shell on MediaWiki, Symfony, Laravel, and phpBB. We’ve confirmed exploits work on pre-patch releases of PHP 8.2–8.5. If you haven’t updated, assume attackers can compromise your server, and that exploitation will only get easier.
    Download
    Dan Guido @dguido
    Update: Our PHP exploit is now production-grade. * stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load * ARM64 + x86-64 targets * MediaWiki, WordPress, phpBB, Laravel * Apache/mod_php and nginx/php-fpm -> root
    145328738.9K
  14. Dan Guido✓@dguido
    Update: Our PHP exploit is now production-grade. * stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load * ARM64 + x86-64 targets * MediaWiki, WordPress, phpBB, Laravel * Apache/mod_php and nginx/php-fpm -> root
    Download
    39105678110K
  15. GGSec@GGASecDe
    Closing out #php2shell: a universal black-box PoC for PHP's session upload-progress bug. One pure-HTTP chain - arm the allocator, spray fake refs, leak the heap, beat ASLR, turn a destructor into system(). Verified blind on Debian 13 PHP 8.4.24, x86-64 + arm64: RCE as www-data.
    Download
    37516.1K
  16. 𝐇𝐚𝐦𝐳𝐚 | Networking Guy✓@Hamzaonchain
    October Recap: - PHP got hacked - Railway got hacked - OpenCode got hacked - Binance got hacked - Polymarket got hacked - GitHub Actions got hacked - SoftBank got hacked - Cursor Marketplace got hacked - Coinbase's vendor got hacked - Fireworks AI got hacked - LiteLLM got hacked - Capcom got hacked - npm packages got hacked - TiDB Cloud got hacked - Warp's vendor got hacked It was a crazy Cybersecurity Awareness Month.
    8311865.4K
  17. Vincenzo Petrucci✓@nahime0
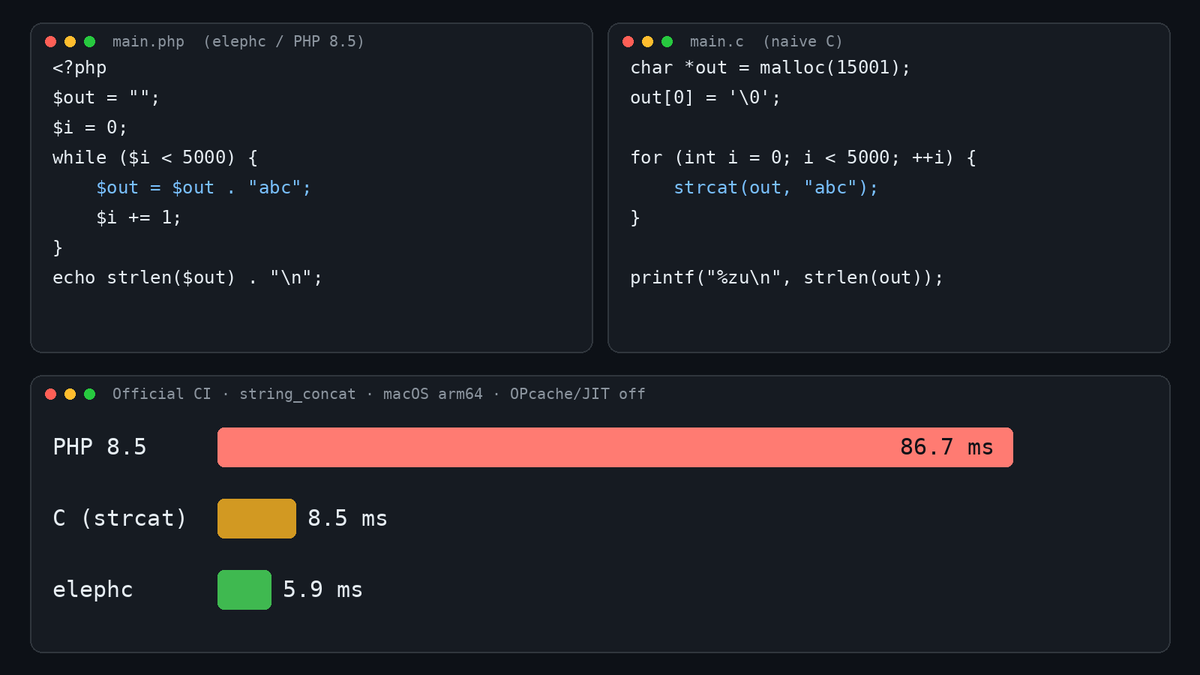
    PHP compiled by elephc just beat C. Well, naive C. 🐘 Official CI, string_concat: PHP 8.5: 86.7 ms C (strcat loop): 8.5 ms elephc: 5.9 ms strcat rescans the string on every call, O(n²). elephc reuses the buffer and grows it geometrically. macOS arm64, OPcache/JIT off.
    Download
    8171269.6K
  18. NCSC UK@NCSC
    The critical PHP security issue highlights the importance of understanding your organisation’s attack surface. The NCSC’s guidance can support your organisation to navigate a vulnerability patch wave and respond with greater confidence. Learn more:
    Download
    113715312.5K
  19. LiveOverflow 🔴 hextree.io✓@LiveOverflow
    I took a closer look at the CTF, which aims to demonstrate that PHP2SHELL is not realistically exploitable. So I gave it a try. Note: My analysis could be wrong, and I'm more than happy to be proven otherwise. Here’s what I found: • The server responds with Server: nginx and X-Powered-By: PHP/8.4.26. • My differential fingerprinting scanner independently confirmed at least PHP 8.2+ • Hypotheses: I considered two possible setups: ◦ nginx → PHP-FPM ◦ nginx → Apache → PHP-FPM/mod_php • After comparing the server's behavior against local test environments, the closest match appears to be nginx → PHP cli-server. Plot twist: the response behavior is consistent with the PHP cli-server serving a static index.html rather than an index.php. If that's indeed the case, the challenge appears to be intentionally made unexploitable. My conclusion (for now) is that I'm questioning whether this is a good-faith challenge. Happy to be corrected if I've missed something!
    Download
    89982.2K574K
  20. Infobae En Vivo✓@infobaenvivo
    🟠 ALERTA MUNDIAL POR UNA FALLA QUE PUEDE DEJAR EXPUESTAS MILLONES DE PÁGINAS WEB El problema afecta a PHP, un sistema utilizado para crear sitios web. Las autoridades advirtieron que los hackers podrían aprovechar las fallas para acceder a información privada y recomendaron actualizarlo cuanto antes.
    Download
    205028237.2K
  21. Black Hills Information Security✓@BHinfoSecurity
    php2shell (CVE-2026-109618/109619, CVSS 9.2) is unauthenticated RCE in PHP core. We took it into the lab to see what it actually looks like on a host, and how a SOC catches it.
    228886.1K
  22. rekdt✓@rekdt
    If your IT guy dresses like this, you don’t need to worry about those later version PHP vulnerabilities
    Download
    243786316.2K
  23. Eric Van Johnson✓@shocm
    🚀 PHP 8.6 just lifted a four-year-old restriction on readonly properties! What does this mean for your code? Say goodbye to those pesky limitations and hello to cleaner, more efficient coding! Dive into the details! #PHP8 #Devel…
    367010.2K
  24. Atlus✓@CLTec
    #AHORA 🚨 MULTIPLES SITIOS DE GOBIENOS BAJO ATAQUE 🇨🇵🇩🇪🇬🇧 🇧🇪🇨🇿🇩🇰🇨🇦 🔺Reporte de Vulnerabilidades críticas en #PHP , han desencadenado una ola de hackeos e intento de acceder a sistemas de información en 12 países, que los ha obligado a cerrar sitios de gobierno 👇🏻
    Download
    68116110.8K
  25. Show more posts