Daniel Lockyer✓

@DanielLockyer

• I make sites faster and cloud/LLM bills lower 🚀 • 2:43 marathoner (🔜 2:39) • Performance is my thing

190 Following73K Followers11.2K Posts
  1. Daniel Lockyer✓@DanielLockyer
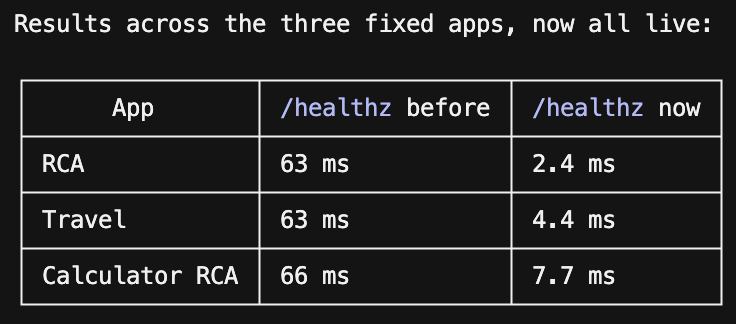
    I've found (and locally fixed) an annoying performance bug on @X web! TLDR: go to a post with a lot of replies, and scroll up and down - notice it's laggy? There's a component that calculates the scroll parent, and then removes the scroll listener when unmounting. But it seems we don't even have a scroll listener most of the time, so we can avoid the heavy _getScrollParent function by wrapping it in a conditional This removes seconds of forced reflow and lag for me Would love to get it fixed! 🙏🏻 @X @engineering @elonmusk @nikitabier
    Download
    115873.2K802K
  2. Daniel Lockyer✓@DanielLockyer
    I actually think right now is a great time in my life to have kids (30yo) Old enough to have done a lot of the crazy solo things but now to feel established in what I'm doing Young enough to be energetic and to be able to spend loads of time with kids and grandchildren
    Steven Bartlett @StevenBartlett
    Darby Saxbe asked her adviser when to have kids, and she laughed. @darbysaxbe
    000165
  3. Daniel Lockyer✓@DanielLockyer
    Daniel Lockyer
    RT @DanielLockyer: Imagine a supply-chain attack on Yubico right now 🫠
    Michael Magán @mrmagan_
    I bet a lot of people are having the same idea I'm having...
    06017.3K
  4. Michael Magán✓@mrmagan_
    I bet a lot of people are having the same idea I'm having...
    Download
    2381707.7K2.2M
  5. Daniel Lockyer✓@DanielLockyer
    Daniel Lockyer
    RT @DanielLockyer: We should be more ambitious
    Dan Luu @danluu
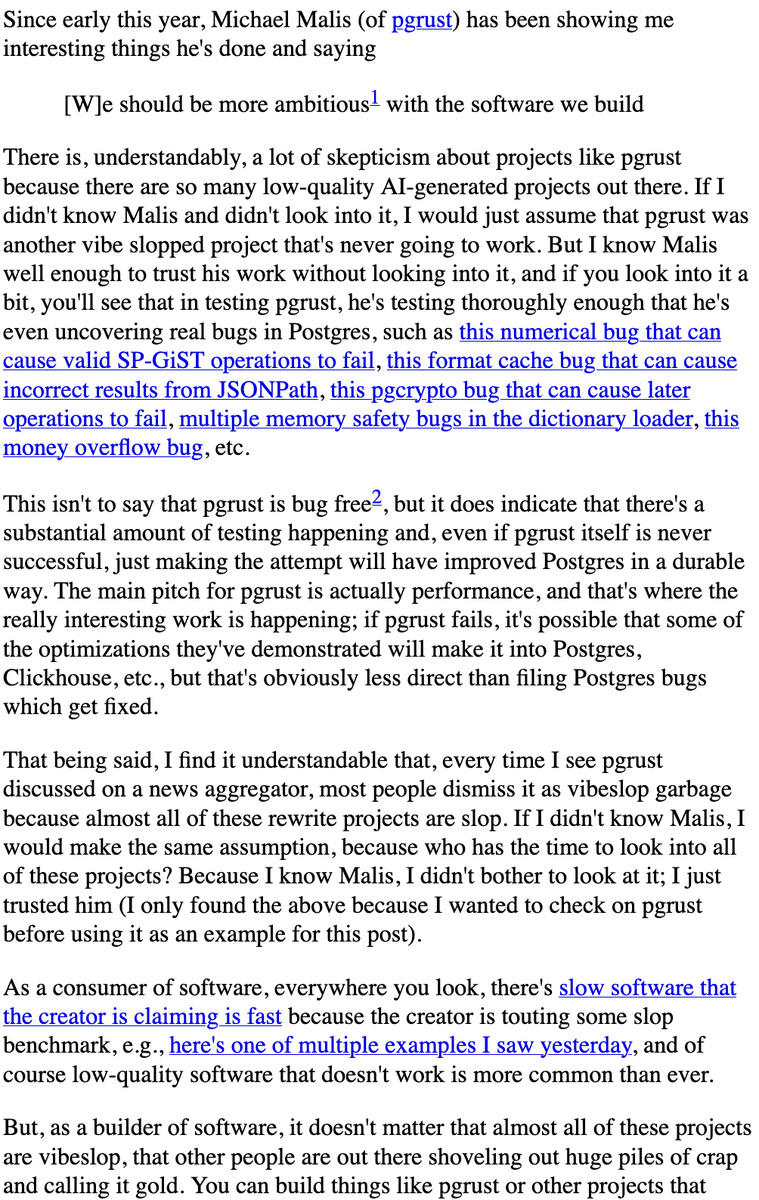
    We should be more ambitious with the software we build:
    0204.2K
  6. Dan Luu@danluu
    We should be more ambitious with the software we build:
    Download
    184748724.7K
  7. Daniel Lockyer✓@DanielLockyer
    Trying out Jellyfin! I previously tried this and had a bad experience, but it appears nicer now Worked with my agent to: - install Jellyfin on my home media server - enable developer mode on my TV - sideload the Jellyfin app - configure all the mounts with correct permissions 🤠
    Daniel Lockyer @DanielLockyer
    Ok, now we've done this, can we figure out why the Plex TV app is so poor quality? It's extremely slow and buggy
    81203.2K
  8. Daniel Lockyer✓@DanielLockyer
    Ok, now we've done this, can we figure out why the Plex TV app is so poor quality? It's extremely slow and buggy
    Md Ismail Šojal 🕷️ @0x0SojalSec
    WTF, $3000 Samsung TV has an always-on mic, automatic content recognition, geo tracking, network mapping, and ships your data to Samsung + 400 partners. Bro Rooted a brand-new 2025 Samsung TV after noticing absurdly targeted ads. Firmware was locked down, so zero-days it was. Got a root shell. then found: always-on voice service, ACR, geo, full telemetry pipeline, and four separate DRM systems. This isn’t a bug, It’s the product bro.
    1117810.2K
  9. Daniel Lockyer✓@DanielLockyer
    Installed Omarchy on a 2018 MacBook Air and WiFi doesn't work at all 😭
    Download
    59020324.5K
  10. Md Ismail Šojal 🕷️✓@0x0SojalSec
    WTF, $3000 Samsung TV has an always-on mic, automatic content recognition, geo tracking, network mapping, and ships your data to Samsung + 400 partners. Bro Rooted a brand-new 2025 Samsung TV after noticing absurdly targeted ads. Firmware was locked down, so zero-days it was. Got a root shell. then found: always-on voice service, ACR, geo, full telemetry pipeline, and four separate DRM systems. This isn’t a bug, It’s the product bro.
    Download
    5322.9K20.9K3.2M
  11. Daniel Lockyer✓@DanielLockyer
    I currently have 4 VPS machines running full blast to find security vulnerabilities in popular OSS projects with open weight models
    481073346.3K
  12. Daniel Lockyer✓@DanielLockyer
    Posts @DanielLockyer
    I'm pretty hands off with the instructions, just some guidance around: - finding novel, un-fixed, un-reported bugs (it sometimes has a habit of looking at the issue trackers to find known bugs) - if it does find a novel issue without prior research, then looking if it has been reported upstream - providing a self-contained proof-of-concept - sometimes the vulnerability class - sometimes extra insights
    21344K
  13. Daniel Lockyer✓@DanielLockyer
    root cause of the pain you'll experience this weekend:
    Download
    OpenAI @OpenAI
    During this red-teaming exercise, we also found a vulnerability that allows for unauthenticated remote code execution in Brotli, a widely-deployed compression library included in many pieces of software such as Node.js, Bun, and Envoy. The flaw could let an attacker run their own code on affected systems by sending or replying with malicious compressed data, without any need to create a user account. That is, an unpatched server that accepts compressed input could be taken over by a malicious client, and an unpatched client that accepts compressed input (such as “curl --compressed”) could be taken over by a malicious server. This root cause issue was actually fixed in the Brotli source code in February, but it wasn’t known at the time that it gave rise to a security vulnerability and there was no more recent release of Brotli. Since Brotli is built into other software, any software which includes this library needs to take the update too, followed by the users of that software. We disclosed the vulnerability to Brotli and other downstream projects such as Node.js, which released or are currently releasing security updates, and Brotli cut new release versions and published a CVE. More details on the patch and mitigations below:
    40354.4K
  14. OpenAI✓@OpenAI
    During this red-teaming exercise, we also found a vulnerability that allows for unauthenticated remote code execution in Brotli, a widely-deployed compression library included in many pieces of software such as Node.js, Bun, and Envoy. The flaw could let an attacker run their own code on affected systems by sending or replying with malicious compressed data, without any need to create a user account. That is, an unpatched server that accepts compressed input could be taken over by a malicious client, and an unpatched client that accepts compressed input (such as “curl --compressed”) could be taken over by a malicious server. This root cause issue was actually fixed in the Brotli source code in February, but it wasn’t known at the time that it gave rise to a security vulnerability and there was no more recent release of Brotli. Since Brotli is built into other software, any software which includes this library needs to take the update too, followed by the users of that software. We disclosed the vulnerability to Brotli and other downstream projects such as Node.js, which released or are currently releasing security updates, and Brotli cut new release versions and published a CVE. More details on the patch and mitigations below:
    OpenAI @OpenAI
    Over the past several months, we have substantially hardened the security of our research training environment. We’ve removed live internet access for all frontier models during training and built an offline world for them to use instead—a cached version of the web where they can still learn to browse, search, and use applications. On September 20, after a model exploited a DNS misconfiguration to find a way outside of this offline world, we paused frontier training to strengthen containment further. We assembled teams of agents, powered by our most cyber-capable models, and tasked them with finding weaknesses in our research environments. While they found no route to the internet they could easily exploit while concealing their activity from our monitors, they did find zero-day vulnerabilities, virtual machine escapes, and hardware side-channels for communication between agents. We used their discoveries to further strengthen our defenses and contribute fixes to open-source software. After strengthening our containment architecture, we resumed our frontier RL training and inference on October 1. We’ve reserved substantial compute for continuous red-teaming, and made high-compute red-teaming part of the safety cases we use to decide whether frontier training and evaluation can proceed securely.
    5671K7.1K2.2M
  15. Daniel Lockyer✓@DanielLockyer
    One advantage of constant security vulnerabilities: We'll become very good at updating/patching systems quicker and quicker
    2351938.2K
  16. Daniel Lockyer✓@DanielLockyer
    graph drop
    Ben Vinegar @bentlegen
    in hindsight we should have switched to @turbopuffer much earlier
    10122.7K
  17. Daniel Lockyer✓@DanielLockyer
    Happy Saturday!!
    Aikido @AikidoSecurity
    Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.” A significant blast radius. This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression. Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
    026410K
  18. Aikido✓@AikidoSecurity
    Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.” A significant blast radius. This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression. Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
    Download
    1178503.5K805K
  19. Daniel Lockyer✓@DanielLockyer
    We should start normalising uptime in software
    pushpak @pushpak1300
    We should start normalising downtime in software for maintenance.
    411345.3K
  20. pushpak✓@pushpak1300
    We should start normalising downtime in software for maintenance.
    35914414K
  21. Daniel Lockyer✓@DanielLockyer
    If you're a cool company working on something exciting in the performance/testing/observability/security area, and you'd like me to give it a try, email my bot: daniellockyer@mail.grokbot.com
    31475.9K
  22. Daniel Lockyer✓@DanielLockyer
    Posts @DanielLockyer
    Can't promise anything, time is short! But I'd like to see some new things and share it if good
    0011K
  23. Daniel Lockyer✓@DanielLockyer
    I've been helping to update an old PHP 5.6 (don't ask) machine, due to the recent vulnerabilities Most of the update flow didn't work by default, due to the age of the PHP + OS versions But I gave my agent SSH access and it did an excellent job Did a full analysis, plan, gathered all the source + patches, compiled it, generated scripts to verify compatibility, updated it, monitored logs for regressions sysadmin with agents is fun!
    21124614.8K