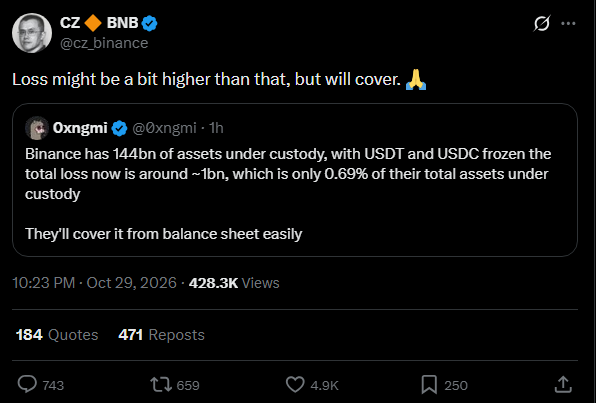Dark Web Informer

@DarkWebInformer

One guy. Global cybercrime. Tracked so you don't have to. Ransomware, data breaches, dark web activity, darknet markets, IOCs & emerging threats. Stay informed!

97 Following254K Followers36.3K Posts
  1. Dark Web Informer@DarkWebInformer
    ‼️ Footage of the LeakBase domain administrator getting arrested in Taganrog, Russia.
    Download
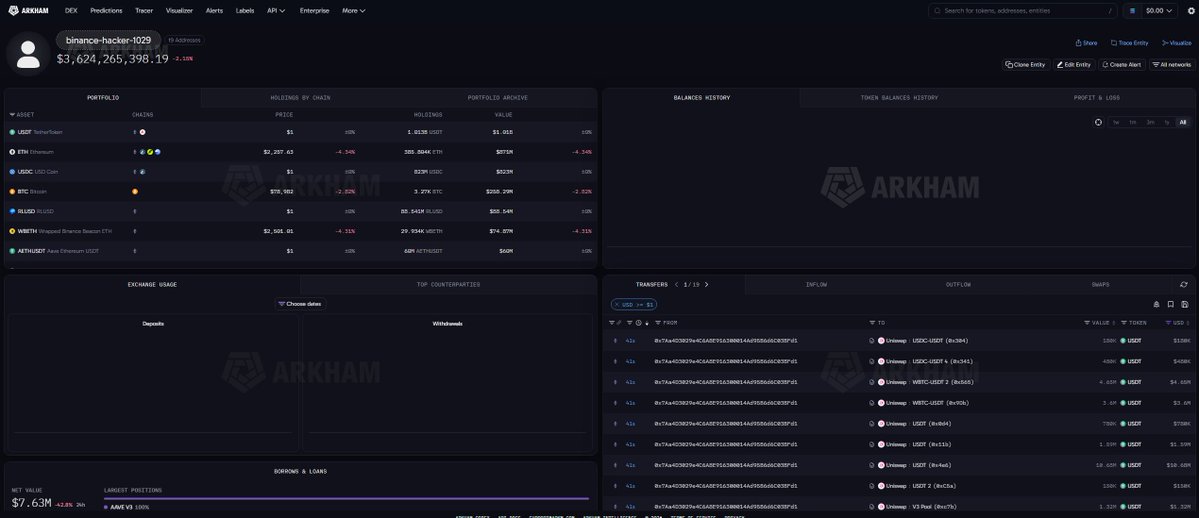
    441291.2K546K
  2. Dark Web Informer@DarkWebInformer
    Movie Fact: In Hackers (1995), Matthew Lillard’s character, “Cereal Killer,” spends nearly the entire film without touching a computer. The only exception is a brief, one-second moment just before his famous “tension breaker” scene at Grand Central Station.
    Download
    12163.4K
  3. Dark Web Informer@DarkWebInformer
    Dark Web Informer
    RT @DarkWebInformer: Major Tor Browser update to v16. Tor Browser 16.0 is a major stable update built on Firefox ESR 153, bringing current Firefox security fixes, redesigned settings, an updated built-in manual, improved Tor connection handling and additional anti-fingerprinting protections. It also updates Tor to 0.4.9.14 and NoScript, while ending support for 32-bit x86 Linux and Android devices and Android versions older than 8.0.
    0707.4K
  4. Dark Web Informer@DarkWebInformer
    This.
    solst/ICE of Astarte @IceSolst
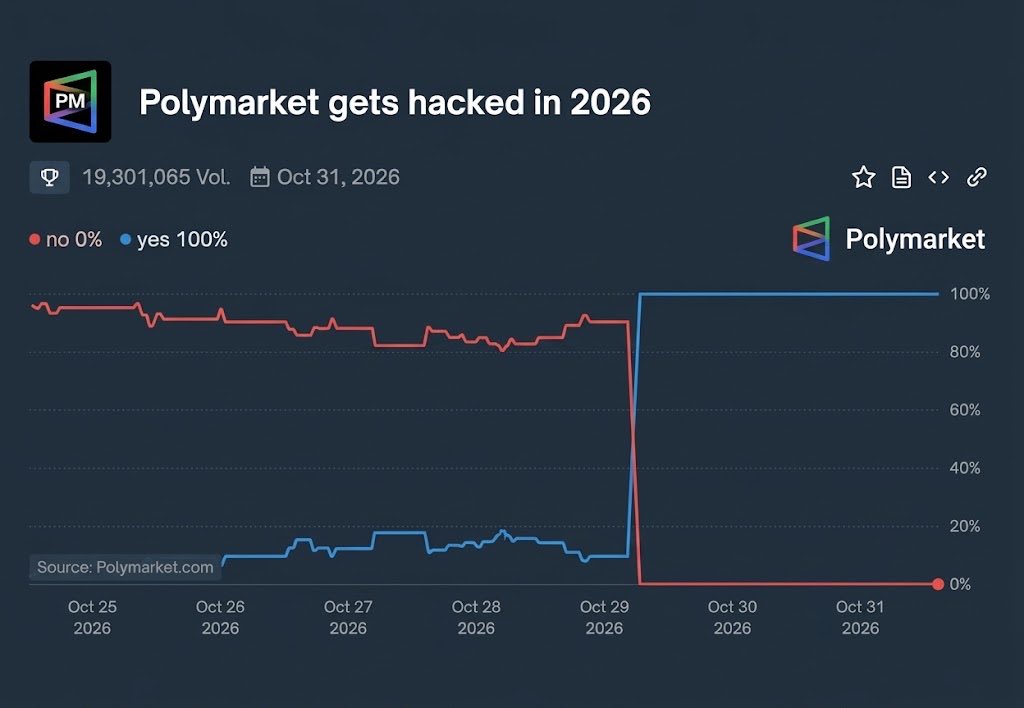
    Btw polymarket and kalshi founders should be in prison
    22716.1K
  5. Dark Web Informer@DarkWebInformer
    What a month.
    Dark Web Informer @DarkWebInformer
    Best Cybersecurity Awareness Month ever. 😭
    7141717.8K
  6. Dark Web Informer@DarkWebInformer
    Best Cybersecurity Awareness Month ever. 😭
    507675.4K85.7K
  7. Dark Web Informer@DarkWebInformer
    $5 Billion being tracked right now. 😬
    Dark Web Informer @DarkWebInformer
    Binance hacker can be tracked on Arkham:
    2412398371.4K
  8. Dark Web Informer@DarkWebInformer
    Binance has made an announcement saying they are looking into the security issue. 👇
    Binance @binance
    Our teams are aware of reports of a potential security issue and are actively investigating. At this stage, we have not confirmed any impact to user funds. Our security teams are reviewing all relevant information with urgency, and we will provide updates through official Binance channels as soon as we have verified information. Users should remain cautious of scams and should not trust unofficial links, messages, or requests for account information.
    22194.9K
  9. Dark Web Informer@DarkWebInformer
    Dark Web Informer
    RT @DarkWebInformer: $3.5 Billion via
    Officer's Notes @officer_secret
    Total hacked is around $3.5B now across multiple chains…
    08018.7K
  10. Officer's Notes✓@officer_secret
    Total hacked is around $3.5B now across multiple chains…
    37160895190K
  11. Dark Web Informer@DarkWebInformer
    Ongoing: Binance possibly drained for $2.77 Billion.
    492052K167K
  12. Dark Web Informer@DarkWebInformer
    ALERT: Binance has possibly been hacked. 👇
    Spreek @spreekaway
    Unconfirmed, but possibly massive binance hack. Entire Binance wallet drained into new EOA. Contract call was funded by Tornado Cash
    44831832.3K
  13. Spreek✓@spreekaway
    Unconfirmed, but possibly massive binance hack. Entire Binance wallet drained into new EOA. Contract call was funded by Tornado Cash
    Download
    6879277.2K2M
  14. Dark Web Informer@DarkWebInformer
    ‼️🇦🇷 Buenos Aires Student Database Leak Claim Lists 1.7 Million Enrollment Records
    110608.3K
  15. Dark Web Informer@DarkWebInformer
    🚨 Critical Linux kernel TCP flaw enables remote root code execution; CVE-2026-98432 A race condition in the Linux kernel’s IPv4 TCP implementation can trigger a use-after-free before application authentication, potentially allowing an unauthenticated remote attacker to leak kernel memory, corrupt memory or crash the system. Anthropic says Claude developed a working exploit that executed attacker-chosen commands as root against Linux servers with a Multipath TCP listener. The exploit took approximately 53 minutes to complete during testing and has not been publicly released. ⠀ • CVSS: 9.8 Critical, according to the Linux kernel CVE team • Affected: Linux kernels beginning with version 4.4 • Fixed: 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.56, 7.2.10 and 7.3 • Attack requirements: Network access, no credentials and no user interaction • Exploitation status: No known attacks in the wild ⠀ Ubuntu and Red Hat Enterprise Linux had not released corrected kernel packages as of October 29. Debian, Oracle Linux, Amazon Linux and SUSE have released fixes for at least some affected branches. Distribution severity ratings differ substantially. Red Hat rates the flaw 5.9 because it considers the race difficult to win and describes denial of service as the most likely practical impact.
    Download
    12915516.7K
  16. Dark Web Informer@DarkWebInformer
    Posts @DarkWebInformer
    Source:
    0012.7K
  17. Dark Web Informer@DarkWebInformer
    Dark Web Informer
    RT @DarkWebInformer: 🚨 Zero-click “SMS of Death” flaw can crash Android phone services A researcher has disclosed an unpatched Android vulnerability that allows a malformed WAP Push SMS to silently crash the process, dropping active calls and temporarily disabling cellular service without any interaction from the victim. The message does not appear in the inbox, and carrier redelivery can repeatedly trigger the crash. The researcher also found that sending multiple messages rapidly could corrupt the SMS dataset, leaving telephony services crashing after every reboot. ⠀ • CVE: None assigned • Attack vector: Remote WAP Push SMS • User interaction: None • Impact: Denial of service, dropped calls and possible persistent loss of telephony • Tested: Pixel 9 and multiple Samsung Galaxy and A-series devices • Patch status: None available • Vendor status: “Won’t Fix” and classified as a non-security issue, according to the disclosure ⠀ The researcher reported the flaw to Google in May and publicly disclosed it on October 29 after the report and subsequent appeals were rejected. There is currently no evidence that the vulnerability is being exploited in the wild.
    031014.3K
  18. Dark Web Informer@DarkWebInformer
    🚨🇩🇴 Edesur Dominicana customer data allegedly leaked, over 500,000 records exposed Edesur Dominicana, an electricity distribution company in the Dominican Republic, has been named in a data leak by the actor "K3RN3L_P4N1C". The dataset reportedly contains over 500,000 records, including customer names, national identification numbers, residential addresses, phone numbers, email addresses, account statuses, and outstanding electricity debts. The actor has published a sample of approximately 1,000 records and is offering additional information through private messages. Claim is currently unverified. 💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it.
    Download
    3197610.9K
  19. Binance@binance
    Our teams are aware of reports of a potential security issue and are actively investigating. At this stage, we have not confirmed any impact to user funds. Our security teams are reviewing all relevant information with urgency, and we will provide updates through official Binance channels as soon as we have verified information. Users should remain cautious of scams and should not trust unofficial links, messages, or requests for account information.
    Download
    2631621K100K