Eric Parizo
@EricParizo
Founder/Chief Analyst, Cernivera Research. Cybersecurity industry analyst, researcher & consultant. Snark warning always in effect.
31 Following731 Followers2.1K Posts
- Eric Parizo@EricParizoThis keynote setup through the business hall? Not good. Borderline dangerous. Definitely unnecessary. Rough start. #bhusa000117
- Eric Parizo@EricParizoA question I'd ask @FBIDirectorKash at his next presser: "The ShinyHunters cybercrime syndicate has now breached 1000s of orgs, extracted 10s of millions in ransom & caused billions in damage over 7.5 years. What is @FBI doing to bring them to justice?"00048
- Eric Parizo@EricParizo.@RSAConference USA is officially bigger than ever: #RSAC2025 final attendance is just under 44k (43,500+), up from 41k attendees in 2024 & topping the previous all-time high of 42,500 in 2019. Also #RSAC2026 will be in calendar Q1, slated for March 23-26 in SF. #RSACRSAC @OneRSAC#RSAC™ Conference Wraps 34th Annual Flagship Event with Many Voices, One Community. Read more:01089

- Eric Parizo@EricParizoAs #RSAC2025 begins, here's a great snapshot of what adversaries are now focused on, and in turn what CISOs should be pivoting to detect & prevent.Florian Roth ⚡️ @cyb3ropsWe’re seeing a clear trend: attackers are bypassing the endpoint entirely. Not just avoiding traditional EDR-monitored systems by pivoting to embedded and edge devices, but now also operating purely in the cloud. No shell, no malware, no persistence on the endpoint. Just an OAuth token and full access to whatever’s in the victim’s Microsoft 365, Google Workspace, or AWS console. It’s a complete inversion of how things used to be. The endpoint, once the weakest link, is now usually the most monitored, most policy-enforced part of the infrastructure. You’ve got EDRs, SIEM integration, automation, threat hunting - the full stack. But attackers don’t need to touch it anymore. Instead, they go after the new soft spots: - Cloud platforms, where logging is limited, expensive, or off by default - Network devices and appliances, which are practically blind spots - obscure OSes, no EDRs, hard to monitor, hard to forensicate. - Embedded systems and IoT junk that no one really knows how to secure, but that sit in critical network paths. Cloud especially is a mess: - Logging tiers cost extra and the good stuff is behind paywalls. - Detection content is lacking, both from vendors and the community. - You don’t get memory dumps or full control like you do on endpoints. - You’re at the mercy of the provider when it comes to visibility and response. And that’s the shift: attackers aren’t hacking computers anymore. They’re hacking trust relationships, identities, and APIs. The whole idea of detection and response needs to evolve with that. Otherwise, we’re securing the hell out of endpoints while attackers happily fish through mailboxes and cloud shares from halfway across the planet.00045
 We’re seeing a clear trend: attackers are bypassing the endpoint entirely. Not just avoiding traditional EDR-monitored systems by pivoting to embedded and edge devices, but now also operating purely in the cloud. No shell, no malware, no persistence on the endpoint. Just an OAuth token and full access to whatever’s in the victim’s Microsoft 365, Google Workspace, or AWS console. It’s a complete inversion of how things used to be. The endpoint, once the weakest link, is now usually the most monitored, most policy-enforced part of the infrastructure. You’ve got EDRs, SIEM integration, automation, threat hunting - the full stack. But attackers don’t need to touch it anymore. Instead, they go after the new soft spots: - Cloud platforms, where logging is limited, expensive, or off by default - Network devices and appliances, which are practically blind spots - obscure OSes, no EDRs, hard to monitor, hard to forensicate. - Embedded systems and IoT junk that no one really knows how to secure, but that sit in critical network paths. Cloud especially is a mess: - Logging tiers cost extra and the good stuff is behind paywalls. - Detection content is lacking, both from vendors and the community. - You don’t get memory dumps or full control like you do on endpoints. - You’re at the mercy of the provider when it comes to visibility and response. And that’s the shift: attackers aren’t hacking computers anymore. They’re hacking trust relationships, identities, and APIs. The whole idea of detection and response needs to evolve with that. Otherwise, we’re securing the hell out of endpoints while attackers happily fish through mailboxes and cloud shares from halfway across the planet.273081.2K197K
- Eric Parizo@EricParizoBest wishes to everyone attending #RSAC 2025 next week. I will be focusing on my new role, but will miss many friends, colleagues, and the buzz of the event. I will *not* miss making lap after lap in and around Moscone on foot!00046
- Eric Parizo@EricParizoOne of the scariest phishing attempts I’ve seen in a long time. Good that Google has agreed to fix the root vulnerability, but in the meantime, be careful.nick.eth @nicksdjohnsonRecently I was targeted by an extremely sophisticated phishing attack, and I want to highlight it here. It exploits a vulnerability in Google's infrastructure, and given their refusal to fix it, we're likely to see it a lot more. Here's the email I got:00037

- Eric Parizo@EricParizoSuper cute marketing/training effort coming up next week from @immersivelabs "Christmas Tree-Son" Virtual Crisis Simulation: "Immerse yourself in a unique and engaging crisis scenario set against the backdrop of the North Pole."00044
- Eric Parizo@EricParizoImportant new primary research: The app for your internet-connected litter box should NOT require your wifi network password for connectivity. (Manufacturers should ensure the device can connect directly and securely w/o an app. Software is always the weakest link!) #IoTsecurity00046
- Eric Parizo@EricParizoGreat quote from special guest Venus Williams, borrowed from Billie Jean King: “Pressure is a privilege… it means that you’re doing things and going places.” #opentextworld
 002104
- Eric Parizo@EricParizoBarrenechea commits @OpenText to masking all of its data and eliminating passwords in favor of biometric authentication over the next two years. #OpenTextWorld
 Eric Parizo @EricParizoBarrenechea on integration: "With enterprise security you need to compose a solution. No company can do it all. All the (technology) partners in your ecosystem throw off security events, so you have to do it in a composable way, connecting disconnected islands." #OpenTextWorld001121
- Eric Parizo@EricParizoBarrenechea on integration: "With enterprise security you need to compose a solution. No company can do it all. All the (technology) partners in your ecosystem throw off security events, so you have to do it in a composable way, connecting disconnected islands." #OpenTextWorldEric Parizo @EricParizoBarrenechea on @OpenText security strategy: "We’re here to make security as important as anything we do... We think it’s no longer human vs machine, it’s machine vs machine." #OpenTextWorld000191
- Eric Parizo@EricParizoBarrenechea on @OpenText security strategy: "We’re here to make security as important as anything we do... We think it’s no longer human vs machine, it’s machine vs machine." #OpenTextWorldEric Parizo @EricParizoIt is notable that security is the dominant theme in the @OpenText multicloud integration strategy. #opentextworld000129
- Eric Parizo@EricParizoIt is notable that security is the dominant theme in the @OpenText multicloud integration strategy. #opentextworld
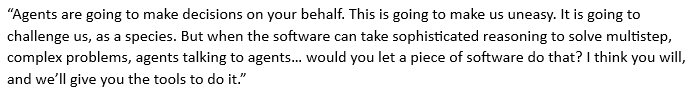
 Eric Parizo @EricParizoThe full quote for accuracy (had to cut too much for the X word limit):00097
- Eric Parizo@EricParizoThe full quote for accuracy (had to cut too much for the X word limit):
 Eric Parizo @EricParizoBarrenechea on AI: “Agents are going to make decisions on your behalf. This is going to make us uneasy... would you let a piece of software do that? I think you will, and we’ll give you the tools to do it.” #OpenTextWorld000217
- Eric Parizo@EricParizoBarrenechea on AI: “Agents are going to make decisions on your behalf. This is going to make us uneasy... would you let a piece of software do that? I think you will, and we’ll give you the tools to do it.” #OpenTextWorldEric Parizo @EricParizoBarrenechea: "We’re going to continue to extoll that security is job one… built all the way into the software, and it needs to work across multicloud." #OpenTextWorld00077
- Eric Parizo@EricParizoBarrenechea: "We’re going to continue to extoll that security is job one… built all the way into the software, and it needs to work across multicloud." #OpenTextWorldEric Parizo @EricParizoI really like how @OpenText CEO/CTO Mark Barrenechea highlights the value of #AI in the enterprise in his opening keynote: "Every organization has two proprietary gifts: talent and data... AI transforms the value of both of those gifts." #OpenTextWorld00087
- Eric Parizo@EricParizoI really like how @OpenText CEO/CTO Mark Barrenechea highlights the value of #AI in the enterprise in his opening keynote: "Every organization has two proprietary gifts: talent and data... AI transforms the value of both of those gifts." #OpenTextWorldEric Parizo @EricParizoPleased to spend time with @OpenText & @OpenTextSec this week at #opentextworld Key Qs: Is this *really* a security company vs an information management co w/ security? Has the Micro Focus deal/integration been a force multiplier? @OmdiaCyber000101
- Eric Parizo@EricParizoPleased to spend time with @OpenText & @OpenTextSec this week at #opentextworld Key Qs: Is this *really* a security company vs an information management co w/ security? Has the Micro Focus deal/integration been a force multiplier? @OmdiaCyber
 012108
- Show more posts