FuzzingLabs✓

@FuzzingLabs

Research-oriented Cybersecurity startup specializing in #fuzzing, Vulnerability Research & Offensive security on Mobile, Browser, AI/LLM, Network & Blockchain.

3.7K Following9.1K Followers831 Posts
  1. FuzzingLabs✓@FuzzingLabs
    💥 We’ve just raised €1M in pre-seed funding to accelerate the development of FuzzForge. When I started FuzzingLabs, everything was bootstrapped: our audits, our trainings, our R&D. No investors, no funding. Just a passionate team obsessed with offensive security and the belief that we could build something different. Three years later, we’re 30 and we are now entering a new chapter. This funding will allow us to: - accelerate the open-source development of FuzzForge, - build its marketplace of agents and workflows, - and expand the SaaS version to automate vulnerability research at scale. A huge thanks to @class_lambda and @ergodicgroup for their strategic support and trust in our vision: --> making offensive security more intelligent, collaborative, and automated. FuzzForge is already open source and under active development. You can check it out here: 🔗
    Download
    54026521.3K
  2. FuzzingLabs✓@FuzzingLabs
    FuzzingLabs
    RT @Pat_Ventuzelo: Project Zero (@5aelo) pitted an LLM agent (BigSleep) against a fuzzer (Fuzzilli) on V8: 45 vs 37 vulns, ~25% overlap. -> Bugs hard for fuzzers are hard for agents too. -> AI won't kill fuzzing. My take long term: Agents that drive fuzzers will win.
    012079
  3. FuzzingLabs✓@FuzzingLabs
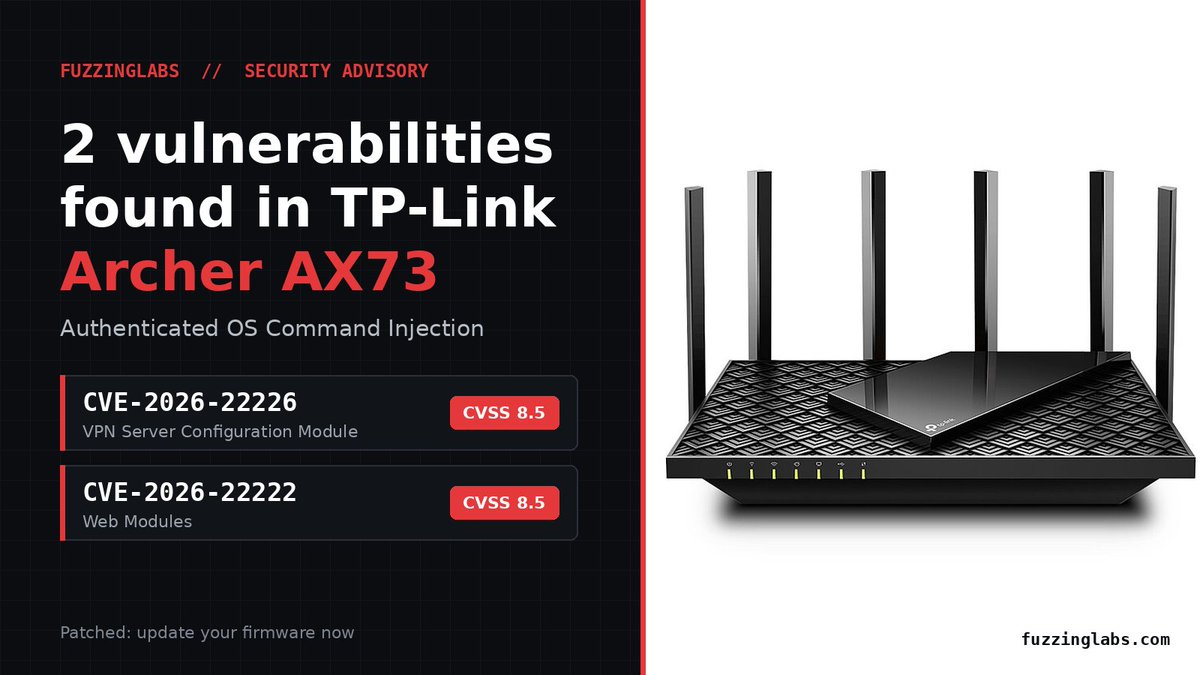
    🔓 2 new CVEs in the TP-Link Archer AX73 by @FuzzingLabs CVE-2026-22226: OS command injection in VPN server config CVE-2026-22222: OS command injection in web modules CVSS 8.5 High, now patched. Update your firmware.
    Download
    0416958
  4. FuzzingLabs✓@FuzzingLabs
    First attempt, first win. 🎯 Congrats to @LucasVanHaaren and @0xNaSu for popping the Brother MFC-L8970CDW with a single 0-day. Thanks @thezdi for a great event! #Pwn2Own
    TrendAI Zero Day Initiative @thezdi
    Brother what? Brother exploited! Lucas Van Haaren (vhash, @LucasVanHaaren) and Hugo Leclercq (0xnasu) of FuzzingLabs (@FuzzingLabs) exploited Brother MFC-L8970CDW with a single zero-day earning $20,000 and 2 Master of Pwn points #Pwn2Own
    00191K
  5. FuzzingLabs✓@FuzzingLabs
    Really proud of the team!!!
    TrendAI Zero Day Initiative @thezdi
    Sweet! Lucas Van Haaren (@LucasVanHaaren) and Hugo Leclercq (@0xNaSu) of FuzzingLabs (@FuzzingLabs) needed little time to exploit the Brother MFC-L8970CDW printer. They head off to the disclosure room to provide the details to us and the vendor. #Pwn2Own
    00141.4K
  6. FuzzingLabs✓@FuzzingLabs
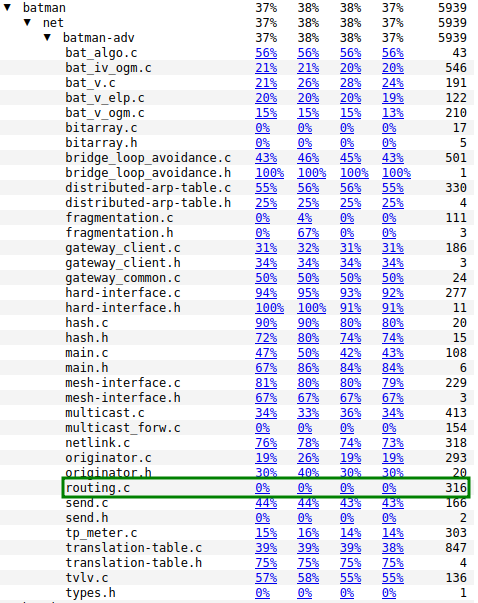
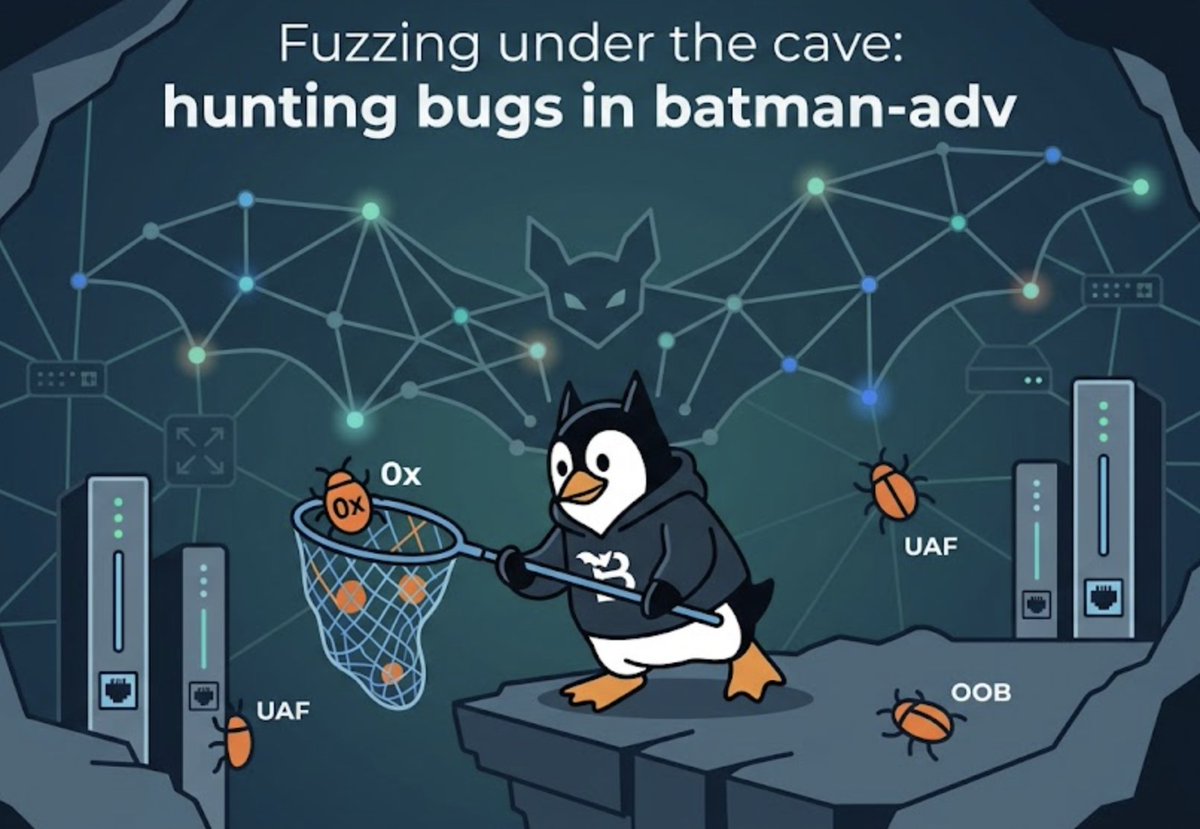
    A file in the Linux kernel with 0% Syzbot coverage is an invitation... That's how our team at @fuzzinglabs ended up looking in batman-adv, the mesh networking subsystem (B.A.T.M.A.N. = Better Approach To Mobile Ad hoc Networking). Nobody had ever fuzzed the Linux kernel's mesh networking subsystem from the frame reception side. So we did. Three bugs, one patch now merged in mainline. 🧵
    Download
    17584K
  7. FuzzingLabs✓@FuzzingLabs
    Posts @FuzzingLabs
    With the harness up, the first crash came quickly. KASAN report in batadv_iv_ogm_send_to_if, the function that splits aggregated OGMs out of a forward packet.
    Download
    100208
  8. FuzzingLabs✓@FuzzingLabs
    Posts @FuzzingLabs
    Takeaway: public coverage dashboards are a map of where the bugs still are. The gaps are the target list. Full write-up by Alexis & Lyes, crash traces, the Syzlang grammar, the kernel patch:
    Download
    025539
  9. FuzzingLabs✓@FuzzingLabs
    FuzzingLabs is joining #SEAstart, @Gican_InduNav 's accelerator for the French naval industry. We break naval systems before attackers do! We already found 6 CVEs across the maritime navigation stack (GNSS/RTK, AIS, NMEA 2000), several with no auth required. Looking for naval design partners. Let's talk. #Cybersecurity #NavalDefense #SEAstart
    Download
    03213.5K
  10. FuzzingLabs✓@FuzzingLabs
    Cryptography on embedded devices: picking AES vs Ascon is the easy part. The hard part? Where keys live, whether the chip has any trustworthy RNG, if it can persist a nonce counter, and which accelerator you're forced to use. Our 101 guide 👇
    25191.8K
  11. FuzzingLabs✓@FuzzingLabs
    FuzzingLabs
    RT @POC_Crew: 🛠️ [POC2026] TRAINING Apple’s Swift - RE, VR and AI by Atlan Pinabel & Nabih Benazzouz (@FuzzingLabs) 📅 Nov 9-11 (3 days) 📍 The Westin Seoul Parnas, Korea Detail 👉 #POC2026
    020127
  12. FuzzingLabs✓@FuzzingLabs
    Our CEO @Pat_Ventuzelo opened @_leHACK_ 2026, France's biggest hacking con, with his keynote: "No need to be a Mythos to do offensive security." You don't need a classified frontier model. The moat moved from model access to the harness and the building blocks are already in your hands. Slides 👇 You don't have to be a Mythos. You just have to keep building.
    Download
    06252.4K
  13. FuzzingLabs✓@FuzzingLabs
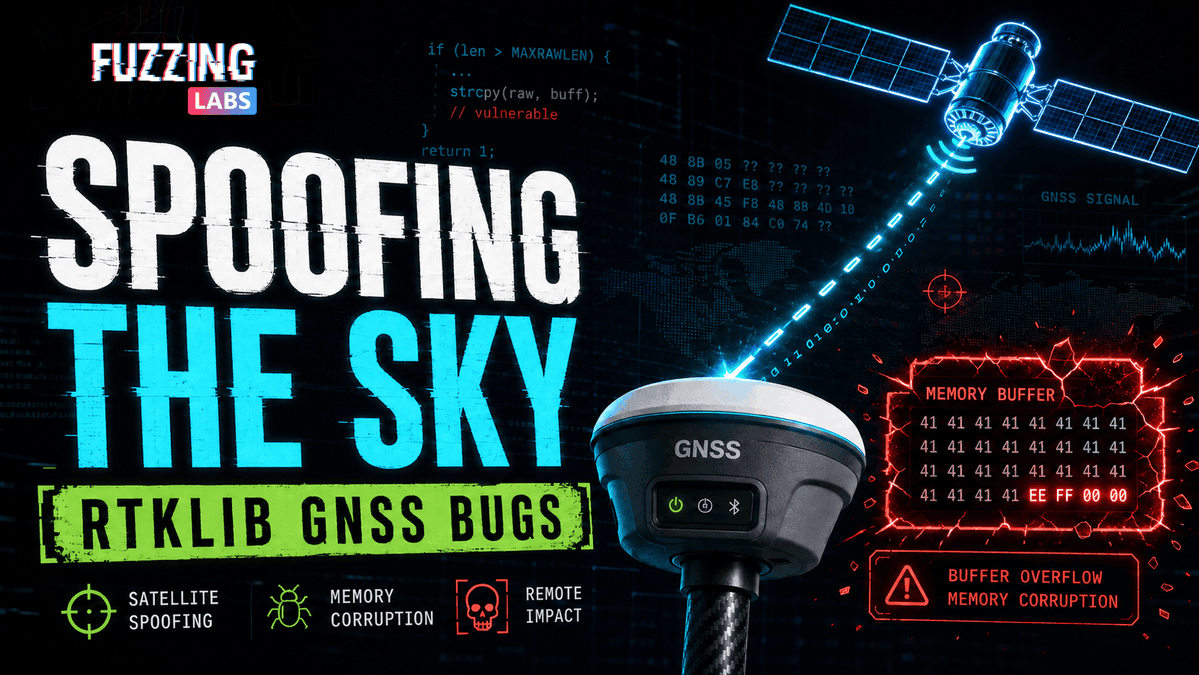
    🛰️ We broke RTKLIB, the open-source engine behind centimeter-accurate GPS in drones, boats, autonomous vehicles & survey networks. 4 memory-corruption bugs in its RTCM3 / RINEX decoders. No auth. Reachable from a single crafted correction stream or one booby-trapped file. 1 OOB write + 3 OOB reads. A rogue NTRIP caster or a MITM'd stream is enough to crash or corrupt the positioning stack of a machine that moves itself. Reported upstream, coordinated disclosure (RTKLIB #796–799). Full write-up 👇
    Download
    013282.5K
  14. FuzzingLabs✓@FuzzingLabs
    Excited to be there end of the year !! Looking forward to show to the community what we have build with fuzzforge, our ai agents orchestration platform for embedded security !
    hardwear.io @hardwear_io
    Excited to welcome @FuzzingLabs as an Exhibit Sponsor for Netherlands 2026. 🚀 Looking forward to having their team and research expertise. Registrations & CFPs now live: #HardwearNL2026 #ExhibitSponsor
    1151.6K
  15. FuzzingLabs✓@FuzzingLabs
    🚀 FuzzingLabs has joined the OVHcloud Startup Program. This will help us scale #FuzzForge, our platform orchestrating specialized AI agents for continuous offensive validation on firmware, binaries, and embedded systems, on sovereign European cloud infrastructure. Aligned with what our customers in defense, industrial, and critical sectors need: sovereign, European & CRA-ready by design. Thanks to the OVHcloud team for the support. #Cybersecurity #AI #SovereignCloud #OVHcloud #FuzzForge
    Download
    03161.3K
  16. FuzzingLabs✓@FuzzingLabs
    🚀 FuzzingLabs is now part of the @NVIDIA Inception Program! We're building FuzzForge, our AI agents platform leveraging GPU infrastructure for Continuous Offensive Validation on firmware, binaries & embedded systems. Scaling fine-tuned Qwen, Gemma & DeepSeek for offensive security. 🔥 #NVIDIAInception #AI #Cybersecurity
    Download
    03412.6K
  17. FuzzingLabs✓@FuzzingLabs
    We have been selected to join the Cyber Defense Factory, a program run by the French Ministry of Armed Forces. This is a concrete validation of what we've been building with FuzzForge and a chance to test it on defense-grade use cases, working directly with DGA teams. Six months of hands-on work, real targets, real feedback from people who know exactly what vulnerability detection security tools need to deliver. Thank you to @DGA - Direction générale de l'armement, COMCYBER and the Agence de l'innovation de défense for making this possible. Excited for what's ahead. 🔥
    Download
    09293.1K
  18. Show more posts