Securance

@SCsecurance

Securance is an IT audit and cybersecurity firm with more than 20 years of experience helping clients improve security, compliance, and risk management.

1.3K Following1.1K Followers2.3K Posts
  1. Securance@SCsecurance
    Your backup admin account is probably one of the most privileged and least reviewed accounts you have. Ransomware crews know it, and they go after it first. If your recovery plan hasn’t been tested against that, it’s a document, not a plan.
    0009
  2. Securance@SCsecurance
    Internal audit at a public university knew its biggest IT risk sat in college-managed networks and endpoints. Convincing the colleges was the hard part. An independent assessment moved the conversation from politics to evidence. #HigherEd #ITAudit
    0003
  3. Securance@SCsecurance
    Volt Typhoon is targeting universities with military ties, utilities, and the MSPs that manage them. The way in: routers, firewalls, and network management platforms, with logs wiped on exit. Edge devices belong in your assessment scope.
    00010
  4. Securance@SCsecurance
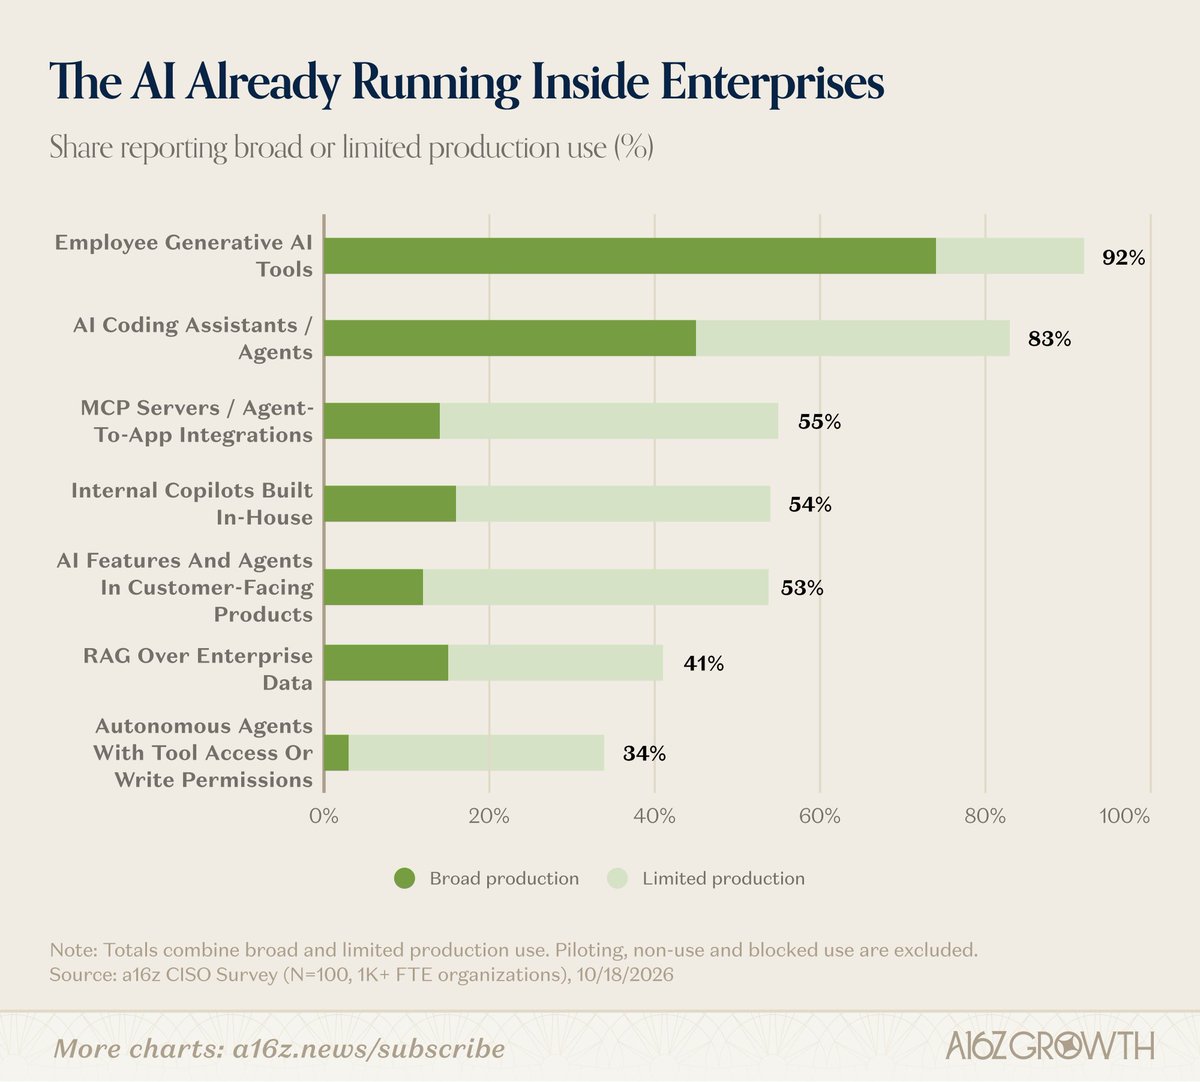
    34% already have autonomous agents with write permissions in production. Before buying more AI security tools, answer the basic question: which agents are running, what can they change, and who approved that access?
    a16z @a16z
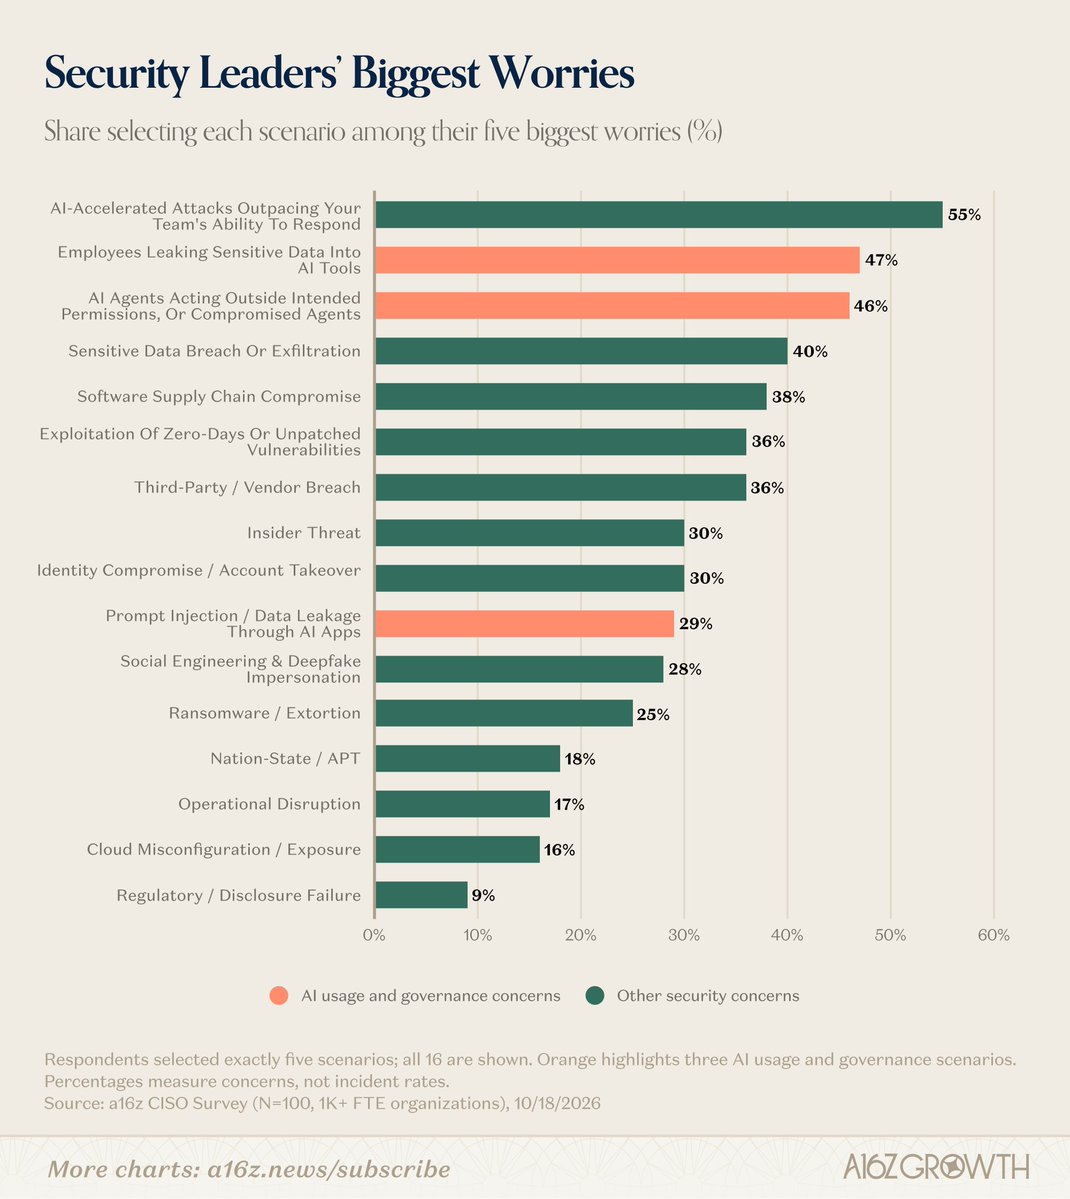
    AI is already running across the enterprise, and securing it is now one of CISOs' biggest concerns Already in production at their companies: - Employee generative AI tools (92%) - AI coding assistants or agents (83%) - MCPs or agent-to-app integrations (55%) - Autonomous agents with tool access or write permissions (34%) Their biggest concerns: - AI attacks outpacing their team (55%) - Employees leaking data into AI tools (47%) - AI agents exceeding permissions or getting compromised (46%) From a16z's @OwenColby and @steph_zhang, breaking down a survey of 100 CISOs at companies with 1,000+ employees:
    00010
  5. a16z@a16z
    AI is already running across the enterprise, and securing it is now one of CISOs' biggest concerns Already in production at their companies: - Employee generative AI tools (92%) - AI coding assistants or agents (83%) - MCPs or agent-to-app integrations (55%) - Autonomous agents with tool access or write permissions (34%) Their biggest concerns: - AI attacks outpacing their team (55%) - Employees leaking data into AI tools (47%) - AI agents exceeding permissions or getting compromised (46%) From a16z's @OwenColby and @steph_zhang, breaking down a survey of 100 CISOs at companies with 1,000+ employees:
    Download
    643430935K
  6. Securance@SCsecurance
    ESXi hosts keep showing up in ransomware playbooks for a simple reason: one compromised hypervisor can take down dozens of VMs at once. If your patch window for KEV entries is measured in weeks, this is a good week to shorten it.
    CISA Cyber @CISACyber
    🛡️We added Broadcom VMWare ESX vulnerability CVE-2026-41709 & Linux Kernel vulnerability CVE-2026-46300 to our KEV Catalog. Visit & apply mitigations to protect your org. #Cybersecurity #InfoSec
    00017
  7. CISA Cyber@CISACyber
    🛡️We added Broadcom VMWare ESX vulnerability CVE-2026-41709 & Linux Kernel vulnerability CVE-2026-46300 to our KEV Catalog. Visit & apply mitigations to protect your org. #Cybersecurity #InfoSec
    Download
    134413819.8K
  8. Securance@SCsecurance
    Your incident response plan is a hypothesis until you test it. Securance founder and president Paul Ashe on why most IR plans have never faced a realistic ransomware scenario, and what we’ve learned running tabletop exercises across industries:
    00017
  9. Securance@SCsecurance
    Who has authority to set a ransom ceiling? Many IR plans assume someone does. In a tabletop with a regional food and beverage manufacturer, that was one of three questions the plan had left to assumption. Each now has a written answer and a named owner.
    00012
  10. Securance@SCsecurance
    NIST’s initial design tenets for agent identity are worth reading in full. The one closest to an auditor’s heart is #10, Immutable Evidence. If an agent can touch its own logs, you don’t have an audit trail. You have a suggestion.
    Cybersecurity @ NIST @NISTcyber
    🎉NEW @NIST BLOG! Design Tenets for Agent Identity Management Systems We’ve defined an initial set of “Design Tenets” for agentic identity, authentication & authorization
    00011
  11. Cybersecurity @ NIST@NISTcyber
    🎉NEW @NIST BLOG! Design Tenets for Agent Identity Management Systems We’ve defined an initial set of “Design Tenets” for agentic identity, authentication & authorization
    Download
    85434.2K
  12. Securance@SCsecurance
    A scanner tells you what might be vulnerable. A penetration test shows you what's actually exploitable, and the exact path an attacker would take to get in. Here's how we test networks from the outside in: #PenetrationTesting #CSaaS
    00036
  13. Securance@SCsecurance
    Michigan's state agencies had about 370 disaster recovery plans. 229 had no recorded test date. Ransomware crews go after the backups first. Untested plans fail the night they're needed. Free white paper, no form: #Ransomware #DisasterRecovery
    00021
  14. Securance@SCsecurance
    Who can still log in to your critical applications after someone leaves or changes roles? Our application provisioning review checks how access is granted, changed, and removed, before the gaps become audit findings. #AccessManagement Watch:
    00022
  15. Securance@SCsecurance
    Worth a look if you run PHP anywhere, including apps a vendor hosts for you. First step SANS recommends: get PHP management interfaces off the internet.
    SANS Institute @SANSInstitute
    Patches for the 2 critical PHP vulnerabilities are out. If you can’t deploy them yet, @mosesrenegade, Senior Instructor at SANS Institute walks through temporary measures, starting with getting PHP management interfaces off the internet. Recording of the emergency livestream here: #PHP #Vulnerabilites
    00018
  16. SANS Institute✓@SANSInstitute
    Patches for the 2 critical PHP vulnerabilities are out. If you can’t deploy them yet, @mosesrenegade, Senior Instructor at SANS Institute walks through temporary measures, starting with getting PHP management interfaces off the internet. Recording of the emergency livestream here: #PHP #Vulnerabilites
    Download
    1151.8K
  17. Securance@SCsecurance
    One compromised login. One ETS file transfer site. About four months of copying California student records before anyone noticed. Transfer monitoring often confirms files arrived, not who took them. Questions to ask about your own exchange points:
    00027
  18. Securance@SCsecurance
    Who has admin rights to your environment right now? If the answer is “I’m not sure,” that’s the gap. A privileged access review finds stale accounts, former employees who still have access, and admins with more than they need. #CSaaS #AccessManagement
    00018
  19. Securance@SCsecurance
    Most organizations need the same cybersecurity assessments every year, then buy them one at a time from different vendors. CSaaS bundles five into one annual program: same team for three years, one price, no starting from scratch. #CSaaS #Cybersecurity
    00027
  20. Securance@SCsecurance
    Three ways to get ready for ransomware: a readiness assessment, an executive tabletop, or living through an attack. Our new white paper, Tested, Not Just Written, follows one real engagement start to finish. Free, no form. #Ransomware #IncidentResponse
    00039
  21. Securance@SCsecurance
    600+ victims across critical infrastructure since 2024. CISA’s SafePay advisory doesn’t stop at patching and MFA. It says test: run your defenses against SafePay’s actual techniques and test your restores, since they wipe network-attached backups. Written isn’t ready.
    CISA Cyber @CISACyber
    SafePay ransomware has affected 600+ #CriticalInfrastructure orgs since 2024. Read our new advisory w/@FBI @SecretService & partners for IOCs + mitigations, including: patch edge devices, limit admin access & enforce multi-factor authentication 👉
    00027
  22. CISA Cyber@CISACyber
    SafePay ransomware has affected 600+ #CriticalInfrastructure orgs since 2024. Read our new advisory w/@FBI @SecretService & partners for IOCs + mitigations, including: patch edge devices, limit admin access & enforce multi-factor authentication 👉
    Download
    716349.1K
  23. Securance@SCsecurance
    Who clicks the phishing email, and what could they reach if they did? Those answers usually sit in two reports from two vendors who never compared notes. CSaaS runs both, plus three more assessments, with one team each year: #Phishing #Cybersecurity
    00141
  24. Show more posts