Michael Ford✓

@fanquake

software maintainer

  • Joined
501 Following8K Followers4.9K Posts
  1. Michael Ford✓@fanquake
    Fully-static, reproducible, release binaries for Bitcoin Core, have been a long-time goal of mine, and we are getting are closer to making them a reality. I've produced test binaries from a PR of mine (#25573), and am looking for feedback, questions, and hopefully testing on various systems or obscure platforms.
    72210413K
  2. Michael Ford✓@fanquake
    After a drawn out 32.x release cycle, we’ve shipped 32.1. v32.0 was tagged, but not fully announced/released, and after this last-minute discovery: we decided to ship v32.1, which fixes this bug, along with others (below) and includes other minor backports.
    Bitcoin Core Project @bitcoincoreorg
    Bitcoin Core v32.1 was released! It is available from: Release notes:
    219572.9K
  3. Bitcoin Core Project✓@bitcoincoreorg
    Bitcoin Core v32.1 was released! It is available from: Release notes:
    177519916.1K
  4. Michael Ford✓@fanquake
    Posts @fanquake
    105202
  5. Michael Ford✓@fanquake
    Posts @fanquake
    Today we also shipped v31.2, v30.4 and v29.5. Which include fixes for all 3 issues, and other minor changes. You can download the latest available version of Bitcoin Core here:
    102145
  6. Michael Ford✓@fanquake
    Could be us
    Tel @telmudic
    statically linked, self-contained software applications rn
    1112879
  7. Tel@telmudic
    statically linked, self-contained software applications rn
    Download
    251553.9K61.3K
  8. Michael Ford✓@fanquake
    > Bitcoin Core has spent more than a century of CPU time fuzzing individual functions and critical components (though oss-fuzz, Fuzzor, bitcoinfuzz and individual contributors), and decades of CPU time simulating small networks of full nodes under test (Antithesis, Fuzzamoto). I can’t establish causality from this alone, but my strong suspicion is that the sustained testing effort is an important reason these projects have become so robust.
    Niklas Gögge @dergoegge
    I wrote a blog post on the recent exploits in the Bitcoin ecosystem, how Bitcoin Core is holding up, and how I think the community can get ahead of the models:
    42211418.7K
  9. Niklas Gögge✓@dergoegge
    I wrote a blog post on the recent exploits in the Bitcoin ecosystem, how Bitcoin Core is holding up, and how I think the community can get ahead of the models:
    44516061.4K
  10. Michael Ford✓@fanquake
    Michael Ford
    RT @n1ckler: gpg --verify SHA256SUMS.asc is easily bypassable for detached signatures. The correct command requires the data file: gpg --verify SHA256SUMS.asc SHA256SUMS This appears to be a common mistake. Without the second argument, gpg succeeds even if the .asc file contains an arbitrary embedded message rather than signing the actual SHA256SUMS file. It prints a warning, but it's easily missed in gpg's output. The gpg manpage explicitly discourages the single-argument form, keeping it only for backward compatibility. I actually keep a list of gpg pitfalls. This is number 8. Mehdi Kerimov reported this in nix-bitcoin's self-updater via @nixbitcoinorg's bounty program. We had originally followed verification instructions, which had the same issue and have since been fixed. That this sat unnoticed on @bitcoincoreorg since 2018 shows just how little-known this footgun is. It's unlikely bad signatures were ever published at scale, as anyone noticing the warning or using the two-argument command would have caught it immediately.
    029041
  11. Michael Ford✓@fanquake
    More progress being made by @remix7531 on the libsecp256k1 Schnorr Signature (BIP 340) formal verification front:
    Download
    412382.3K
  12. Michael Ford✓@fanquake
    Posts @fanquake
    Also see:
    016314
  13. Michael Ford✓@fanquake
    Hopefully it’ll only take one round of trying closed source “security through obscurity”, to convince everyone that this is (certainly nowadays) mostly pointless/confusing, and undermines the whole “don’t trust, verify” ethos. The way forward is writing robust, open source code.
    Nirvati @getnirvati
    We've published a blog post on the dangers of what @BtcpayServer, @Core_LN, and probably other maintainers are doing with security at the moment:
    17405.7K
  14. Nirvati@getnirvati
    We've published a blog post on the dangers of what @BtcpayServer, @Core_LN, and probably other maintainers are doing with security at the moment:
    02169.1K
  15. Michael Ford✓@fanquake
    Reproducible builds give you a source code -> binary mapping. Without this, any open source project needs to pick a single “trusted” person to produce binaries; where no one else can even double check that person compiled the source code they claimed to have compiled (given no reproducibility). So even if you don’t trust the contents of a binary, reproducible builds still solve the problem of a project deciding which binary to make available to end users, given its source code.
    Samson Mow @Excellion
    Given the cost and difficulty, I’m not sure this is the way forward, especially with AI. If you really think about it, all reproducible builds did was move the locus of trust (for most people, except those that verified themselves, which are few and far between). Developer writes code and makes it reproducible. Another guy creates the reproducible builds and posts that they reproduced it. User trusts the other guy blindly. What would actually be far better is you point your agent to a codebase and say “scan for vulns and build it for me.” That would be far more practical for everyone.
    213504.5K
  16. Samson Mow✓@Excellion
    Posts @Excellion
    Given the cost and difficulty, I’m not sure this is the way forward, especially with AI. If you really think about it, all reproducible builds did was move the locus of trust (for most people, except those that verified themselves, which are few and far between). Developer writes code and makes it reproducible. Another guy creates the reproducible builds and posts that they reproduced it. User trusts the other guy blindly. What would actually be far better is you point your agent to a codebase and say “scan for vulns and build it for me.” That would be far more practical for everyone.
    70226.9K
  17. Michael Ford✓@fanquake
    Michael Ford
    RT @bitcoinoptech: Michael Ford (@fanquake) and Martin Zumsande (@Lightlike1) joined Optech to discuss Newsletter #418: News ● Conditional message transfer contract to solve jamming (33:07) ● Static Bitcoin Core binaries available for testing (1:19) ● Replacing per-peer transaction rate-limiting with global rate limits (18:44) Releases and release candidates ● BTCPay Server 2.4.2 (43:16) ● LND v0.21.2-beta (45:45) ● LND v0.20.3-beta (45:45) Notable code and documentation changes ● Bitcoin Core #35493 (48:10) ● Core Lightning #9150 (50:57) ● BIPs #2248 (54:13) ● BIPs #2225 (56:07) ● Eclair #3346 (58:50) ● Eclair #3341 (1:02:22) ● LND #11019 (1:05:18) ● LND #11023 (1:09:03) ● Libsecp256k1 #1904 (1:11:49) ● HWI #839 (1:13:58)
    07045
  18. Michael Ford✓@fanquake
    Michael Ford
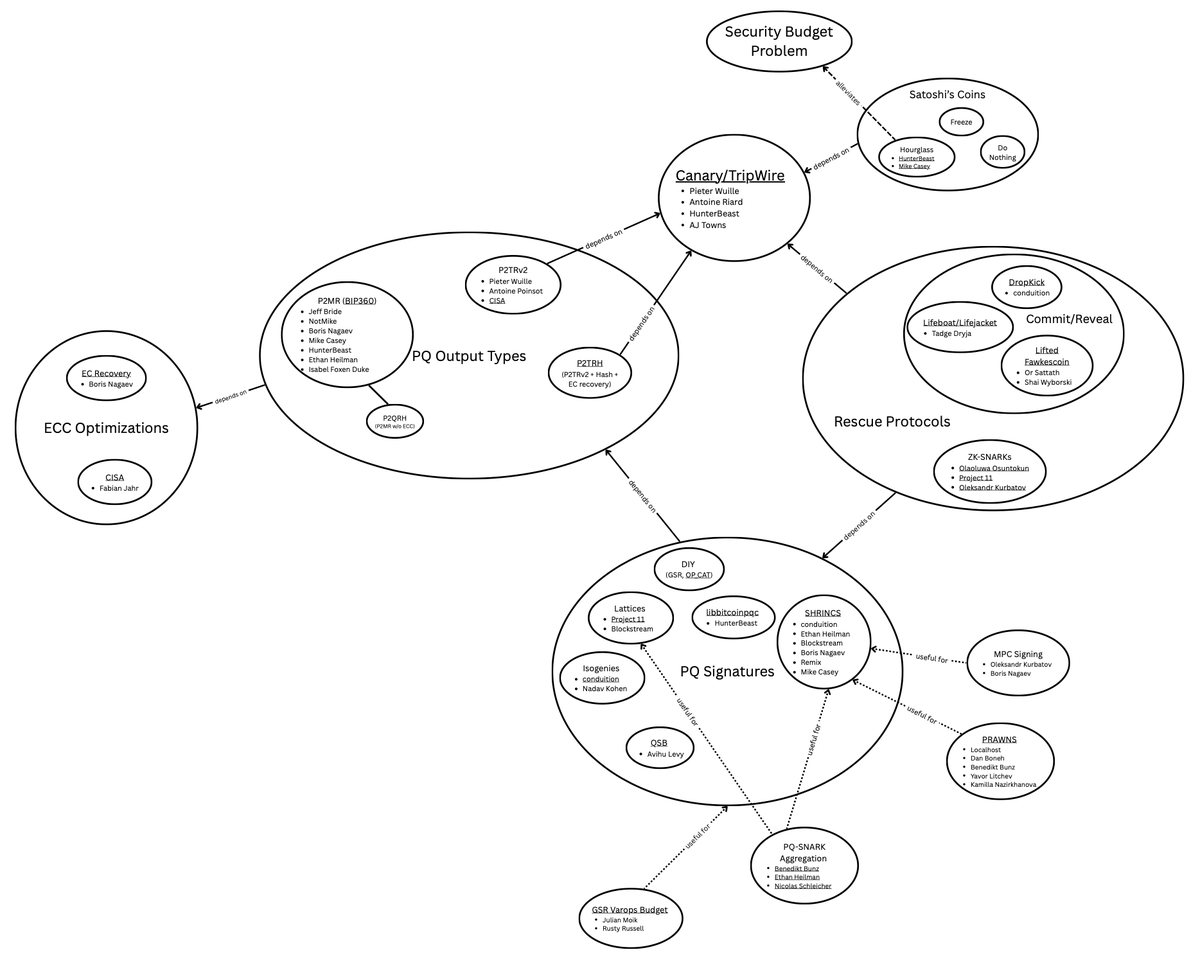
    RT @bitschmidty: Bitcoin post-quantum R&D tldr If you want to get up to speed on the last ~year of Bitcoin post-quantum research and development, the first 20 minutes of @conduition_io's presentation on Brink’s engineering call is a great primer. Every major proposal and how they all fit together.
    Brink @bitcoinbrink
    Brink grantee @conduition_io presented on the state of post-quantum Bitcoin research: - Post-quantum output types - Quantum canaries and tripwires - Freezing, ignoring, or rate-limiting Satoshi-era coins - Rescue protocols - Hash-based, lattice, isogeny signature schemes - Q&A
    020044
  19. Brink@bitcoinbrink
    Brink grantee @conduition_io presented on the state of post-quantum Bitcoin research: - Post-quantum output types - Quantum canaries and tripwires - Freezing, ignoring, or rate-limiting Satoshi-era coins - Rescue protocols - Hash-based, lattice, isogeny signature schemes - Q&A
    Download
    4166313.2K
  20. Michael Ford✓@fanquake
    Michael Ford
    RT @bitschmidty: When you download Bitcoin Core today, the binary doesn't contain everything your node runs. It still loads the C library (glibc and friends) from your operating system which means there are version requirements, behavior that can vary from machine to machine, and code that your node executes that isn’t covered by reproducible builds. New static test builds pack it all into one deterministic Bitcoin Core binary. @fanquake is asking node runners to test out these new static binaries and report results.
    051039
  21. Michael Ford✓@fanquake
    No third-party code. No runtime dependencies.
    ReproducibilityMatters @sedited_
    Cash on the internet. No auto-updates.
    16302.6K
  22. Michael Ford✓@fanquake
    Getting good feedback so far; yet to break anybody’s usage of bitcoind
    Bitcoin Optech @bitcoinoptech
    Michael Ford (@fanquake) posted to the Bitcoin-Dev mailing list announcing test builds of static Bitcoin Core release binaries produced using the project’s existing Guix infrastructure...
    12272.3K
  23. Bitcoin Optech✓@bitcoinoptech
    Posts @bitcoinoptech
    Michael Ford (@fanquake) posted to the Bitcoin-Dev mailing list announcing test builds of static Bitcoin Core release binaries produced using the project’s existing Guix infrastructure...
    1271.8K
  24. Michael Ford✓@fanquake
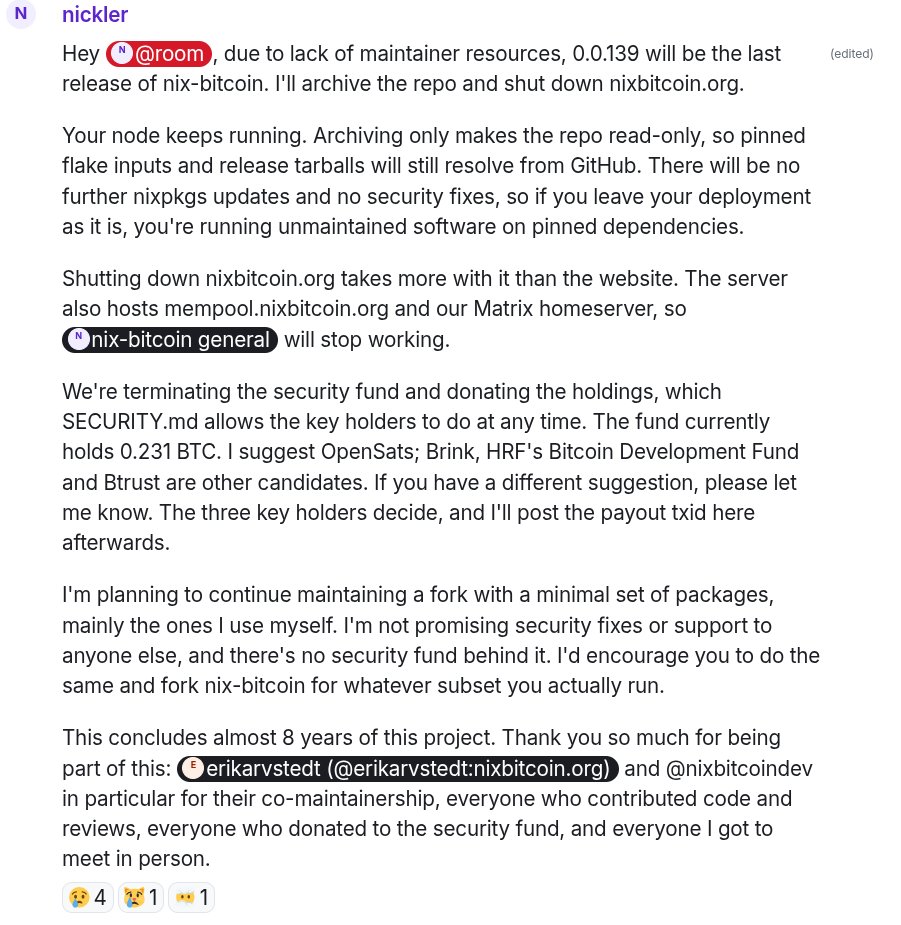
    Who wants to be maintainer
    nix-bitcoin @nixbitcoinorg
    0.0.139 is the final version of nix-bitcoin. Really enjoyed these 8 years developing Bitcoin infrastructure on NixOS, very grateful for your support. The code is there, so fork it.
    18243.2K
  25. nix-bitcoin@nixbitcoinorg
    0.0.139 is the final version of nix-bitcoin. Really enjoyed these 8 years developing Bitcoin infrastructure on NixOS, very grateful for your support. The code is there, so fork it.
    Download
    6157420.9K
  26. Show more posts