Posts avec #https

#https

Les posts publics sur X qui utilisent #https.

Hashtags associés

  1. pilvar (Philippe Dourassov)✓@pilvar222
    We made a website to check if your http client is vulnerable to CVE-2026-111497 (Node2Shell/HTTP2Shell) Also open-source: Some examples:
    Télécharger
    63019815.6K
  2. Juan Sebastián Henao✓@juanhenaoparra
    just open sourced a gateway for herdr: an HTTP API + task queue for running coding agents on your own VPS. i’m a big herdr fan, and wanted to automate coding tasks from apps, scripts, or other agents, not just from my terminal. send a repo + prompt, and it: - queues the task - creates a dedicated git worktree + branch - opens a herdr tab and starts claude code or pi - reports progress through polling or webhooks you can send follow ups to the same agent with its context intact, or jump into its terminal and take over. use it to trigger bug fixes from your app, investigate failing tests from CI, or let one agent delegate coding work to another. how i built it: a small node.js + express service wrapping the herdr CLI. FIFO queue with configurable concurrency, state persisted to disk, and automatic cleanup of old sessions and worktrees. no redis or database required. herdr handles the terminals and agents. the gateway makes them accessible over HTTP.
    14321383
  3. 偏見で語る兵器bot✓@heikihenken
    TOG2 英国が開発した重戦車。名前の意味は老害その2、いや比較的マジで。時代遅れも甚だしい古い設計を象徴する筆箱のように長い車体はなんというか呆れというやつである。重さのせいか地味に電気駆動だったり足回りは頑張っている最新の老害だ
    Télécharger
    34642.7K
  4. Promix@Promixyz
    it's f*cking gold Claude Code can turn reverse engineering into an AI powered investigation lab 18 GitHub tools to inspect Android apps, analyze binaries, trace network traffic, and rebuild software from verified evidence GIVE AI THE FULL TOOLBOX 01 REA ▸ → connect an AI assistant to reverse engineering tools through MCP DECOMPILE THE CODE 02 Ghidra ▸ → decompile binaries and inspect program structure 03 GhidraMCP ▸ → expose Ghidra analysis tools to AI agents 04 IDA Pro MCP ▸ → let agents inspect functions and cross references in IDA REVERSE ENGINEER MOBILE APPS 05 JADX ▸ → recover Java like source from Android APKs 06 Apktool ▸ → decode and rebuild Android application resources 07 Frida ▸ → instrument running applications for dynamic analysis 08 ILSpy ▸ → decompile and inspect .NET assemblies ANALYZE BINARIES 09 radare2 ▸ → inspect machine code, functions, and binary structures 10 x64dbg ▸ → debug Windows applications at runtime 11 ImHex ▸ → inspect binary formats with patterns and hex analysis 12 angr ▸ → explore program behavior using symbolic execution TRACE NETWORK BEHAVIOR 13 mitmproxy ▸ → inspect HTTP traffic in authorized test environments 14 dnSpyEx ▸ → debug and inspect managed .NET applications 15 rizin ▸ → analyze executable files and disassembly 16 raddebugger ▸ → debug native programs with a visual interface REBUILD FROM EVIDENCE 17 Awesome AI Reverse Engineering ▸ → discover AI assisted reverse engineering tools 18 Awesome Reverse Engineering ▸ → find curated resources for binary analysis Start with software you own or have permission to analyze 1 → Decompile the target with Ghidra or JADX 2 → Collect function names, cross references, and observed behavior 3 → Feed the evidence into Claude Code with a strict analysis prompt 4 → Write SPEC.md describing inputs, outputs, and edge cases 5 → Implement an independent version from the specification 6 → Run comparison tests and repeat until the documented behavior matches COPY THIS PROMPT: " Analyze the supplied reverse engineering evidence Separate verified behavior from assumptions Produce SPEC.md with inputs, outputs, state transitions, and edge cases Propose an independent implementation based only on authorized evidence Generate tests for every documented behavior Flag anything that cannot be verified " The expensive part of reverse engineering isn't opening a decompiler It's turning thousands of disconnected observations into a specification you can actually implement and test 18 tools, one investigation workflow, a reproducible path from evidence to working code should I write the full guide to building this with Claude Code?
    Télécharger
    Promix @Promixyz
    84632.6K
  5. Promix@Promixyz
    1124188418K
  6. Bun@bunjavascript
    Bun v1.4.4 - Fixes 271 issues, addressing 544 👍 - `bun fmt` is a fast Prettier-compatible code formatter - `bun check` gets 1.4x - 7.8x faster - New in Bun.SQL & WebSocket - Security fixes, including for Brotli, TLS certs, HTTP/3, and more
    48761.3K91.7K
  7. Ed✓@ed__marquez
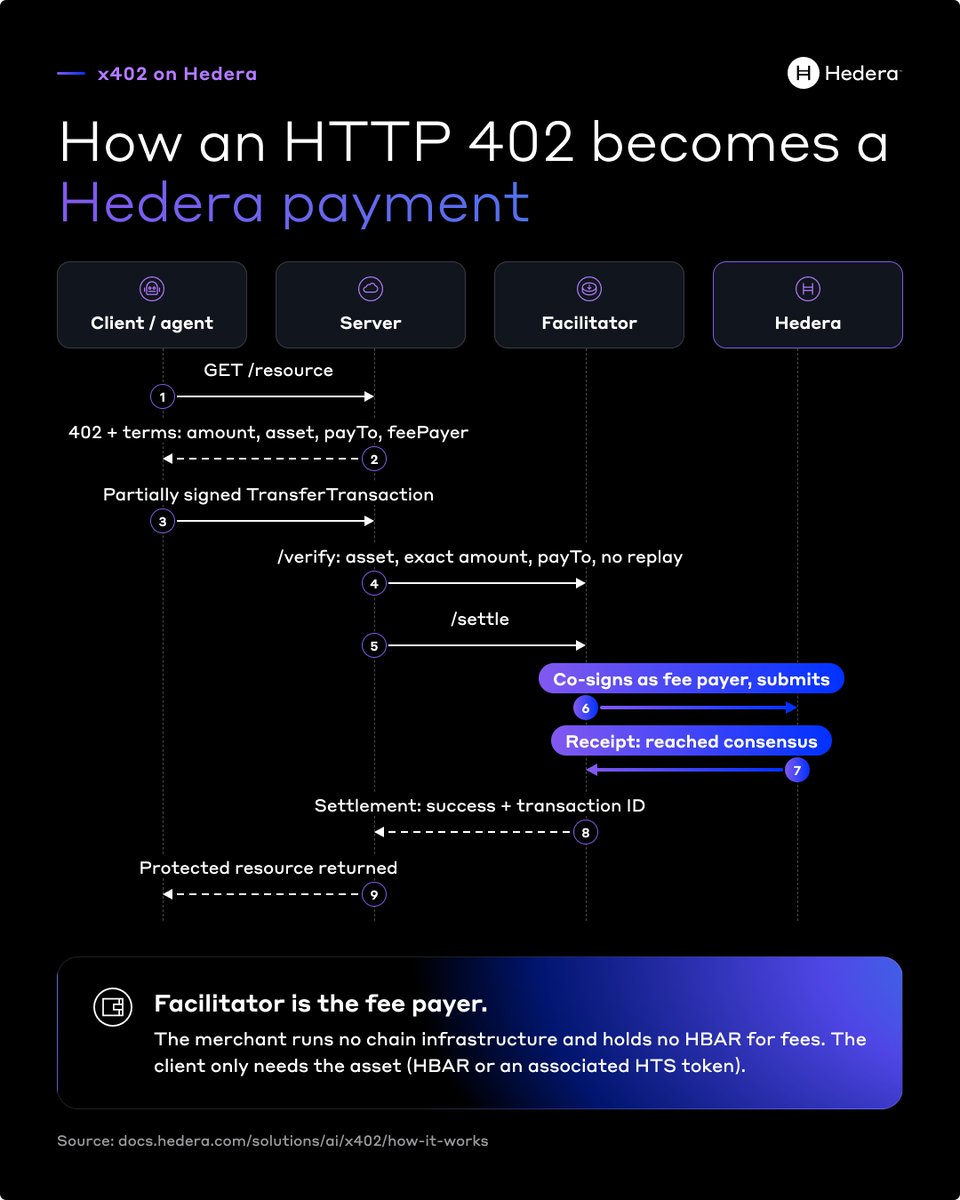
    1/ HTTP has a status code for payments that was never really used: 402 Payment Required x402 is an open standard that puts it to work A server asks for payment inside a normal request, and a client, like an AI agent, pays without a checkout page or an account... kinda genius
    Télécharger
    417693.3K
  8. Sodi✓@sodi_trade
    rx402: private x402 payments for agents, on Sodi. rx402 lets an agent pay for an API with an HTTP 402 response and a stablecoin transfer. The catch: every payment comes from the agent’s wallet, so anyone can link every call it makes back to its owner. rx402 breaks that link. The owner deposits USDG into a privacy pool on Robinhood Chain, and an approval service screens deposits before they can be spent. The agent opens a session: a zero-knowledge proof that it owns funds in the pool, and a withdrawal of a small budget to a brand-new address. A relayer pays the gas, so nothing funds that address traceably. From there the agent pays x402 endpoints (data feeds, APIs, inference) like any other wallet, and rotates to a fresh address when the budget runs out. Merchants see an ordinary payment. Nobody can link a session to the owner, or to the next session. SDK (@sodi/rx402), MCP server and contracts, open source:
    Télécharger
    203402.2K
  9. Duong Phat✓@duongphat99
    Q: Can AI agents hire people through Vangrid? A: Yes, per the docs. An agent sends one HTTP request, pays in USDC on Base or Arc through x402, and a contributor goes to film the place. Q: How much of the bounty board is agents? A: One of 973 bounties, per an independent read of the public board on 19 October 2026. Q: So is the agent path real? A: The path exists and is documented. The board says usage is early. Both can be true. Q: Where does that number move? A: On the board at so check there before repeating mine. Capability and usage are different columns, ngl, and coverage tends to fill in only the first one. has the path, covers the product, and @vangrid_io is the account behind it.
    Duc Crypto @DucCryptoX
    An independent write-up read Vangrid's public pages on 19 October 2026. The numbers are a good lesson in why counters need their definitions. Captures: 1,304,193. Footage fingerprints recorded. Events: 2,644,152. Captures plus accesses, so more than double the capture count and not a measure of footage. Trees: 5,356 listed on the explorer, 5,175 anchored. 181 weren't anchored yet at that moment. Bounties: $636,514 created and funded, of which $620,030 accepted, 942 out of 973. Four counters, four questions: how much footage, how much activity, how much is anchored, how much money moved. Quote one without its definition and it says something it doesn't. That was one afternoon's reading and the pages update constantly, so confirm on and before repeating any of it. @vangrid_io is the account behind it, and has the product.
    2627222867
  10. Duc Crypto✓@DucCryptoX
    An independent write-up read Vangrid's public pages on 19 October 2026. The numbers are a good lesson in why counters need their definitions. Captures: 1,304,193. Footage fingerprints recorded. Events: 2,644,152. Captures plus accesses, so more than double the capture count and not a measure of footage. Trees: 5,356 listed on the explorer, 5,175 anchored. 181 weren't anchored yet at that moment. Bounties: $636,514 created and funded, of which $620,030 accepted, 942 out of 973. Four counters, four questions: how much footage, how much activity, how much is anchored, how much money moved. Quote one without its definition and it says something it doesn't. That was one afternoon's reading and the pages update constantly, so confirm on and before repeating any of it. @vangrid_io is the account behind it, and has the product.
    26572538.7K
  11. Barely Working@BarelyWorkingHQ
    That padlock in your browser doesn't mean a website is safe. It never did. It only means your connection is encrypted. Scam sites can get the same padlock for free. Did you think it meant safe? Reply YES. #cybersecurity #https #barelyworking
    Télécharger
    0003
  12. The Hacker News@TheHackersNews
    ‼️ PHP patches Windows builds AGAIN, just 5 days after the PHP2Shell fixes. This time, a Brotli flaw could allow code execution when cURL automatically decompresses crafted HTTP responses. Updated builds cover PHP 8.2–8.5. Full details:
    Télécharger
    1612451966.2K
  13. Rafał@rafalohaki
    Working RCE against PHP 8.5.12 (the 2026-10-21 security release that fixed CVE-2026-109618/109619). Pure logic bug — no memory corruption, ASAN-clean, orthogonal to the CVE-2026-109618/19 class. Receipt: uid=33(www-data) over HTTP, one-shot #infosec #php2shell #php
    Télécharger
    Jλckλι @J4ck3LSyN
    .... Dude the internet is cooked .... This can't be patched out 😈... #CyberSecurity #infosec
    2496849166K
  14. 偏見で語る兵器bot✓@heikihenken
    VI号戦車 ティーガーI みんな大好きドイツの重戦車。何気にマトモに配備された独軍重戦車ってコイツが初めてのような。これまでドイツ戦車なんか性能はクソザコと思っていた赤軍をビビらせたぞ。それで独ソ戦の戦況は好転しましたか?(振え声)
    Télécharger
    6142205.8K
  15. Holmms✓@Nyerishi
    The most counterintuitive detail in @vangrid_io's documentation is the line about latency: "A person has to go and film, so this takes hours or days." Most infrastructure projects try to hide the human delay. Vangrid built it into the product. An AI agent can commission a capture with one HTTP call, pay in USDC on Base or Arc through x402, and receive the reconstructed 3D model back through the same API. No account. No API key. The transfer settles before the request is even processed . But the agent doesn't sign the escrow directly. It goes through @vangrid_io 's operator wallet, tagged "AGENT" on the bounty board. And the spend caps only constrain signing. They don't constrain the two calls that matter most: accepting a submission releases the escrow, cancelling ends it. Both irreversible. Both outside the caps. The docs tell operators to gate those two calls behind human approval when the agent is unattended . So the loop has three parties. Software requests. A human walks and films. Another human (or a gated approval) decides if the work was good enough. The employer can be software. The judgment layer doesn't disappear. It moves. Source:
    24110119800
  16. Mark Maunder✓@mmaunder
    StealMyBitcoin is solved! This is the absolute best explanation you’ll see on how hard #php2shell is to exploit. The author had to trigger a precise memory corruption condition, leak internal memory addresses, bypass aslr, reverse engineer php’s internal memory structures, forge structures to hijack execution, and account for php build differences, worker behavior and timing to get RCE. 20 http requests with a 7 out of 10 success rate. What an amazingly successful CTF. Impressive the creator was able to keep the server up during all the attempts. With all the BS around it’s nice to see something concrete that moves the art forward.
    Mark Maunder @mmaunder
    Love this. The💰is still in the wallet. Finally we get some ground truth around how hard php2shell is to exploit. The amount of bullshit flying around from vendors capitalizing on the moment is staggering, And the alert fatigue they’re creating is really going to hurt when a mass exploitable RCE emerges. We still haven’t seen a production site hacked via #php2shell at Wordfence.
    341621.7K143K
  17. Mark Maunder✓@mmaunder
    Love this. The💰is still in the wallet. Finally we get some ground truth around how hard php2shell is to exploit. The amount of bullshit flying around from vendors capitalizing on the moment is staggering, And the alert fatigue they’re creating is really going to hurt when a mass exploitable RCE emerges. We still haven’t seen a production site hacked via #php2shell at Wordfence.
    1016203149K
  18. Chris - Local SEO✓@ChrisSimpson
    Your website loads with www and without www. To Google, that's two identical sites. Half your crawl budget goes to each. Pick one version. 301 redirect the other. Same for http to https. Then make everything match it: your canonical tag your internal links (contact, appointment buttons) your citations and social profiles Check yours: type your domain both ways and see where each one lands. If your canonical points to a URL that redirects, you're teaching Google not to trust your canonical tags.
    132283.5K
  19. Bun@bunjavascript
    We published three security advisories for Bun 1.4.3 and earlier: compromised eMudhra certificates, the brotli decoder bug (HTTP2Shell), and the HTTP/3 "Header Accordions" attack. These are all fixed in Bun 1.4.4. Please upgrade, and rebuild anything made with `bun build --compile` $ bun upgrade
    194760540.4K
  20. 偏見で語る兵器bot✓@heikihenken
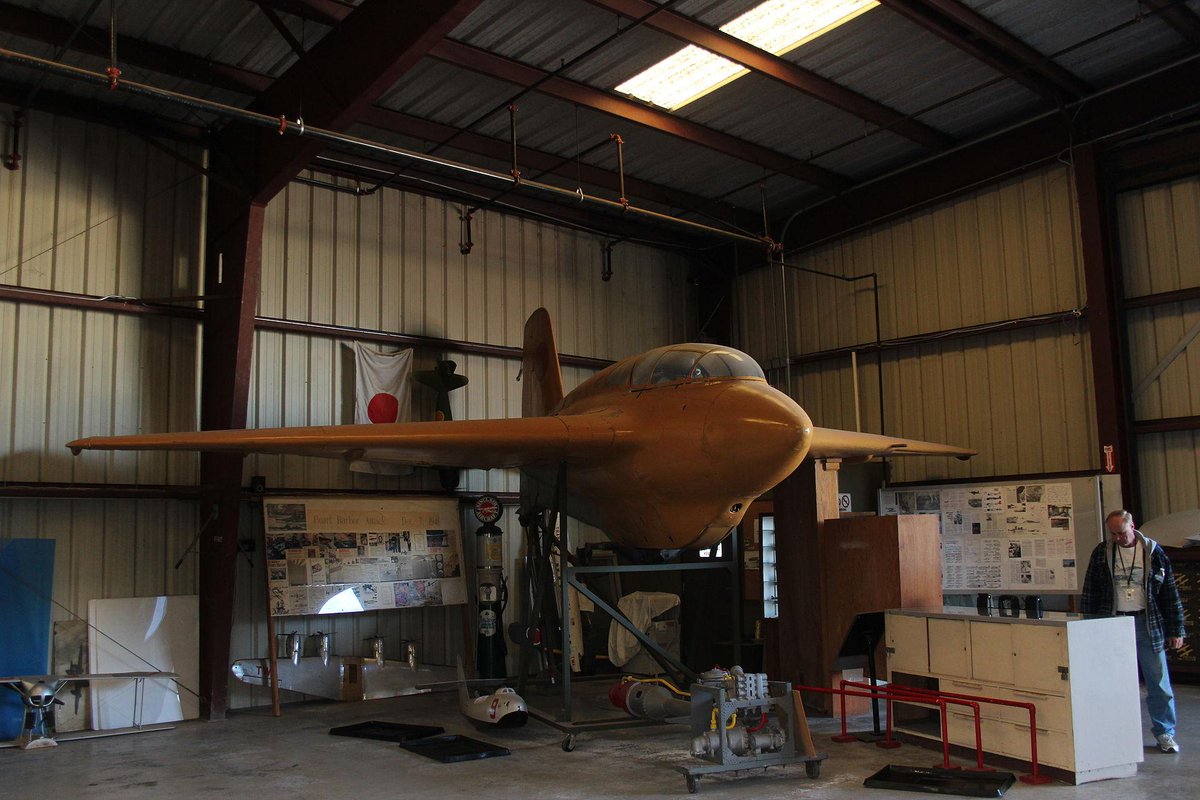
    秋水 コメートじゃないです。いや図面貰ってるから参考にはしてるけど完コピはできなかったんだよなぁ…とにかくその上昇力と速度でB-29をぶち殺すために作られたけど完成は間に合わなかった模様。B-29が速すぎて追いつけない日本機の悲しみ
    Télécharger
    10161649.3K
  21. 横浜生活保護利用者の会@dppyokohama
    以前、解放派全学連のHPに、「今いじめられている君へ」と言うアピールが掲載されていた。何の掛け値なしに秀逸な文章だと感じた。小生もイジメ被害者だが、あのような考え方には至らなかった。もう40年以上たつのにフラッシュバックに襲われる。もう一度あの文章を読み返したい。
    217863.9K
  22. 偏見で語る兵器bot✓@heikihenken
    Hs-129 機関砲で装甲車両を駆逐してやるぜマシーンとして生まれたドイツ軍攻撃機。安く作れるが出力が不安なエンジンでも双発だからどうにか飛べて低コスト。強くても作れなきゃ無意味。改良のたびに大型化した機関砲で空飛ぶ缶切りと言われた
    Télécharger
    271105.9K
  23. Afficher plus de posts